

picard
 neitzert/picard
Protocol-Introspecting Chunk Adapter for Resilient Data
bluetooth-securitycryptographydata-exfiltration+6
neitzert/picardProtocol-Introspecting Chunk Adapter for Resilient Data
 tonixtoolkitofficial-afk/esp32-blue-ducky
ESP32 firmware that emulates a Bluetooth HID keyboard to auto-pair with Android phones and inject scripted keystrokes for authorized security testing.
 wh02m1/cve-2026-77812
Proof-of-concept that passively sniffs cleartext BLE DUML traffic from DJI drones to recover Wi-Fi PSK and trusted session UUIDs, demonstrating…
 roostercoopllc/flipper-mcp
AI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
 idkwim/cve-2020-0022
Research repository documenting BlueFrag (CVE-2020-0022) Android Bluetooth heap overflow experiments, including GDB crash analysis and memcpy…
 barghest-ngo/cve-2026-51376
Proof-of-concept exploit for BLE cache poisoning in Bitchat 1.15.0, demonstrating a man-in-the-middle attack that poisons the Bluetooth Low Energy…
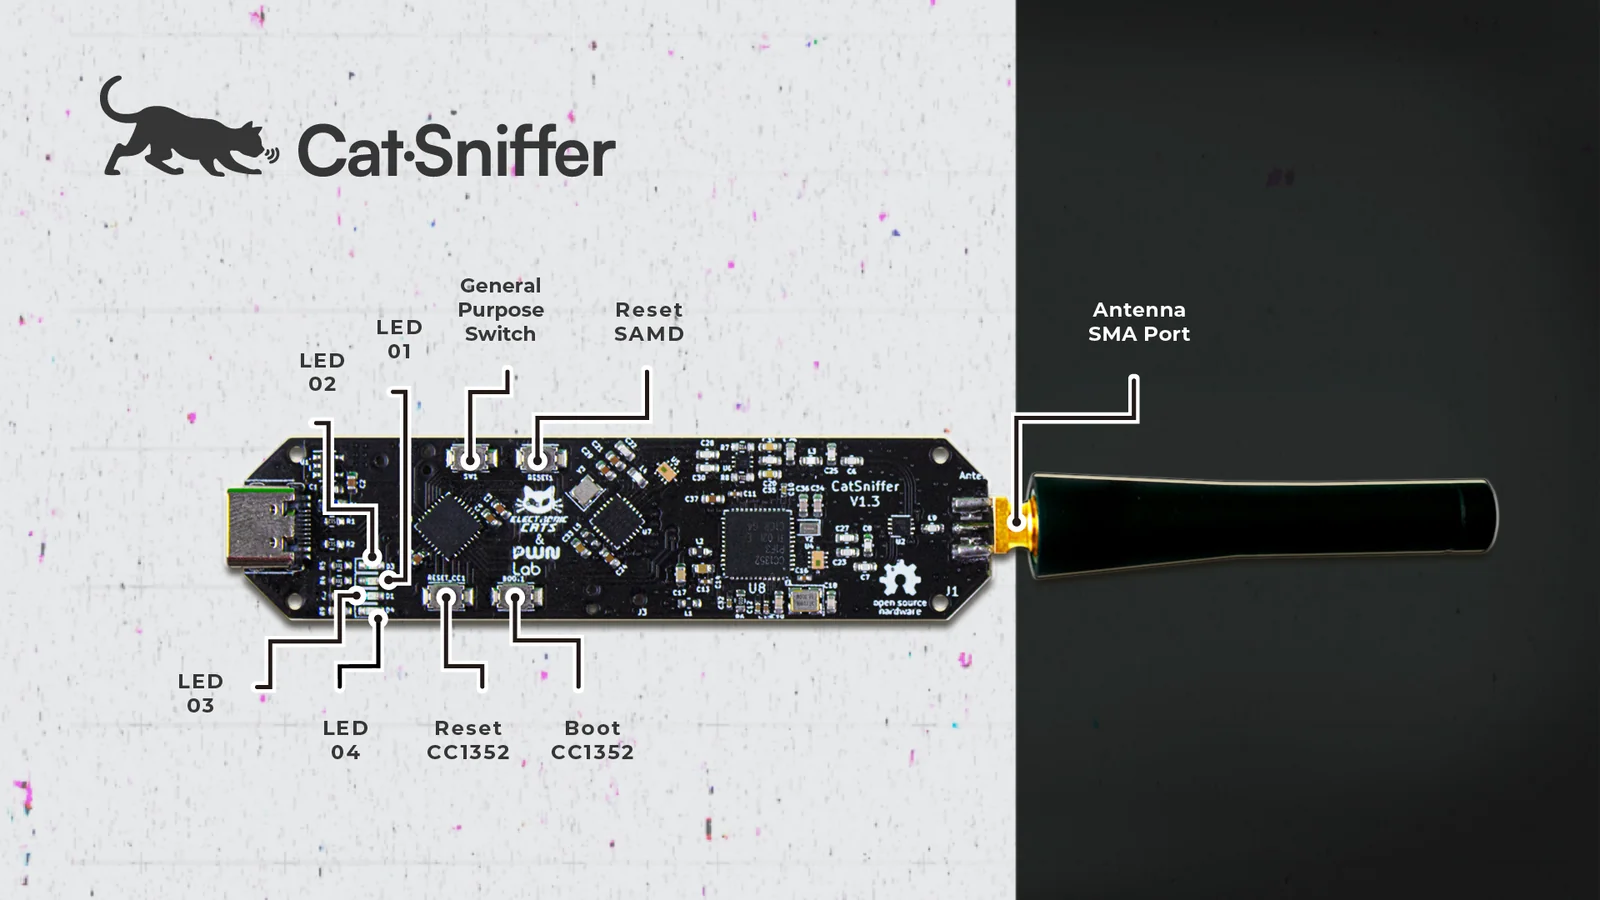 electroniccats/catsniffer-firmware
Firmware repository for CatSniffer, a multi-protocol IoT security research board supporting BLE, Zigbee, Sub-1 GHz, and more, with version-specific…
 eason-zz/bluetoothducky
Exploit implementation for CVE-2023-45866 enabling unauthenticated Bluetooth keyboard injection using DuckyScript payloads on Raspberry Pi.
 greatscottgadgets/libbtbb
C library for decoding Bluetooth baseband packets and extracting piconet information from Ubertooth and USRP hardware for wireless analysis.
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
 antoinet/obike
Reverse engineering of the oBike protocol communication (BLE and HTTP)
 nccgroup/bleboy
BLEBoy is a training tool to teach users about BLE security by providing a single BLE peripheral that can be used to experiment with each BLE pairing…
 nccgroup/blesuite
BLESuite is a Python package that provides an easier way to test Bluetooth Low Energy (BLE) device
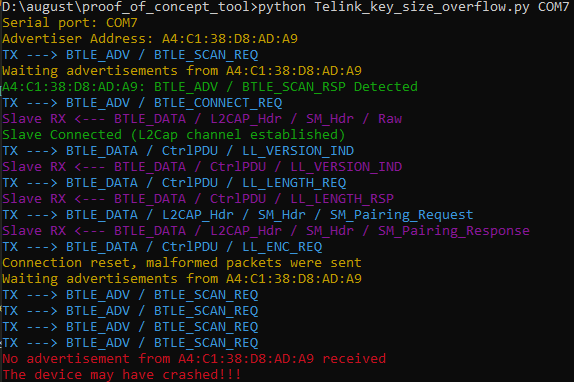 matheus-garbelini/sweyntooth_bluetooth_low_energy_attacks
Proof of Concept of Sweyntooth Bluetooth Low Energy (BLE) vulnerabilities.
 oxasploits/oxasploits
A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast
 f4r3sx0/ios-bluetooth-ethernet-exploit
iOS Bluetooth PAN vulnerability that opens USB port 62078 and displays Ethernet icon without any adapter (€0). Apple sells a €89.95 adapter for the…