

x64dbg
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
ai-assisted-reversingbinary-analysisbinary-exploitation+7
49.1k6 days ago
x64dbg/x64dbgAn open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 x86rc/vmp-lazy-unpack
Emulation-based unpacker and import resolver for Windows x86/x64 VMProtect 3.x binaries, using Unicorn to emulate syscalls and rebuild the IAT…
 tiger3080/cve-2025-9267
Seagate Toolkit for Windows (Installer <2.35.0.6) is vulnerable to insecure DLL loading. The installer loads DLLs from the working directory without…
 ngwg/ceasta
Disassembler, decompiler and x64dbg-style debugger for PE/ELF binaries with IDA-style listing, function graphs, Lua plugins, CLI, and a built-in MCP…
 homjxi0e/cve-2017-3078
Proof-of-concept exploit for CVE-2017-3078, a memory corruption vulnerability in Adobe Flash Player ATF module enabling arbitrary code execution on…
 worawit/cve-2019-0708
CVE-2019-0708 (BlueKeep)
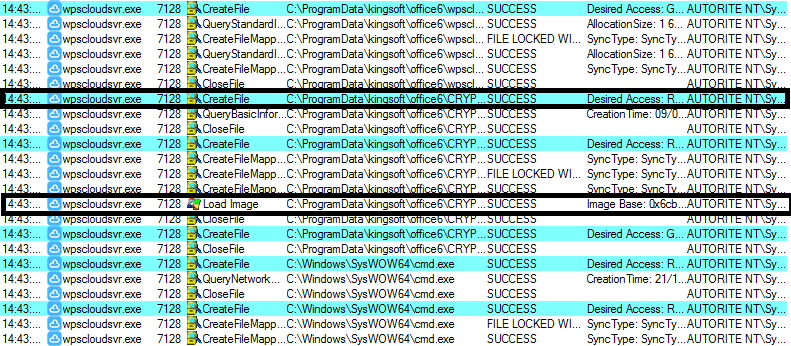 hadimed/kingsoft-wps-office-lpe
CVE-2022-25943
 freeide/cve-2021-31955-poc
Proof-of-concept exploit for CVE-2021-31955, a Windows kernel information disclosure vulnerability. Demonstrates exploitation on 64-bit systems to…
 structio-labs/n0xis
Reverse-engineering toolkit: disassembler, SSA decompiler, C++ class recovery and live-process analysis for PE and ELF. Scriptable CLI, every answer…
 gmh5225/lithium-kernel
Windows kernel-mode driver with user-mode client exposing IOCTL-based physical and virtual memory read/write, page table walking, pattern scanning,…
 aaroncaiii/cve-2020-0796-poc
CVE-2020-0796-POC
 exploits-forsale/prefetch-tool
Windows KASLR bypass using prefetch side-channel
 mein-0/cve-2026-29923
Proof-of-concept for CVE-2026-29923, a local privilege escalation in pstrip64.sys kernel driver. Demonstrates physical memory read/write primitive…
 ianyong/cve-2022-32223
Demonstration exploit for CVE-2022-32223: DLL hijacking in Node.js on Windows via malicious providers.dll, targeting OpenSSL installations.
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
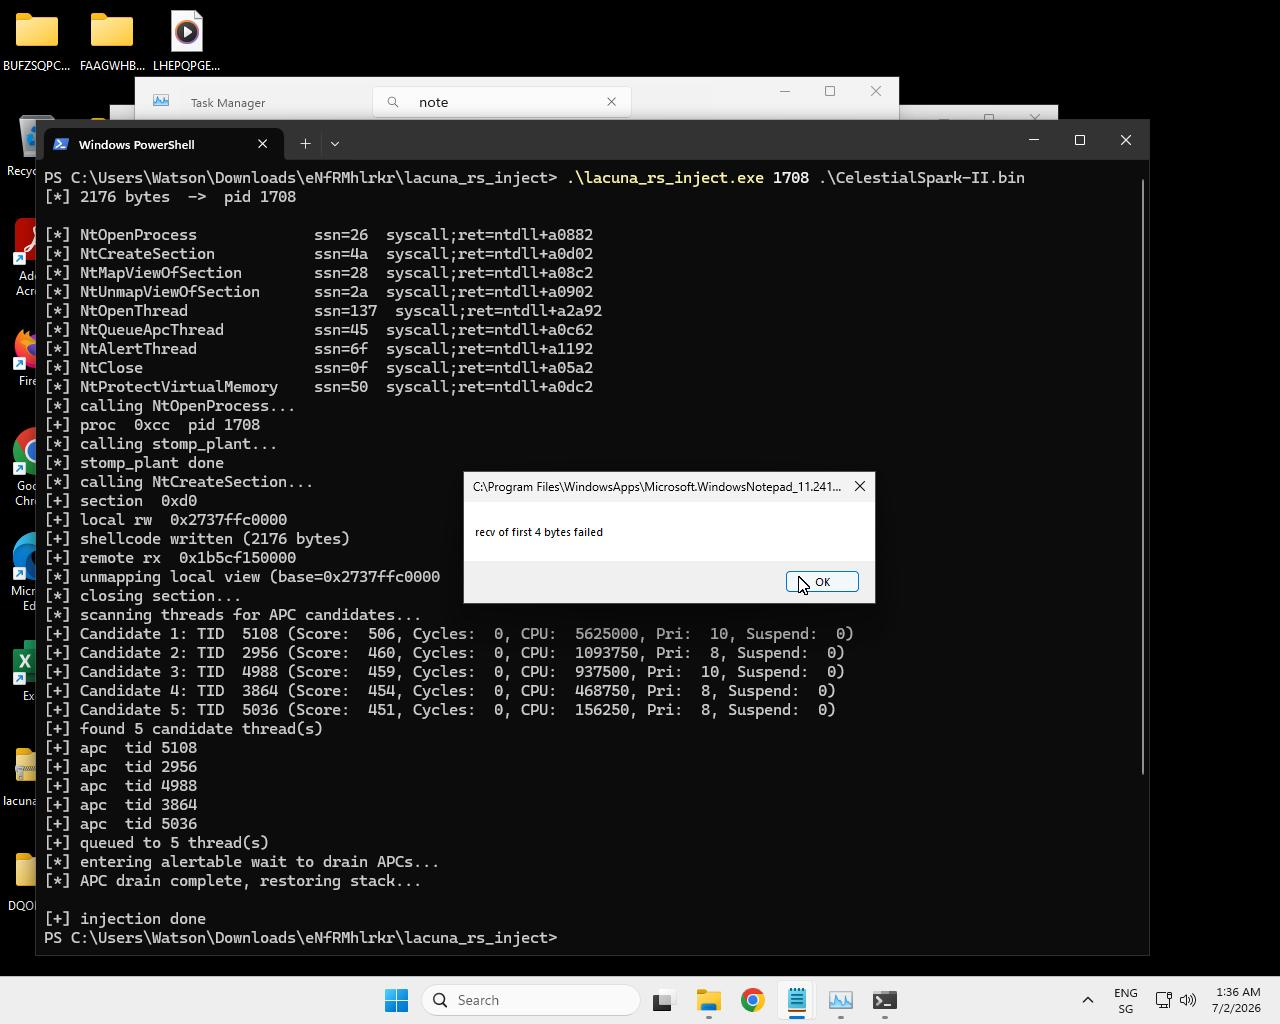 karkas66/lacuna-rs
Rust crate for ghost-frame call-stack spoofing, runtime indirect syscalls, and APC injection on Windows x64. Provides SSN resolution, JIT stub…
 devianntsec/cve-2024-51324
Master's Thesis research on CVE-2024-51324 (BYOVD). Advanced exploit with 4 operational modes (SCANNER, LOADER, KILLER, CLEANUP), SHA-256 driver…