

CVE-2025-65264
 cwjchoi01/cve-2025-65264
Proof-of-concept exploit for CVE-2025-65264 demonstrating arbitrary kernel memory read via IOCTL in CPU-Z driver, enabling token theft and potential…
binary-exploitationeducationexploitation+2
cwjchoi01/cve-2025-65264Proof-of-concept exploit for CVE-2025-65264 demonstrating arbitrary kernel memory read via IOCTL in CPU-Z driver, enabling token theft and potential…
 rsmudge/cve-2020-0796-bof
Cobalt Strike Beacon Object File implementing CVE-2020-0796 SMBGhost local privilege escalation with dual weaponization paths for token theft and…
 de7ec7ed/cve-2016-0040
64-bit Windows kernel privilege escalation exploit for CVE-2016-0040 (WMI Receive Notification vulnerability) using GDI bitmap manipulation for token…
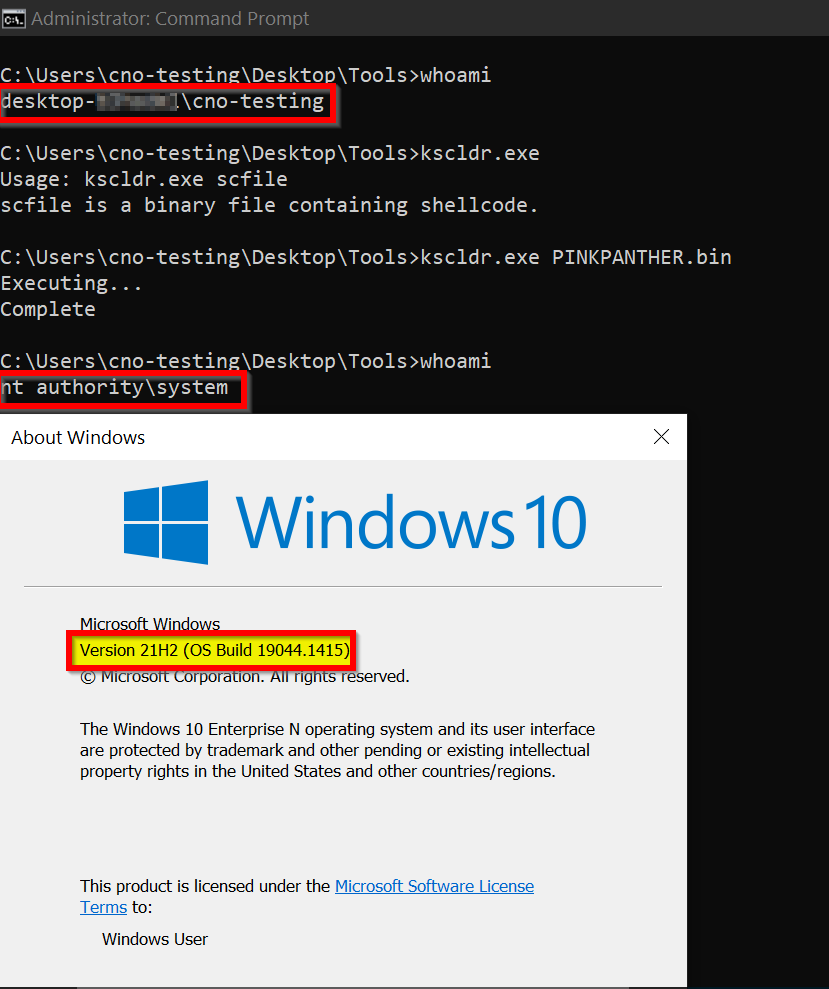 winterknife/pinkpanther
Windows x64 handcrafted token stealing kernel-mode shellcode
 hoangprod/cve-2021-31956-poc
Proof-of-concept exploit for CVE-2021-31956, a Windows kernel NTFS elevation-of-privilege vulnerability. Demonstrates exploitation techniques…
 avielzecharia/cve-2015-5736
PoC for CVE-2015-5736
 zeze-zeze/hitcon-2023-demo-cve-2023-20562
Demonstrates exploitation of AMD μProf driver (CVE-2023-20562) for privilege escalation via EPROCESS token write and DSE bypass, enabling unsigned…
 grisuno/cve-2022-22077
BYOVD exploitation framework for CVE-2022-22077 targeting RTCore64.sys. Demonstrates kernel token theft, privilege escalation to SYSTEM, and C2…
 hakivvi/cve-2021-40449
Windows LPE exploit for CVE-2021-40449, a use-after-free in win32kfull!GreResetDCInternal, leveraging token leaking, kernel gadget abuse, and…
 dbgbgtf1/cve-2026-40369-exploit
Exploit for CVE-2026-40369 that leverages kernel address leak and token forging to achieve privilege escalation in a browser sandbox environment.
 davidcarliez/cve-2026-66804-crossdevice-lpe
Local privilege escalation PoC for Windows CVE-2026-66804 using CrossDevice DLL planting and SigmaPotato token impersonation to spawn a SYSTEM…
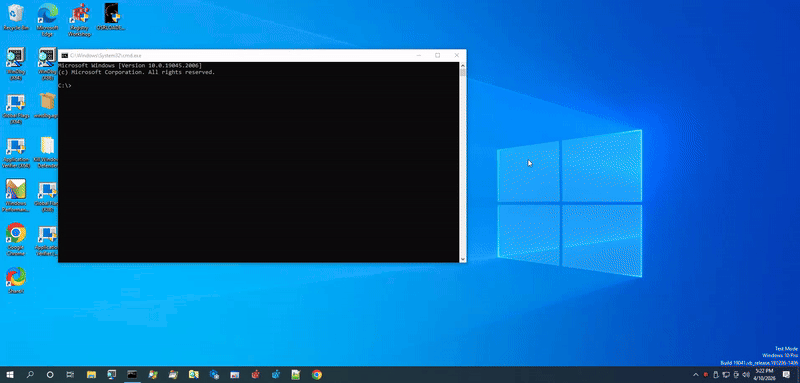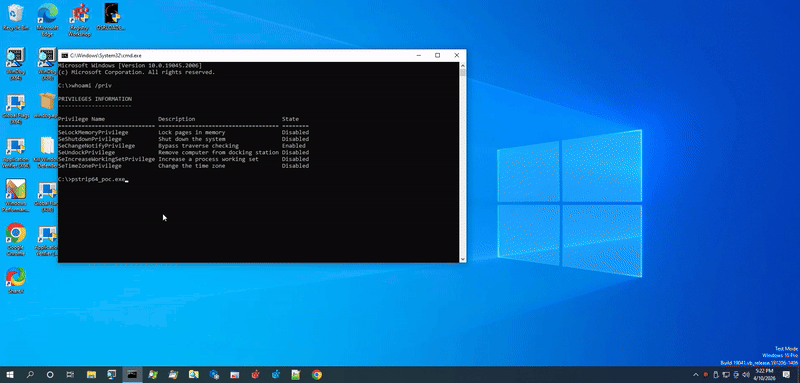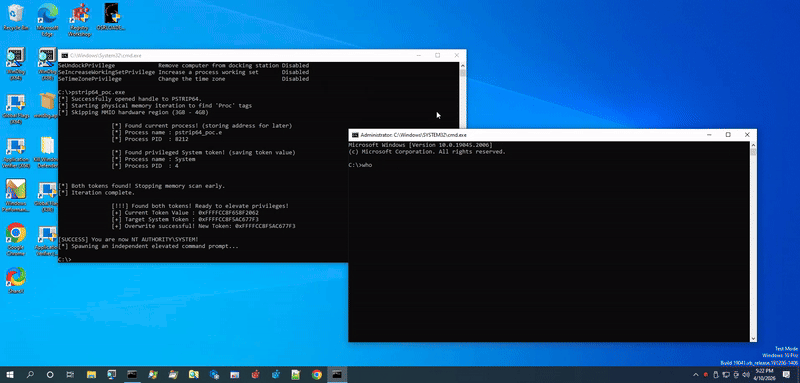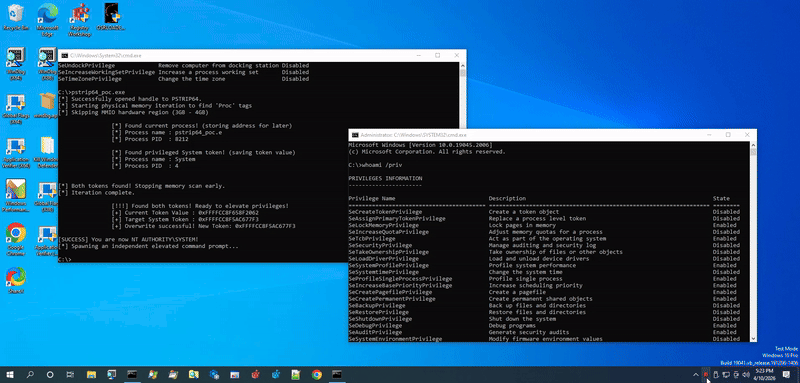 athenasec16/cve-2026-29923
Proof-of-concept exploit for CVE-2026-29923, a BYOVD privilege escalation in pstrip64.sys. Demonstrates physical memory read/write via IOCTL to steal…
 fortra/cve-2022-37969
Proof-of-concept exploit for CVE-2022-37969, a Windows Common Log File System driver local privilege escalation. Demonstrates heap spray, token…
 vportal/cve-2022-22715
Exploit code for CVE-2022-22715 (Windows Dirty Pipe), a sandbox escape and privilege escalation via named pipe TOKEN object corruption, with a linked…
 passwa11/hitcon-2023-demo-cve-2023-20562
Exploit for CVE-2023-20562 targeting AMD μProf driver to achieve SYSTEM privilege escalation via EPROCESS token arbitrary write, with DSE bypass and…
 mein-0/cve-2026-0828
Proof-of-concept exploit for CVE-2026-0828, a BYOVD vulnerability in Safetica ProcessMonitorDriver.sys allowing unprivileged termination of…
 bananoname/cve-2024-49138-poc
Proof-of-concept exploit for CVE-2024-49138 in Windows CLFS.sys, achieving local privilege escalation to system shell via token manipulation.
 uname1able/cve-2025-21333
Proof-of-concept exploit for CVE-2025-21333, a heap-based buffer overflow in Hyper-V's vkrnlintvsp.sys leading to local privilege escalation via I/O…