
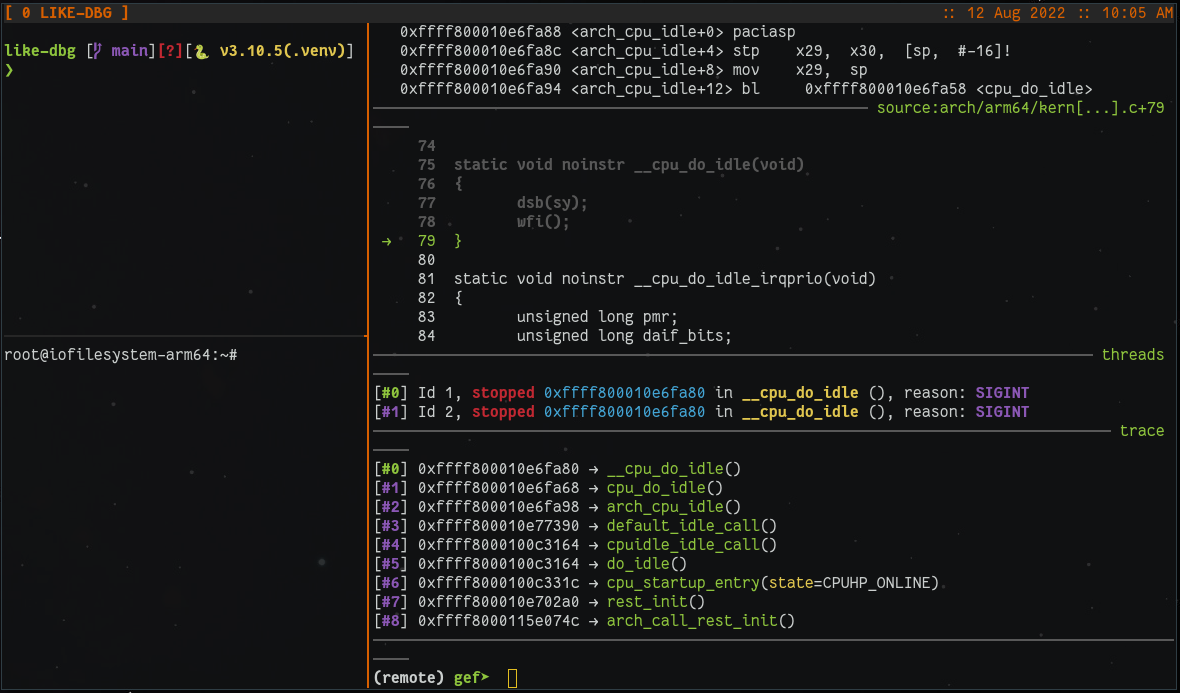
like-dbg
 0xricksanchez/like-dbg
Fully dockerized Linux kernel debugging environment
binary-exploitationctfdebuggers+2
0xricksanchez/like-dbgFully dockerized Linux kernel debugging environment
 petitoto/chromium-exploit-dev
Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits
 horkimhab/cve-2022-25477
CVE Realtek SD card reader. CVE-2022-25477, CVE-2022-25478, CVE-2022-25479, CVE-2022-25480, CVE-2024-40432, CVE-2024-40431
 horkimhab/cve-2026-53359
CVE-2026-53359 - Draft
 bend0us/dexloader
A demo Android project showcasing dynamic DEX loading using DexClassLoader, PathClassLoader, and in-memory execution. For educational purposes only.
 sarabpal-dev/ionstack-s22u
CVE-2026-43499 full exploit chain for Samsung Galaxy S22 Ultra (Android 5.10 kernel)
 oscerd/cve-2026-43867
Reproducer for CVE-2026-43867 — Apache Camel camel-pqc AwsSecretsManagerKeyLifecycleManager unsafe key-metadata deserialization (RCE)
 oscerd/cve-2026-40473
Reproducer for CVE-2026-40473: Apache Camel camel-mina MinaConverter.toObjectInput unsafe deserialization (RCE over TCP/UDP)
 oscerd/cve-2026-40048
Reproducer for CVE-2026-40048: Apache Camel camel-pqc FileBasedKeyLifecycleManager unsafe deserialization (RCE)
 oscerd/cve-2026-43865
Reproducer for CVE-2026-43865 — Apache Camel camel-hazelcast default-configured instance unsafe Java deserialization (RCE)
 oscerd/cve-2026-27172
Reproducer for CVE-2026-27172: Apache Camel camel-consul ConsulRegistry Java deserialization (RCE)
 oscerd/cve-2026-40859
Reproducer for CVE-2026-40859 — Apache Camel camel-netty-http / camel-vertx-http producer-side unsafe deserialization of HTTP response bodies (RCE)
 oscerd/cve-2026-40860
Reproducer for CVE-2026-40860 — Apache Camel camel-jms/sjms/amqp JMS ObjectMessage unsafe deserialization (RCE)
 oscerd/cve-2026-40858
Reproducer for CVE-2026-40858 — Apache Camel camel-infinispan remote aggregation repository unsafe deserialization (RCE)
 aperikube/pwn-arm-nfc
ARM buffer overflow challenge exploiting NFC tag input on Raspberry Pi. Includes hardware assembly guide, server code, and flag retrieval for CTF and…
 felix-pb/kfd
kfd, short for kernel file descriptor, is a project to read and write kernel memory on Apple devices.