
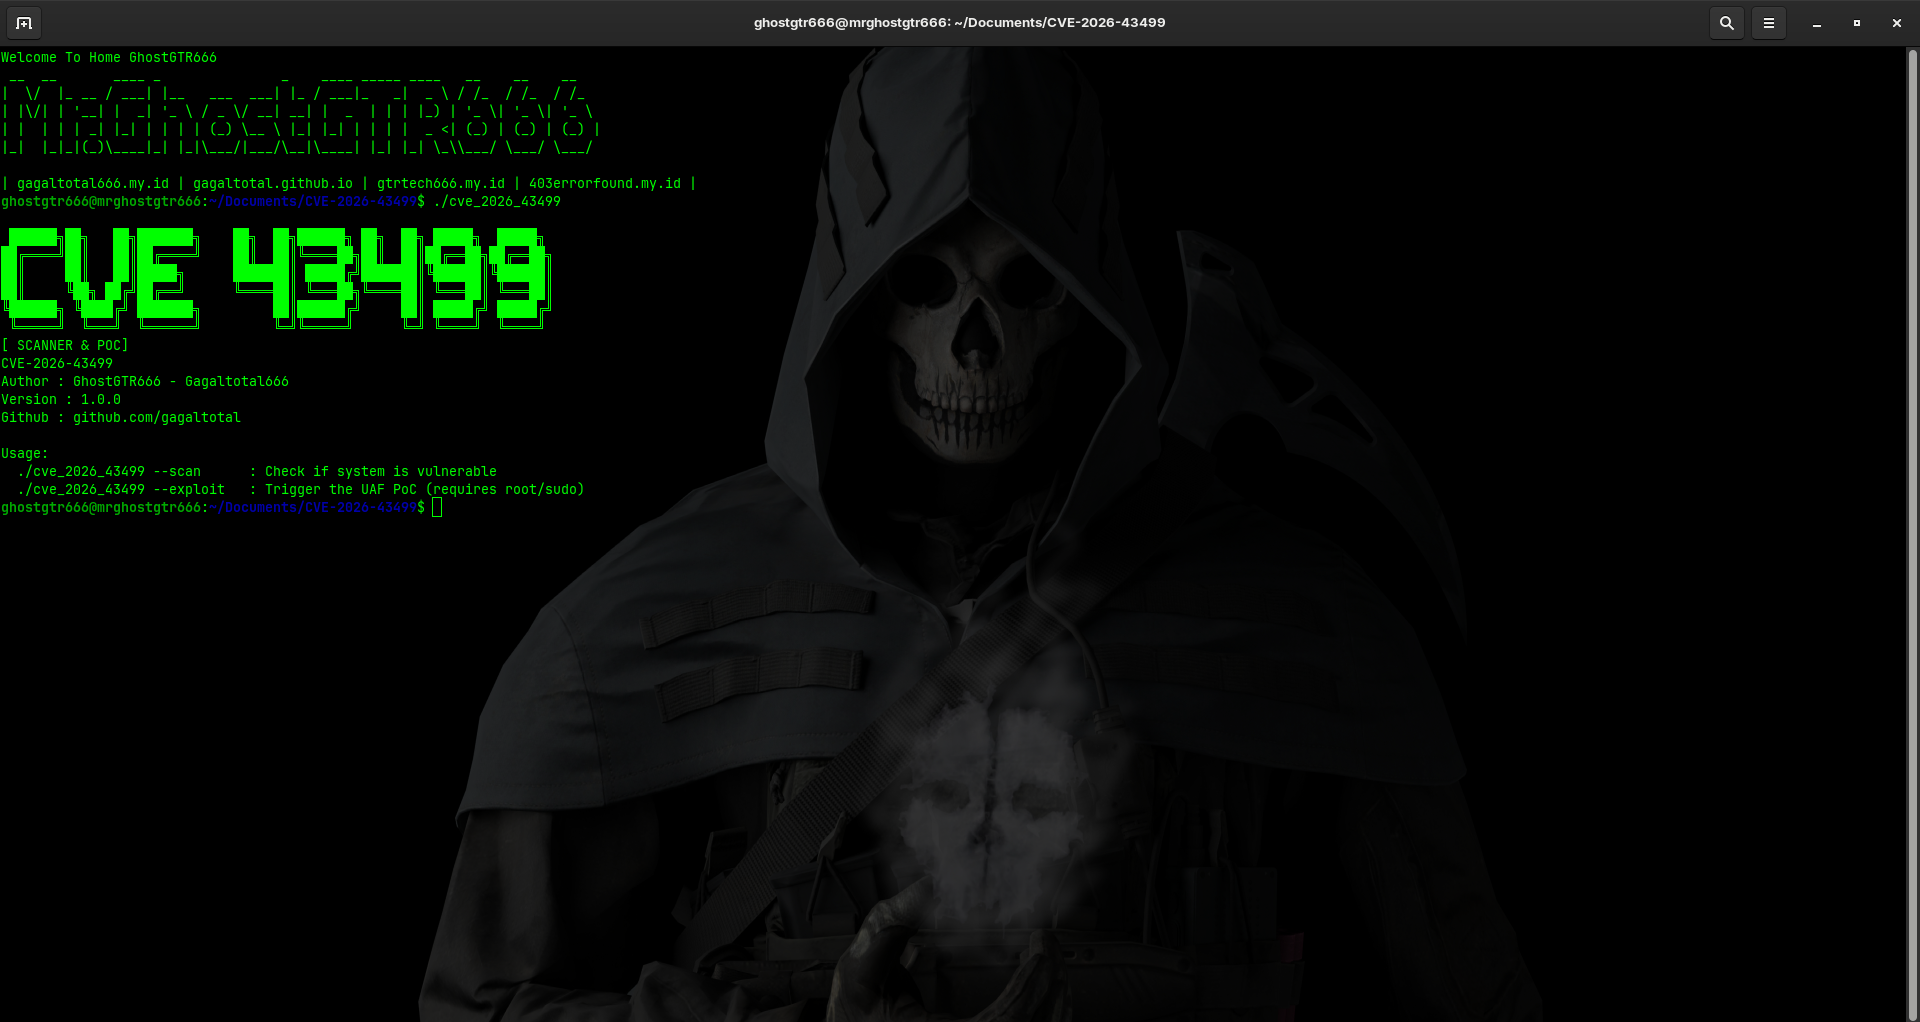
CVE-2026-43499-PoC-Scanner
 gagaltotal/cve-2026-43499-poc-scanner
CVE-2026-43499 PoC Scanner
binary-exploitationeducationexploitation+2
19
gagaltotal/cve-2026-43499-poc-scannerCVE-2026-43499 PoC Scanner
 nisec-eric/cve-2026-31431
Linux kernel local privilege escalation exploit for CVE-2026-31431, providing a reliable single-shot PoC with multiple language implementations,…
 zhanghangorg/cve-2026-31431
Detector and proof-of-concept for a Linux kernel page-cache write vulnerability (CVE-2026-31431) in algif_aead, including a non-destructive scanner…
 devianntsec/cve-2024-51324
Master's Thesis research on CVE-2024-51324 (BYOVD). Advanced exploit with 4 operational modes (SCANNER, LOADER, KILLER, CLEANUP), SHA-256 driver…
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 rizinorg/cutter
Free and Open Source Reverse Engineering Platform powered by rizin
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 angr/angr
A powerful and user-friendly binary analysis platform!
 axi0mx/ipwndfu
open-source jailbreaking tool for many iOS devices
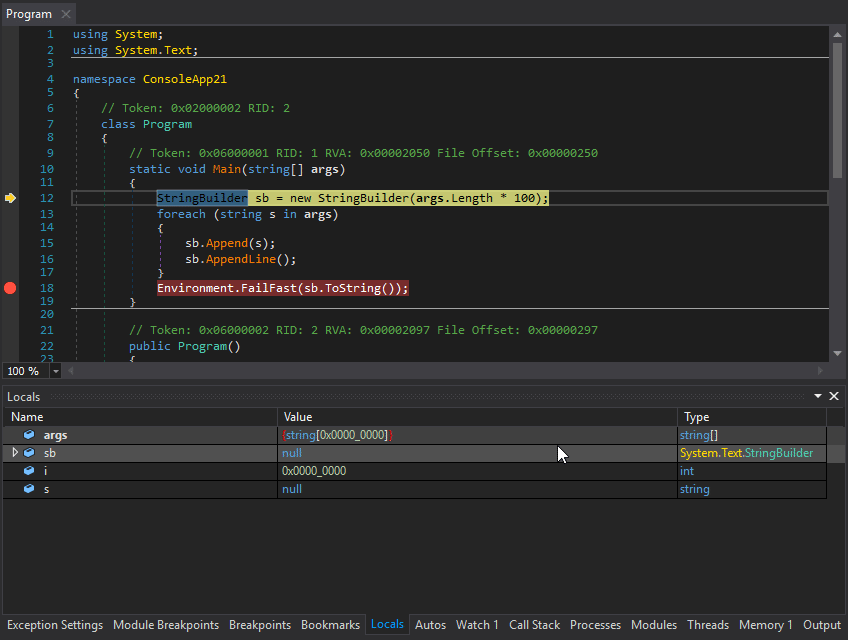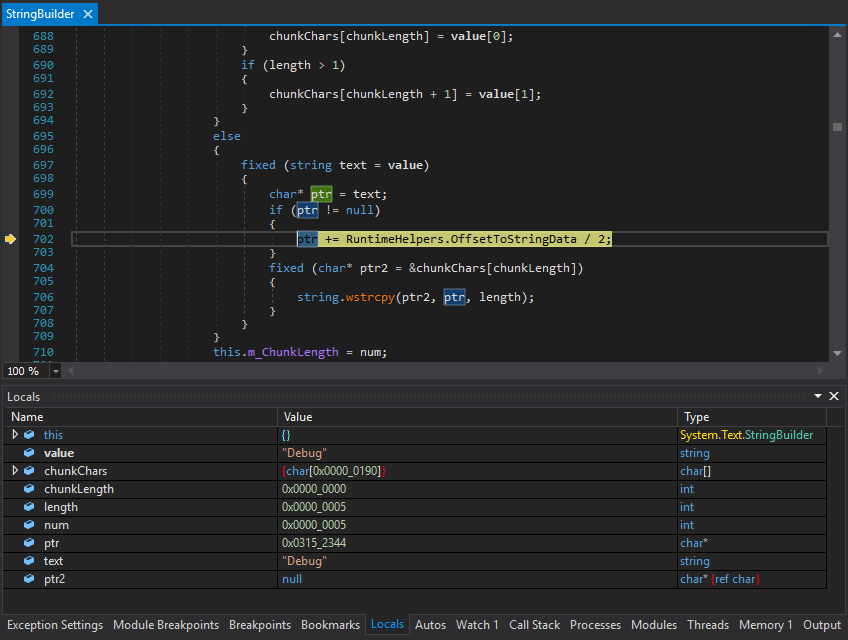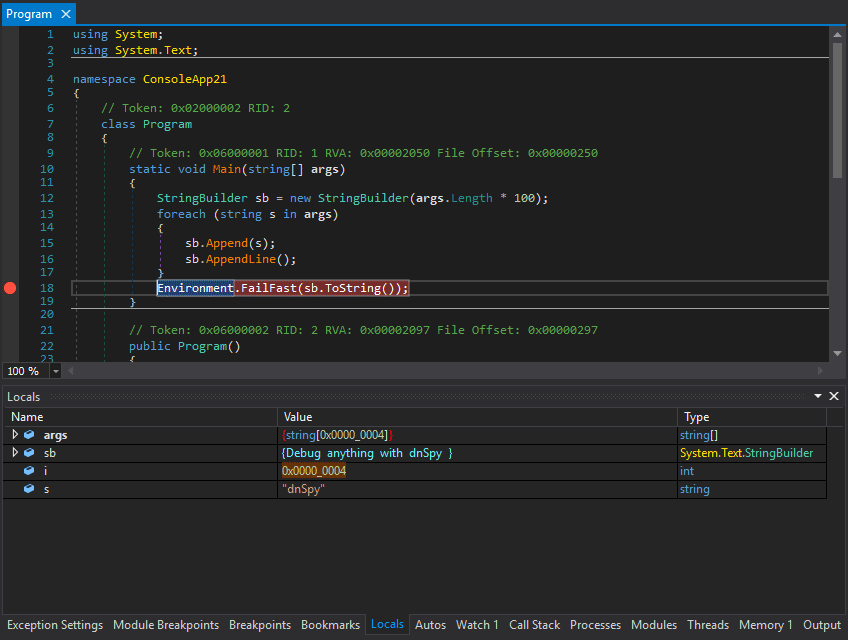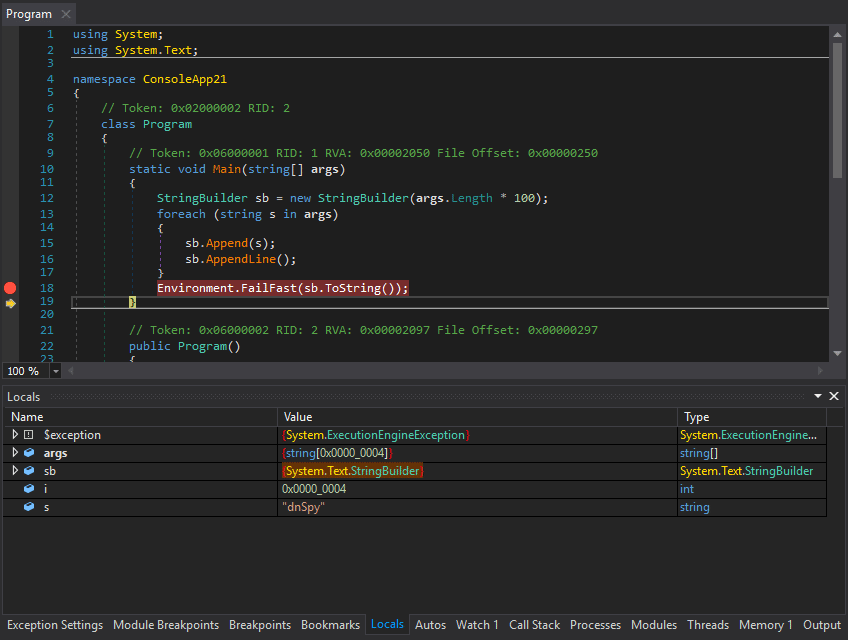 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.