
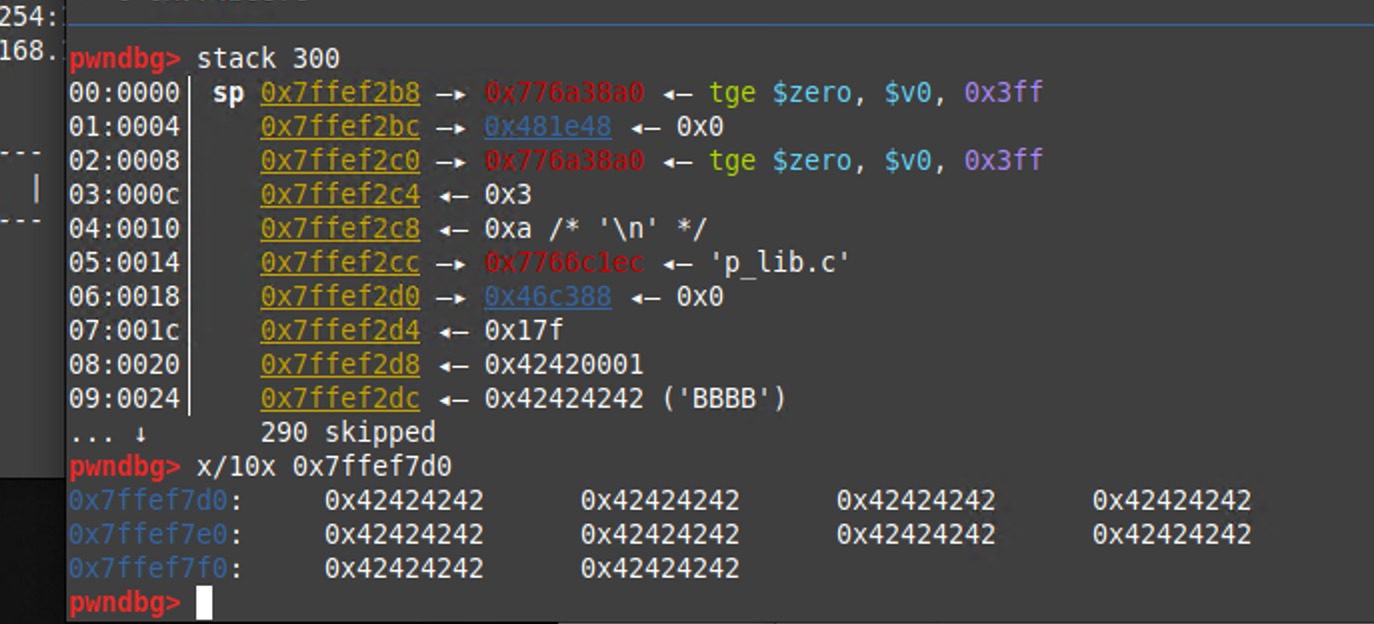
CVE-2024-29671-POC
 laskdjlaskdj12/cve-2024-29671-poc
This is POC of CVE-2024-29671
binary-exploitationembedded-systems-securityexploitation+7
1
laskdjlaskdj12/cve-2024-29671-pocThis is POC of CVE-2024-29671
 siddolo/gosign-desktop-exploit-poc
CVE-2025-34324, CVE-2025-34327: GoSign Desktop TLS Bypass & Insecure Update Exploit Proof of Concept
 stevenjoezhang/cve-2023-21537
PoC of CVE-2023-21537
 alt3kx/cve-2007-5036
Airsensor M520 - HTTPd Unauthenticated Remote Denial of Service / Buffer Overflow (PoC)
 natteesetobol/chakra-cve-2019-0567
A POC of a type confusion bug in chakracore framework that leads to code execute.
 sslab-gatech/pwn2own2020
Compromising the macOS Kernel through Safari by Chaining Six Vulnerabilities
 cryptogenic/ps4-6.20-webkit-code-execution-exploit
A WebKit exploit using CVE-2018-4441 to obtain RCE on PS4 6.20.
 hacksysteam/cve-2022-28672
Foxit PDF Reader Remote Code Execution Exploit
 h4x0r-dz/cve-2024-21762
out-of-bounds write in Fortinet FortiOS CVE-2024-21762 vulnerability
 fsecurelabs/cve-2018-4121
macOS 10.13.3 (17D47) Safari Wasm Exploit
 reigningshells/cve-2015-3073
CVE-2015-3073 PoC
 sneakynachos/cve-2026-87491-and-cve-2026-85046-the-bagel-fell-off-the-counter
Chrome 152 V8 exploit chaining CVE-2026-85046 and CVE-2026-87491 to corrupt the heap, forge Wasm metadata, and execute native code from the renderer.
 sneakynachos/cve-2026-87575-cve-2026-87606-cve-2026-87491-and-cve-2026-85046.-escape-the-v8-carcass.
Chained Chrome V8 renderer escape proof-of-concept exploiting four CVEs: Float64Array corruption, Wasm overwrite, popup navigation retargeting, and…
 springsec/cve-2022-22620
Webkit (Safari) - Exploit
 sam00/poc-cve-2026-0300-exploit
Palo Alto - CVE-2026-0300 exploit
 shinycolumn/cve-2025-56799
OS Command Injection Vulnerability via Cache Clearing Scheduler in Reolink Desktop Application
 paulsery/cve-2021-30632
m-y-mo: https://github.com/github/securitylab/tree/main/SecurityExploits/Chrome/v8/CVE-2021-30632
 jezzus/cve-2018-4121
Proof-of-concept remote code execution exploit targeting Safari 11.0.3 on macOS 10.13.3 via a WebAssembly section vulnerability (CVE-2018-4121).…