
CVE-2024-29510
 swsmith2391/cve-2024-29510
POC code for CVE-2024-29510 and demo VulnApp
binary-exploitationcontainer-escapeexploitation+3
12 years ago
swsmith2391/cve-2024-29510POC code for CVE-2024-29510 and demo VulnApp
 grimmmbo/ros2_cve-2024-28231
Demonstrating the usage of Fastrtps-DDS vulnerability CVE-2024-28231 within Ros2
 krypton-0x00/cve-2025-32463-chwoot-poc
Rust-based proof-of-concept exploit for CVE-2025-32463, a Sudo privilege escalation vulnerability. Spawns an interactive root shell or executes…
 vpr-labs/cve-2025-32463
C reimplementation of chwoot PoC
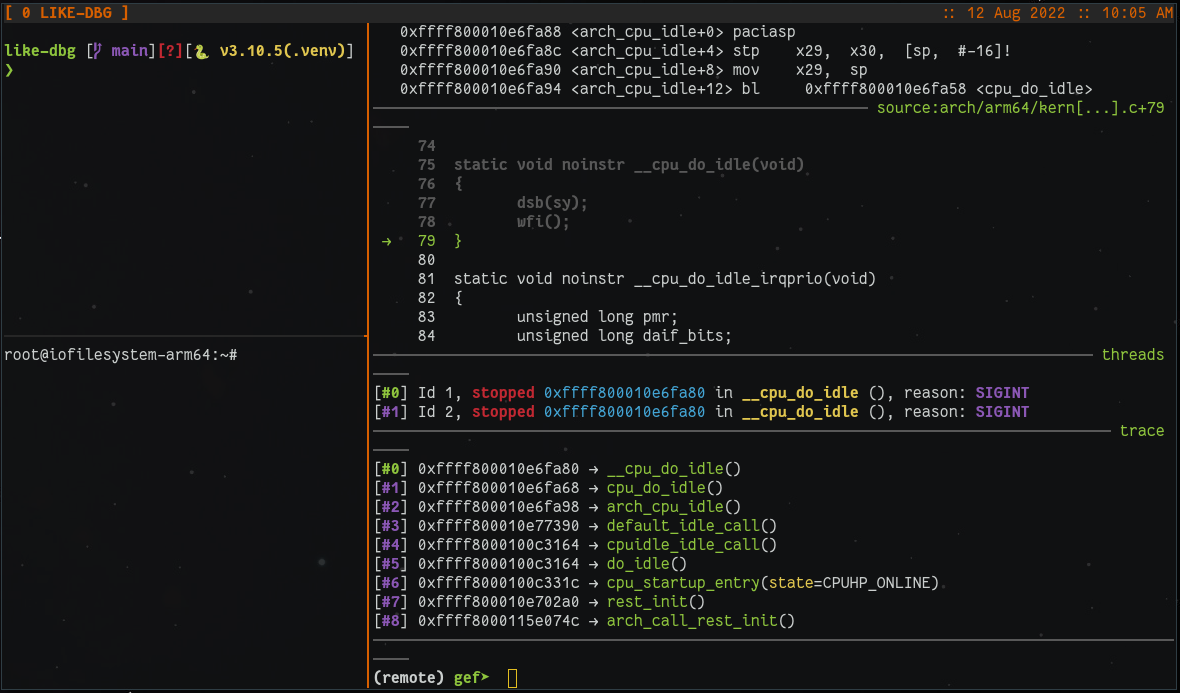 0xricksanchez/like-dbg
Fully dockerized Linux kernel debugging environment
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
 sgkdev/page_inject
CVE-2026-31431-killed page-cache exploit — code exec into containers sharing the same image layer
 ifpdz/cve-2025-24104
Technical writeup of CVE-2025-24104: an iOS sandbox escape via symlink validation bypass in backup restoration, enabling arbitrary file reads outside…
 0xbinder/android-kernel-exploitation-lab
This lab guides you through setting up an environment to explore CVE-2019-2215, a critical Android kernel vulnerability in the binder subsystem.
 chenaotian/cve-2022-0185
CVE-2022-0185 POC and Docker and Analysis write up
 xeloxa/copyfail-exploit
Copy Fail (CVE-2026-31431) LPE exploit. A clean, multi-arch Python reimplementation targeting the Linux kernel AF_ALG page cache vulnerability.
 baeseungwon1010/cve-2023-4911
CVE-2023-4911 (Looney Tunables) analysis report and Docker reproduction lab
 krleejihyeong/whs4_cve-2021-4034
Educational PoC and analysis of CVE-2021-4034 (PwnKit) local privilege escalation vulnerability in polkit's pkexec, with a Docker-based lab for…
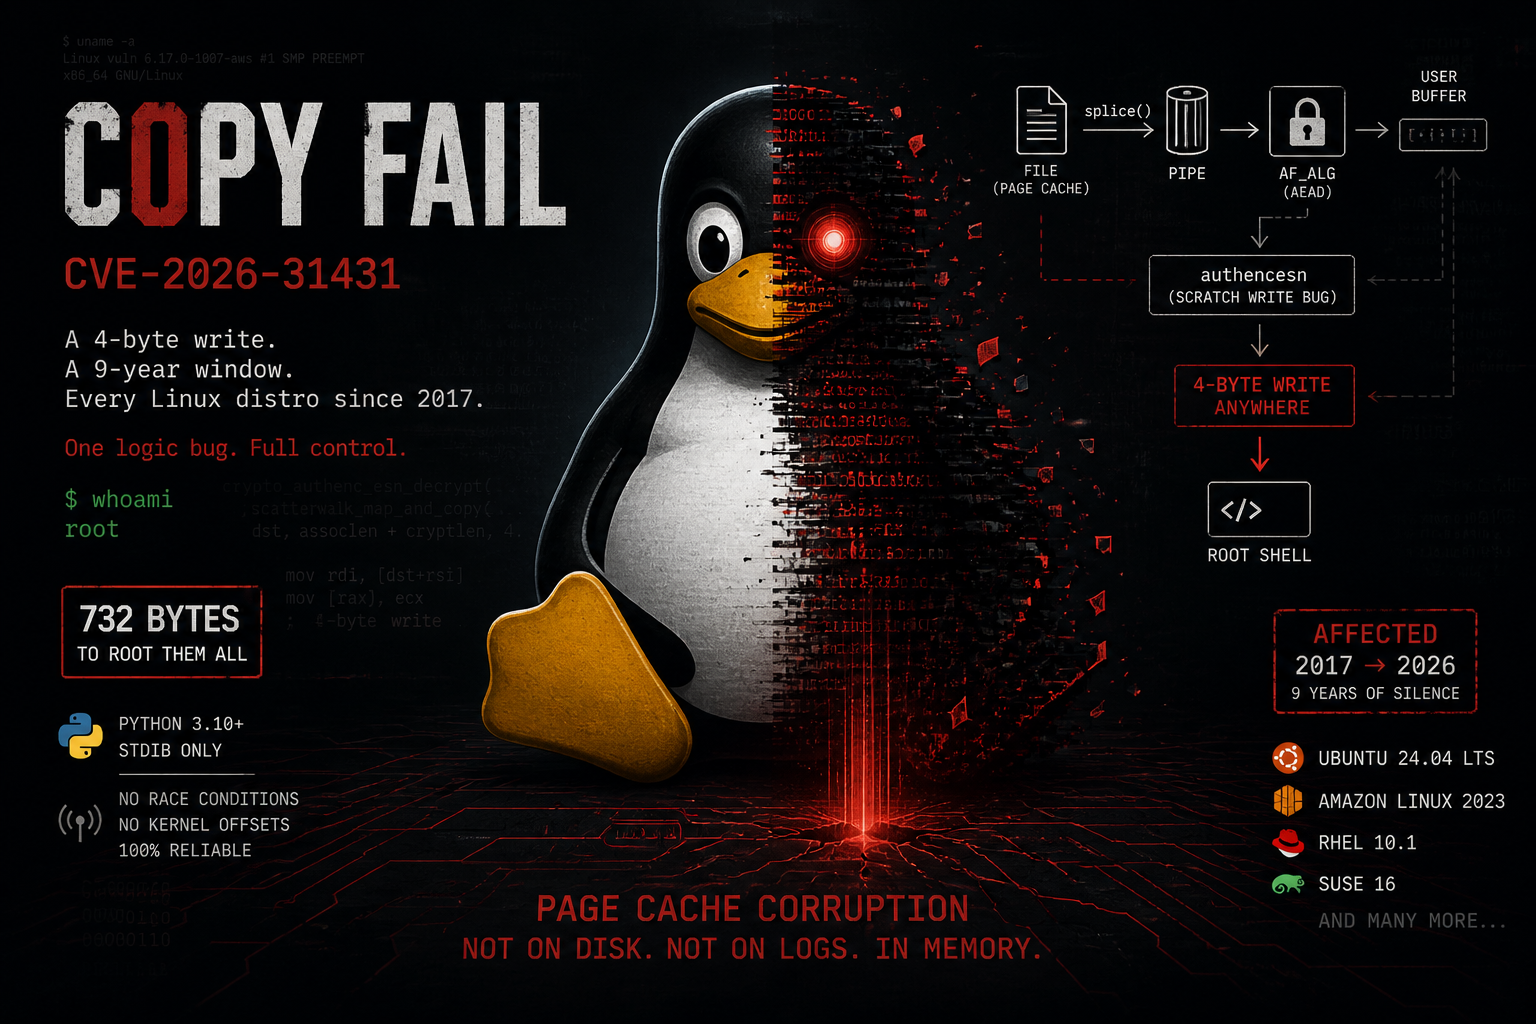 themalwareguardian/cve-2026-31431
A structured explanation of CVE-2026-31431 (Copy Fail), connecting the three kernel changes that introduced the vulnerability and enabled its…
 gr-1m/cve-2026-31431
Golang rewrite of the Copy Fail (CVE-2026-31431) local privilege escalation exploit, corrupting page cache to gain root on Linux systems.
 giverofgifts/cve-2019-5736-custom-runtime
CVE-2019-5736 implemented in a self-written container runtime to understand the exploit.
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 hanakim3945/bl_sbx
itunesstored & bookassetd sbx escape