
CVE-2025-5548
 javyan05/cve-2025-5548
Entorno y explotación de la vulnerabilidad CVE-2025-5548
binary-exploitationdebuggerseducation+6
javyan05/cve-2025-5548Entorno y explotación de la vulnerabilidad CVE-2025-5548
 ismaelcosma/cve-2025-8088
Python-based exploit generator for CVE-2025-8088 in WinRAR, crafting malicious RAR archives that execute payloads upon extraction for authorized…
 anasrami12/cve-2025-5548
Methodology for vulnerability analysis and exploit development, covering static/dynamic analysis, fuzzing, patch diffing, and 0-day research with…
 h4xl0r/winrar_ace_exploit_cve-2018-20250
This program is an script developed in Python which exploit the ACE vulnerability on WinRar - Vulnerability CVE-2018-20250
 mrk336/cve-2025-27480
CVE-2025-27480 exposes a buffer overflow in OpenSSH 8.9p1 via a malformed SSH_USERAUTH packet. Attackers can inject shellcode and gain SYSTEM-level…
 mrk336/cve-2025-27480-the-silent-gateway-risk
Letting attackers run malicious code without needing a cracked password, user interaction, or even a foothold in your network. That’s CVE-2025-27480
 murdok1982/exploit-en-python-para-cve-2023-4147
PoC educativo del exploit CVE-2023-4147 (Linux kernel Netfilter UAF) — solo para entornos autorizados
 zeppperoni/cve-2015-1578
Achat 0.150 beta7 - Remote Buffer Overflow Rewrite for python3 for the PNPT course.
 ch4rli3kop/cve-2020-12928
Proof-of-concept privilege escalation exploit for CVE-2020-12928 targeting AMD RyzenMaster driver, demonstrating local privilege escalation via…
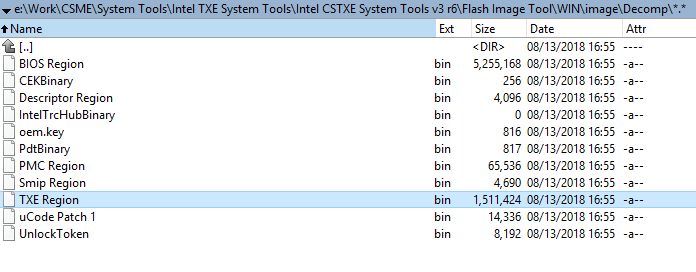 ptresearch/inteltxe-poc
Intel Management Engine JTAG Proof of Concept
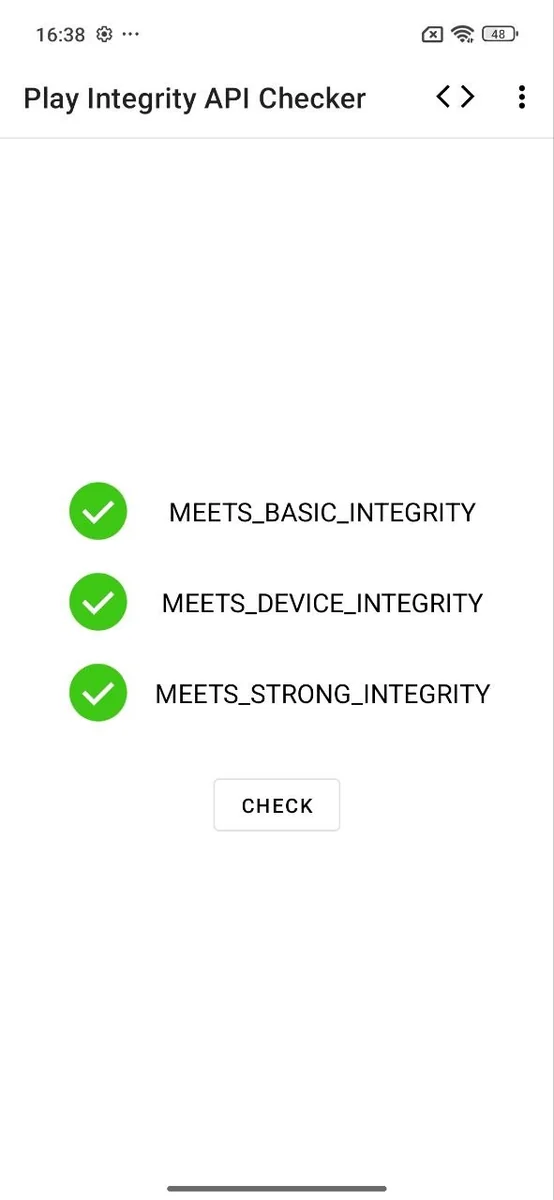 aniketlab/poco-m7-plus-jailbreak
Temporary Root Research on Poco M7 Plus (SM6375) via Qualcomm GBL Exploit (CVE-2026-24088) + GhostLock Kernel Analysis (CVE-2026-43499)
 wonjj6768/lenovo-tb365fc-ghostlock-cve-2026-43499
GhostLock (CVE-2026-43499) root + KernelSU LKM for the Lenovo TB365FC (ZUXOS / Android 16, kernel 5.15.170)