
OffensiveNim
 byt3bl33d3r/offensivenim
My experiments in weaponizing Nim (https://nim-lang.org/)
binary-exploitationcode-analysiscommand-and-control+8
3.1k2 years ago
byt3bl33d3r/offensivenimMy experiments in weaponizing Nim (https://nim-lang.org/)
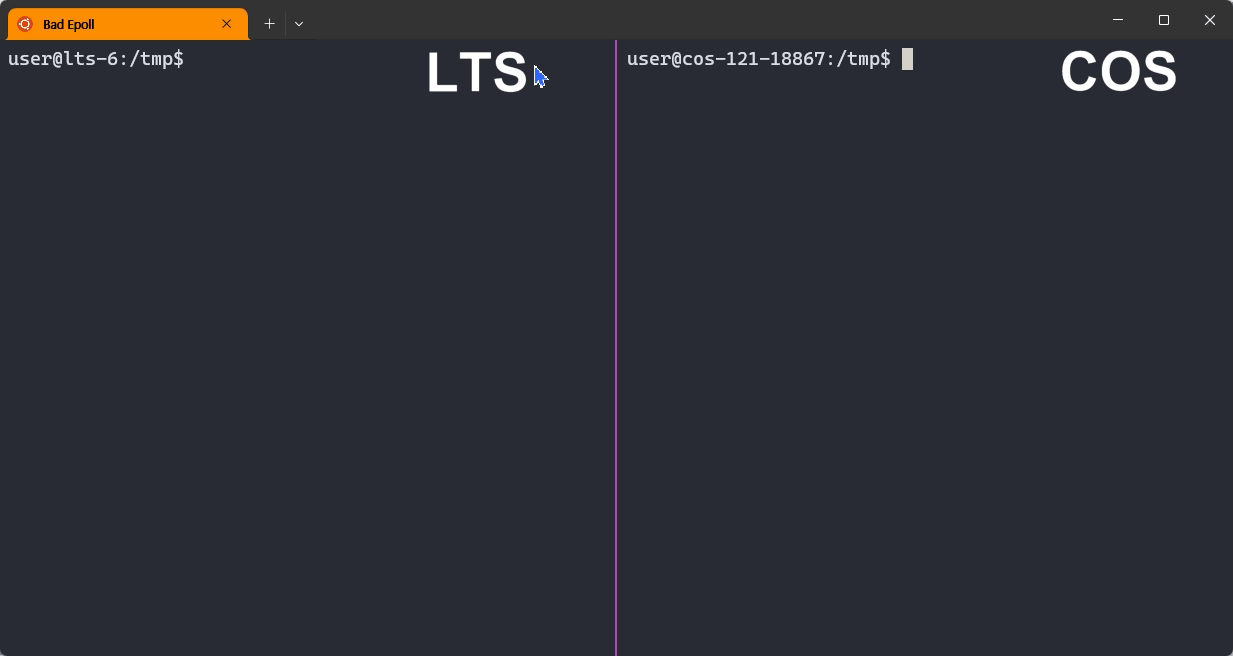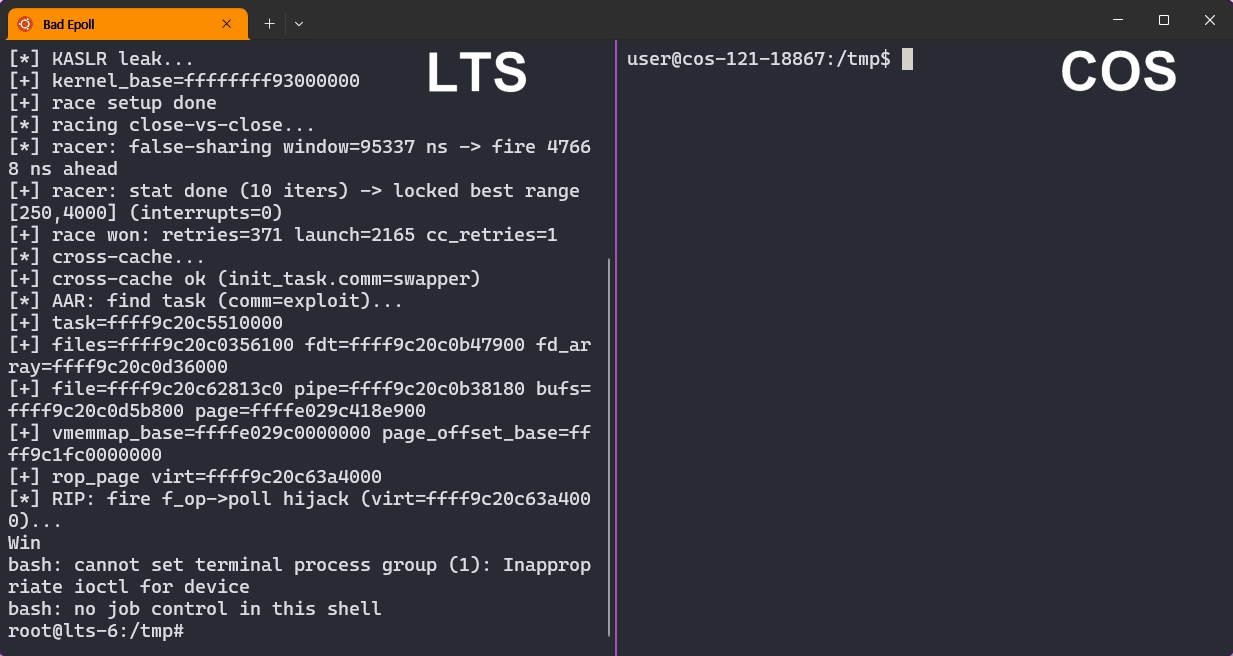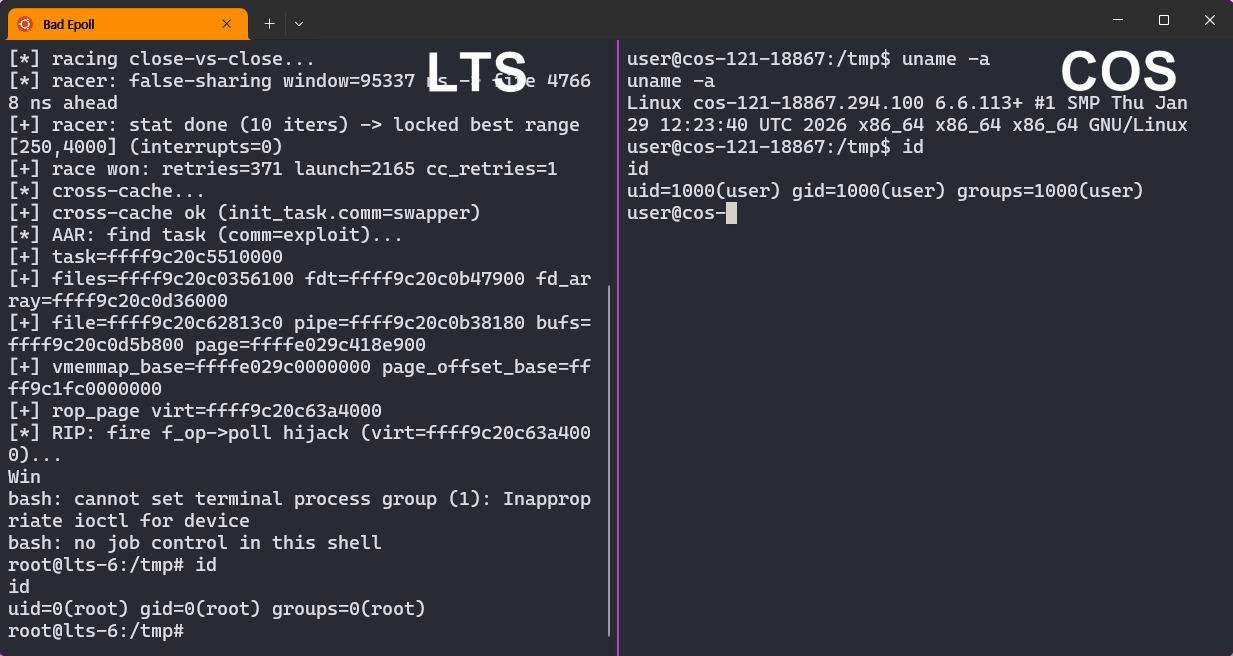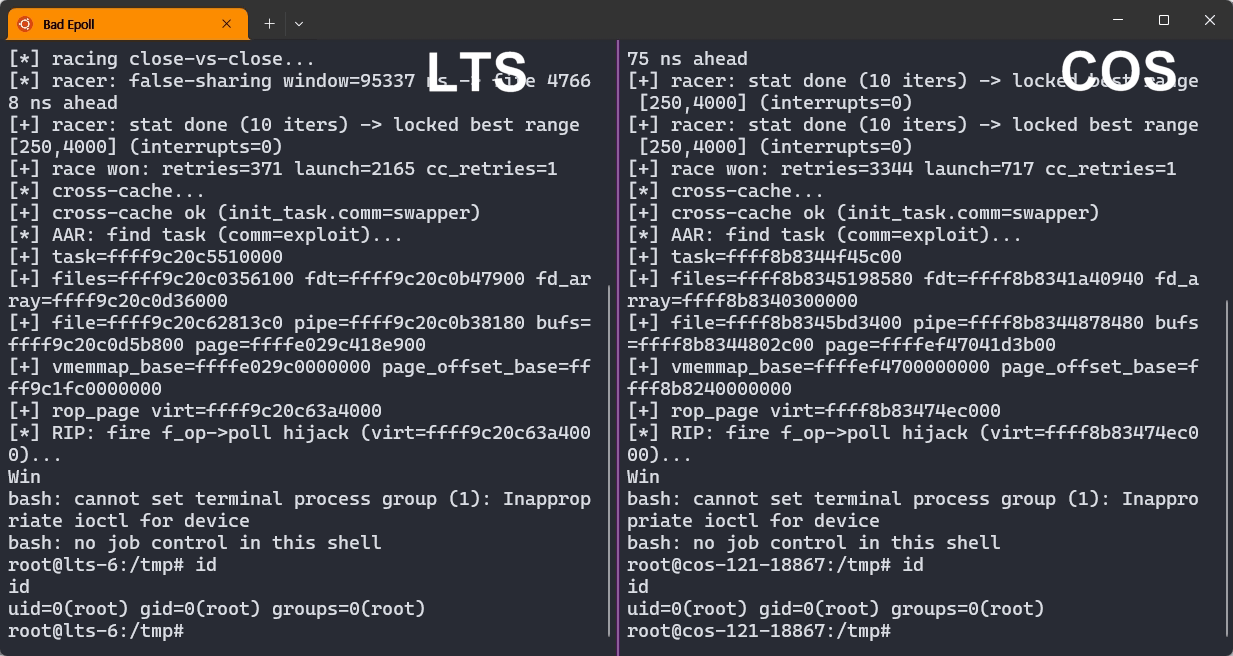 j-jaeyoung/bad-epoll
Linux kernel privilege-escalation exploit for CVE-2026-46242, a race-condition use-after-free in epoll, with 99% reliable root on desktops, servers,…
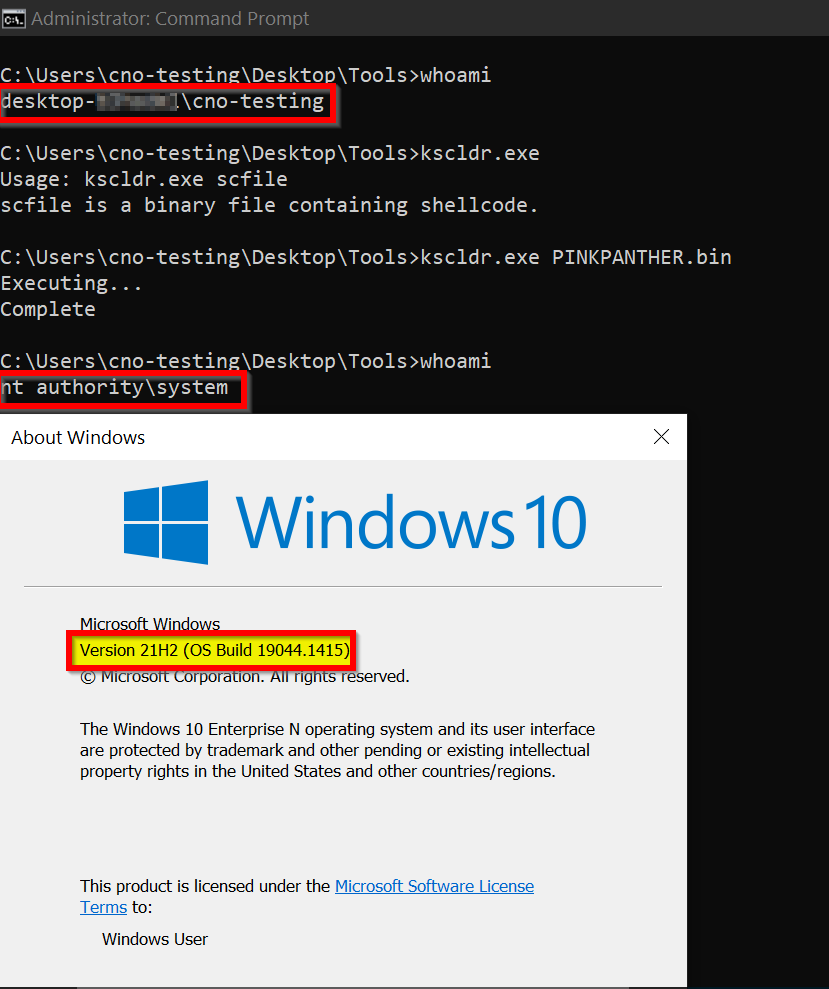 winterknife/pinkpanther
Windows x64 handcrafted token stealing kernel-mode shellcode
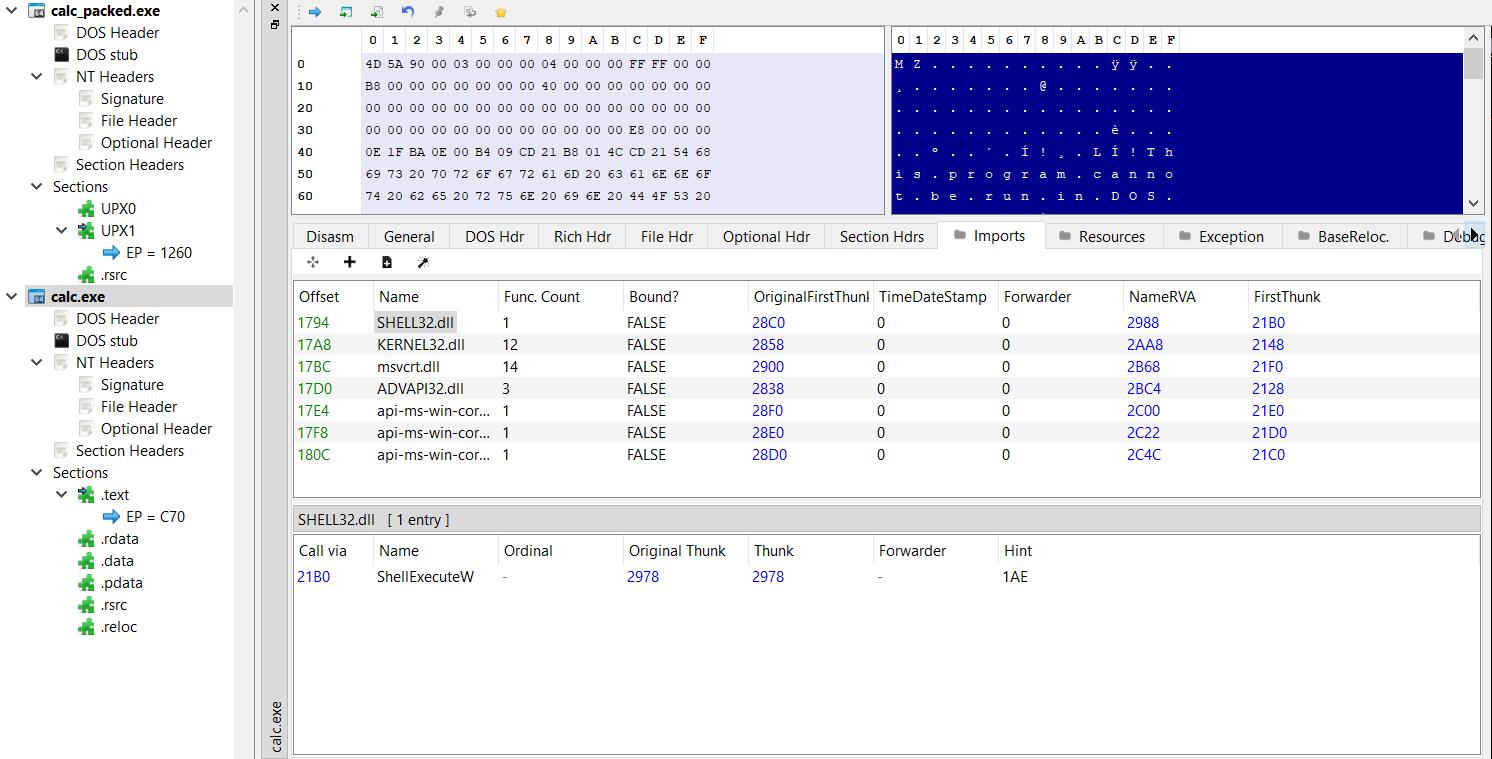 senzee1984/inflativeloading
Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.
 ustayready/wnfexec
WNF Code Execution Library Using C#
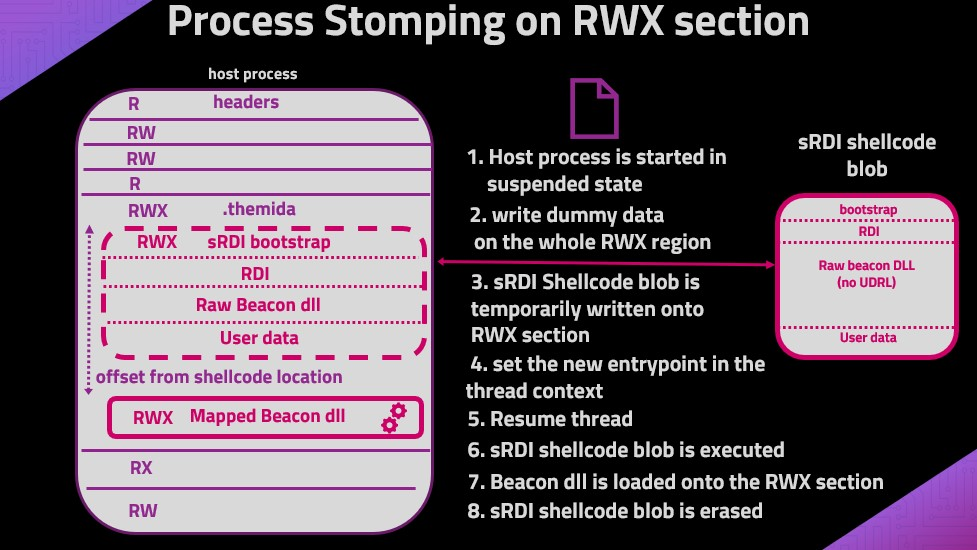 naksyn/processstomping
A variation of ProcessOverwriting to execute shellcode on an executable's section
 iilegacyyii/datainject-bof
Hijacks code execution via overwriting Control Flow Guard pointers in combase.dll
 klezvirus/rpcproxyinvoke
Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar
 bazad/launchd-portrep
CVE-2018-4280: Mach port replacement vulnerability in launchd on macOS 10.13.5 leading to local privilege escalation and SIP bypass.
 kaist-hacking/cve-2023-6702
Chrome Renderer 1day RCE via Type Confusion in Async Stack Trace (v8ctf submission)
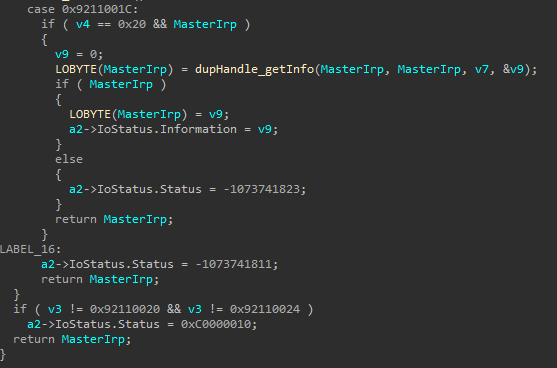 alfarom256/logmeinpochandledup
Exploit for a LogMeIn/GoTo Windows kernel driver race condition that duplicates SYSTEM handles, enabling thread-token impersonation and local…
 infobyte/exploit-cve-2021-21086
Python-based exploit for CVE-2021-21086 in Adobe Acrobat Reader DC, generating malicious PDFs with shellcode execution via crafted font charstrings.
 blacksnufkin/credshunter
PoC for CVE-2026-3609 - XIGNCODE3 xhunter1.sys handle leak enabling PPL bypass and LSASS dumping
 badmonkey7/cve-2021-34730
Cisco RV110w UPnP stack overflow
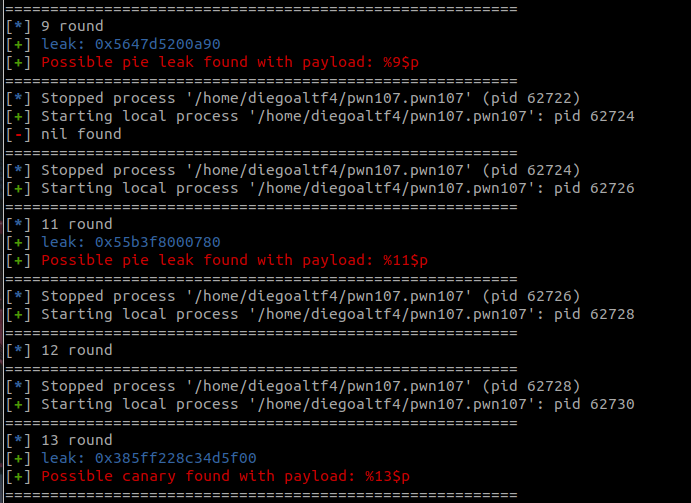 diego-altf4/glufs
Automated format string vulnerability exploitation tool for discovering stack, PIE, and canary leaks with flag search capability via %s or %p…
 3tternp/cve-2023-21554
Python proof-of-concept for CVE-2023-21554 targeting Windows Message Queuing; crashes mqsvc.exe to demonstrate the vulnerability.
 aydinnyunus/cve-2024-24576-exploit
CVE-2024-24576 Proof of Concept