
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-46333 — CVE-2026-46333 | Kitploit
Tools/GitHubGitHub/0xblackash/cve-2026-46333
Privilege EscalationVulnerability AnalysisExploitationInformation GatheringPenetration TestingLearning & EducationBinary Exploitation
GitHub0xblackash/cve-2026-46333

CVE-2026-46333

CVE-2026-46333

View Repository
3812326 months agoReviewed by Kitploit
Share

🚀 CVE-2026-46333 - ssh-keysign-pwn

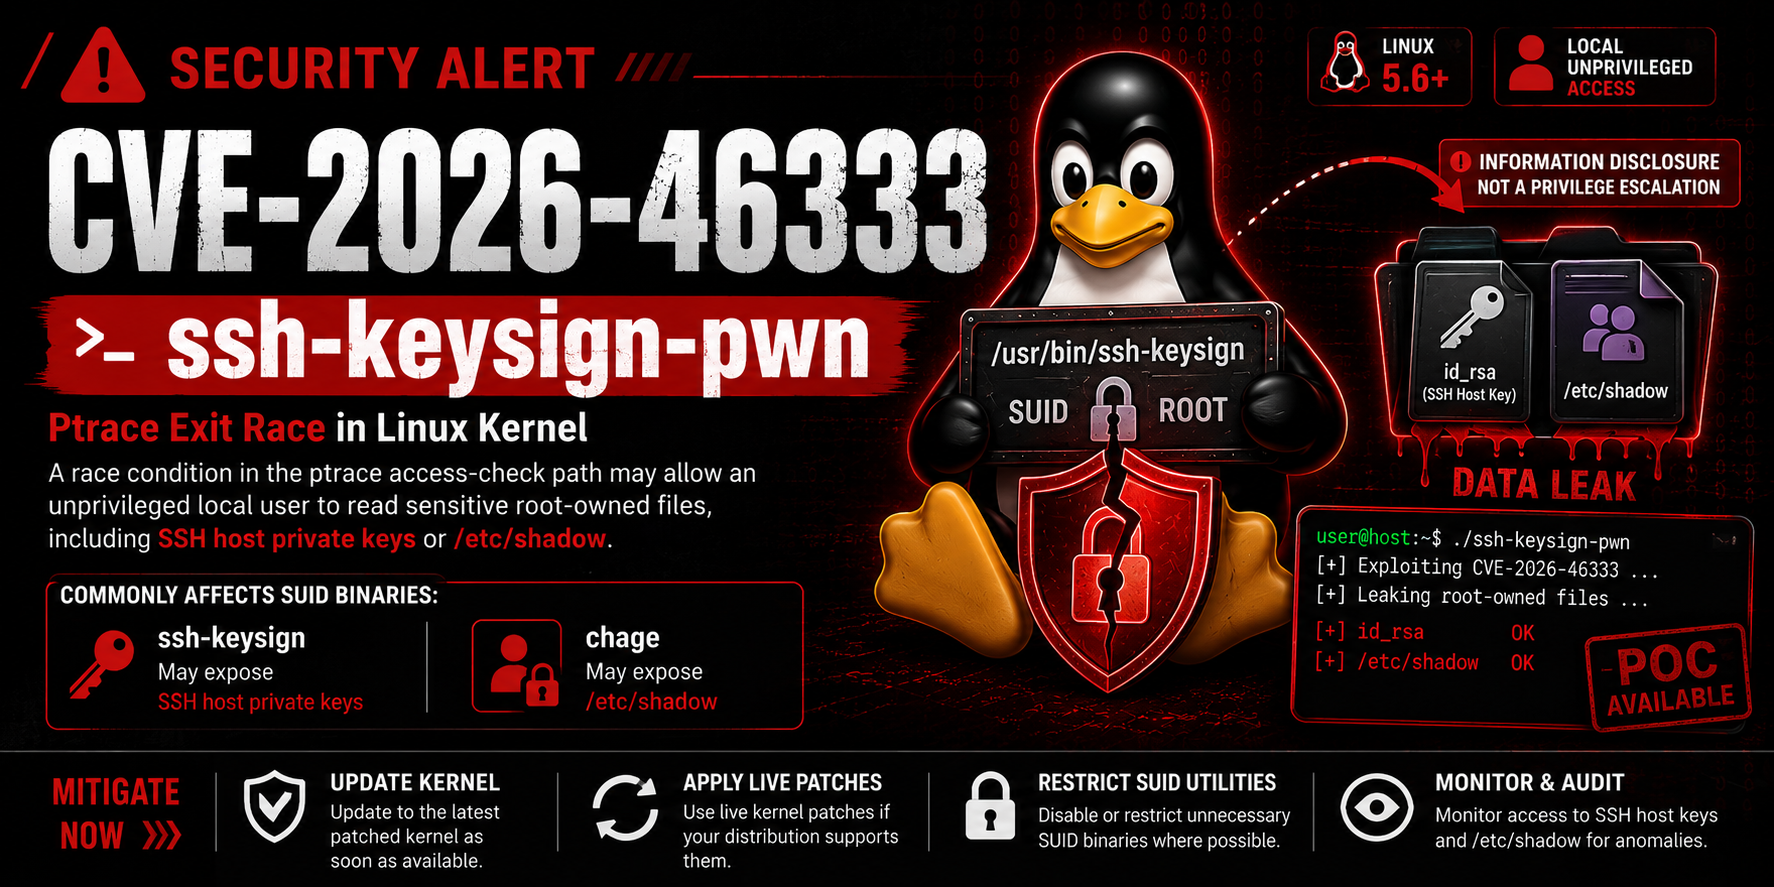
ChatGPT Image May 17, 2026, 11_32_19 AM

High-quality Proof of Concept for the Linux kernel race condition vulnerability

Linux Kernel Exploit License

A clean and reliable proof-of-concept exploit for CVE-2026-46333 — Local information disclosure via race condition in the Linux kernel's process exit path.


🖼️ Screenshot

CVE-2026-46333

Successfully stealing SSH host private key and /etc/shadow on Kali Linux


📌 About the Vulnerability

CVE-2026-46333 (also known as ssh-keysign-pwn) is a race condition in the Linux kernel's ptrace and process exit logic (do_exit() → exit_mm() before exit_files()).

When a privileged process (e.g. SUID ssh-keysign or chage) has mm == NULL during exit, the dumpability check is bypassed, allowing an unprivileged local attacker to use pidfd_getfd() to steal open file descriptors.

Impact:

  • Steal SSH host private keys (/etc/ssh/ssh_host_*_key)
  • Dump /etc/shadow
  • Potential for further attacks using stolen credentials

Discovered by: Qualys
Fixed in: Kernel commit 31e62c2ebbfdc3fe3dbdf5e02c92a9dc67087a3a (May 2026)


✨ Features

  • Original clean code (not copied from existing repos)
  • High success rate
  • Two working exploits:
    • SSH Host Private Key Stealer
    • /etc/shadow Stealer via chage
  • Clean output with progress feedback
  • No external dependencies
  • Well commented

🛠️ Usage

1. Clone & Build

git clone https://github.com/0xBlackash/CVE-2026-46333.git
cd CVE-2026-46333

2. Run SSH Host Key Exploit

sudo ./CVE-2026-46333

3. Run Shadow File Exploit

sudo ./CVE-2026-46333-shadow

📂 Files

FileDescription
cve-2026-46333.cSSH host private keys stealer
cve-2026-46333-shadow.c/etc/shadow stealer via chage
README.mdThis file

📖 Example Output

SSH Key Stealer:

[+] SUCCESS! Stolen fd 3 -> /etc/ssh/ssh_host_ecdsa_key (round 0)
-----BEGIN OPENSSH PRIVATE KEY-----
b3BlbnNzaC1rZXktdjEAAAAABG5vbmUAAAAEbm9uZQAAAAAAAAAB...

Shadow Stealer:

[+] SUCCESS! Stolen /etc/shadow (round 0)
root:*:19953:0:99999:7:::
kali:$y$j9T$zY1oKFxJlTgP2WcJhzbNl1$...

🛡️ Mitigation

  • Update your kernel to any version containing commit 31e62c2ebbfd...
  • Recommended: Use latest stable kernel from your distribution
  • Disable EnableSSHKeysign in sshd_config if not needed

⚠️ Legal Disclaimer

This exploit is for educational and security research purposes only.
Use it only on systems you own or have explicit written permission to test.
The author is not responsible for any misuse or damage.


⭐ Credits

  • Vulnerability: Qualys
  • PoC Development: Ashraf Zaryouh ""0xBlackash""
  • Original Research: Various kernel researchers

📜 License

This project is licensed under the MIT License — feel free to use, modify, and distribute.


Made with ❤️ for the security community

Keeping systems updated is the best defense.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    576
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    477
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    388
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    330
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    255
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    247

Explore all tools

Browse our collection of tools

View all tools →