
DirtyPipe-CVE-2022-0847
 vinukalana/dirtypipe-cve-2022-0847
This repository is developed to analysis and understand DirtyPipe exploit CVE-2022-0847
binary-exploitationeducationexploitation+3
2
vinukalana/dirtypipe-cve-2022-0847This repository is developed to analysis and understand DirtyPipe exploit CVE-2022-0847
 hessandrew/cve-2020-13885
Citrix Workspace app before 1912 for Windows - Privilege Escalation #1
 themalwareguardian/cve-2020-13768
Stack-based buffer overflow in MiniShare 1.4.1 reachable through a single HTTP PUT request.
 themalwareguardian/cve-2025-34096
SEH-based buffer overflow in Easy File Sharing Web Server 7.2, reachable through the password recovery endpoint.
 rippsec/cve-2025-27591-meta-below-lpe
CVE-2025-27591 – Meta below symlink following local privilege escalation (HackTheBox CTF)
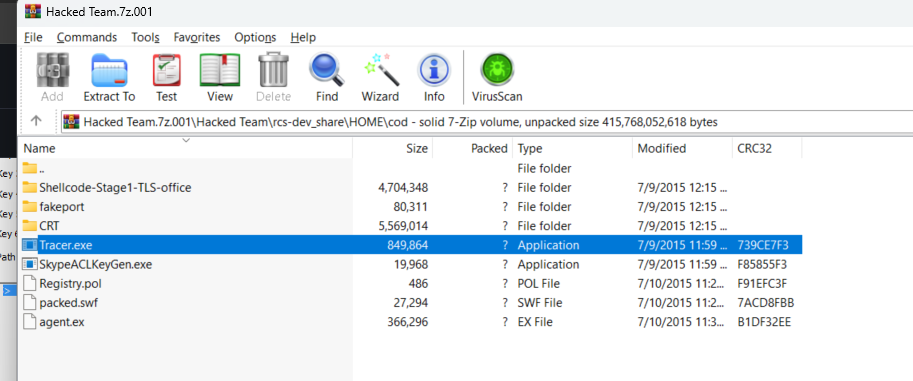 spiralbl0ck/skypeaclkeygen.exe-analysis-for-hacking-team
SkypeACLKeyGen.exe analysis for hacking team
 fath0218/cve-2016-2233
Step-by-step guide to exploiting a stack-based buffer overflow in HexChat (CVE-2016-2233) with a malicious IRC server, including a patch to fix the…
 oliviaisntcringe/cve-2025-30216-poc
PoC
 antisecc/cve-2022-23935
Exploit for CVE-2022-23935, a command injection vulnerability in Exiftool versions prior to 12.38, allowing arbitrary command execution via crafted…
 bhathiya404/exploiting-stagefright-vulnerability-cve-2015-3864
Exploit implementation for Android Stagefright vulnerability CVE-2015-3864, enabling remote code execution and privilege escalation on Android 5.1.1…
 z00z00z00/safenet_sac_cve-2021-42056
Safenet Authentication Client Privilege Escalation - CVE-2021-42056
 0xkickit/icue_dllhijack_lpe-cve-2024-22002
Proof-of-concept exploit for CVE-2024-22002, demonstrating local privilege escalation via DLL hijacking in CORSAIR iCUE's update service to run code…
 hfiref0x/kdu
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
 secretsquirrel/the-backdoor-factory
Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors
 a0rtega/metame
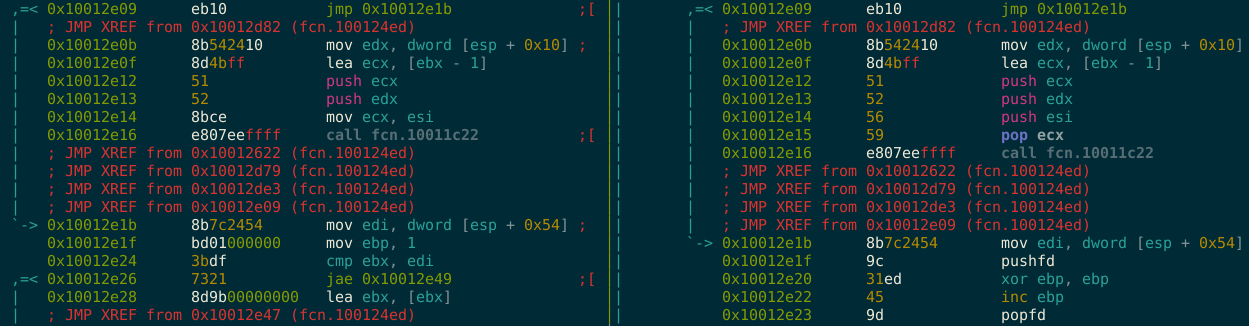
metame is a metamorphic code engine for arbitrary executables
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 ubfx/bindiffhelper
Ghidra Extension to integrate BinDiff for function matching
 s3cur3th1ssh1t/nim-runpe
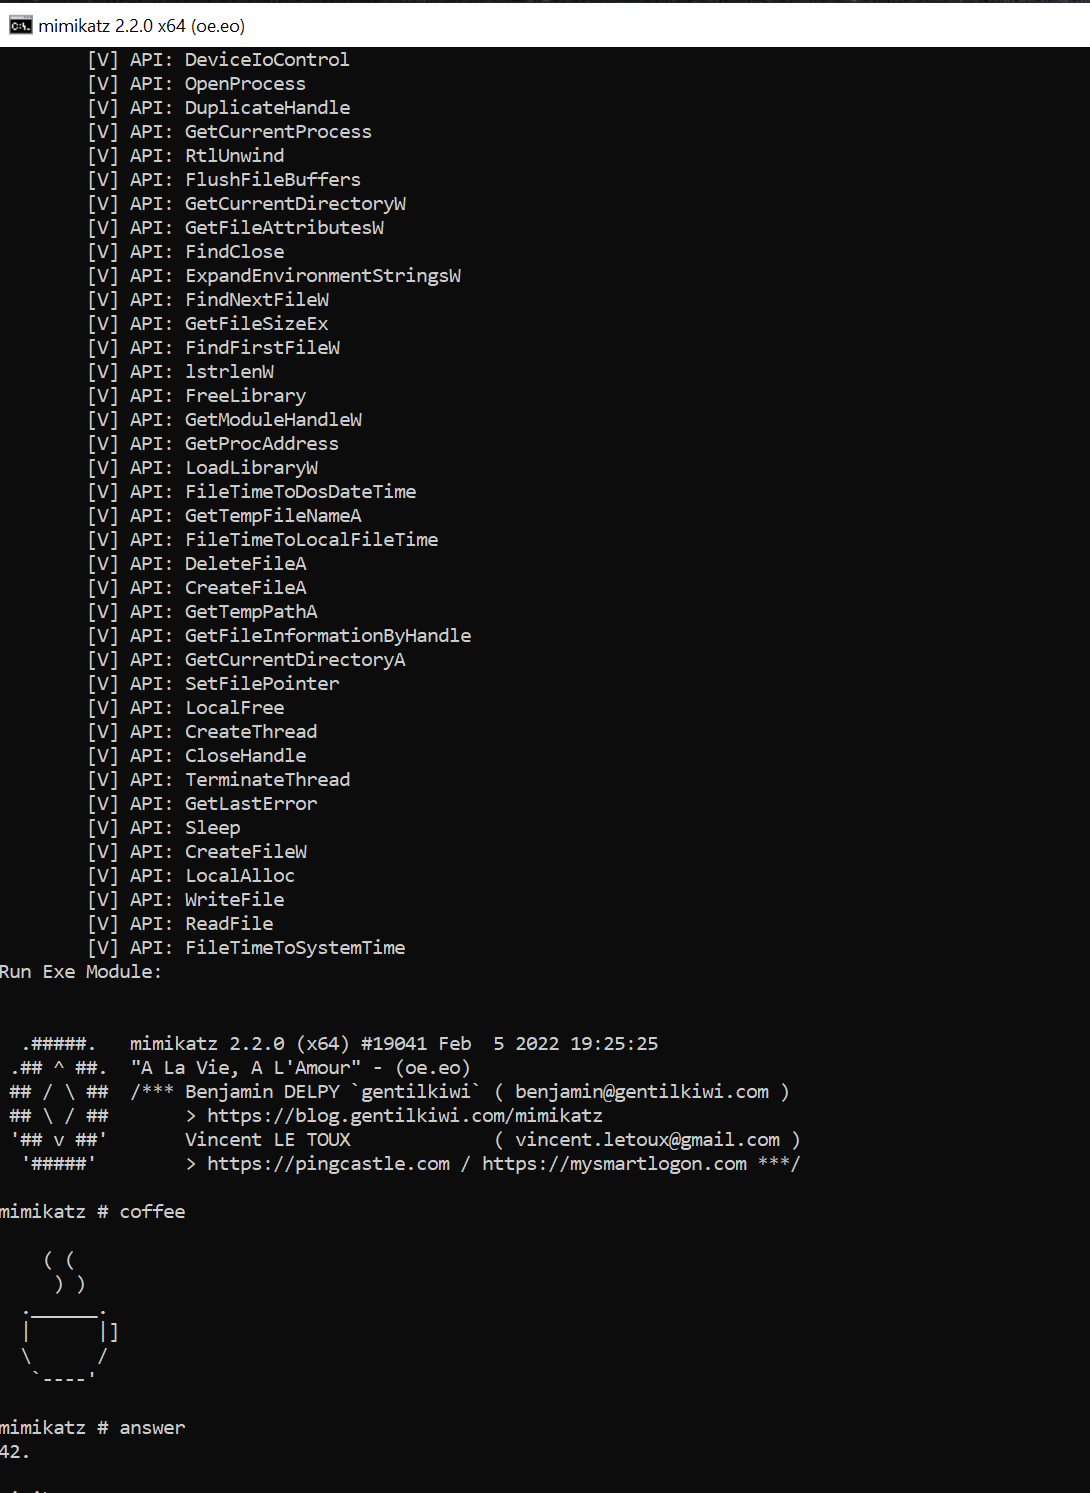
A Nim implementation of reflective PE-Loading from memory