
CVE-2023-38831
 idkwastaken/cve-2023-38831
Exploit code for CVE-2023-38831, a WinRAR vulnerability enabling remote code execution via crafted archive files. Designed for penetration testing…
binary-exploitationexploitationpayload-generation+2
idkwastaken/cve-2023-38831Exploit code for CVE-2023-38831, a WinRAR vulnerability enabling remote code execution via crafted archive files. Designed for penetration testing…
 1nteger-c/cve-2019-8605
C-language proof-of-concept implementation targeting CVE-2019-8605; intended for security research, validation, and defensive testing.
 neodarwin/cve-2020-27955
CVE-2020-27955 Poc
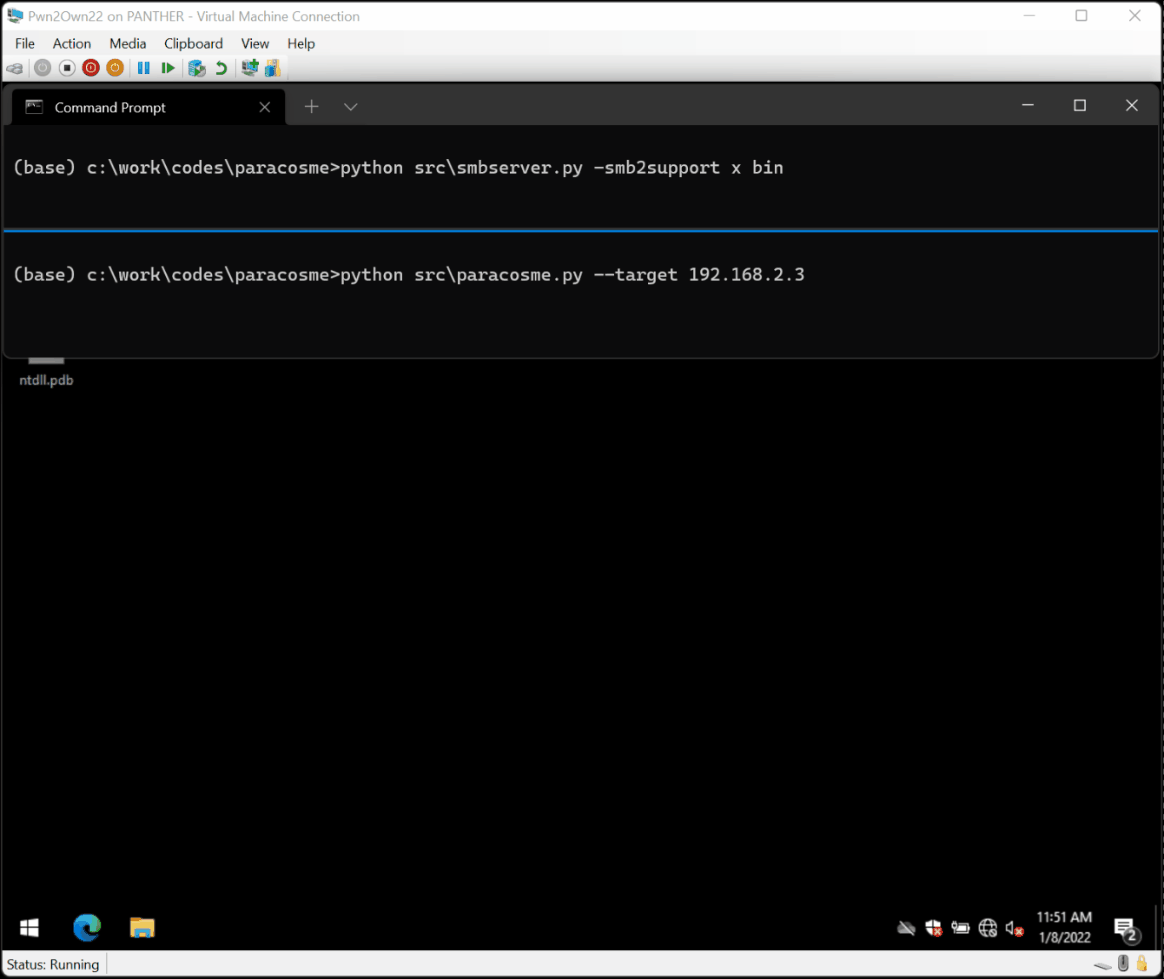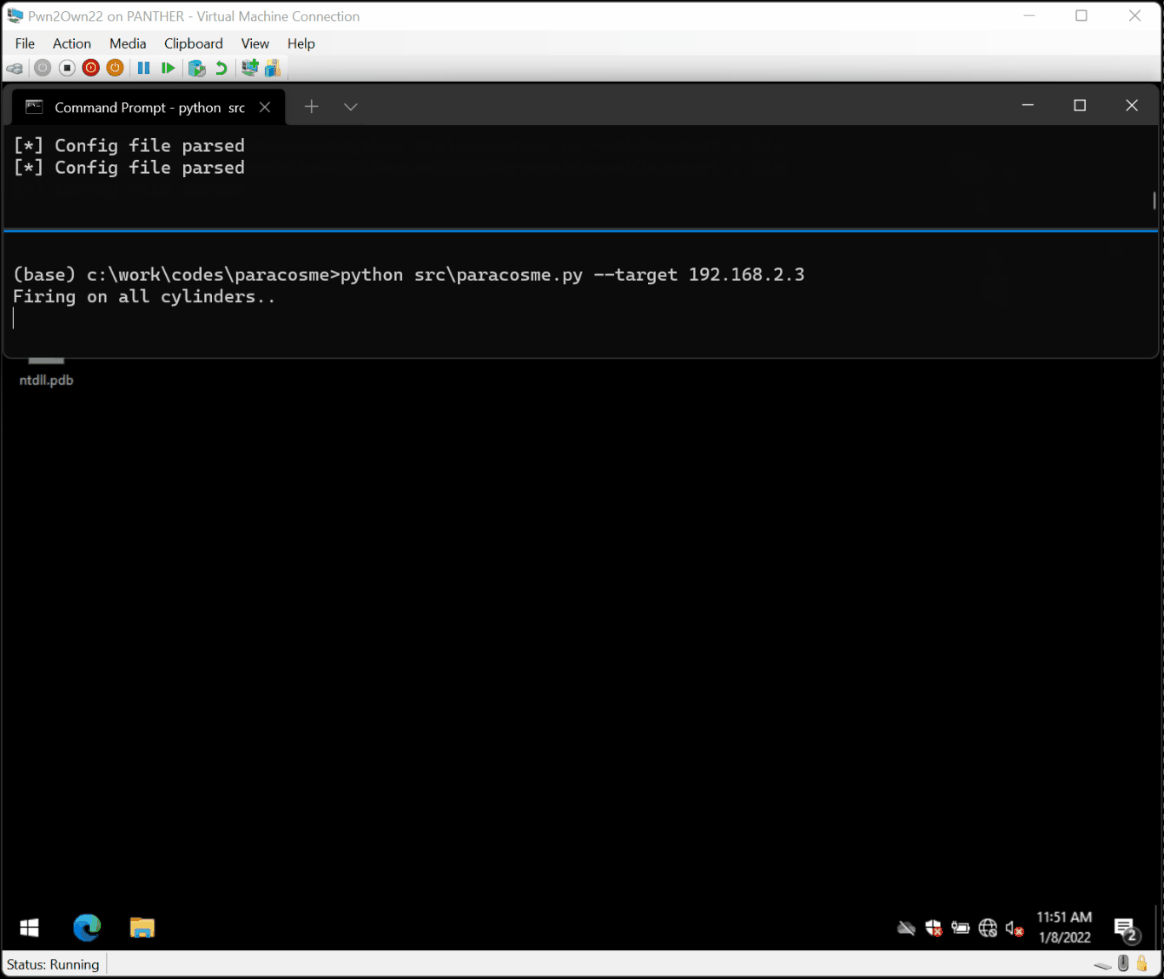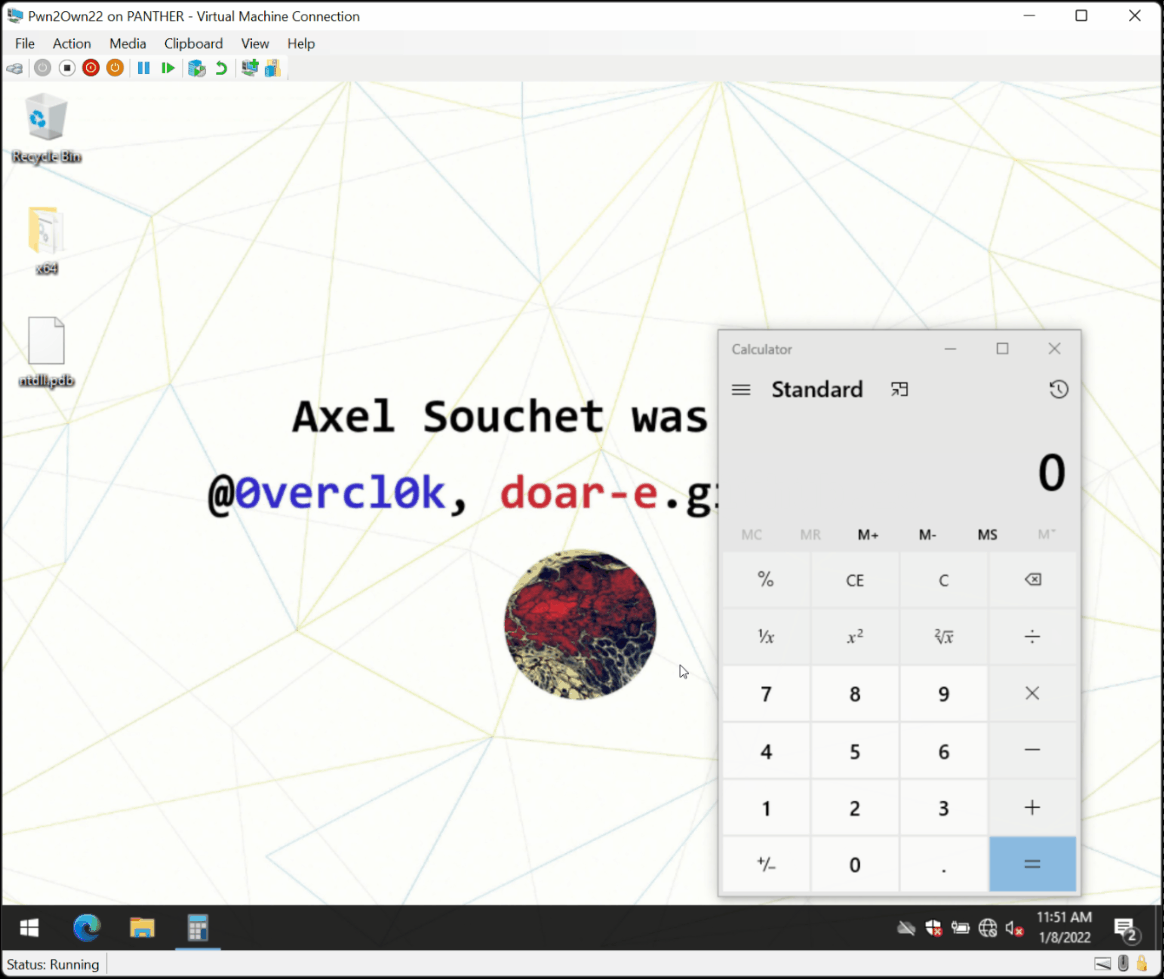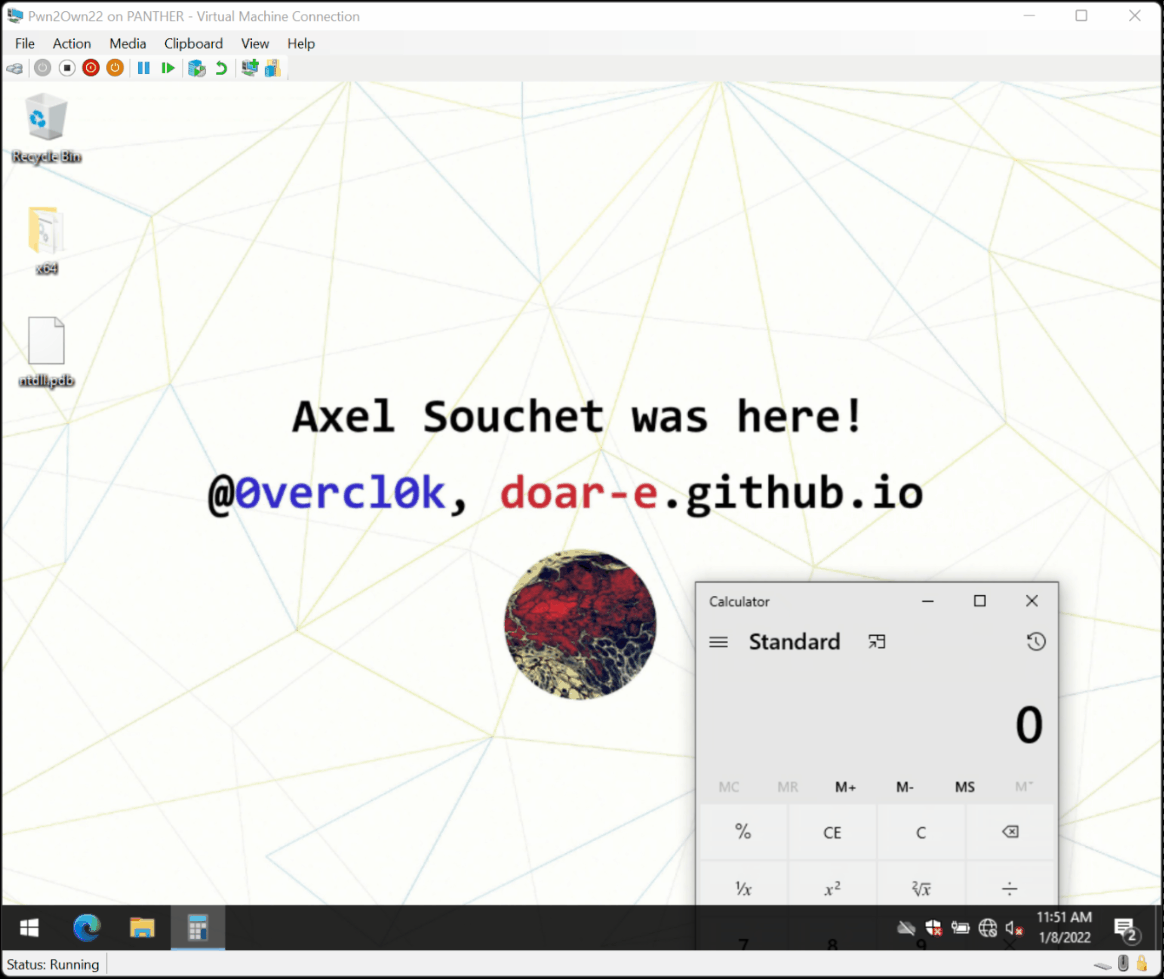 0vercl0k/paracosme
Paracosme is a zero-click remote memory corruption exploit that compromises ICONICS Genesis64 which was demonstrated successfully on stage during the…

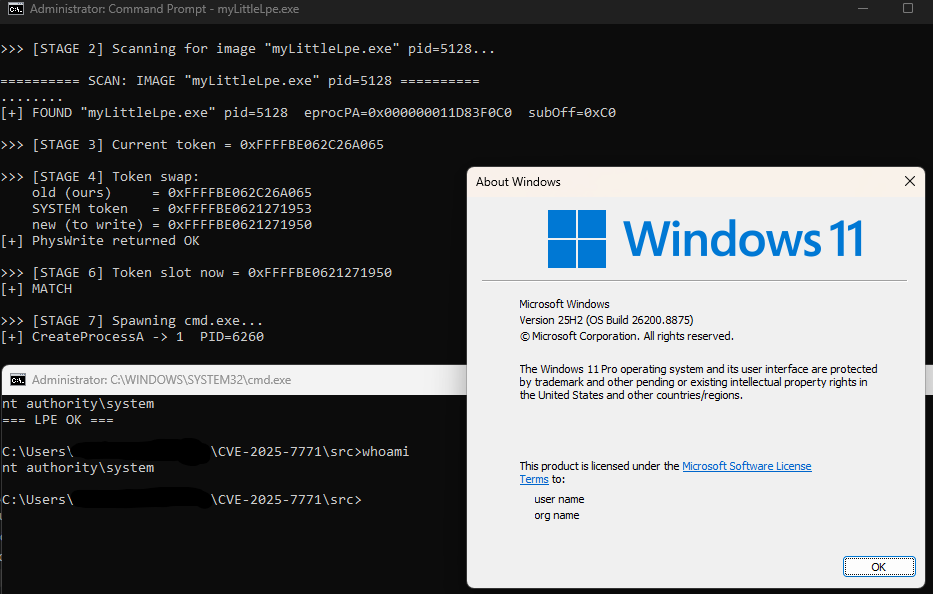 yulisec/cve-2025-7771
Full exploit chain for CVE-2025-7771 in ThrottleStop.sys, abusing unvalidated physical memory R/W IOCTLs to escalate from administrator to SYSTEM on…
 damariion/cve-2015-1925.rce
Stack-based buffer overflow in the server in IBM Tivoli Storage Manager FastBack 6.1 before 6.1.12 allows remote attackers to cause a denial of…
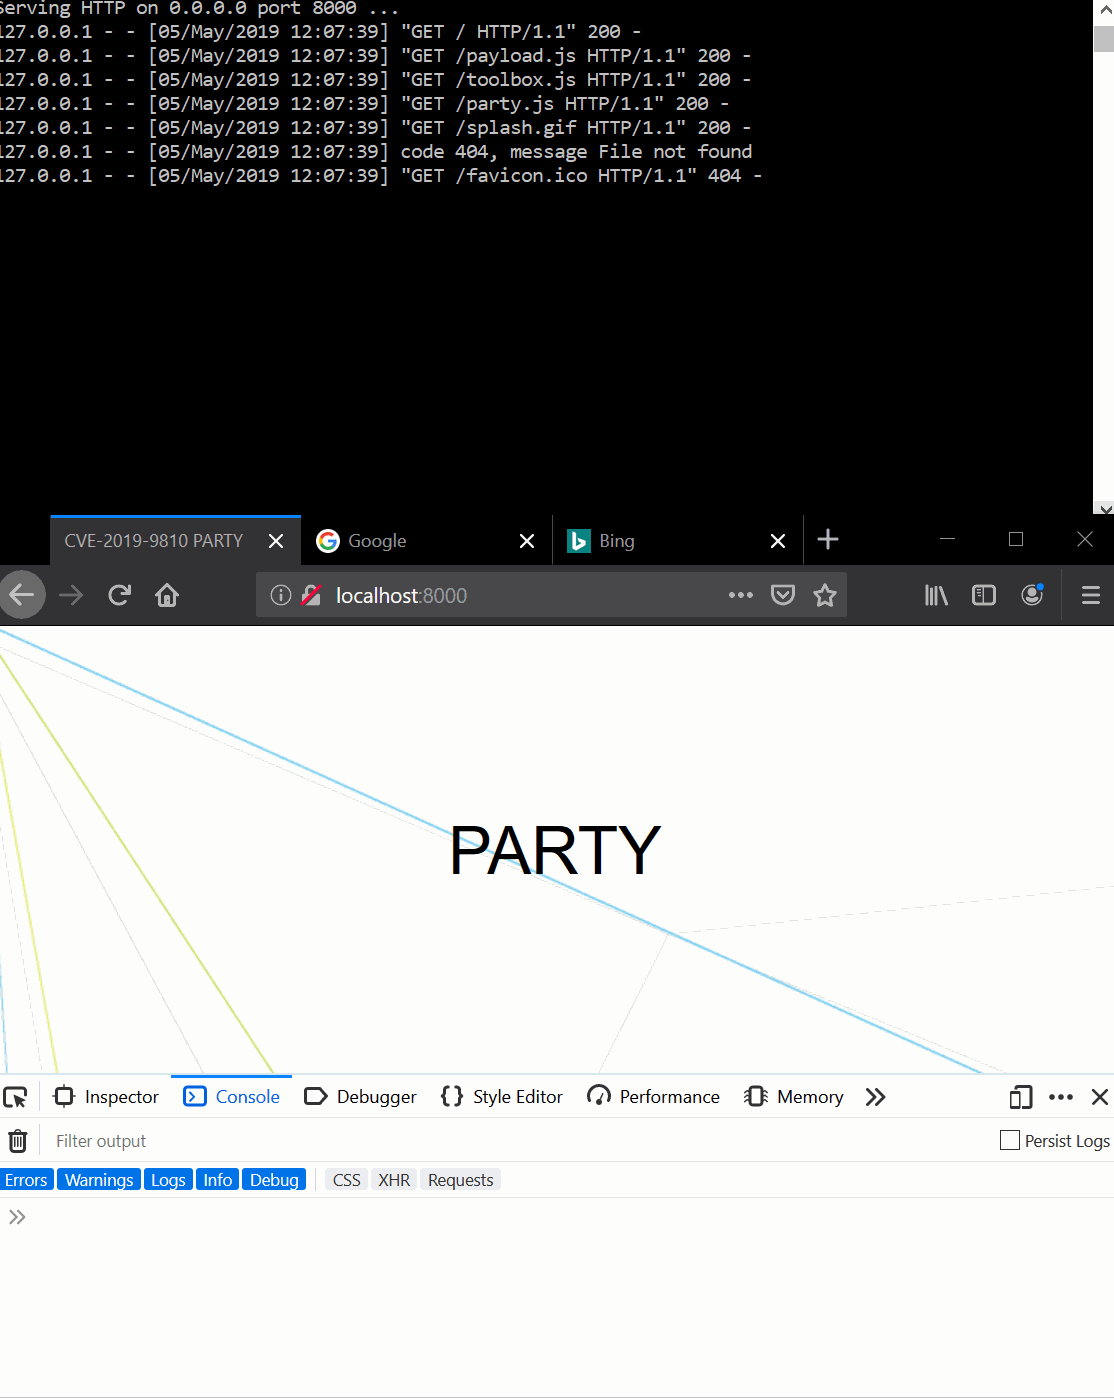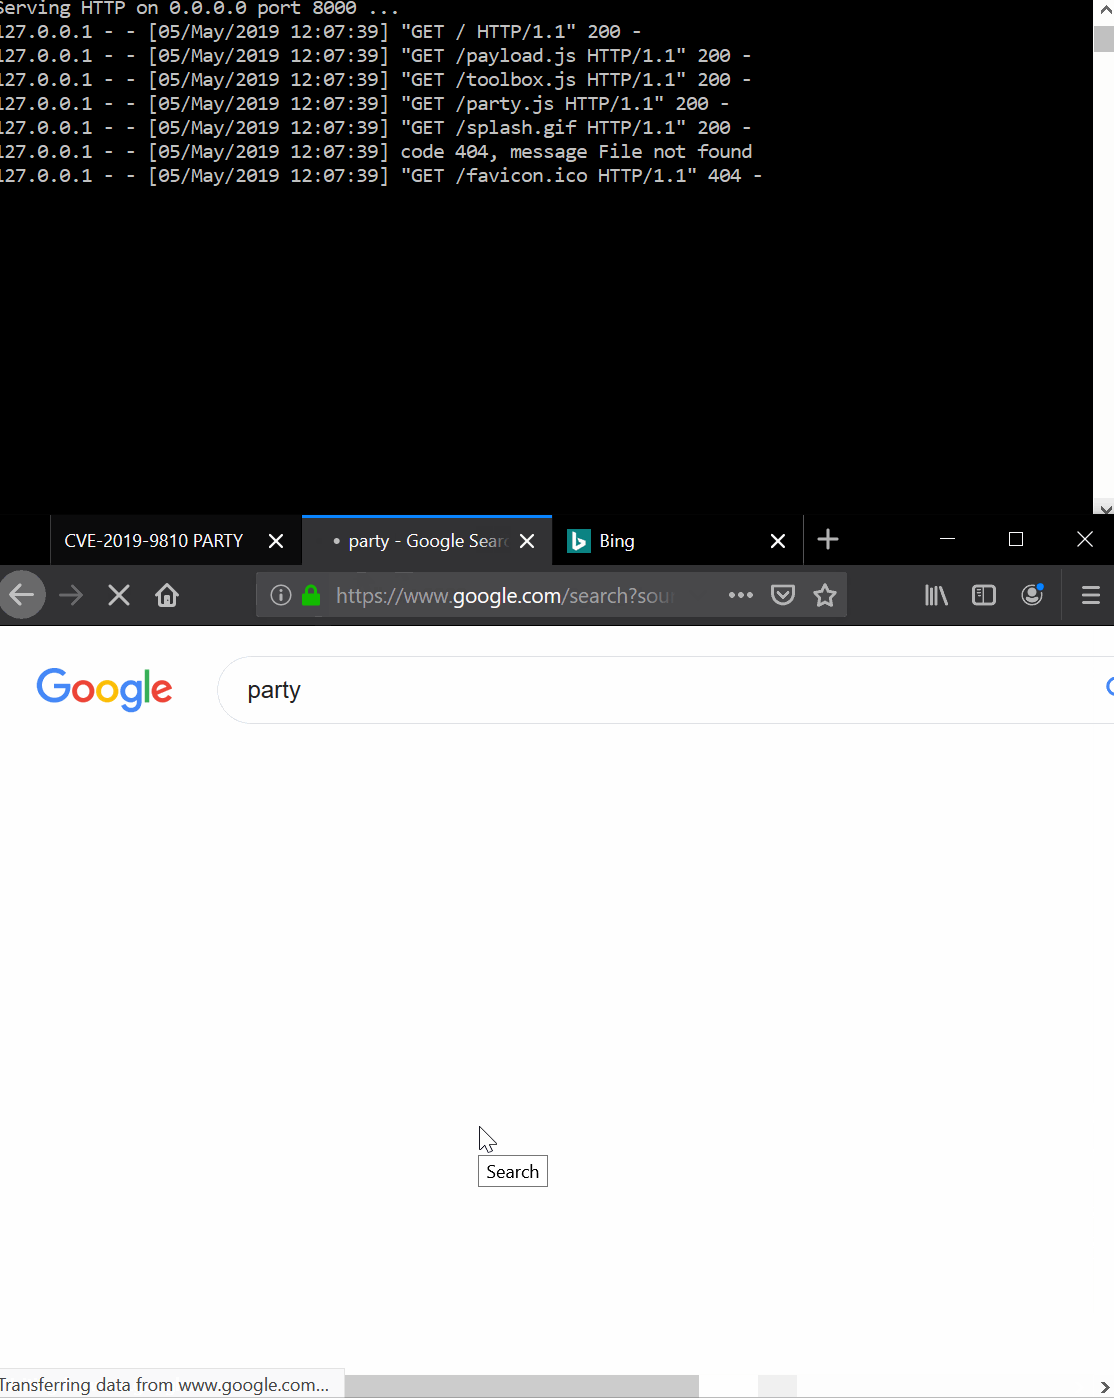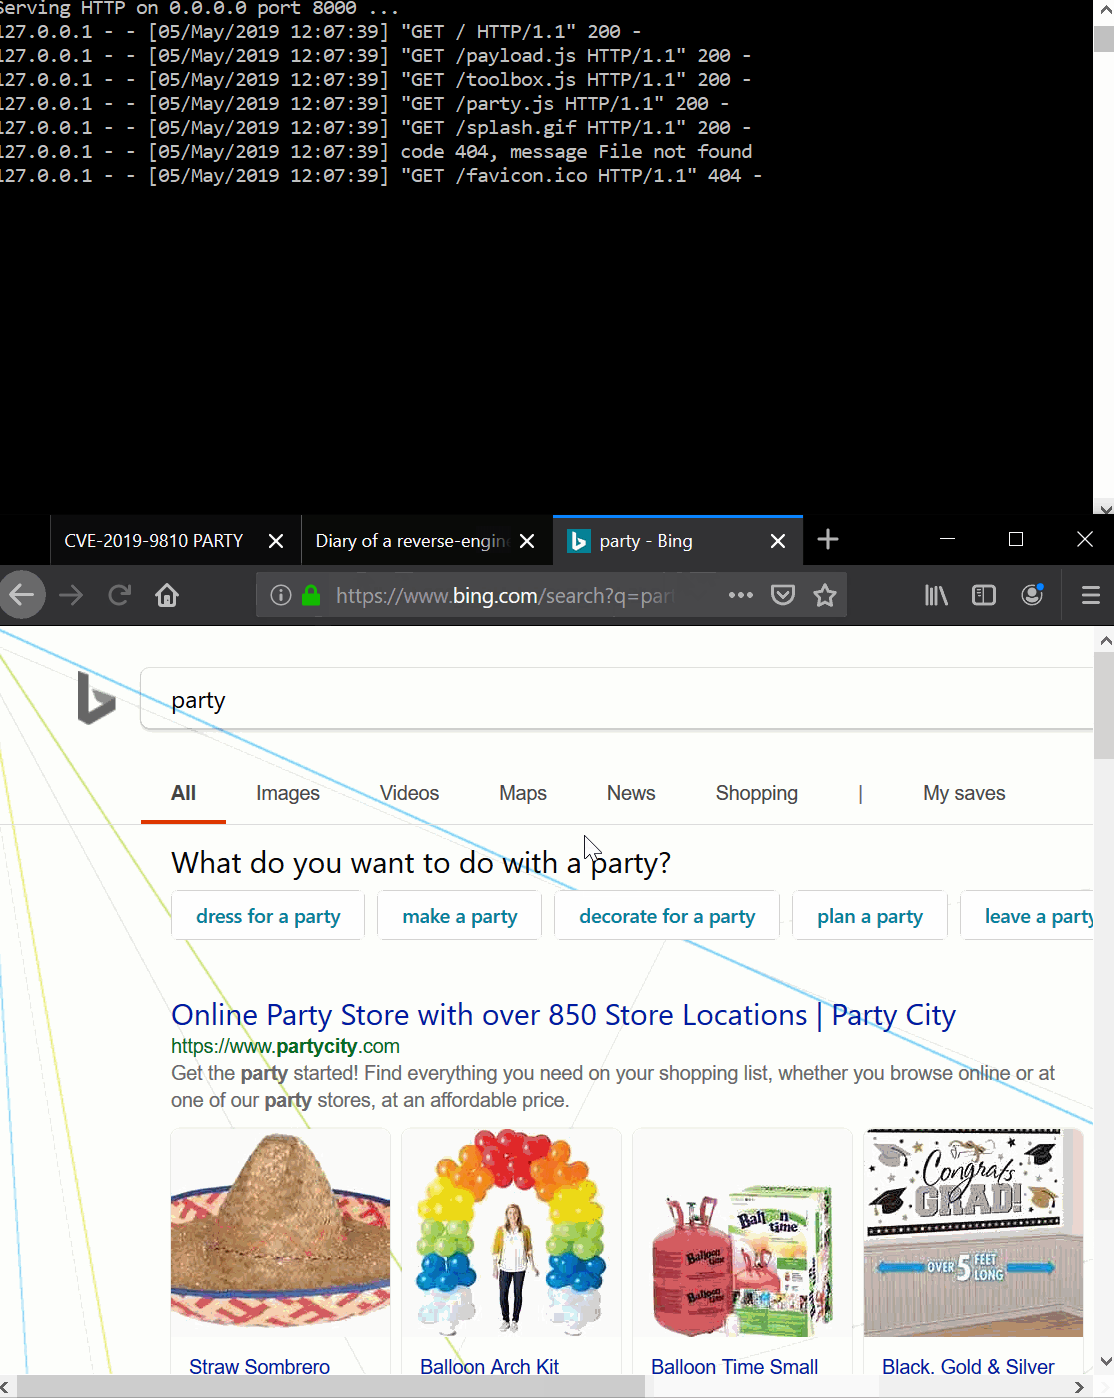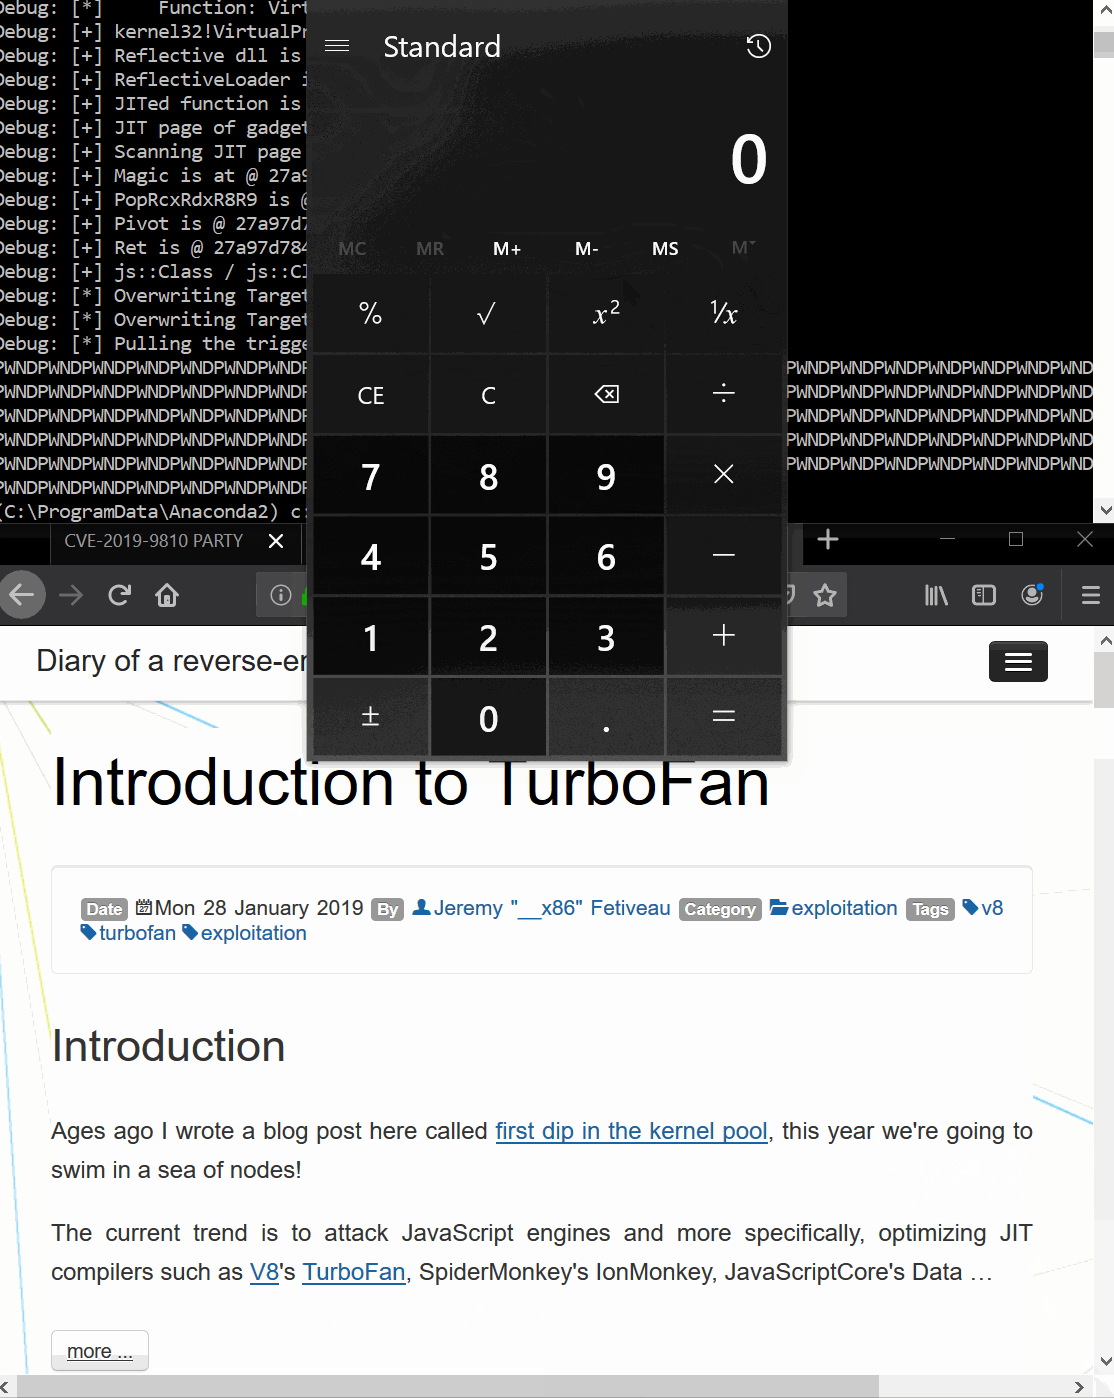 0vercl0k/cve-2019-9810
Exploit for CVE-2019-9810 Firefox on Windows 64-bit.
 damariion/cve-2017-14980.rce
Buffer overflow in Sync Breeze Enterprise 10.0.28 allows remote attackers to have unspecified impact via a long username parameter to /login

 hfiref0x/stryker
Multi-purpose proof-of-concept tool based on CPU-Z CVE-2017-15303
 damariion/cve-2018-6537.rce
A buffer overflow vulnerability in the control protocol of Flexense SyncBreeze Enterprise v10.4.18 allows remote attackers to execute arbitrary code…
 bytereaper77/webmin_exploit_reverse_shell
A simple C-based vulnerability in Webmin versions 1.890 to 1.920
 starnightcyber/cve-2017-11882
CVE-2017-11882 exploitation