

av_CVE-2020-0162_A10r33
 pazhanivelmani/av_cve-2020-0162_a10r33
Exploit for CVE-2020-0162 targeting a specific vulnerability, implemented in C++ for binary exploitation and security testing.
binary-exploitationcode-analysisexploitation+2
pazhanivelmani/av_cve-2020-0162_a10r33Exploit for CVE-2020-0162 targeting a specific vulnerability, implemented in C++ for binary exploitation and security testing.
 terribledactyl/cve-2025-55891
Proof-of-concept for CVE-2025-55891: heap corruption in TIFFCP.EXE via malformed TIFF file, triggering segmentation fault during LZW decompression in…
 satheesh575555/external_v8_aosp10_r33_cve-2021-0396
Repository containing V8 JavaScript engine source code with a specific commit for CVE-2021-0396, likely for vulnerability research and exploitation.
 jeromeyoung/ps4_8.00_vuln_poc
My take on CVE-2021-30858 for ps4 8.xx
 exploitcn/cve-2021-1732-exp-
Analyzes and debugs the CVE-2021-1732 Windows privilege escalation exploit, providing commented code for educational purposes.
 driverunload/cve-2024-25423
Cinema 4D out-of-bounds write vulnerability when parsing c4d files
 defrancescojp/cve-2013-3664_bmp
Proof-of-concept exploit for CVE-2013-3664: heap overflow in SketchUp BMP RLE4 texture parsing enabling arbitrary code execution via malicious .skp…
 defrancescojp/cve-2013-3664_mac
Sketchup MAC Pict Material Palette Stack Corruption
 bongbongco/cve-2008-4654
VideoLAN VLC media player 0.9.4 Media Player ty.c buffer overflow
 spiralbl0ck/exploit-starcraft-rop-virtualalloc-eud
 synacktiv/bfs_challenge_2019
Solution for BFS Ekoparty challenge 2019
 pixelofapicture/001-malware-analysis-cve-2017-11882
Malware Analysis CVE-2017-11882
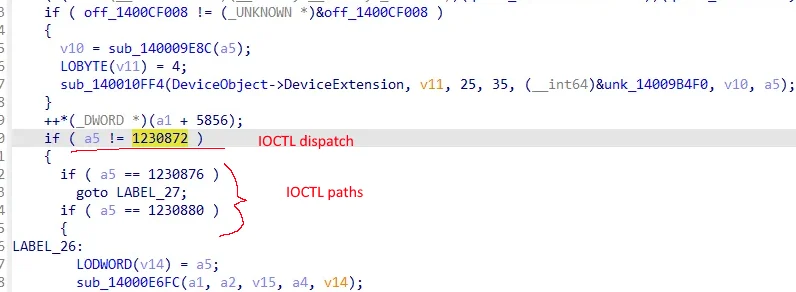 catforgor/cve-2026-51585
rt26cx21x64.sys exploit (Realtek PCIe GbE/2.5GbE/5GbE family)
 openl2d/moc3ingbird
MOC3ingbird Exploit for Live2D (CVE-2023-27566)
 aperikube/pwn-arm-nfc
ARM buffer overflow challenge exploiting NFC tag input on Raspberry Pi. Includes hardware assembly guide, server code, and flag retrieval for CTF and…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset