

CVE-2025-5548
 popclom/cve-2025-5548
Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
binary-exploitationdebuggerseducation+8
popclom/cve-2025-5548Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
 lorenzoporrasduque/cve-2025-5548-poc
Educational lab demonstrating a stack buffer overflow (CVE-2025-5548) in FreeFloat FTP Server. Covers full exploit development: vulnerability…
 shakyanayann/cve-2023-0179
Proof-of-concept exploit for CVE-2023-0179, a Linux kernel vulnerability enabling local privilege escalation via a crafted Netfilter nftables payload.
 reggyraider/cve-2023-21716
CVE-2023-21716 - Microsoft Word RTF fonttbl Heap Corruption RCE exploit with reverse shell payload
 fancyzll/cve-2026-43499_oppo-mt6835
Exploit source and PoC for CVE-2026-43499 targeting OPPO MT6835 Android device, including preload payload, build scripts, and analysis notes for…
 ill-deed/cve-2025-32463_illdeed
Privilege escalation exploit for CVE-2025-32463 using a malicious NSS module injected via sudo -R. This version creates a stealth payload called…
 ghostn4444/cve-2025-8088
Proof-of-concept exploit for CVE-2025-8088, a WinRAR path traversal vulnerability enabling arbitrary code execution via crafted RAR archives.…
 xi0onamdev/winrar-cve-2025-8088-exploitation-toolkit
GUI tool for creating malicious RAR archives exploiting CVE-2025-8088 path traversal. Uses NTFS ADS stealth and RAR5 header injection for payload…
 mohammadamin382/dirtycow-lab
Educational PoC for Dirty COW (CVE-2016-5195) with logging, ptrace fallback, and binary payload support.
 victoriousknight/cve-2023-38831_exploit
Python script that generates a malicious RAR file exploiting CVE-2023-38831 to execute a reverse shell payload, intended for educational and ethical…
 hmascs/ksuroot
One-click Android kernel rooting tool exploiting CVE-2026-43499 to install KernelSU, with official, bundled, and custom .so payload sources.
 commit-regrets/samsung_tizen_tv_root
Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…
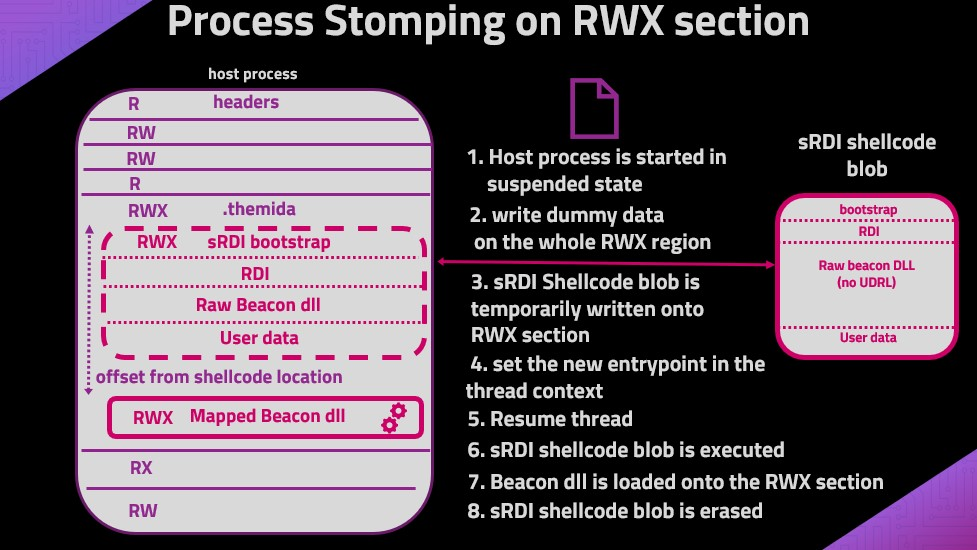 naksyn/processstomping
A variation of ProcessOverwriting to execute shellcode on an executable's section
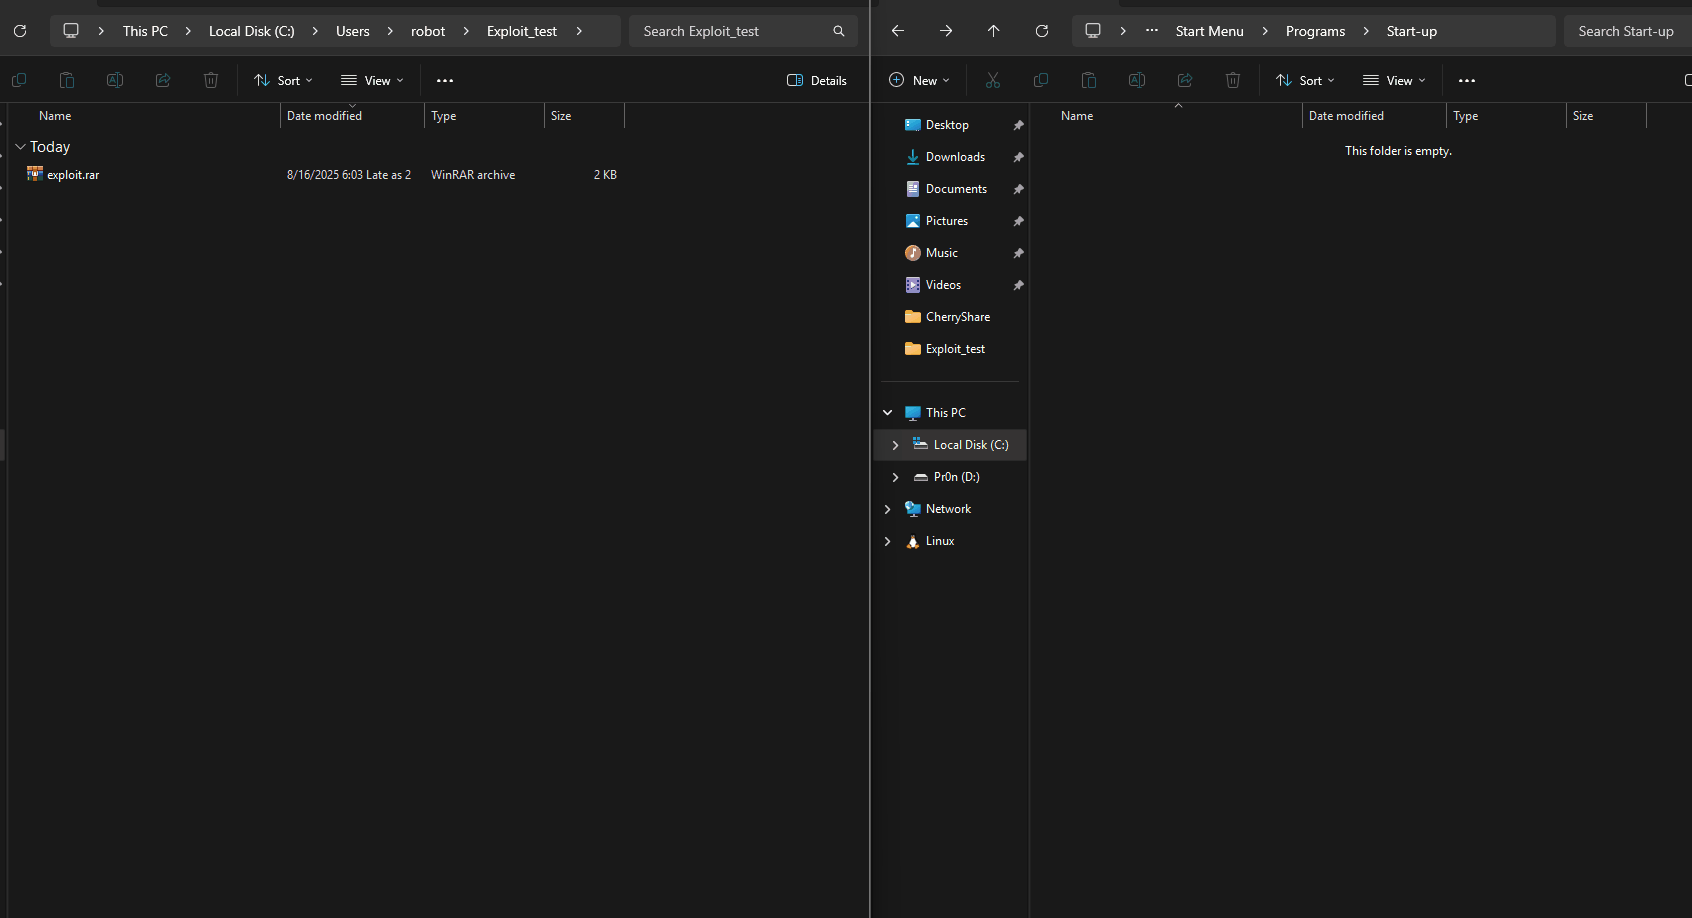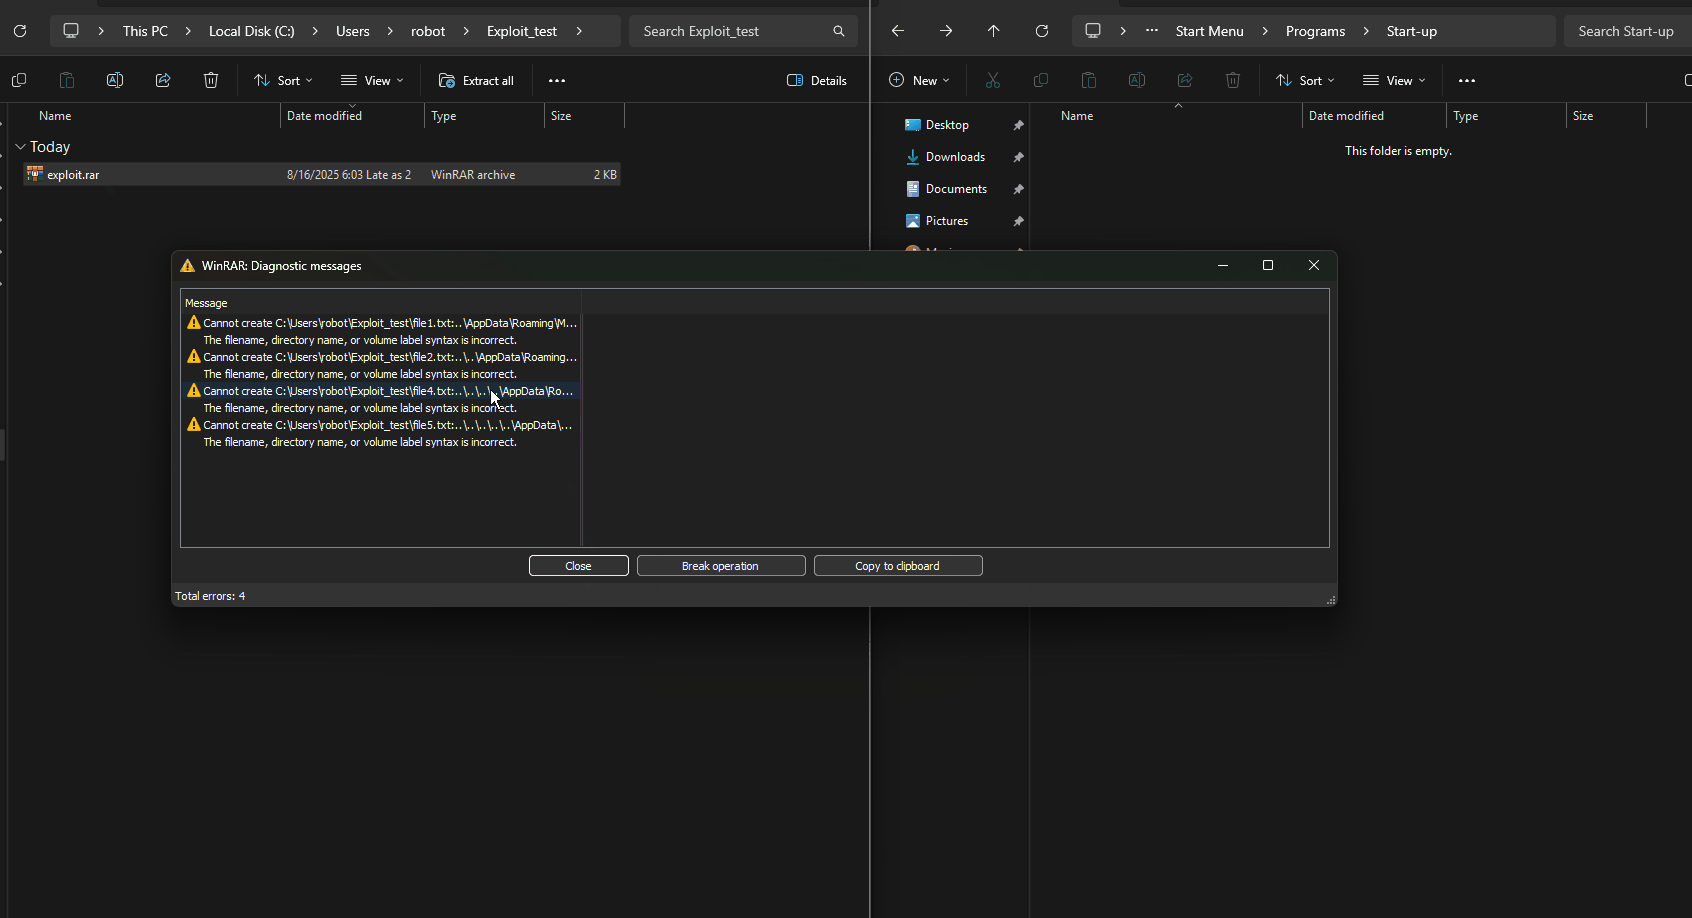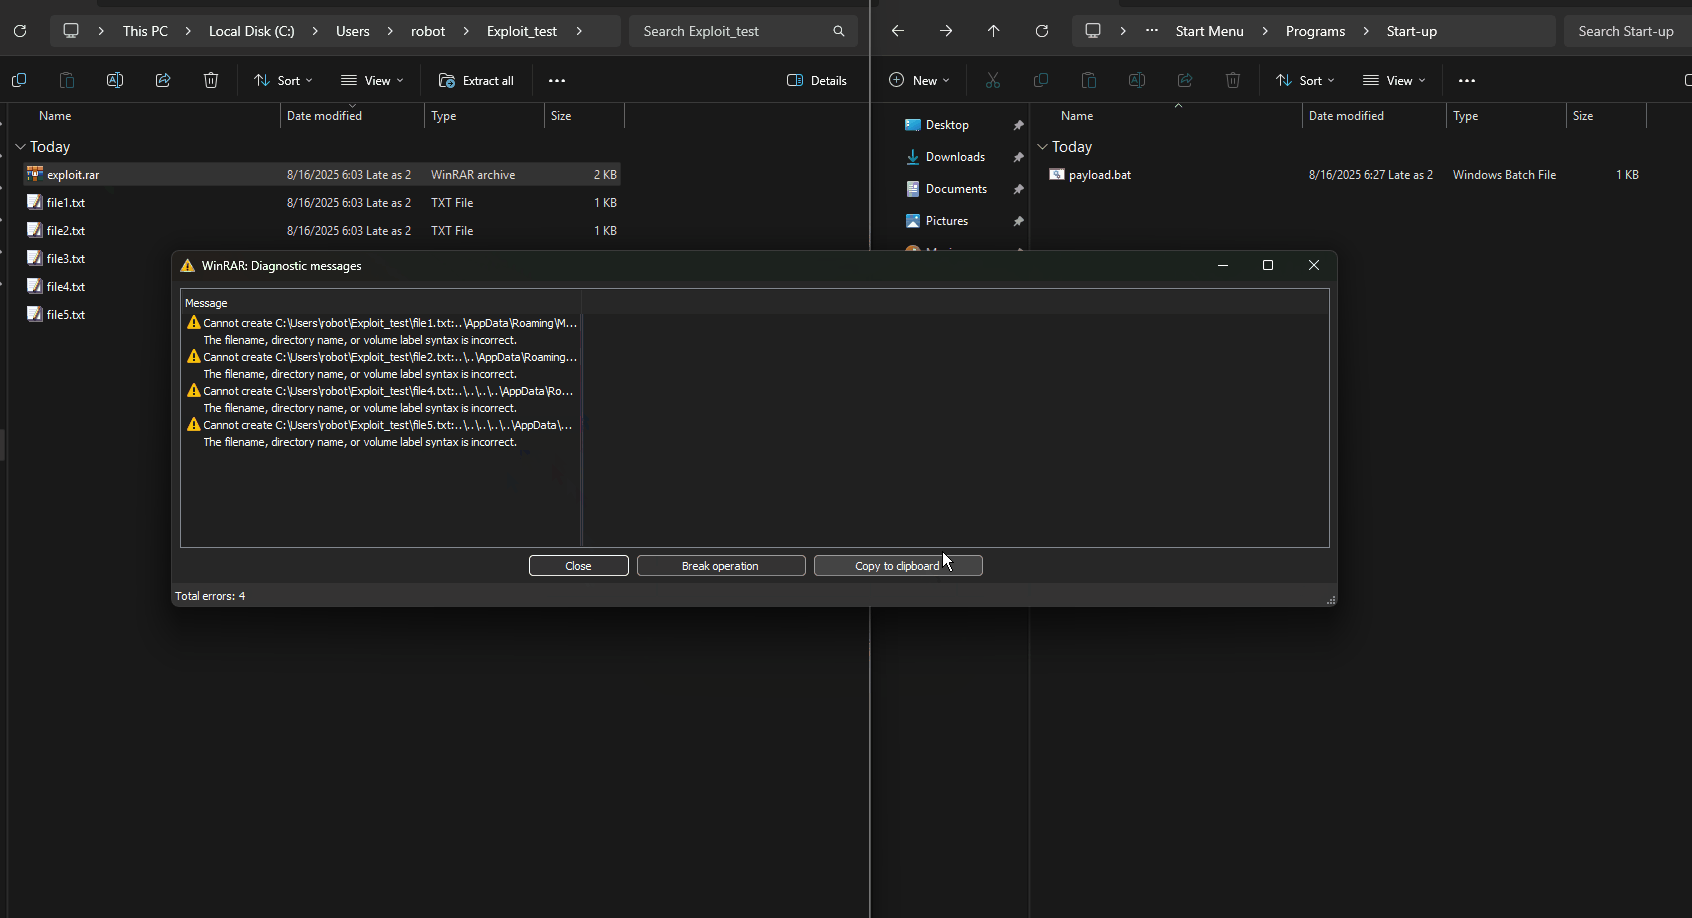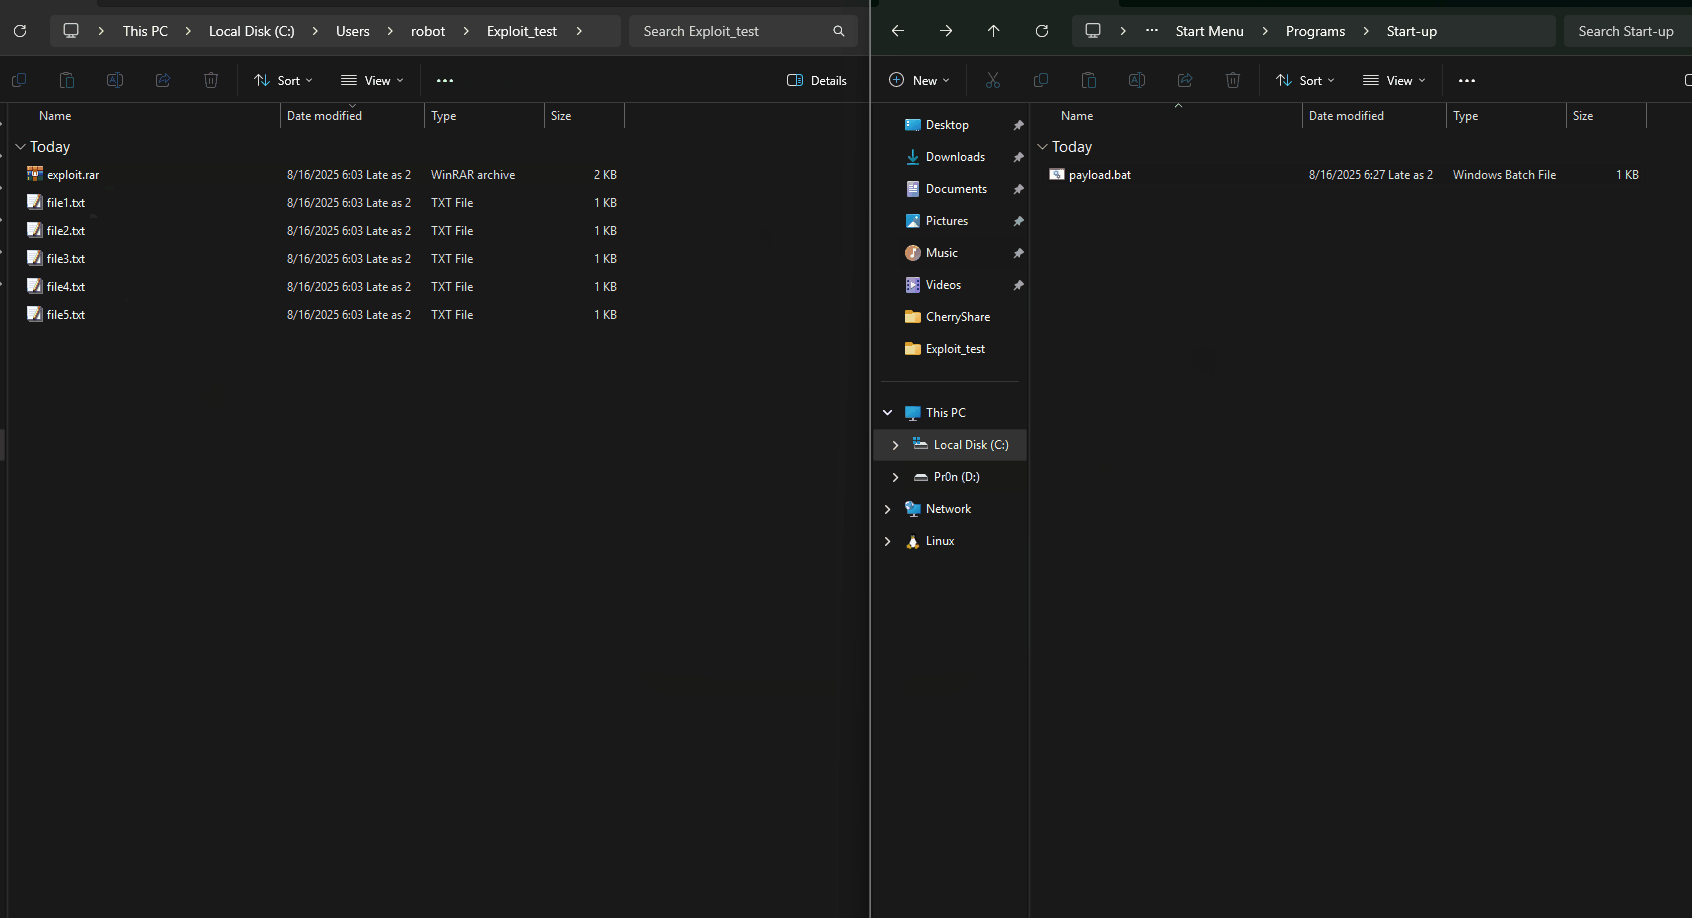 pentestfunctions/cve-2025-8088-multi-document
Exploit systems using older WinRAR without knowing their username (unlike other projects)
 kitsuneshade/winrar-exploit-tool---rust-edition
A high-performance, memory-safe implementation of the WinRAR CVE-2025-8088 exploit tool, rewritten in Rust for better reliability and performance.
 xerxes-2/cve-2026-31431-rs
Rust-based proof-of-concept for CVE-2026-31431, exploiting AF_ALG and splice to overwrite /bin/su and spawn a root shell. Self-contained no_std…
 justintroup85/exploits-forsale-collateral-damage
Kernel exploit for Xbox SystemOS using CVE-2024-30088
 dosamp/pkwned
Proof of Concept for CVE-2021-4034 (with experimental traceless exploitation)