
abhinavagarwal07.github.io
 abhinavagarwal07/abhinavagarwal07.github.io
RingWraith: CVE-2026-33150 and CVE-2026-33179 — Use-After-Free and NULL Dereference in libfuse io_uring
binary-exploitationeducationexploitation+3
abhinavagarwal07/abhinavagarwal07.github.ioRingWraith: CVE-2026-33150 and CVE-2026-33179 — Use-After-Free and NULL Dereference in libfuse io_uring
 angr/angr
A powerful and user-friendly binary analysis platform!
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 cookiengineer/actual-php2shell
🤖 NO, There is an easy way to exploit this vulnerability! (vibecoded to prove a point)
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 dinosn/php-cve-2026-10961x-lab-poc
PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…
 9bie/php2shell-bypass-aslr-exp
Pure-HTTP exploit achieving RCE on PHP 8.4.26 + Apache mod_php via session upload_progress heap leak, dangling pointer reuse, and ASLR bypass to call…
 franklinf25/cve-2026-42945
Analyzes CVE-2026-42945, an NGINX rewrite heap overrun, providing a differential detector, deterministic DoS PoC, and a credited RCE port with…
 franklinf25/cve-2026-31431
Analyzes CVE-2026-31431, a Linux kernel AF_ALG AEAD vulnerability, providing a safe detector, in-lab LPE exploit, and QEMU-based A/B kernel lab for…
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 xuehuolll/cve-2026-109618-109619-audit
CVE-2026-109618 / CVE-2026-109619 audit: session poisoning to command execution reproduced; BGCTX OOM precondition reproduced; claimed progress-array…
 oxasploits/oxasploits
A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast
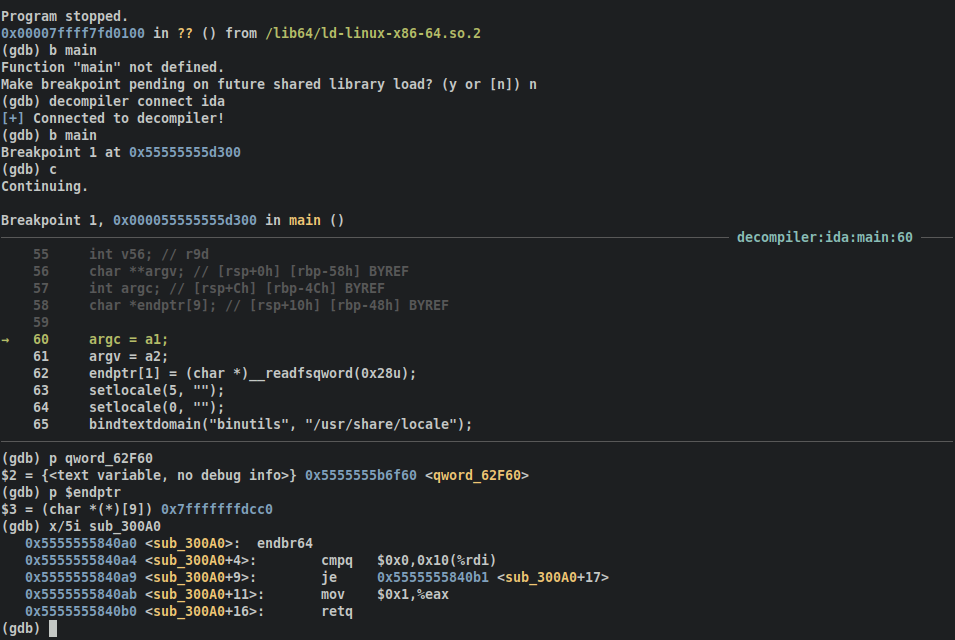 mahaloz/decomp2dbg
A plugin to introduce interactive symbols into your debugger from your decompiler
 ljagiello/ctf-skills
Agent skills for solving CTF challenges - web exploitation, binary pwn, crypto, reverse engineering, forensics, OSINT, and more
 star-sg/presentations
Curated collection of offensive security conference slide decks covering kernel and mobile exploitation, VM/container escapes, and…
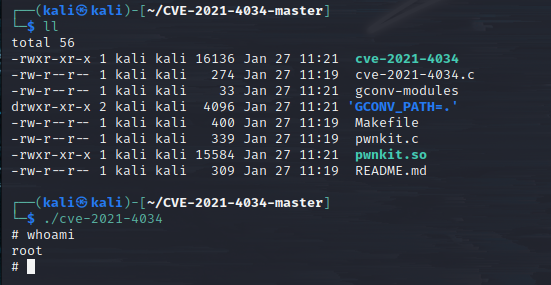 locksec/cve-2021-4034
Exploit PoC for the polkit pkexec (PWNKIT) vulnerability
 neurosaki987/tvm-recover
Devirtualizes Tencent VM .tvm0 sections: lifts VM handlers to guest-level listings and LLVM IR, recovers CFG and dispatch, and patches recovered code…
 yv1ing/secbox
Conducting cybersecurity testing using the pi agent in a pre-built sandbox environment.