

Detect-It-Easy
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
ai-assisted-reversingbinary-analysisbinary-exploitation+10
11.6k
horsicq/detect-it-easyProgram for determining types of files for Windows, Linux and MacOS.
 vudangducminh/cve-2022-0847
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe), a Linux kernel race condition enabling unprivileged writes to read-only files and privilege…
 karollooool/cve-2026-83991-writeup-and-poc
Proof-of-concept demonstrating a Windows Cloud Files access-check bypass (CVE-2026-83991) that converts a read-only file into a cloud placeholder via…
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
 abhinavagarwal07/abhinavagarwal07.github.io
RingWraith: CVE-2026-33150 and CVE-2026-33179 — Use-After-Free and NULL Dereference in libfuse io_uring
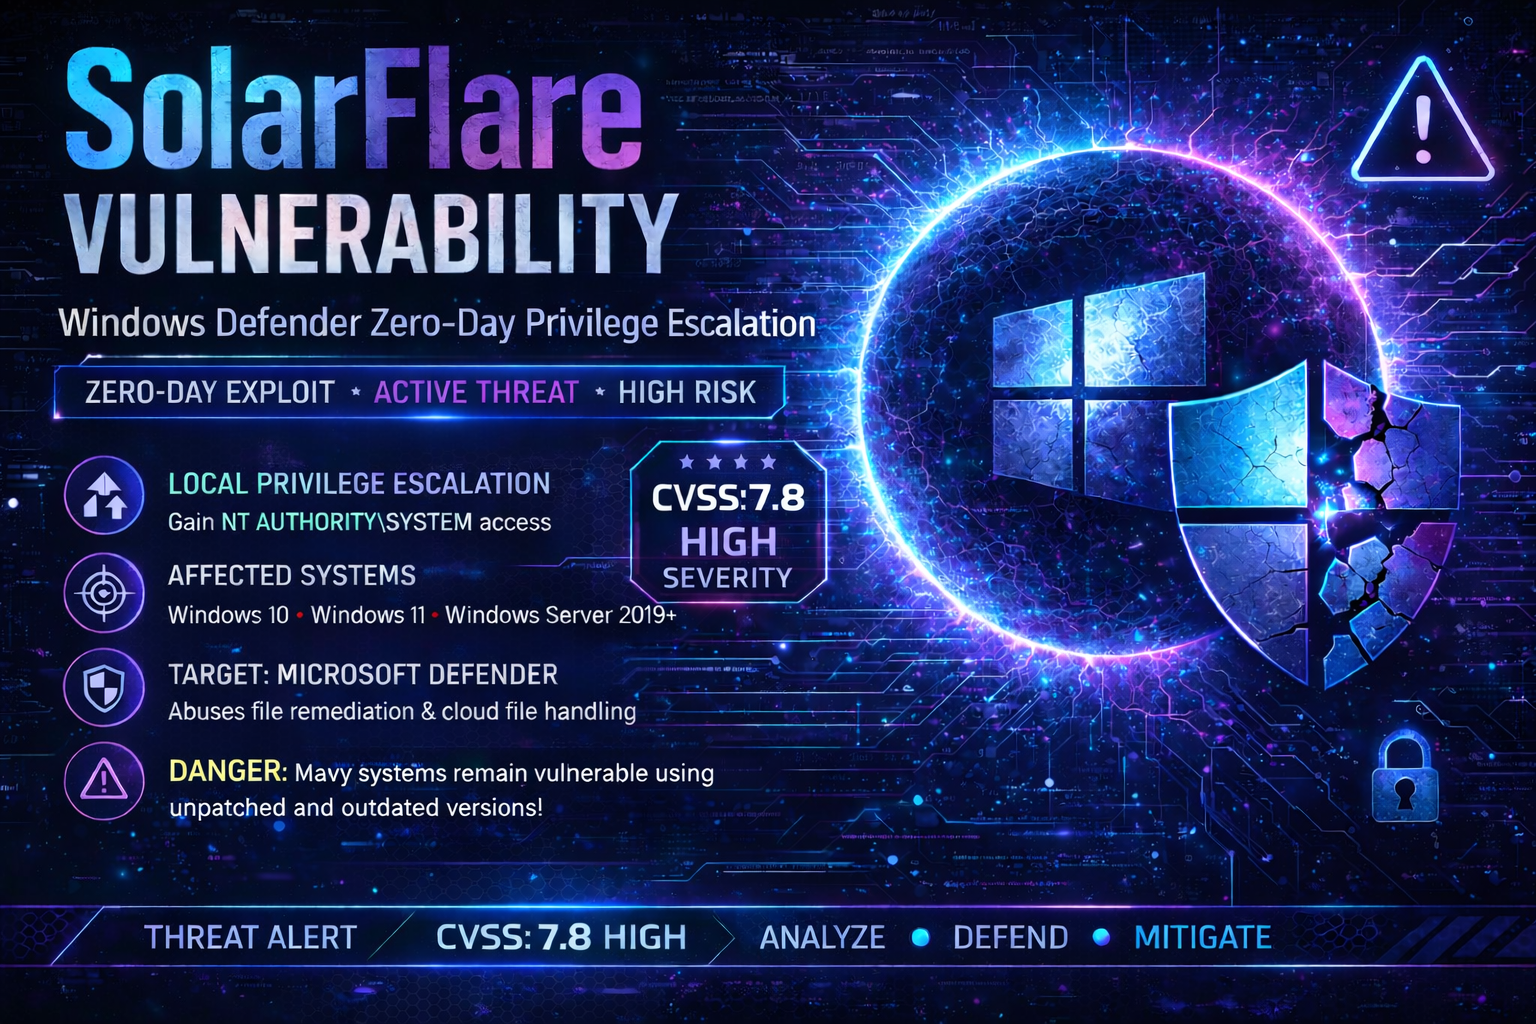 tc4dy/cve-2026-41091-poc-exploit
CVE-2026-41091 RedSun | Microsoft Defender LPE exploit. Low-privileged users gain NT AUTHORITY\SYSTEM 🔥 via Cloud Files API + NTFS junction…
 sashs/ropper
Display information about files in different file formats and find gadgets to build rop chains for different architectures (x86/x86_64, ARM/ARM64,…
 xcracker000/cve-2024-56426
CVE-2024-56426 Exynos9830 Bootrom Exploit - SM-G985F
 skimask1690/wisedelete
Windows utility that uses the vulnerable WiseDelfile64.sys driver affected by CVE-2025-66680 to enable kernel-assisted file deletion.
 trevocastles/cve-2026-31431-copy-fail
Exploit PoC for CVE-2026-31431 that uses AF_ALG and splice() to overwrite Linux page cache and patch /usr/bin/su in memory, escalating unprivileged…
 bailan766/rmx3888-cve-2026-43499-config
CVE-2026-43499 exploit configuration for realme RMX3888 (Android 16) - 20 verified kernel offsets
 pealeap/cve-2026-21045_and_cve-2026-21048
Generates crafted TIFF/DNG files to trigger out-of-bounds writes in Samsung's libimagecodec.quram.so, including binary analysis and reproduction…
 martinclauss/exim-rce-cve-2018-6789
This repository provides a learning environment to understand how an Exim RCE exploit for CVE-2018-6789 works.
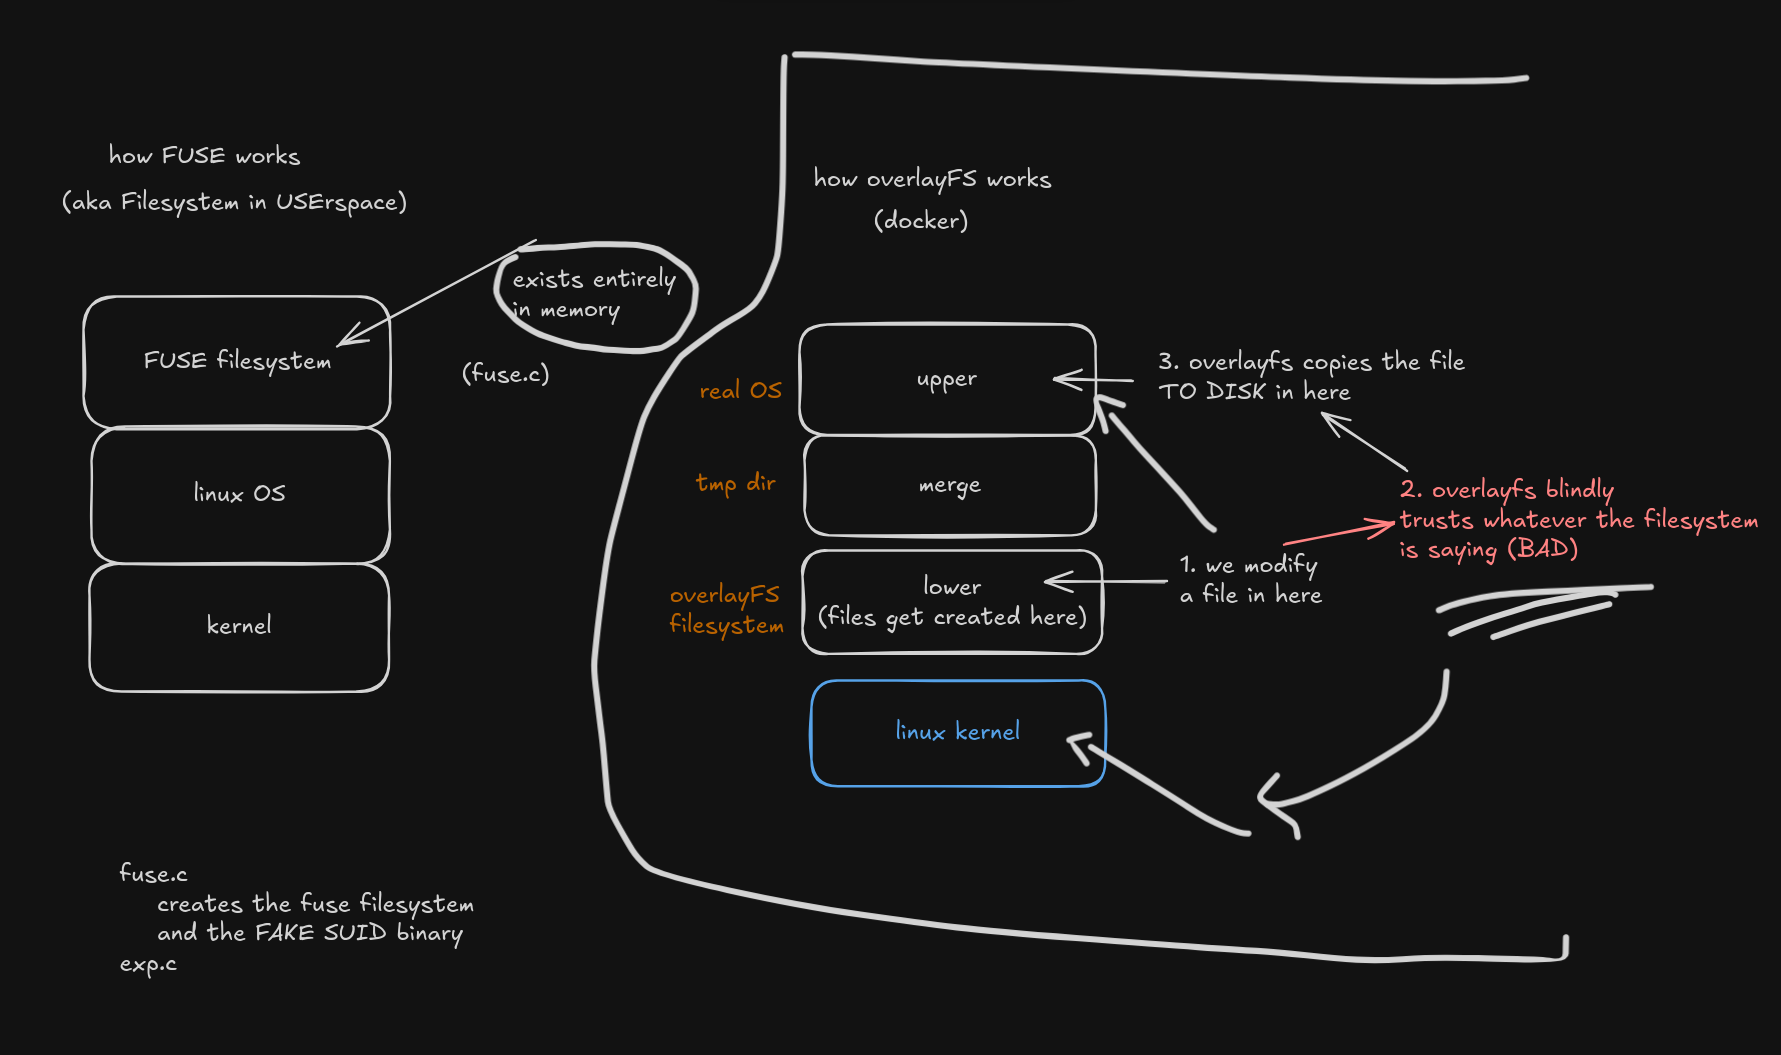 pwncone/cve-2023-0386-overlayfs
Copy fake in-memory files to disk using overlayFS
 0x00jeff/cve-2025-27591
self cleaning CVE-2025-27591 Poc that grants a root reverse shell instead of modifying passwd files
 benedictejepu/cve-2026-46300-fragnesia---tryhackme-lab-project
The project documents the completion and analysis of the Fragnesia (CVE-2026-46300) TryHackME lab, which demonstrates a Linux kernel page -cache…
 0xfuffm3/cve-2026-31635-dirtydecrypt
Linux kernel local privilege escalation exploit for CVE-2026-31635 that corrupts page cache via RxRPC in-place decryption, overwrites read-only…
 adityasingh108/cve-2026-31431-metasploit-exploit
Automated Metasploit post-exploitation module for CVE-2026-31431 ("Copy Fail"). Weaponizes a deterministic logic flaw in the Linux kernel AF_ALG…