

Cobaltstrike_BOFLoader
 codextf2/cobaltstrike_bofloader
open source port/reimplementation of the Cobalt Strike BOF Loader as is
binary-exploitationexploit-frameworkspayload-development+3
73
codextf2/cobaltstrike_bofloaderopen source port/reimplementation of the Cobalt Strike BOF Loader as is
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
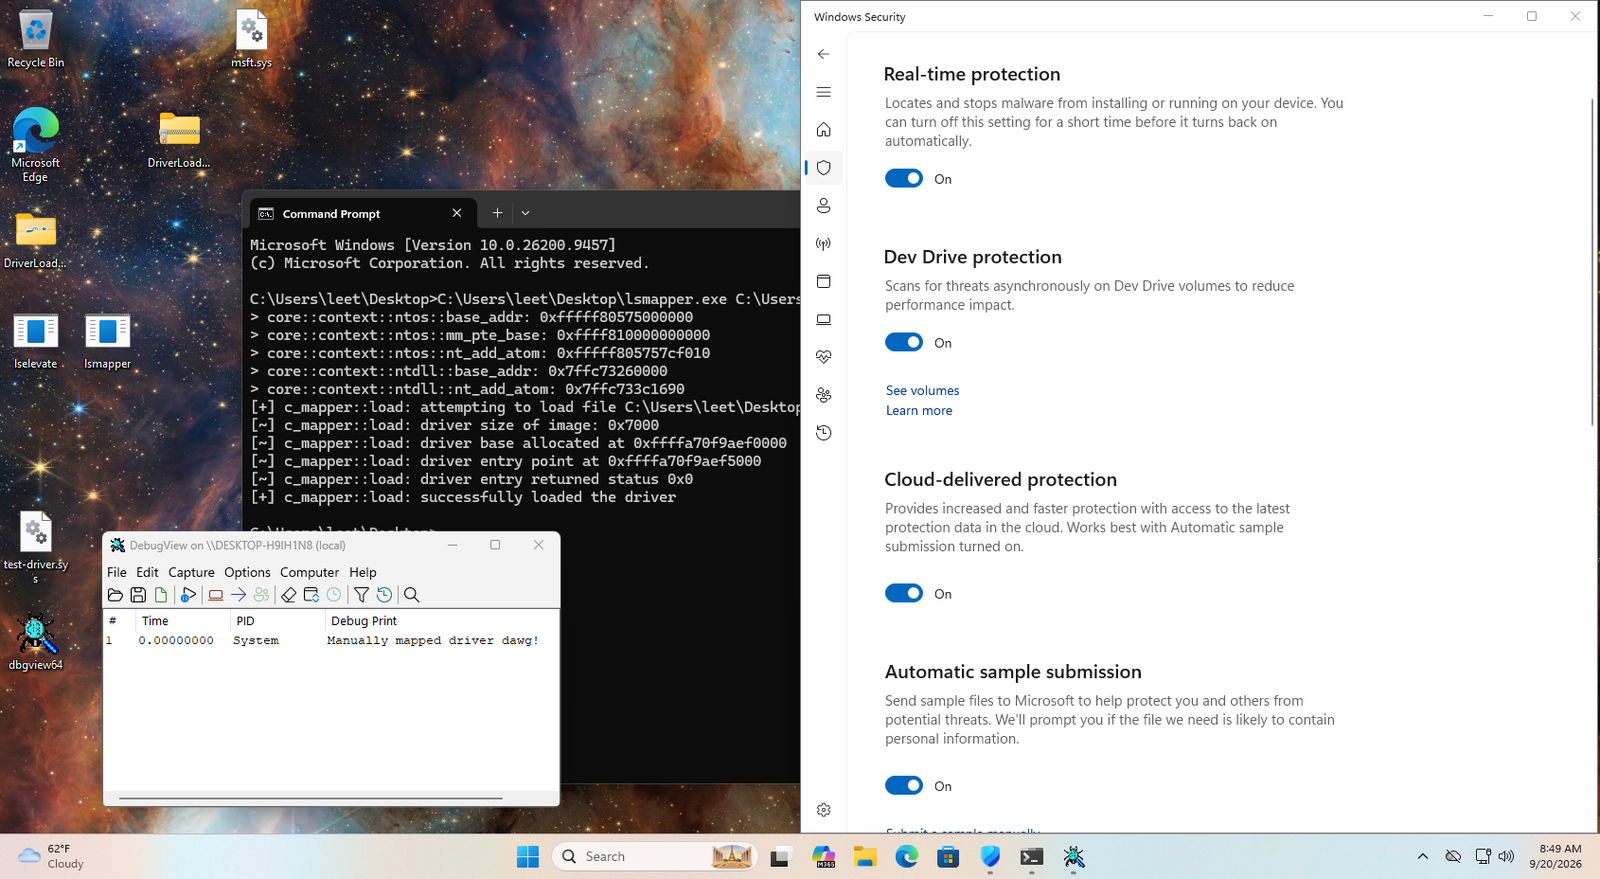 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 0b0111100/2009
Collection of Linux kernel exploits targeting CVE-2009-1185, CVE-2009-1337, CVE-2009-2692, CVE-2009-2698, and CVE-2009-3547, providing…
 joaovicdev/exploit-cve-2024-7804
Docker lab + Python exploit for CVE-2024-7804 (PyTorch torch.distributed.rpc unsafe pickle deserialization RCE, CWE-502, torch <= 2.3.1)
 eddinos2/cve-2026-64747
Root-cause analysis and reachability PoC for CVE-2026-64747, a buffer overflow in the AppleAVE2 kernel extension. Includes reversed IOKit wire…
 tenor-z/cve-2025-4255---buffer-overflow
Exploit framework targeting CVE-2025-4255, a buffer overflow vulnerability, providing a structured environment for developing and testing exploits.
 amorcool/ios26.6-cve-2026-65343
CVE-2026-65343 PoC — AppleKeyStore OOB read → KASLR defeat (iOS 26.6 / 23G71)
 r3dw4n48m3d/cve-2021-3493-exploit
C-based local privilege escalation exploit for CVE-2021-3493, targeting OverlayFS in Linux kernels prior to 5.11. Provides compilation and usage…
 sneakynachos/cve-2026-74939-escape-the-mac-n-cheese-box
Firefox content-to-parent IPDL privilege escalation (N-day, bug 2054416): forged PDocumentChannel with RemoteTypeOverride -> privilegedabout process…
 genericcoding/pois0nsword
A demonstration of read write using cve-2025-43529 and userland PAC bypass on iOS 26.1
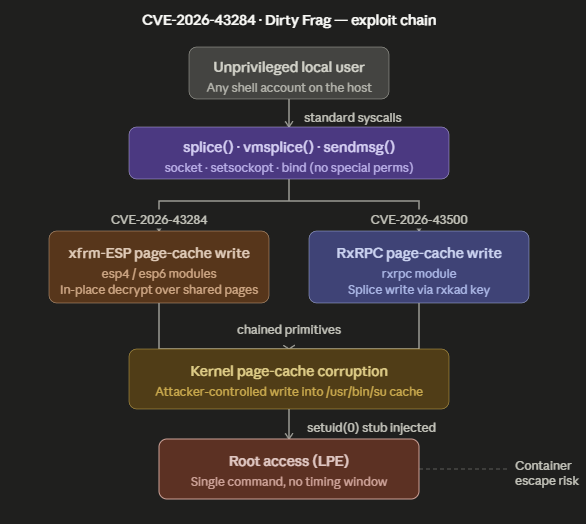 lucaspdiniz/cve-2026-43284
Dirty Frag - kernel Linux critical Vulnerability
 ryan2929/cve-2026-43284-
Local privilege escalation exploit for Linux kernel CVE-2026-43284 (Dirty Flag), providing root access on vulnerable systems.
 mr-bv/copy-fail-cve-2026-31431-exploit-in-c
C exploit for CVE-2026-31431, a Linux kernel page-cache corruption vulnerability in the AF_ALG AEAD path, using splice() to influence cached file…
 ikow/cve-2026-31431-live-code-corruption
CVE-2026-31431 (Copy Fail) novel exploit: live code corruption via page cache. Overwrites libc exit() code through MAP_PRIVATE page sharing — affects…
 guiimoraes/cve-2026-31431
Python implementation of a Linux kernel local privilege escalation exploit for CVE-2026-31431, leveraging xfrm ESP-in-UDP MSG_SPLICE_PAGES no-COW to…
 julichaan/cve-2026-31431-python-copyfail-poc
Python exploit for CVE-2026-31431, a Linux kernel privilege escalation via page cache corruption of setuid binaries, achieving root access.