

StealMyBitcoin-PoC
 killaboi/stealmybitcoin-poc
A public release of the Steal My Bitcoin challenge
binary-exploitationctfexploitation+5
216
killaboi/stealmybitcoin-pocA public release of the Steal My Bitcoin challenge
 xuehuolll/cve-2026-109618-109619-audit
CVE-2026-109618/109619 — PHP session.upload_progress pre-auth RCE. Exploit research: remote ASLR chain, PoC & patch analysis.
 silentisvox/syscallrevenant
Clean Indirect Syscalls with Syscall Tampering.
 abraxas/qemu-xhci-complete-uaf
QEMU 11.1.2 - High - Local - UAF - xhci_complete leftover of CVE-2026-17588 doorbell DMA
 gmh5225/memory-relocalloc
C proof-of-concept that locates code caves in the .reloc section of mapped DLLs to allocate and execute small shellcode, replacing typical memory…
 bignerd95/chimay-red
Working POC of Mikrotik exploit from Vault 7 CIA Leaks
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
 xf1les/fsop-finder
Binary Ninja plugin that scans glibc libio for FSOP code paths capable of hijacking control flow and stack pointer, aiding heap exploitation research.
 fortbridge-uk/libheif-grid-nextjs-rce
Private Fortbridge PoC for the CVE-2026-32740 Next.js/sharp leak-to-memcpy-GOT RCE chain
 gmh5225/icall-gadget
Exploit for redirecting control flow of a legit kernel module to your own illegitimate kernel module to evade anti-cheats stack walking
 jazho76/house_of_apple_2
Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
 rafabd1/vectorfreed
Documents the VectorFreed librsvg use-after-free RCE chain (CVE-2026-96889) with an SVG generator PoC and remediation guidance for librsvg, Next.js,…
 se1ims/pixelsmash
Proof-of-concept and lab harness for CVE-2026-8461, an out-of-bounds write in FFmpeg's MagicYUV decoder, with payload generator and Qt demo player.
 devrodt2/cve-2026-28609-matroska-pcm-oob
Proof-of-concept and instrumented reproduction harness for CVE-2026-28609, an out-of-bounds write in Android's MatroskaExtractor reachable via a…
 manizada/dirtyah6
Python PoC for CVE-2026-80844: IPv6 AH6 skb corruption and ESP-in-UDP decryption to overwrite /etc/pam.d/su and escalate to root on Linux.
 manizada/tunderflow
Python PoC for CVE-2026-81000, a Linux kernel local privilege escalation via TUN/OVS out-of-bounds write and pipe_buffer flag manipulation to gain…
 deaurity/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
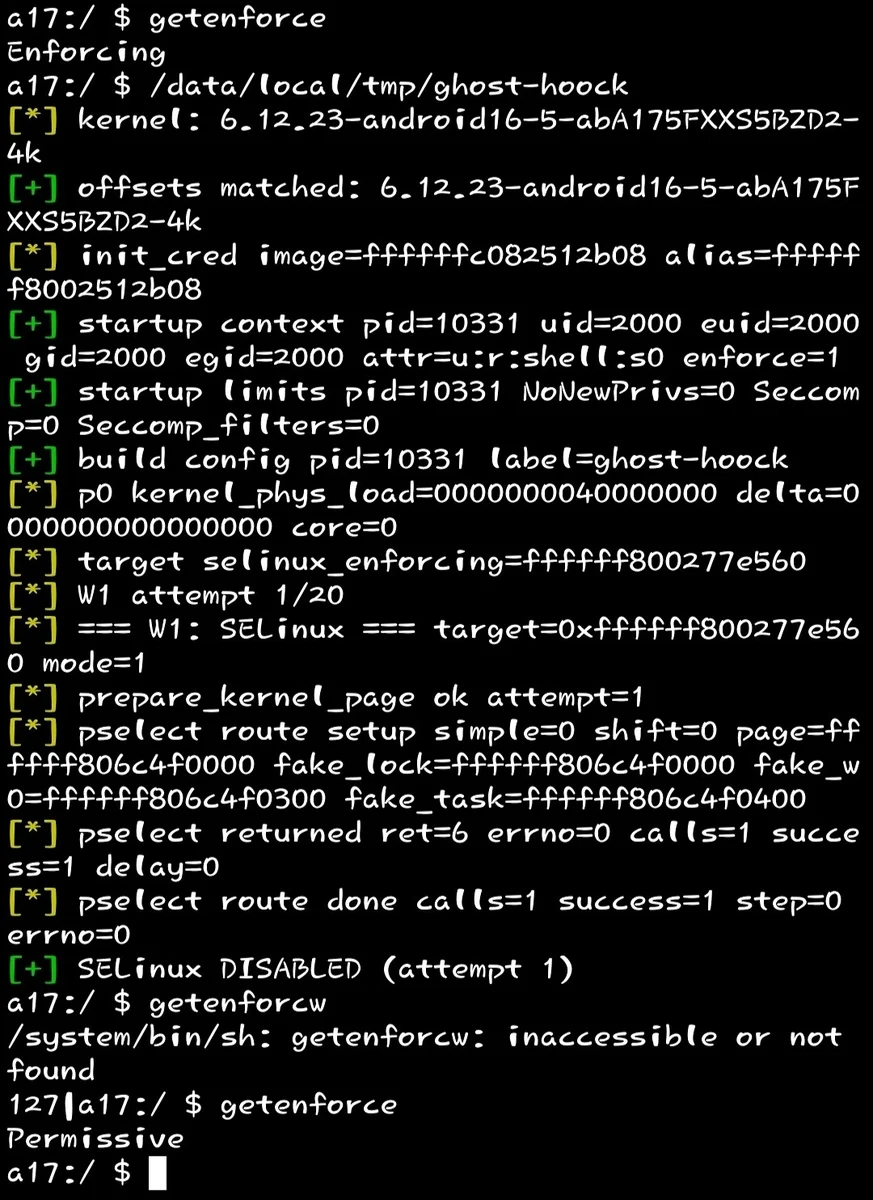 genksome/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.