
lithium-kernel
 gmh5225/lithium-kernel
Windows kernel-mode driver with user-mode client exposing IOCTL-based physical and virtual memory read/write, page table walking, pattern scanning,…
anti-botbinary-exploitationmemory-forensics+1
gmh5225/lithium-kernelWindows kernel-mode driver with user-mode client exposing IOCTL-based physical and virtual memory read/write, page table walking, pattern scanning,…
 not-matthias/amd_hypervisor
Rust AMD SVM hypervisor framework with customizable vmexit handlers (MSR, CPUID, RDTSC) and NPT hooking for kernel-level monitoring and research.
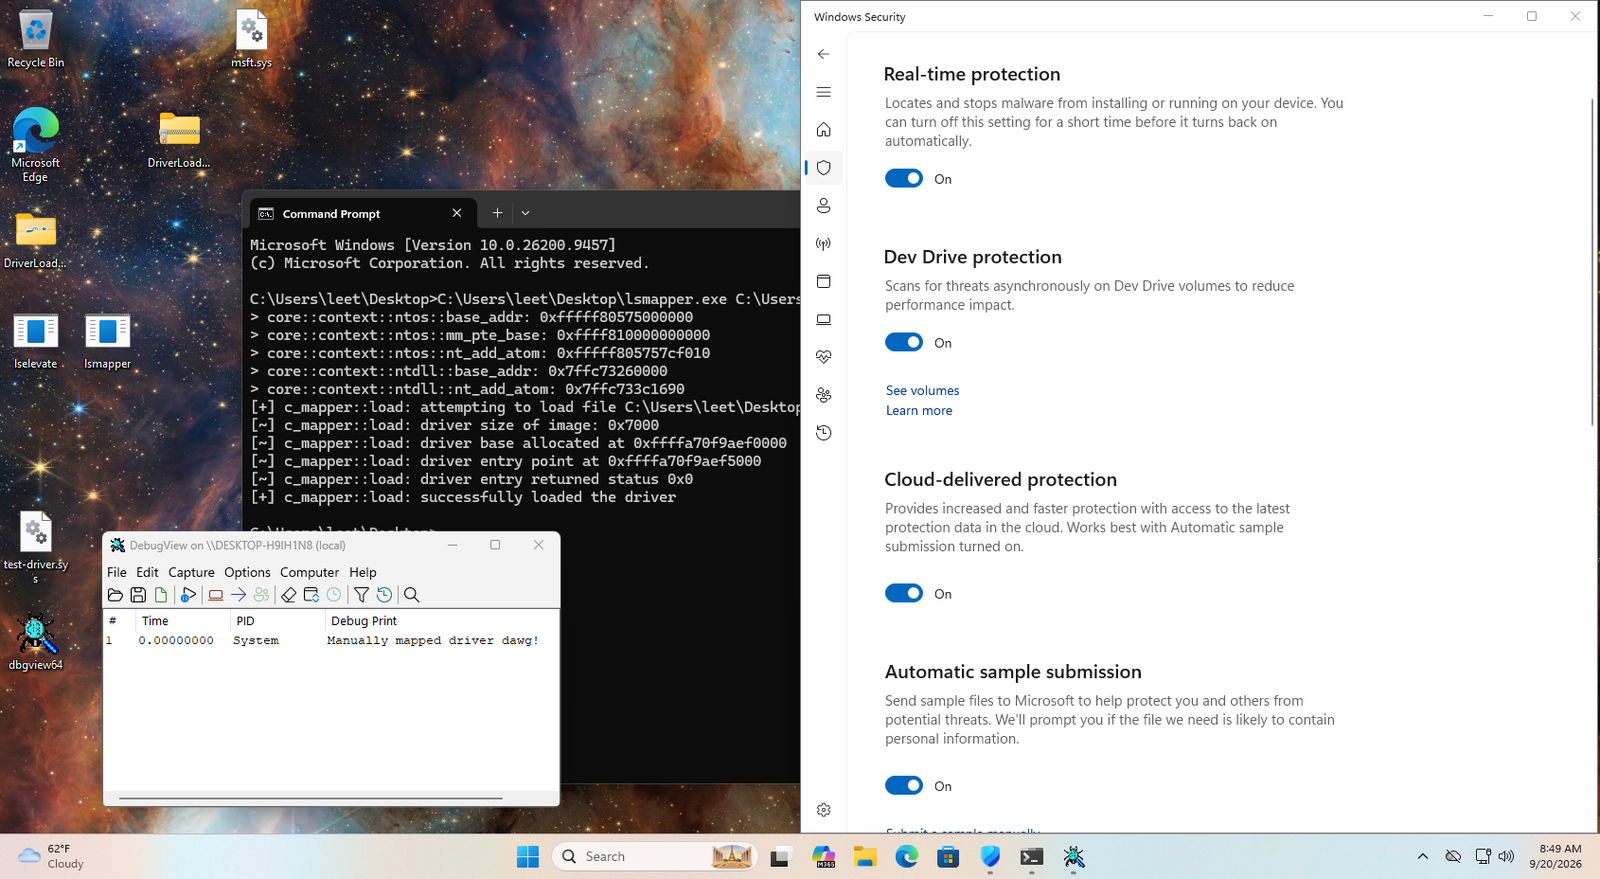 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 rainbowdynamix/fortilol
FortiClient FortiShield exploit (CVE-2015-5736) for Windows 10 1809
 tarpeg007/cve-2026-74586
Unprivileged proof-of-concept for CVE-2026-74586, a Linux kernel SCTP ASCONF use-after-free. Provides a raw-packet trigger, reliability metrics, and…
 teamn4c/sg-2026-0024
CVE-2026-43284 and CVE-2026-43500 Dirty Frag PoC and exploit
 dbgbgtf1/cve-2026-40369-exploit
Exploit for CVE-2026-40369 that leverages kernel address leak and token forging to achieve privilege escalation in a browser sandbox environment.
 0b0111100/2004
Linux kernel privilege escalation exploits targeting CVE-2004-0077 and CVE-2004-1235, including caps_to_root technique for gaining root access.
 0b0111100/2005
Linux kernel exploit implementations targeting CVE-2005-0736 and CVE-2005-1263, providing proof-of-concept code for privilege escalation on…
 0b0111100/2006
Linux kernel privilege escalation exploits targeting CVE-2006-2451 and CVE-2006-3626, providing proof-of-concept code for local privilege escalation…
 0b0111100/2008
Linux kernel exploit implementations targeting CVE-2008-0600, CVE-2008-0900, and CVE-2008-4210, providing proof-of-concept code for privilege…
 0b0111100/2009
Collection of Linux kernel exploits targeting CVE-2009-1185, CVE-2009-1337, CVE-2009-2692, CVE-2009-2698, and CVE-2009-3547, providing…
 joaovicdev/exploit-cve-2024-7804
Docker lab + Python exploit for CVE-2024-7804 (PyTorch torch.distributed.rpc unsafe pickle deserialization RCE, CWE-502, torch <= 2.3.1)
 eddinos2/cve-2026-64747
Root-cause analysis and reachability PoC for CVE-2026-64747, a buffer overflow in the AppleAVE2 kernel extension. Includes reversed IOKit wire…
 ethanevans92/cve-2025-32463
Proof-of-concept exploit for CVE-2025-32463, a local privilege escalation in sudo. Demonstrates chroot-based NSS manipulation to load a malicious…
 tenor-z/cve-2025-4255---buffer-overflow
Exploit framework targeting CVE-2025-4255, a buffer overflow vulnerability, providing a structured environment for developing and testing exploits.
 hackspeak/cve-2026-62735
Local privilege escalation exploit for Windows HTTP.sys integer overflow (CVE-2026-62735), demonstrating crash and full SYSTEM shell via nonpaged…