Phantom-Evasion-Loader

x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…

x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…

Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…

Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…

POC for CLFS CVE-2022-24481

Repository containing V8 JavaScript engine source code with a specific commit for CVE-2021-0396, likely for vulnerability research and exploitation.

Academic Research Edition - T1: User-mode evasion (obfuscation + syscall gateway), T2: BYOVD kernel bridge, T3: DMA hardware (future work).

Builds a root exploit for vivo/iQOO devices targeting CVE-2026-43499, leveraging kernel techniques like KASLR bypass and CFI manipulation to achieve…

Proof-of-concept exploit for CVE-2026-2763, a use-after-free in Mozilla's JavaScript engine, demonstrating a constrained 1-bit write primitive…

CVE-2026-41091 RedSun | Microsoft Defender LPE exploit. Low-privileged users gain NT AUTHORITY\SYSTEM 🔥 via Cloud Files API + NTFS junction…

Detailed proof-of-concept and technical analysis for CVE-2026-2441, a Chrome CSS use-after-free vulnerability enabling sandboxed renderer RCE via…

bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)

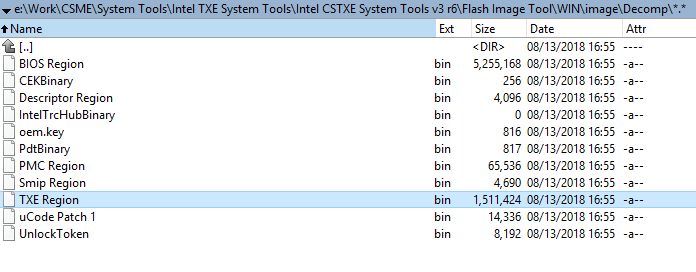
Intel Management Engine JTAG Proof of Concept

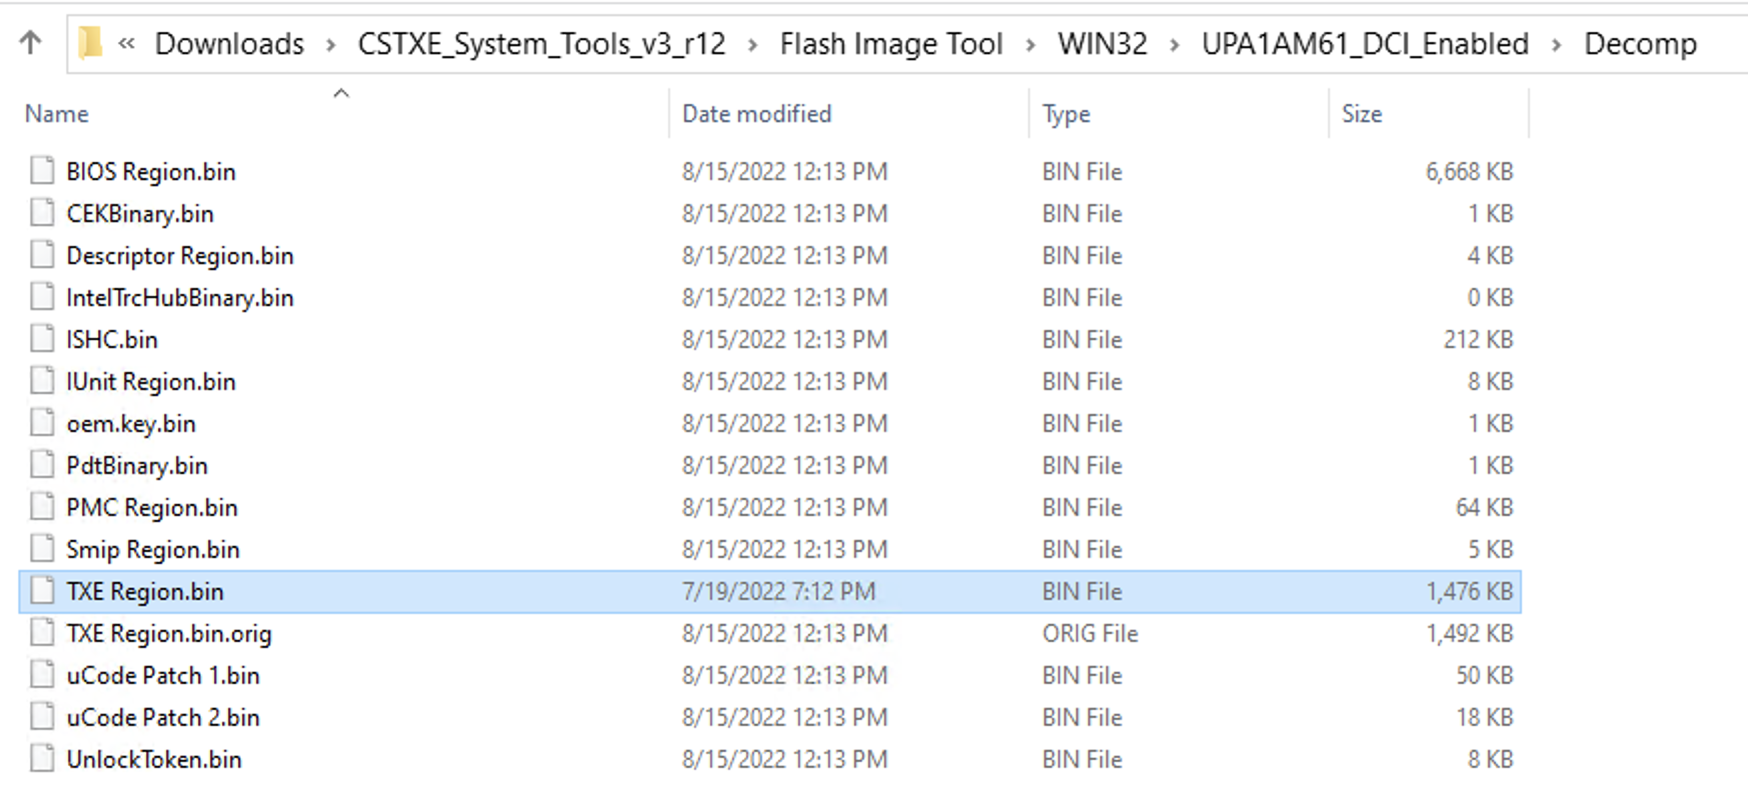
Intel Management Engine JTAG Proof of Concept - 2022 Instructions

Exploit for CVE-2026-14431 providing V8 sandbox read/write primitives via a crafted JavaScript file, targeting Chromium's V8 engine on Linux x64.

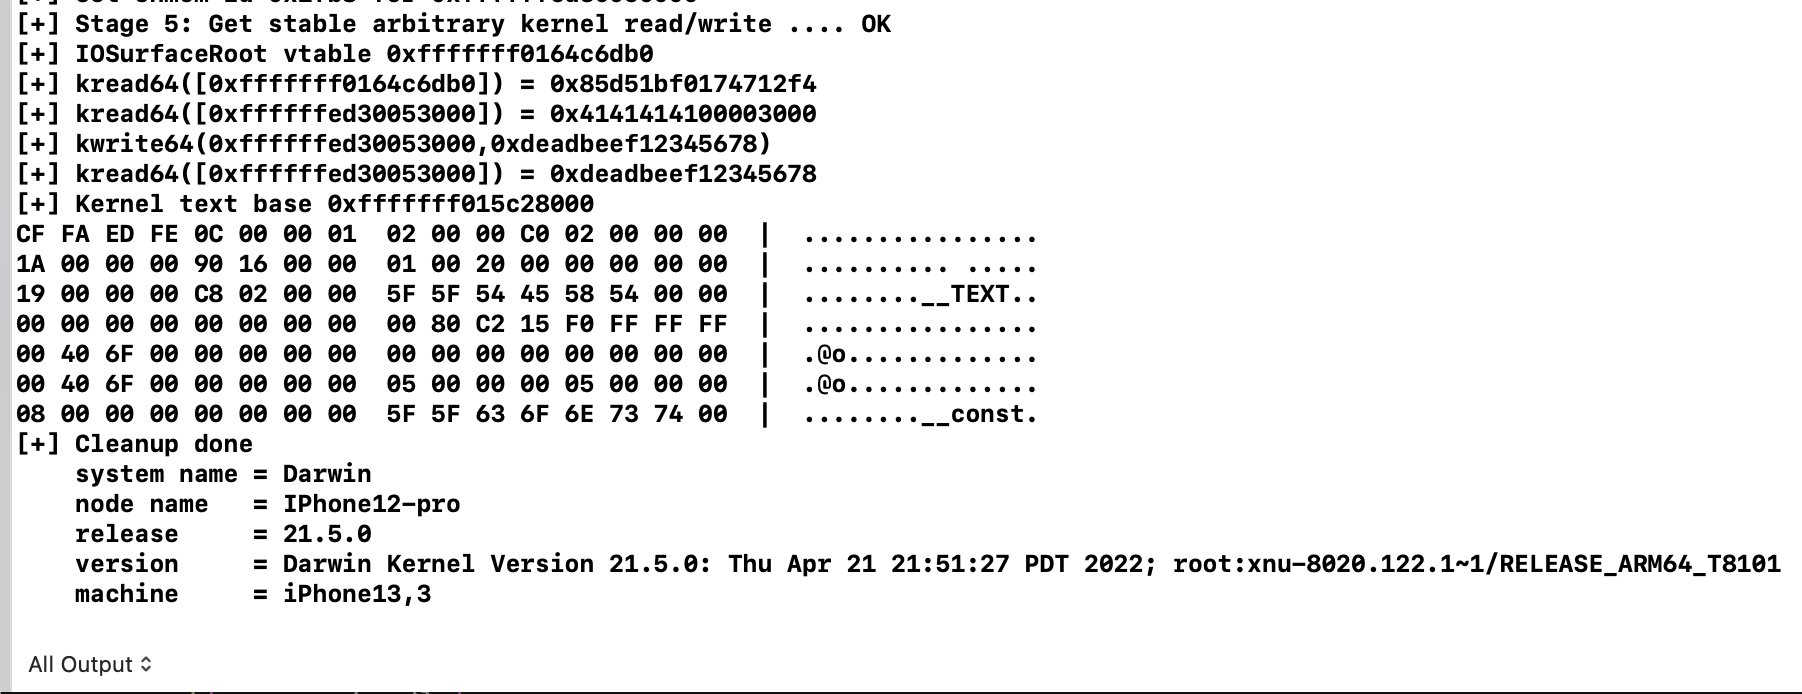
Technical analysis and exploit demonstration of CVE-2022-32898, a kernel memory corruption vulnerability in Apple Neural Engine driver, with detailed…

Technical analysis of CVE-2014-1773, a heap corruption vulnerability in Internet Explorer's MSHTML engine, with detailed crash callstack,…

metame is a metamorphic code engine for arbitrary executables

Proof-of-concept exploit for a use-after-free vulnerability in Internet Explorer's MSHTML engine, triggered via a crafted URL and documented with…