

x64dbg
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
ai-assisted-reversingbinary-analysisbinary-exploitation+7
49.7k8 days ago
x64dbg/x64dbgAn open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 czs108/windows-pe-packer
🗜️ A packer for Windows x86 executable files written in C and Intel x86 Assembly. The new file after packing can obstruct reverse…
 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
 therealdreg/ida_bochs_windows
Helper script for Windows kernel debugging with IDA Pro on native Bochs debugger (including PDB symbols)
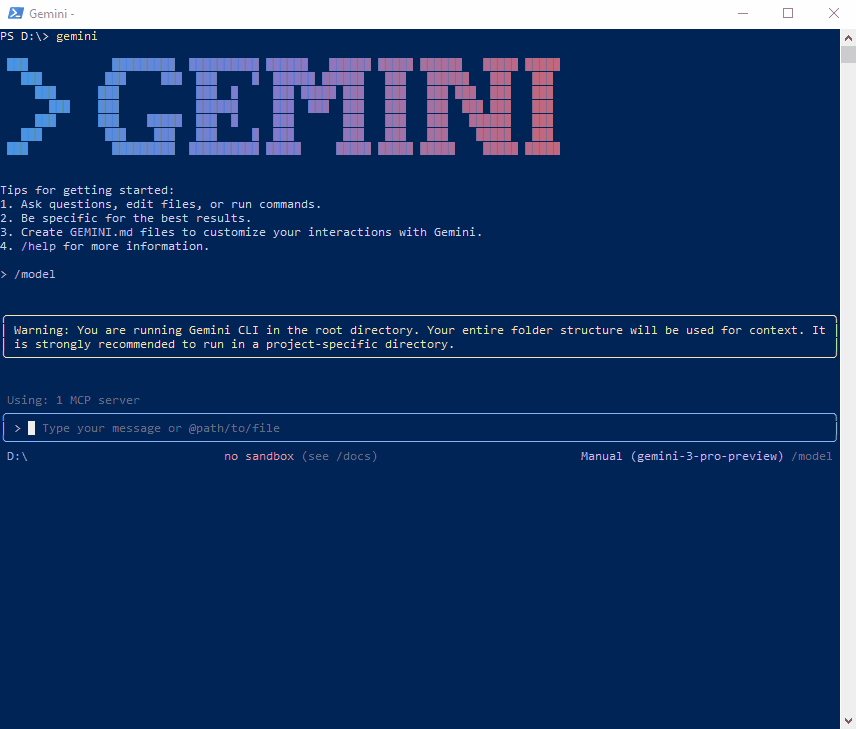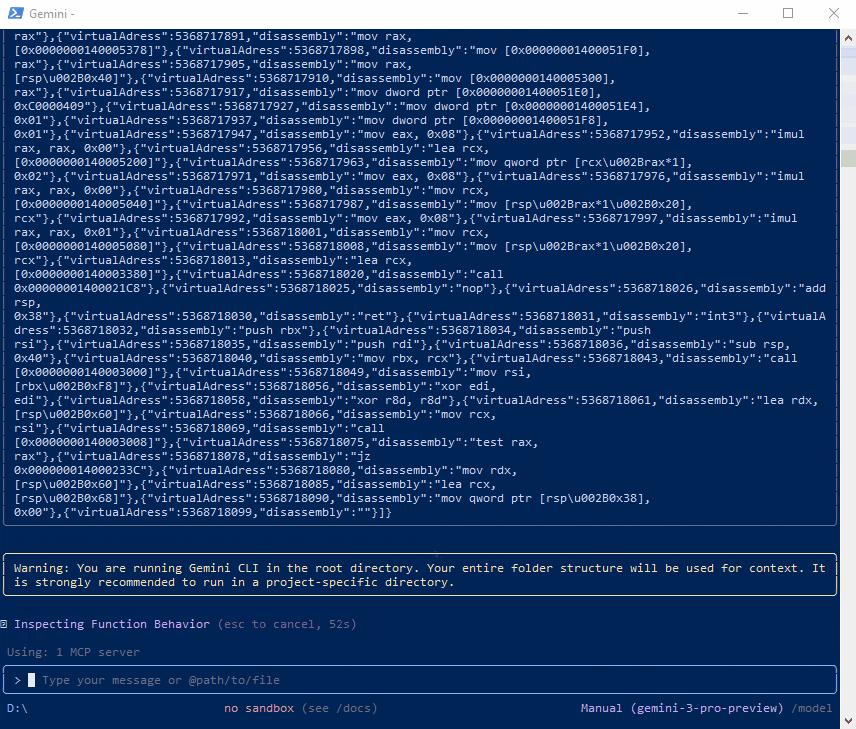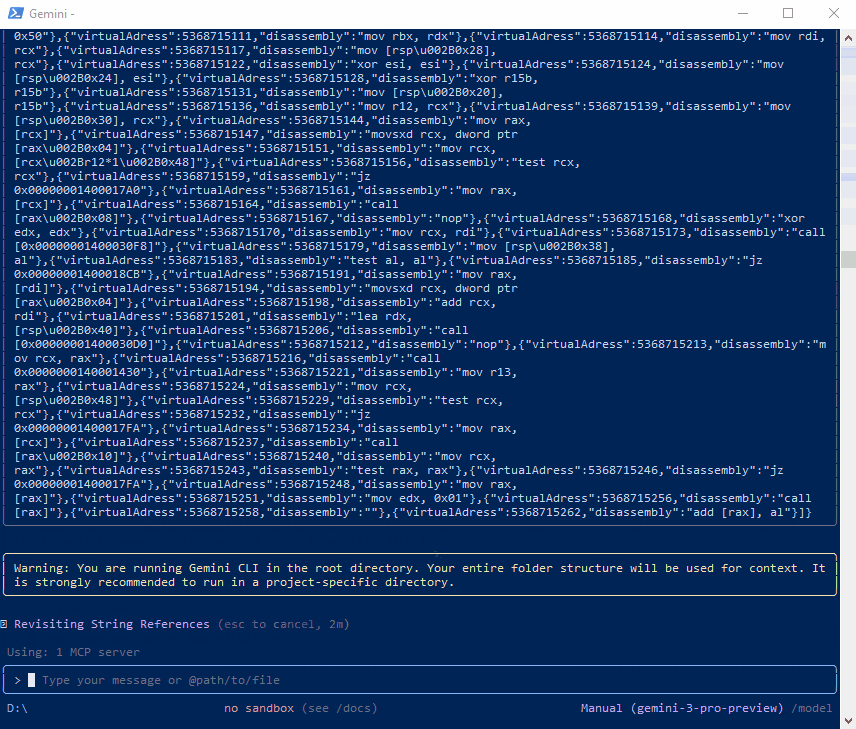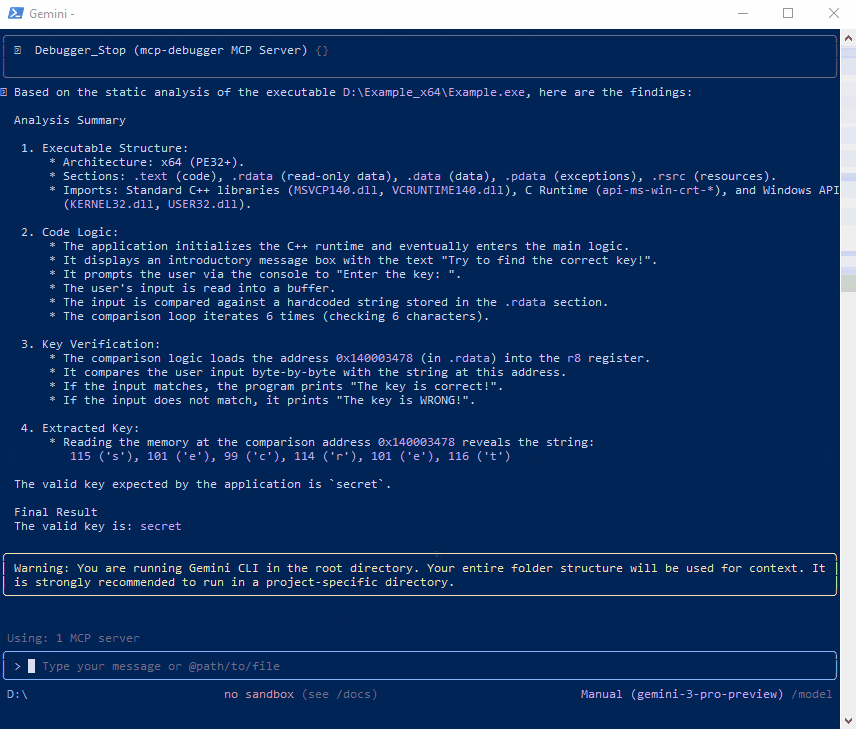 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 sentinel-one/peafl64
Static Binary Instrumentation tool for Windows x64 executables
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
 hasherezade/malware_training_vol1
Materials for Windows Malware Analysis training (volume 1)
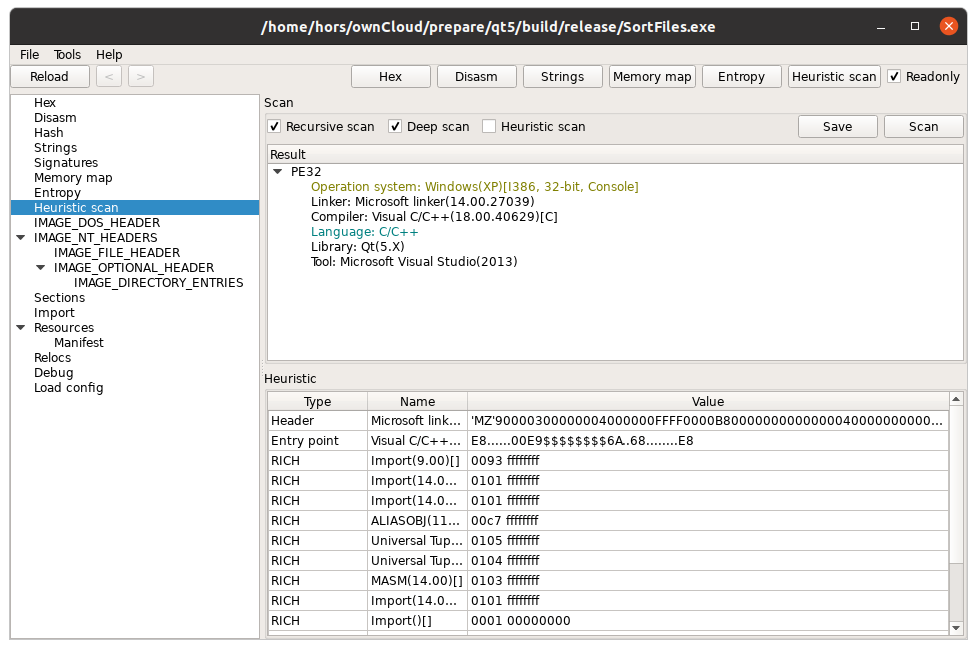 horsicq/xpeviewer
PE file viewer/editor for Windows, Linux and MacOS.
 horsicq/xmachoviewer
XMachOViewer is a Mach-O viewer for Windows, Linux and MacOS
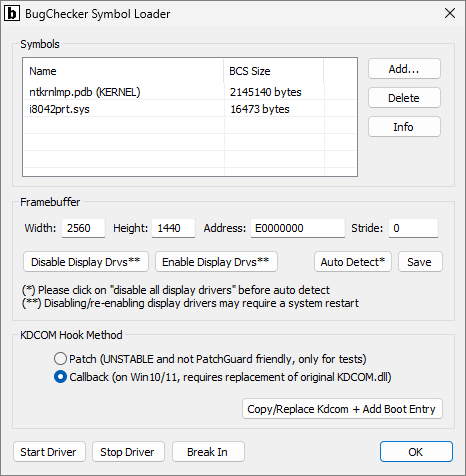 vitoplantamura/bugchecker
SoftICE-like kernel debugger for Windows 11
 notrequiem/antidbg
A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
 frank2/packer-tutorial
A tutorial on how to write a packer for Windows!
 own2pwn/r0ak
r0ak ("roak") is the Ring 0 Army Knife -- A Command Line Utility To Read/Write/Execute Ring Zero on for Windows 10 Systems