

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
74 results
capa preview

capa

GitHubmandiant/capa

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…

ai-assisted-reversingbinary-analysiscode-analysis+10
6.2k
24 days ago
frida-ios-hook preview

frida-ios-hook

GitHubnoobpk/frida-ios-hook

A tool that helps you easy trace classes, functions, and modify the return values of methods on iOS platform
binary-analysisdynamic-analysis-sandboxingios-security+3
1.2k7 months ago
Crassus preview

Crassus

GitHubvu-ls/crassus

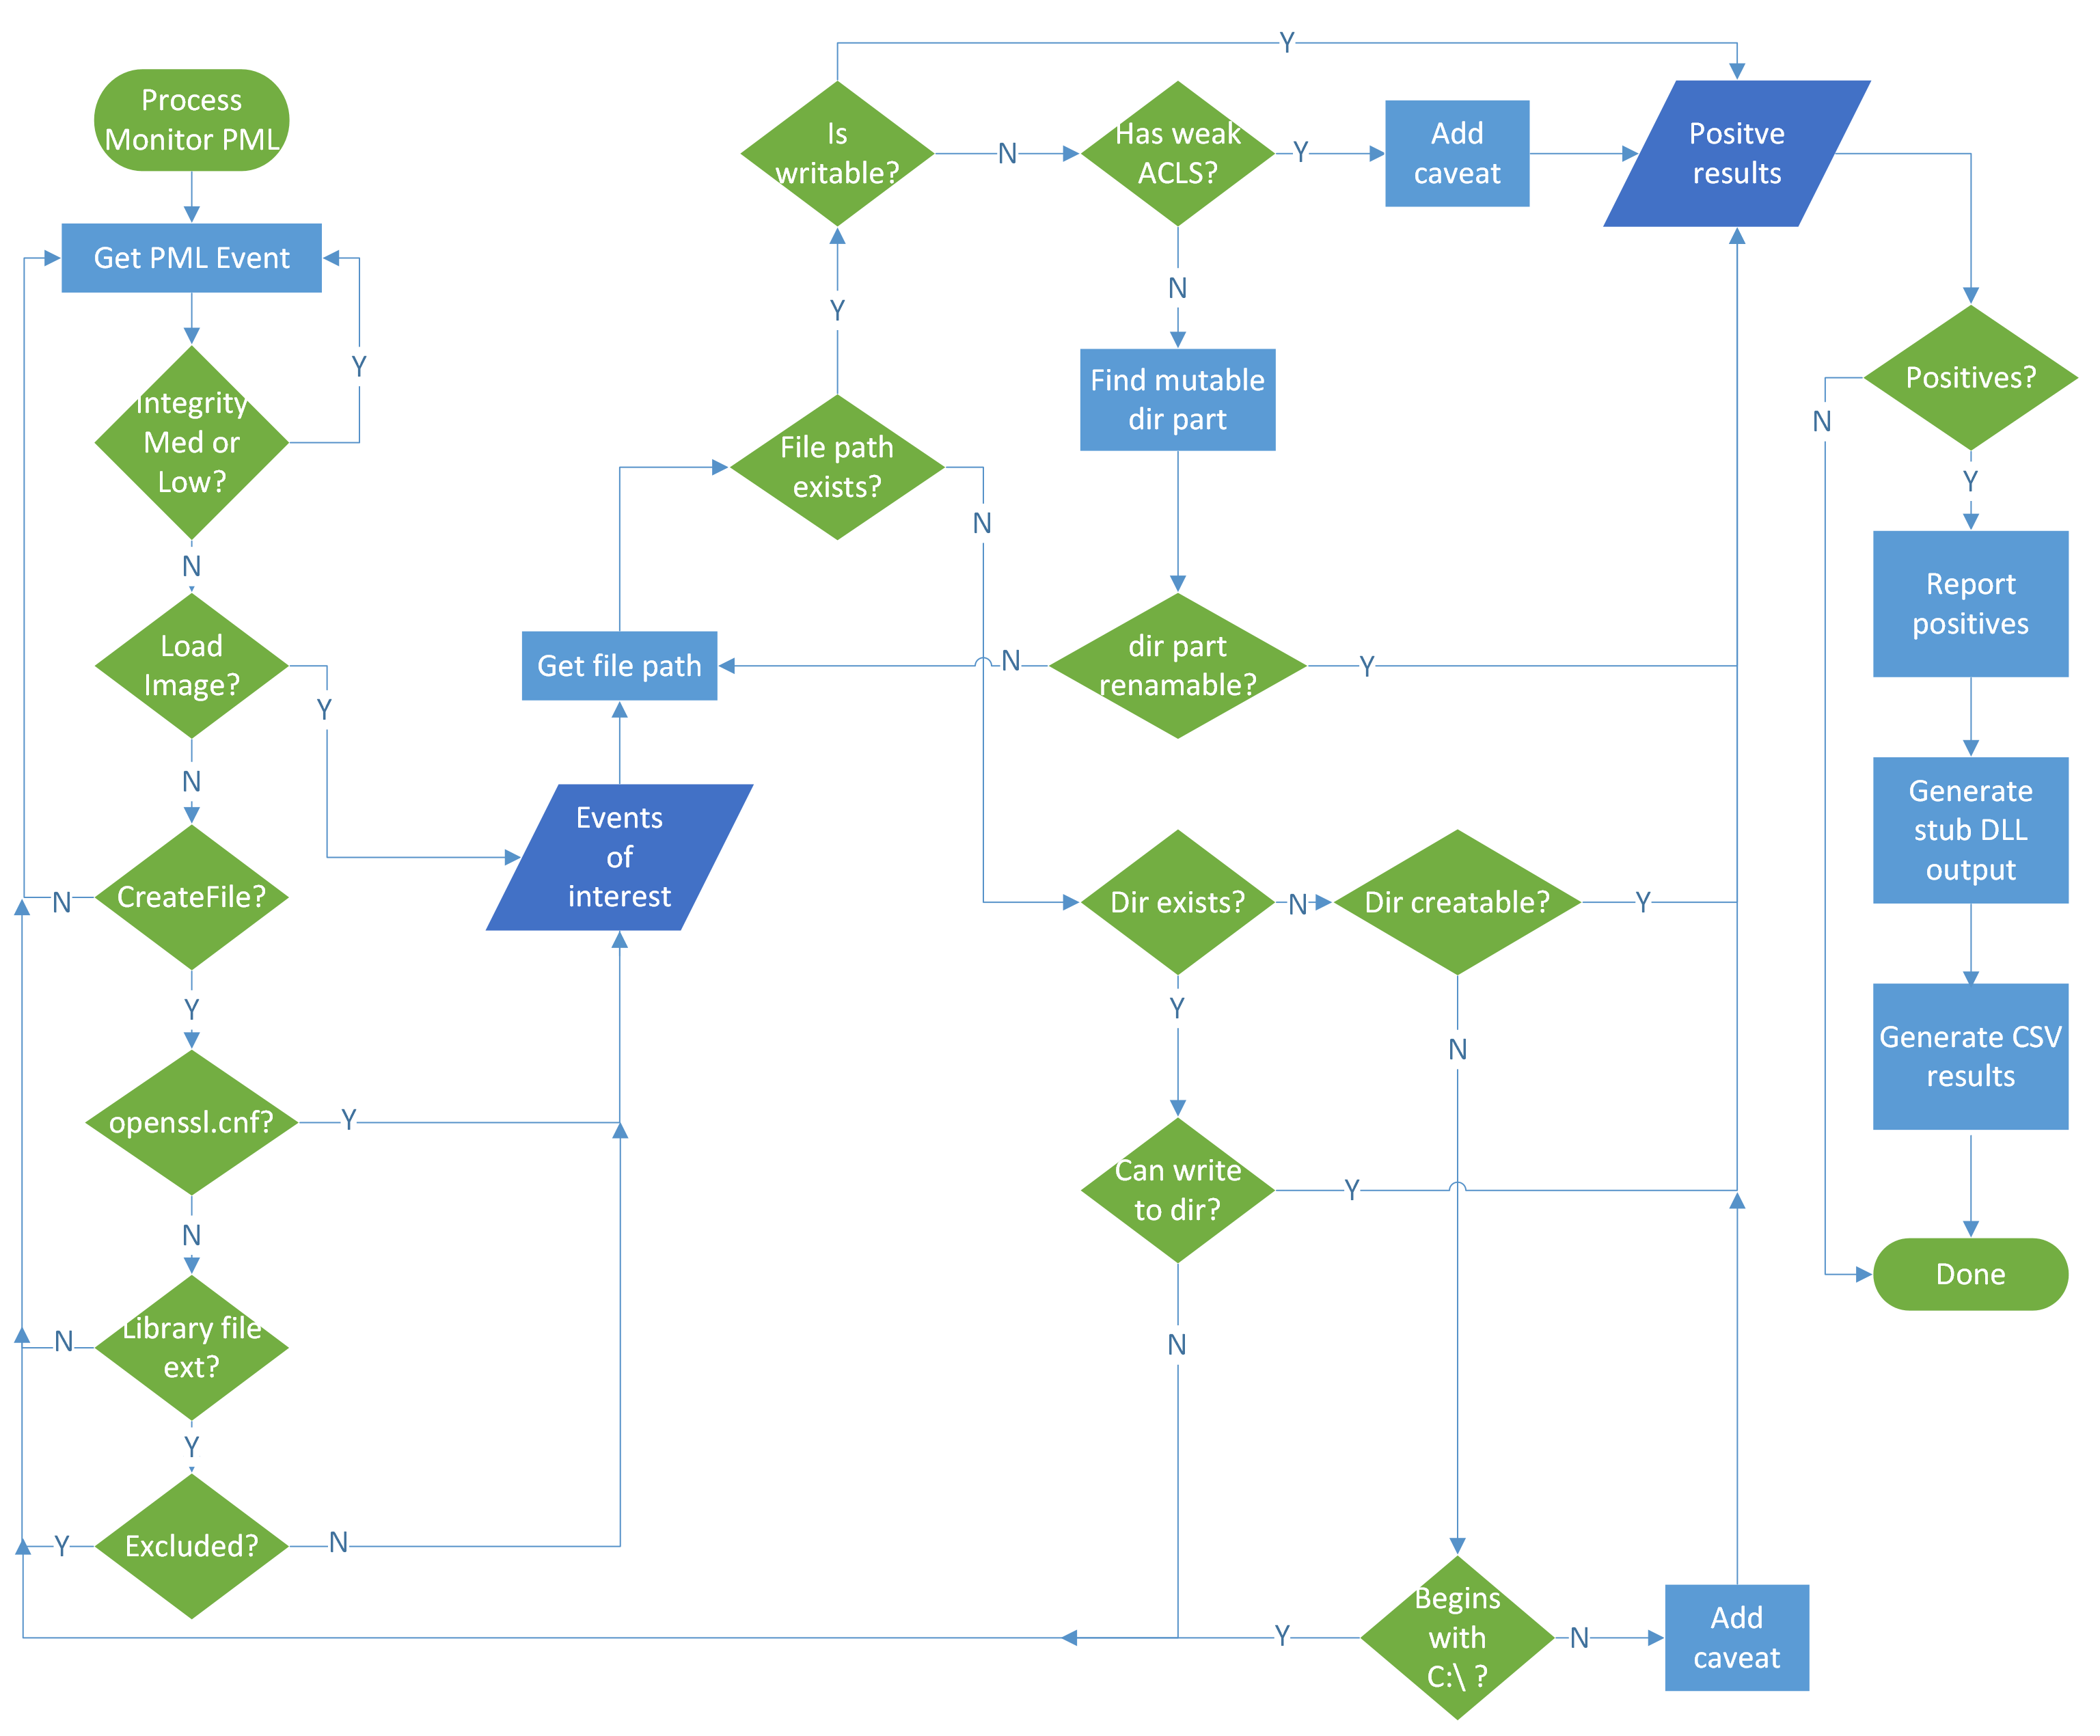
Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…
binary-analysisexploitationpenetration-testing+1
6317 months ago
ioctlance preview

ioctlance

GitHubzeze-zeze/ioctlance

A tool that is used to hunt vulnerabilities in x64 WDM drivers
binary-analysisdynamic-analysis-sandboxingexploit-frameworks+4
4733 months ago
stringsifter preview

stringsifter

GitHubmandiant/stringsifter

A machine learning tool that ranks strings based on their relevance for malware analysis.
binary-analysismachine-learningmalware-analysis+2
7643 years ago
WFH preview

WFH

GitHubconscioushacker/wfh

Frida-based dynamic analysis tool that automatically identifies DLL sideloading and COM hijacking vulnerabilities in Windows executables through…
binary-analysisdynamic-analysis-sandboxingexploitation+1
4374 years ago
windiff preview

windiff

GitHubergrelet/windiff

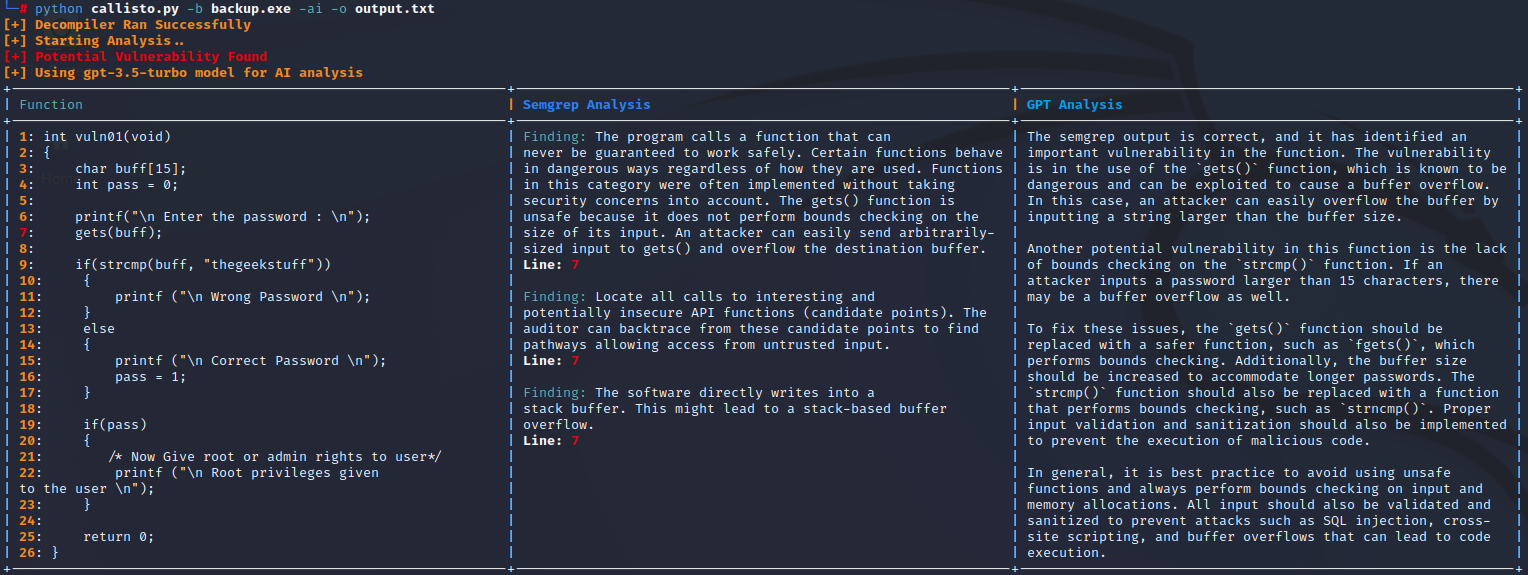
Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
binary-analysisinformation-gatheringreverse-engineering+1
3905 days ago
Callisto preview

Callisto

GitHubjetp1ane/callisto

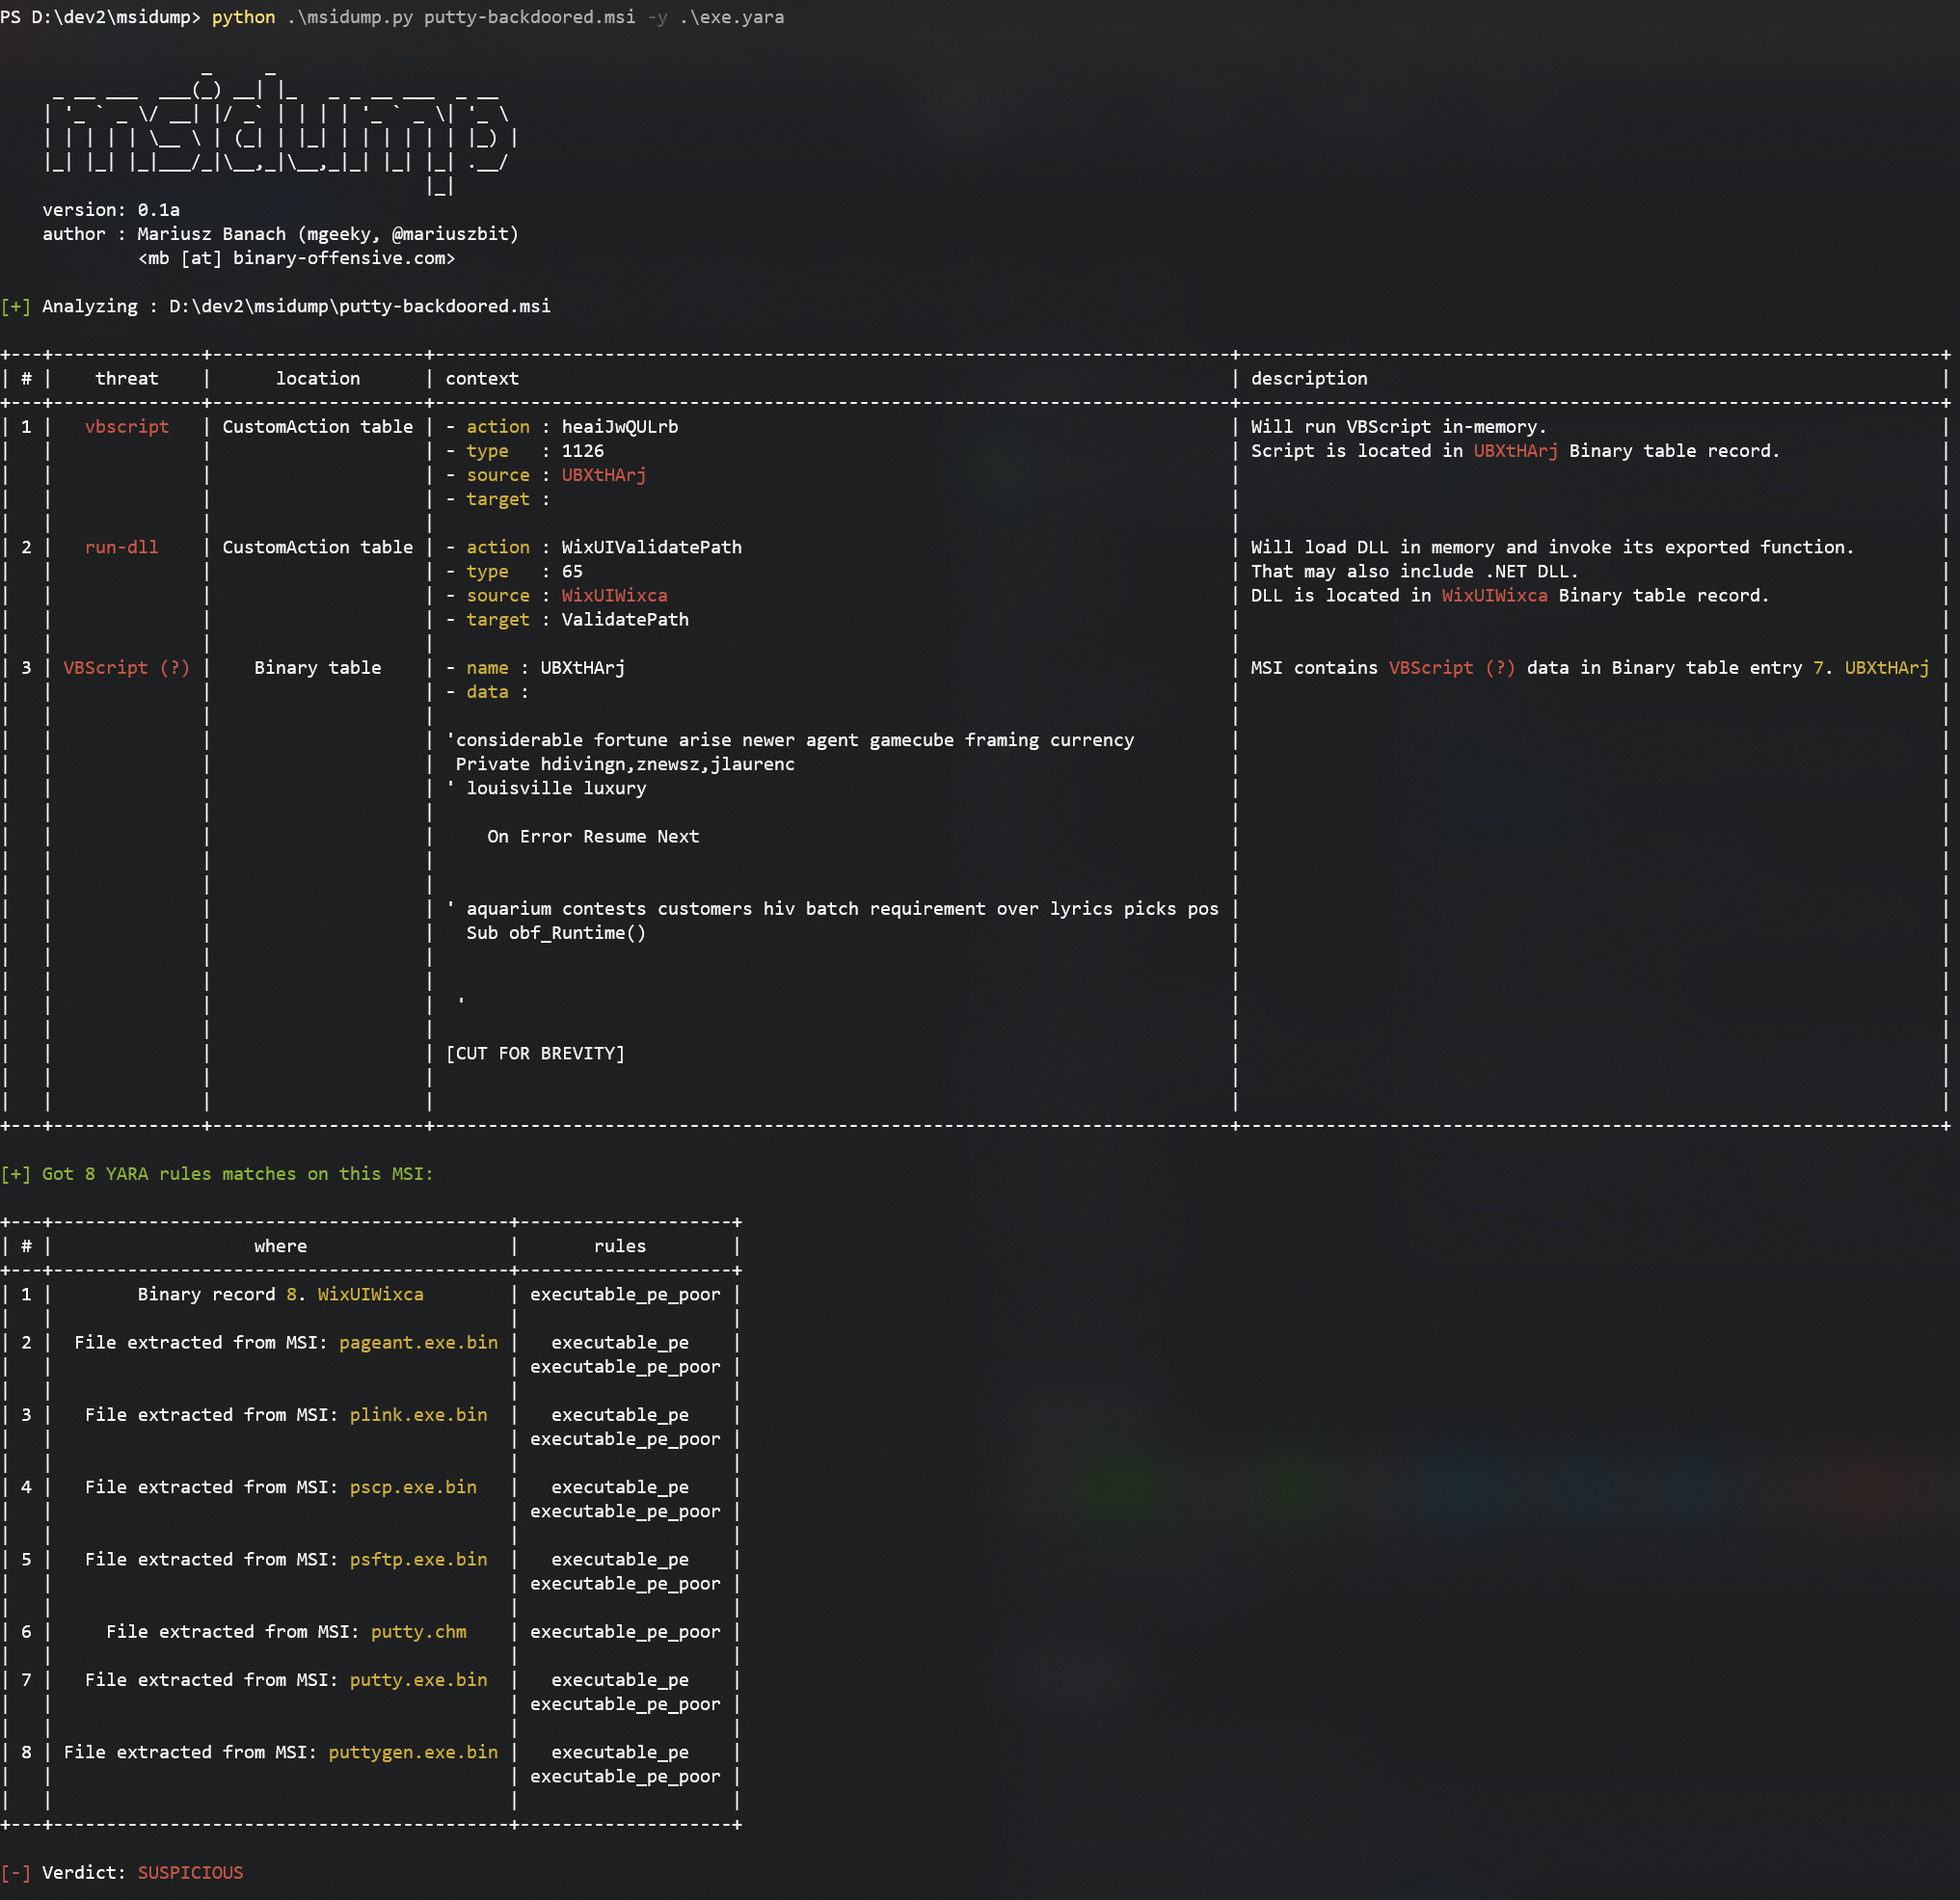
Automated binary vulnerability analysis tool that decompiles executables via Ghidra, scans pseudo-C code with Semgrep, and validates findings using…
ai-assisted-reversingbinary-analysisreverse-engineering+2
3703 years ago
msidump preview

msidump

GitHubmgeeky/msidump

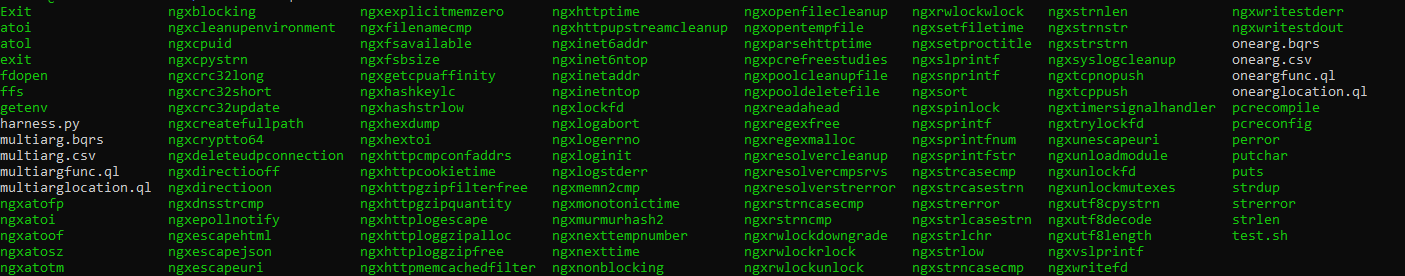
MSI Dump - a tool that analyzes malicious MSI installation packages, extracts files, streams, binary data and incorporates YARA scanner.
binary-analysisforensicsmalware-analysis+1
2323 years ago
autoharness preview

autoharness

GitHubparikhakshat/autoharness

A tool that automatically creates fuzzing harnesses based on a library
binary-analysiscode-analysisfuzzing+1
2954 years ago
IDA2Obj preview

IDA2Obj

GitHubjhftss/ida2obj

Static binary instrumentation tool that dumps COFF object files from executables, enabling code/data insertion at any location for black-box fuzzing…
binary-analysisdebuggersfuzzing+2
1225 years ago
Bypass-Sandbox-Evasion preview

Bypass-Sandbox-Evasion

GitHubzeromemoryex/bypass-sandbox-evasion

C++ tool that patches Windows API calls to bypass sandbox RAM size checks, enabling malware to evade detection in isolated analysis environments.

anti-botbinary-analysisids-ips-evasion+1
1413 years ago
aDLL preview

aDLL

GitHubideaslocas/adll

Automated DLL hijacking vulnerability discovery tool that analyzes PE binaries at load-time and runtime via API hooking, enumerating missing DLLs and…
binary-analysisdynamic-analysis-sandboxingexploitation+1
735 years ago
StegoScan preview

StegoScan

GitHublcbower33/stegoscan

Automated steganography detection tool that scans websites, web servers, and local directories using AI-driven object/text recognition and deep file…

ai-securitybinary-analysiscrawler+7
1091 year ago
patriot preview

patriot

GitHubjoe-desimone/patriot

In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…

anomaly-detectionbinary-analysisdefensive-tools+3
1654 years ago
aether preview

aether

GitHub0xsp-srd/aether

Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
binary-analysiscommand-and-controldigital-forensics+7
672 months ago
columbo preview

columbo

GitHubvisma-prodsec/columbo

ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…
anomaly-detectionbinary-analysisdigital-forensics+3
614 years ago
NullSection preview

NullSection

GitHubmatheuzsecurity/nullsection

ELF anti-reversing tool that overwrites section headers with nullbytes to prevent static analysis by disassemblers and debuggers, rendering functions…

anti-botbinary-analysiseducation+2
673 years ago
Previous12345Next