RTCore64-probe
 crowthearchfiend/rtcore64-probe
A tiny cpp program to test reading memory using a vulnerable RTCore64.sys driver/device (CVE-2019-16098). It tries to read a "secret" from its own…
binary-analysisexploitationhardware-security+2
crowthearchfiend/rtcore64-probeA tiny cpp program to test reading memory using a vulnerable RTCore64.sys driver/device (CVE-2019-16098). It tries to read a "secret" from its own…
 xoreaxeaxeax/schrodingers-toctou
Detect compiler-invented memory loads that turn secure C into TOCTOU vulnerabilities. Includes automated source audits, Unicorn-based binary…
 lfi-project/lfi
Top-level repository for LFI: Practical, Efficient, and Secure Software-based Sandboxing
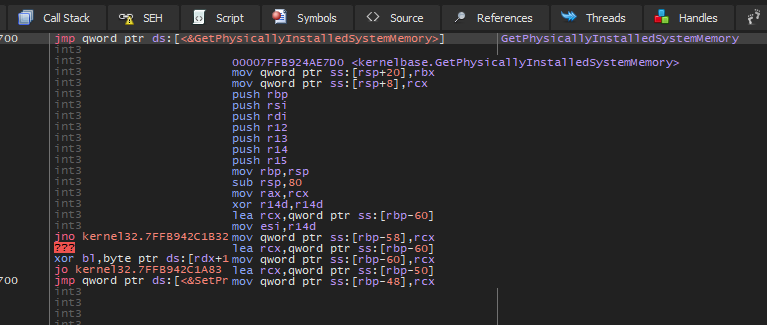 zeromemoryex/bypass-sandbox-evasion
C++ tool that patches Windows API calls to bypass sandbox RAM size checks, enabling malware to evade detection in isolated analysis environments.
 themalwareguardian/cve-2025-4275
Analysis and exploitation of CVE-2025-4275 (Hydr0ph0bia), a Secure Boot trust-chain weakness where firmware variables are used to introduce…
 trinadh465/platform_external_libvpx_v1.8.0_cve-2023-5217
Patched libvpx codebase addressing CVE-2023-5217 with sanitizer support and cross-platform build configurations for secure VP8/VP9 encoding.
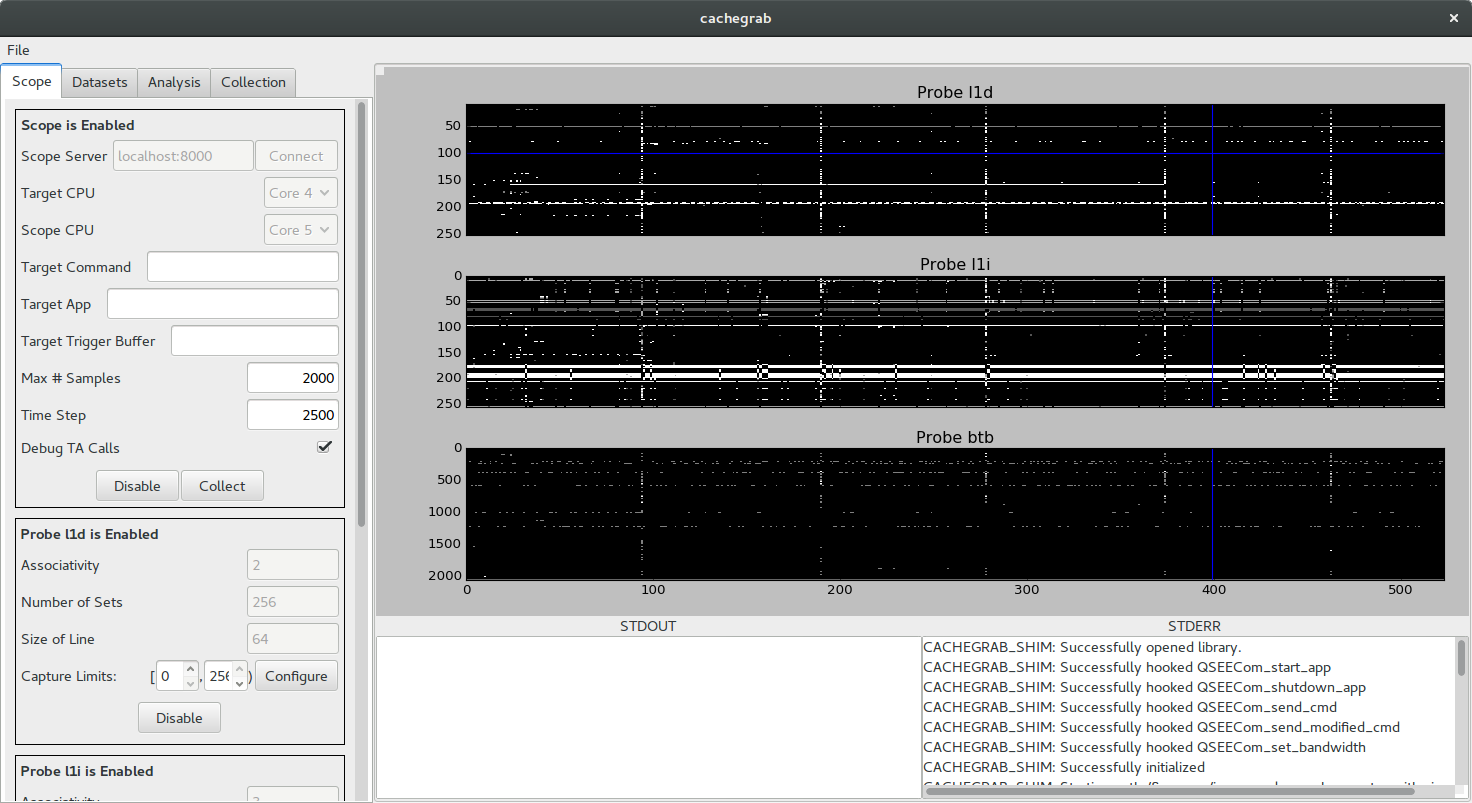 nccgroup/cachegrab
a tool designed to help perform and visualize trace-driven cache attacks against software in the secure world of TrustZone-enabled ARMv8 cores
 timon-l/3007project
Secure coding project, research on CVE-2019-17498 and implement a player score function written in C.
 google/silifuzz
Fuzzes CPU implementations by generating test inputs from software proxies, then executes them on real hardware to detect microarchitecture defects…
 demining/phoenix-rowhammer-attack-cve-2025-6202
Phoenix Rowhammer Attack: Systemic Risk of Bitcoin Wallet Private Key Compromise in Global Blockchain Infrastructure Due to a Critical SK Hynix DDR5…
 themalwareguardian/cve-2026-79298
Research repository documenting CVE-2026-79298, an incomplete UEFI Secure Boot bypass remediation in Howyar SysReturn's IA-32 boot path, with reverse…
 mav3r1ck0x1/cve-2023-23583-reptar-
This script can help determine the CPU ID for the processor of your system, please note that I have not added every CPU ID to this script, edit as…
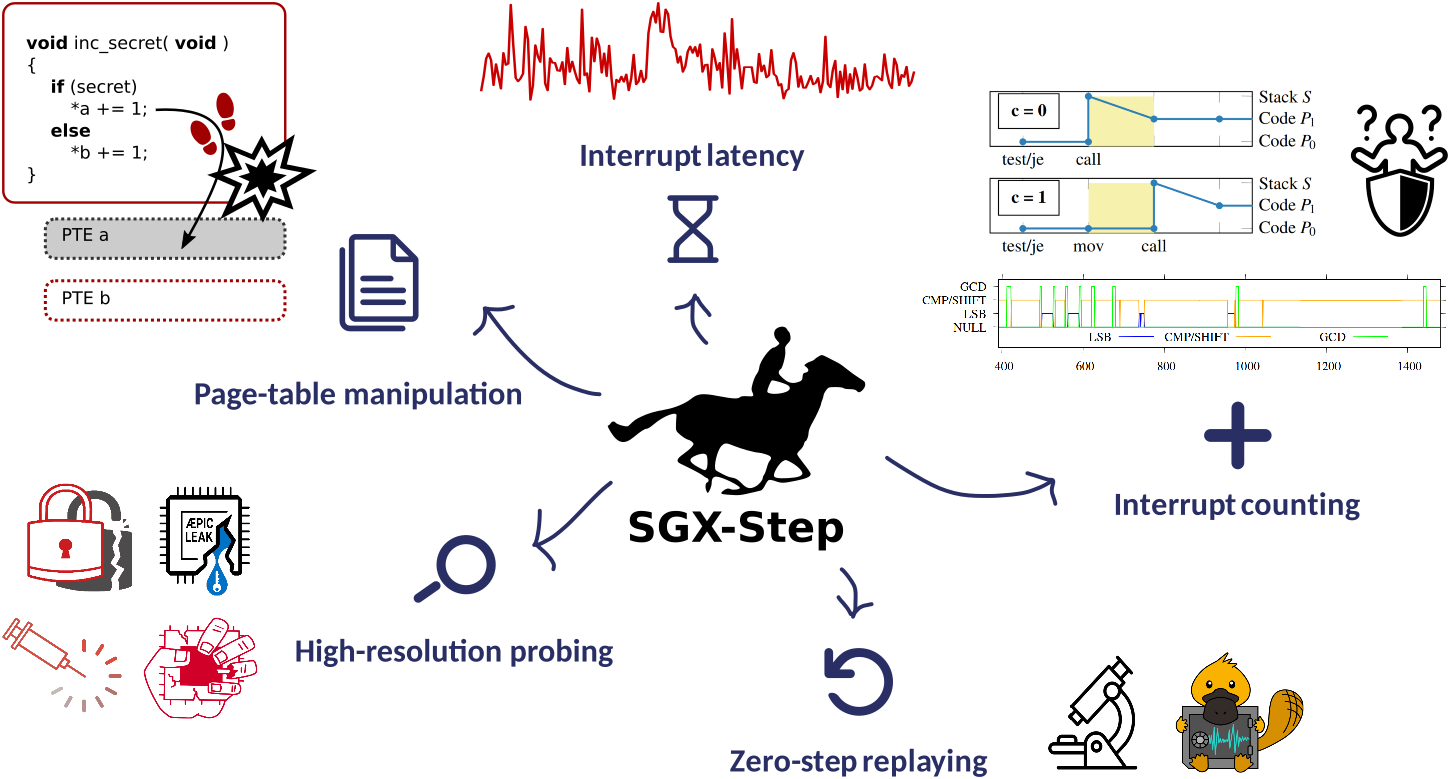 jovanbulck/sgx-step
A practical attack framework for precise enclave execution control
 harshrajsinghania/cve-2026-90782-s2opc-status-clobber
Standalone PoC for CVE-2026-90782: status-clobbering NULL dereference in S2OPC alloc_notification_message_items() (DataChange fails, Event succeeds)
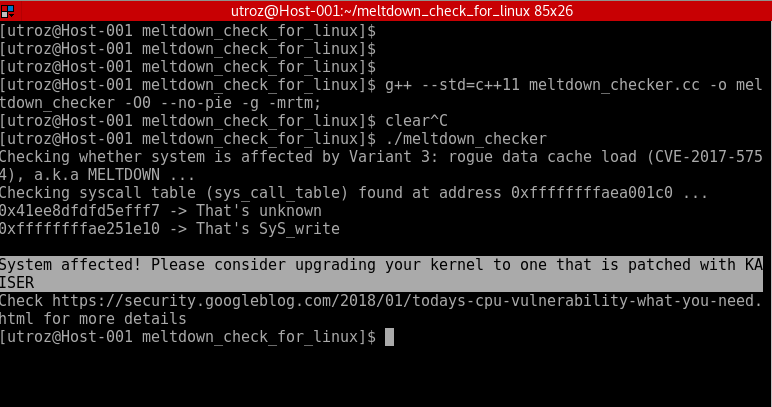 raphaelsc/am-i-affected-by-meltdown
Meltdown Exploit / Proof-of-concept / checks whether system is affected by Variant 3: rogue data cache load (CVE-2017-5754), a.k.a MELTDOWN.
 typeconfused/cve-2025-14174-analysis
Analysis and PoC for CVE-2025-14174 - ANGLE Metal OOB write (iOS Safari, macOS Chrome)