
Hunt-Sleeping-Beacons
 theflink/hunt-sleeping-beacons
Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…
binary-analysisdefensive-toolsforensics+3
688
theflink/hunt-sleeping-beaconsCallstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…
 nickcano/xenoscan
Open source memory scanner written in C++
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
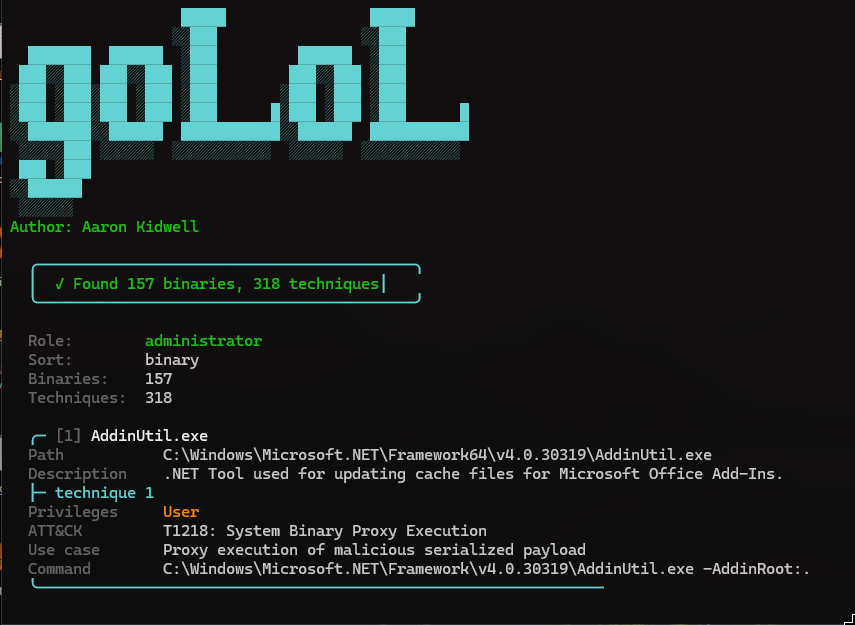 aaron-kidwell/golol
goLoL is a Windows host scanner with dual support for LOLBAS binaries and LOLDrivers. It lists LOLBAS techniques runnable at your current privilege…
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
 shcesama/cve-2023-4863-analysis
Educational analysis of CVE-2023-4863 (libwebp heap buffer overflow) with Blue Team detection tools, static WebP scanner, defensive Java validator,…
 adem-hosni/mappedimagesdetector
Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk
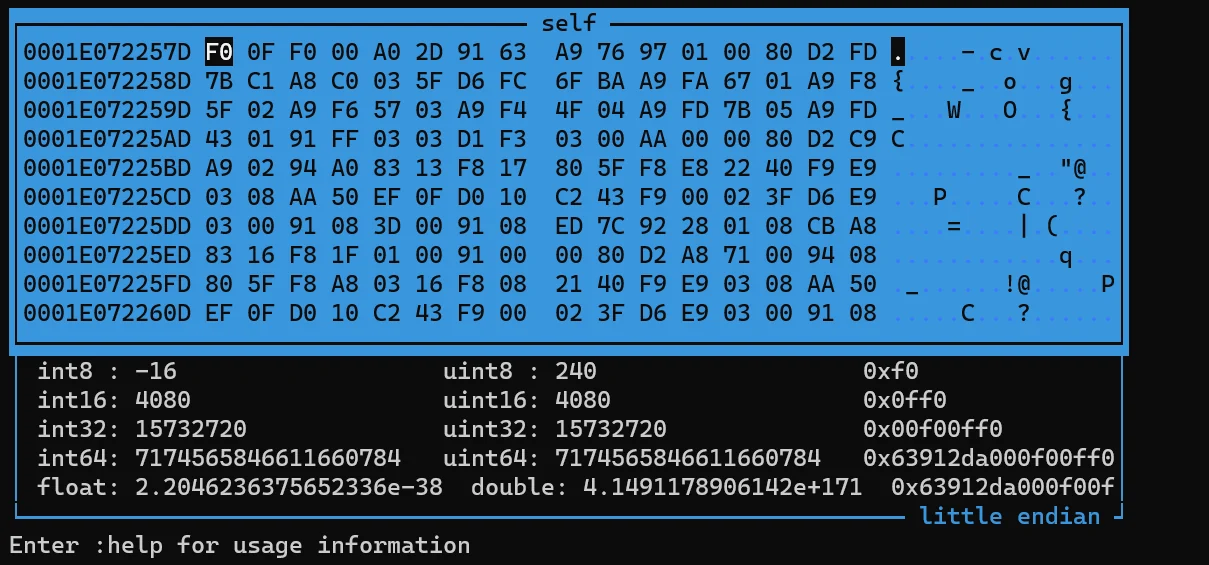 gmh5225/frida-medit
Cross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…
 backdoorskid/win-def-clickfix
A scanner that estimates whether Microsoft Defender is likely to flag a command as ClickFix.
 gmh5225/ollytlscatch
OllyDbg plugin that intercepts and dumps TLS/SSL plaintext traffic during debugging sessions, aiding reverse engineering and malware analysis of…
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 robertcprice/ncpu
Research runtime for differentiable neural computers, GPU-based CPU emulation, and program synthesis. Features neural ALU, constant-time crypto, JEPA…
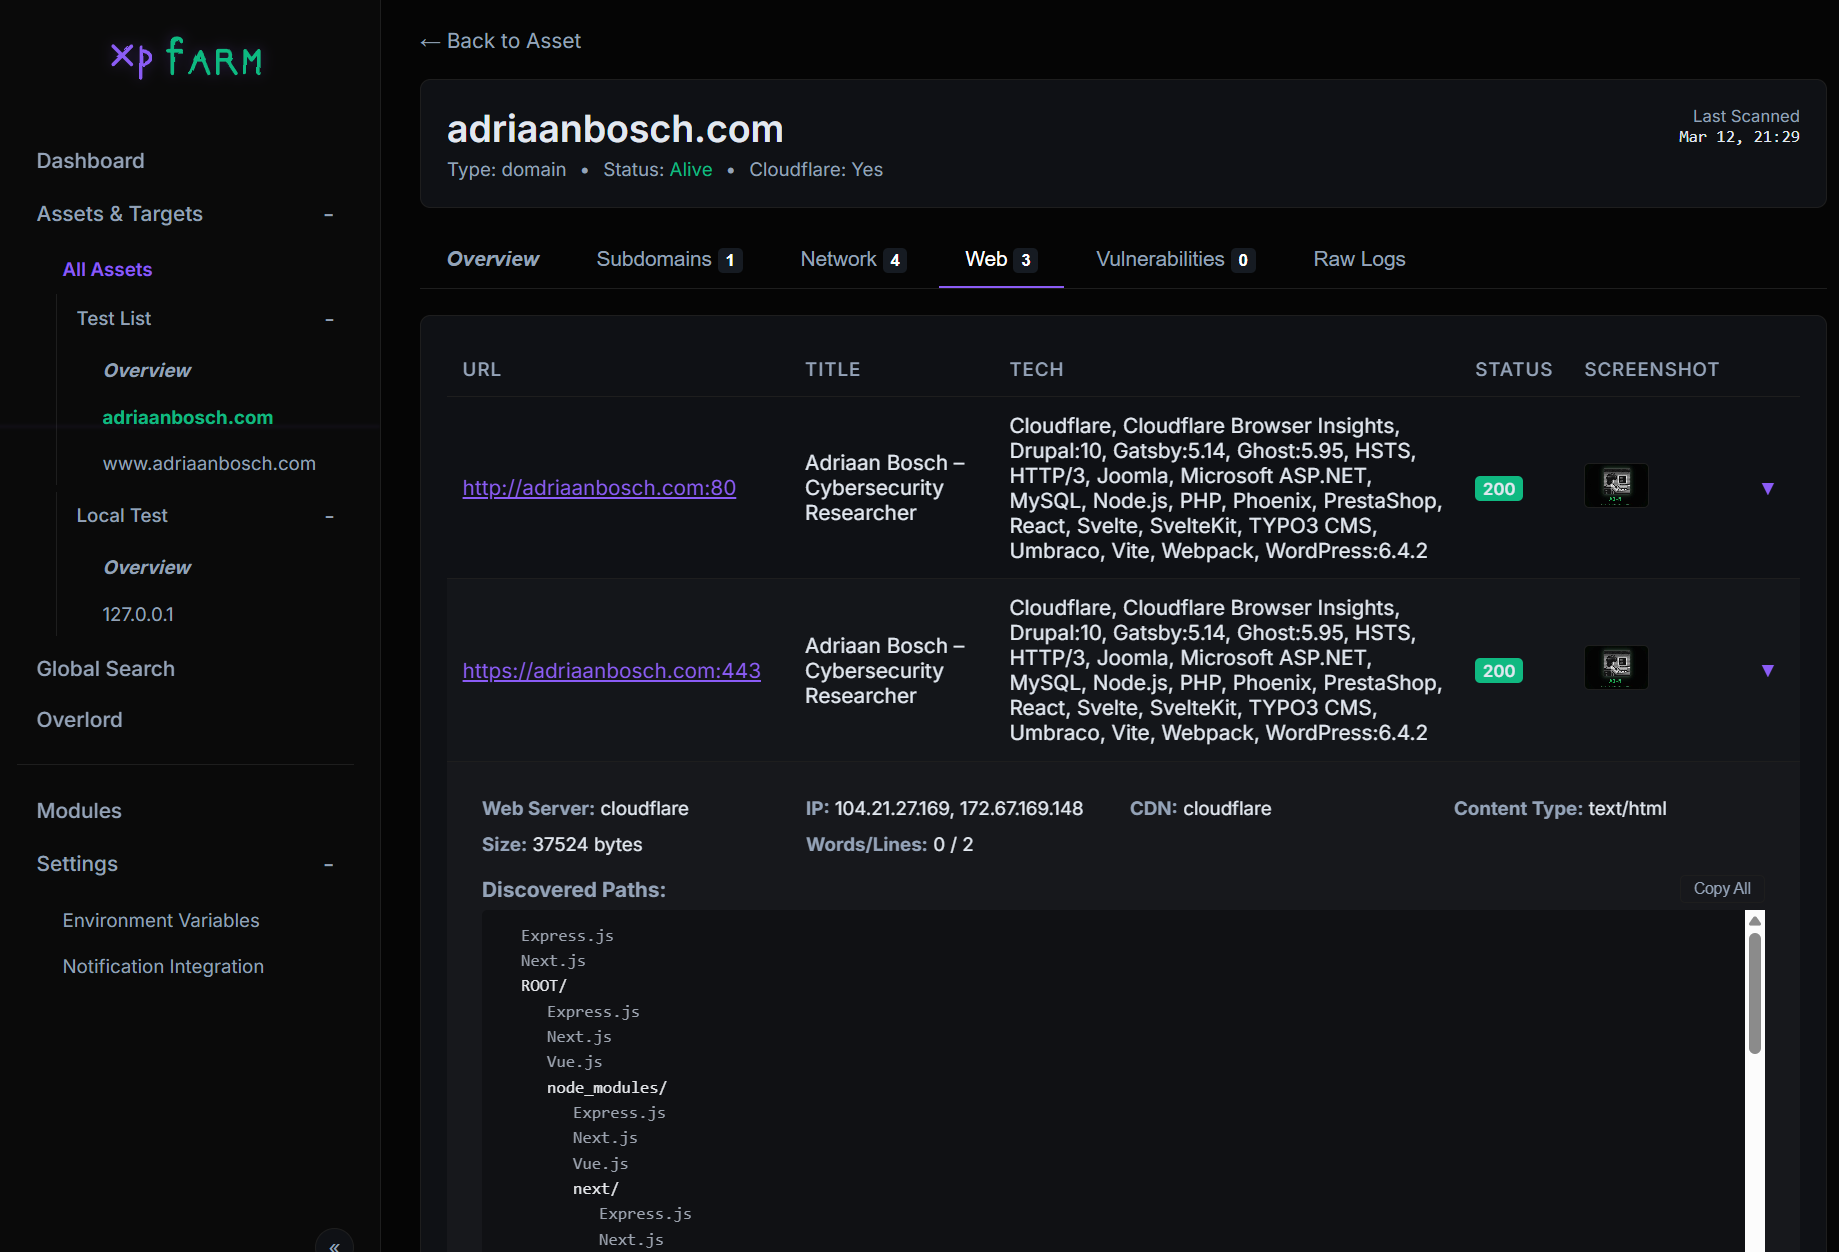 a3-n/xpfarm
Free XP on bug bounty, vulnerability scanning by wrapping well maintained tools, to perform automated tests. Alongside AI agents for binary analysis,…
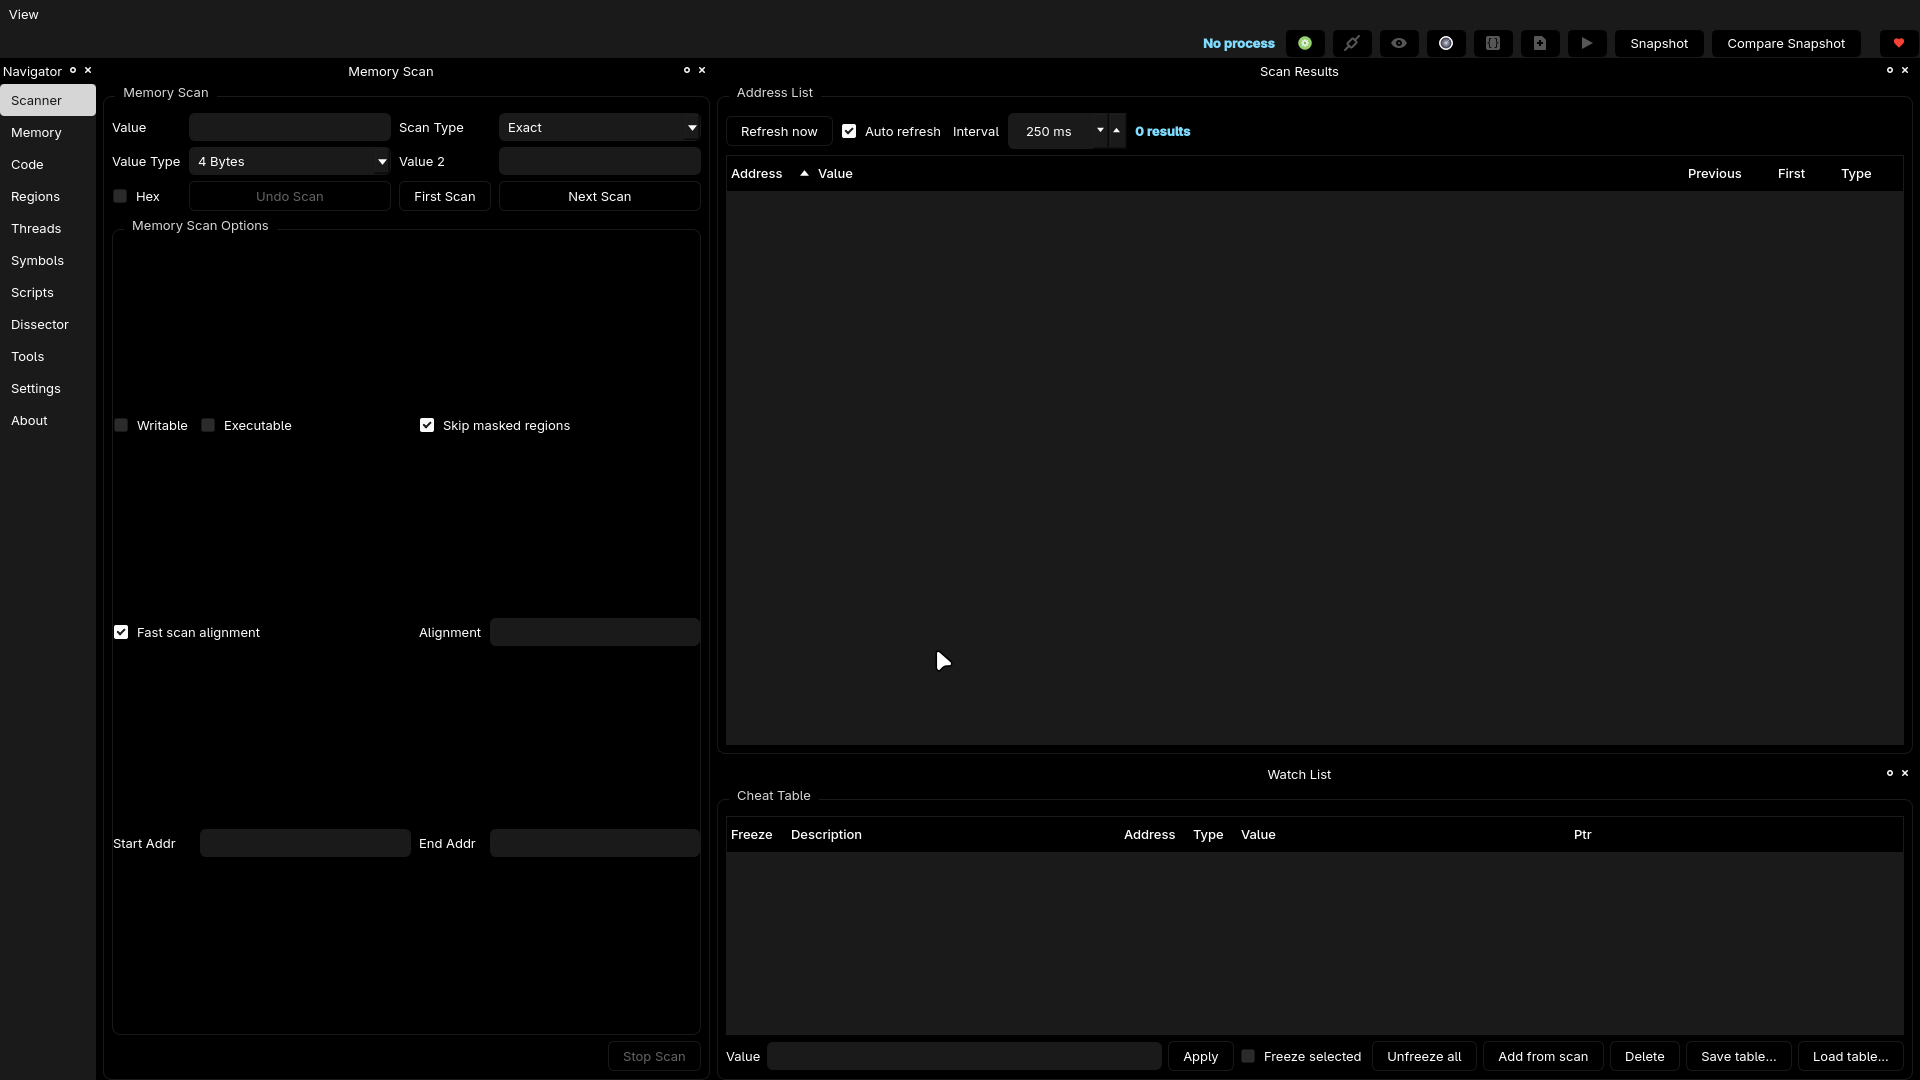 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 maximilianfeix/hexvero
Know what changed inside your Electron release: diff two builds for IPC, preload, windows, fuses and hosts, with file:line. CLI, CI gate, MCP server.
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.