

V8Harvest
 star-sg/v8harvest
Curated dashboard for browsing recent V8 vulnerability patterns, parsing regression test files with linked Chromium bug reports, code reviews, and…
binary-analysiscurated-resourceseducation+2
35
star-sg/v8harvestCurated dashboard for browsing recent V8 vulnerability patterns, parsing regression test files with linked Chromium bug reports, code reviews, and…
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 pxb1988/dex2jar
Tools to work with android .dex and java .class files
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
 codinggay/blackdex
Android APK unpacker that dumps DEX files from running or installed apps on Android 5.0–12 without root, Xposed, or Frida, supporting deep unpacking…
 erocarrera/pefile
pefile is a Python module to read and work with PE (Portable Executable) files
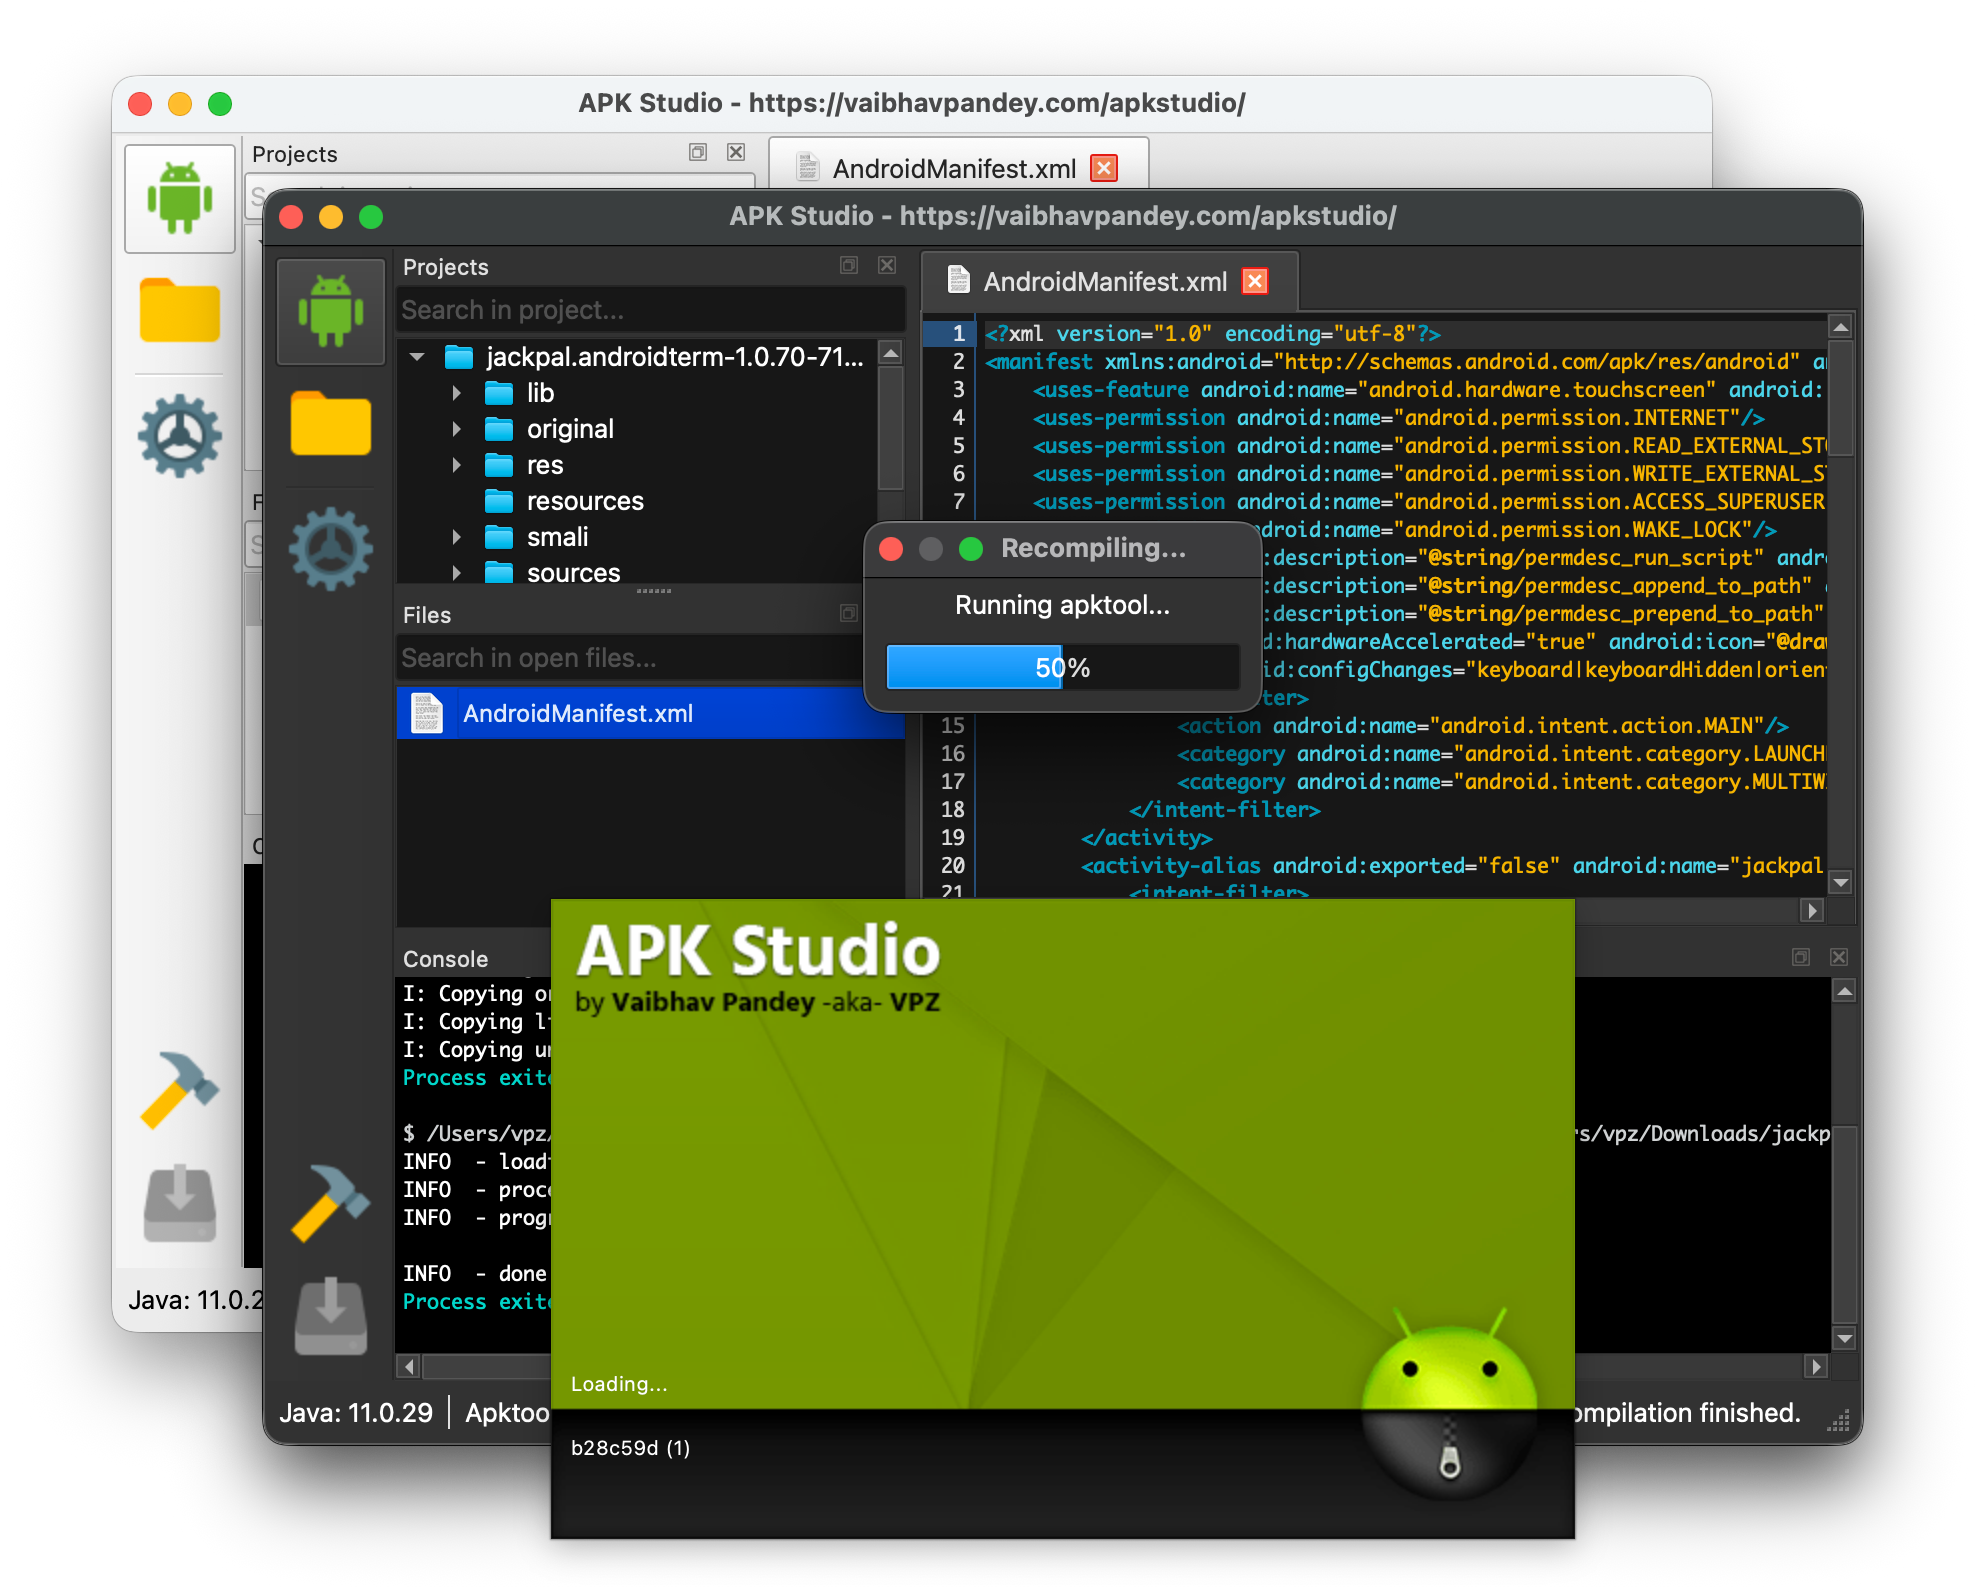 vaibhavpandeyvpz/apkstudio
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
 kjcracks/clutch
Jailbreak-only iOS utility that decrypts installed app executables and dumps them as .ipa or raw binary files for security research and…
 nygard/class-dump
Generate Objective-C headers from Mach-O files.
 onekey-sec/unblob
Extract files from any kind of container formats
 sashs/ropper
Display information about files in different file formats and find gadgets to build rop chains for different architectures (x86/x86_64, ARM/ARM64,…
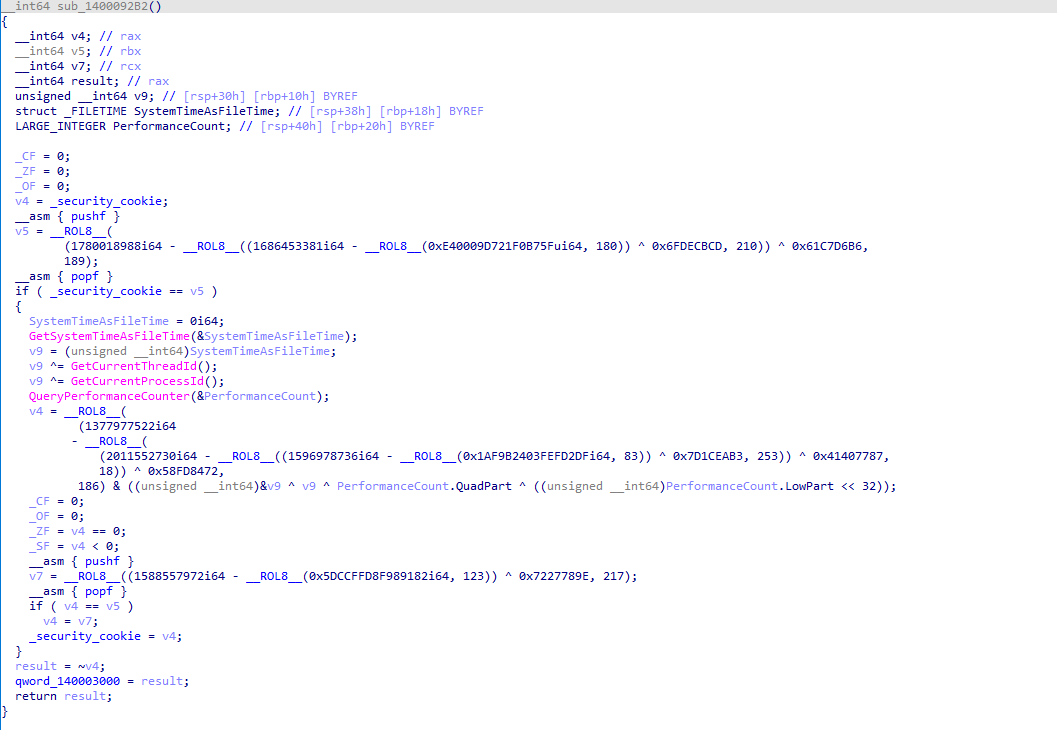 weak1337/alcatraz
x64 binary obfuscator for PE files with control flow flattening, anti-disassembly, import obfuscation, and instruction mutation to hinder reverse…
 washi1337/asmresolver
A library for creating, reading and editing PE files and .NET modules.
 trustedsec/coffloader
Run Beacon Object Files (BOFs) outside Cobalt Strike by parsing 64-bit COFF object files, with Beacon-compatible argument generation and helper…
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.