MalwareForge---Advanced-Static-Malware-Analyzer

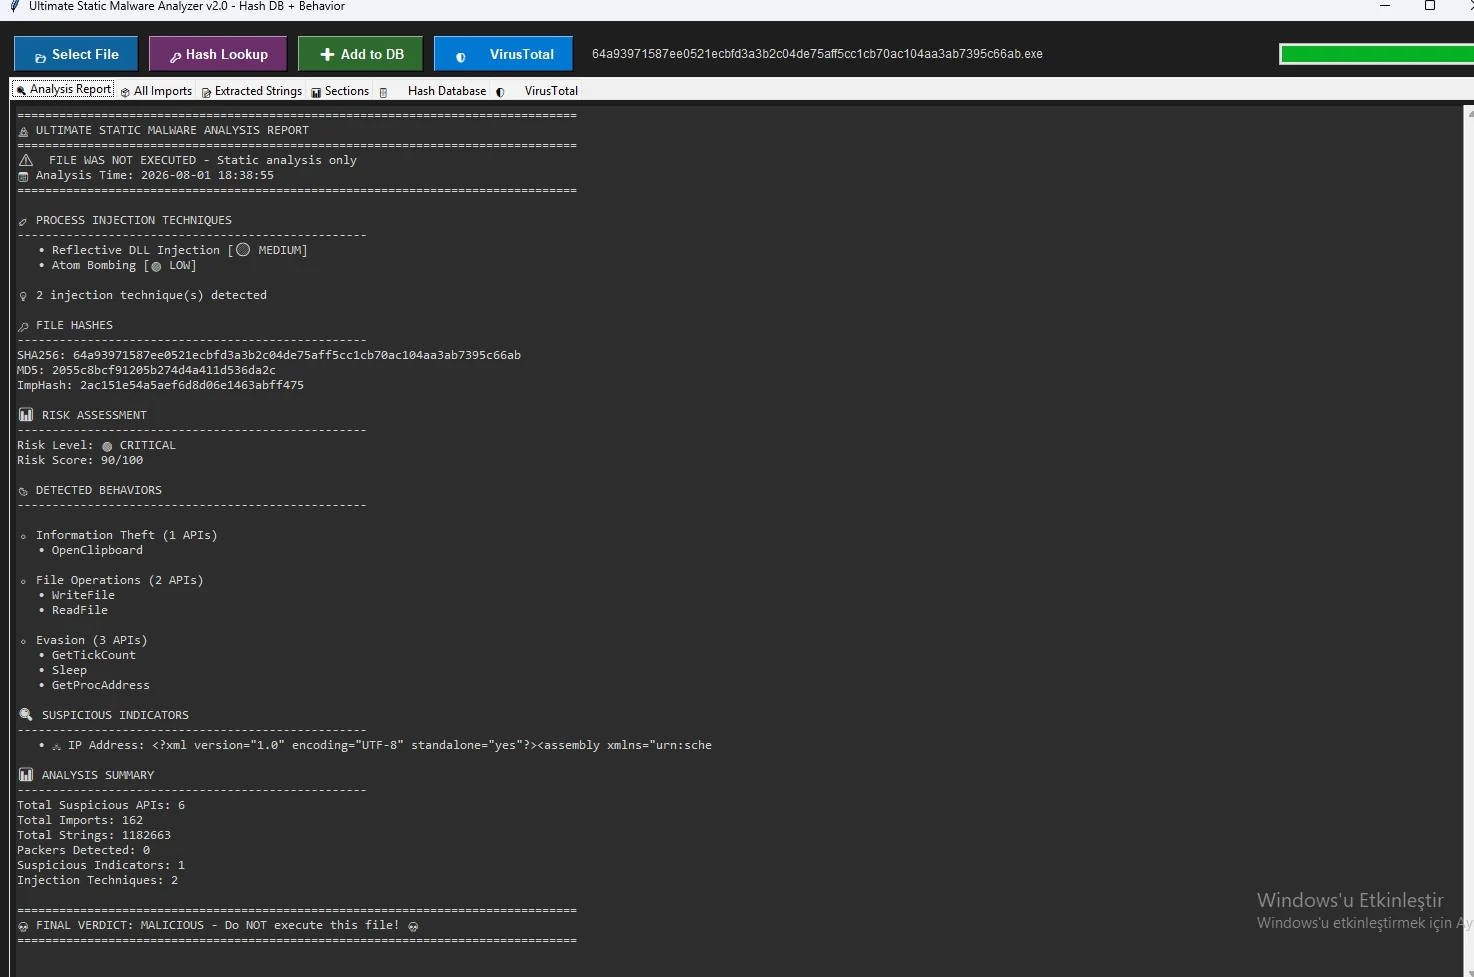
Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…

Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…

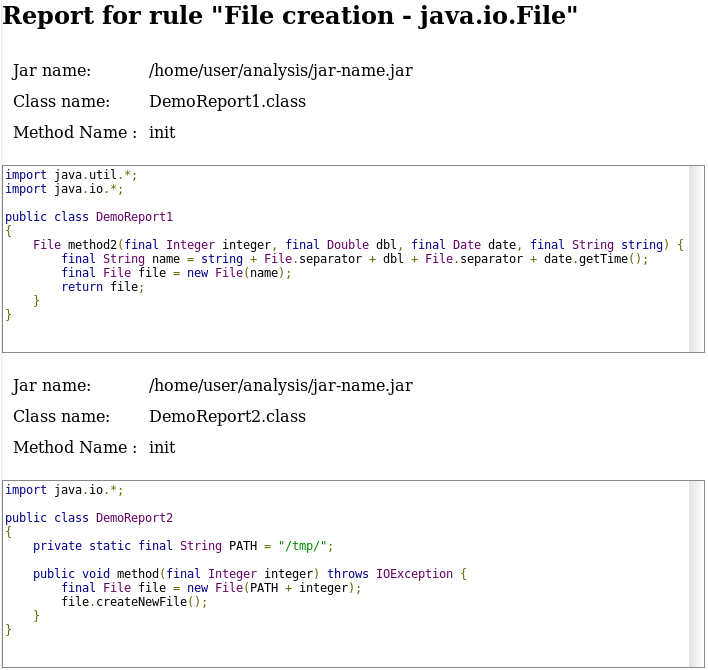
Java bytecode analyzer customizable via JSON rules

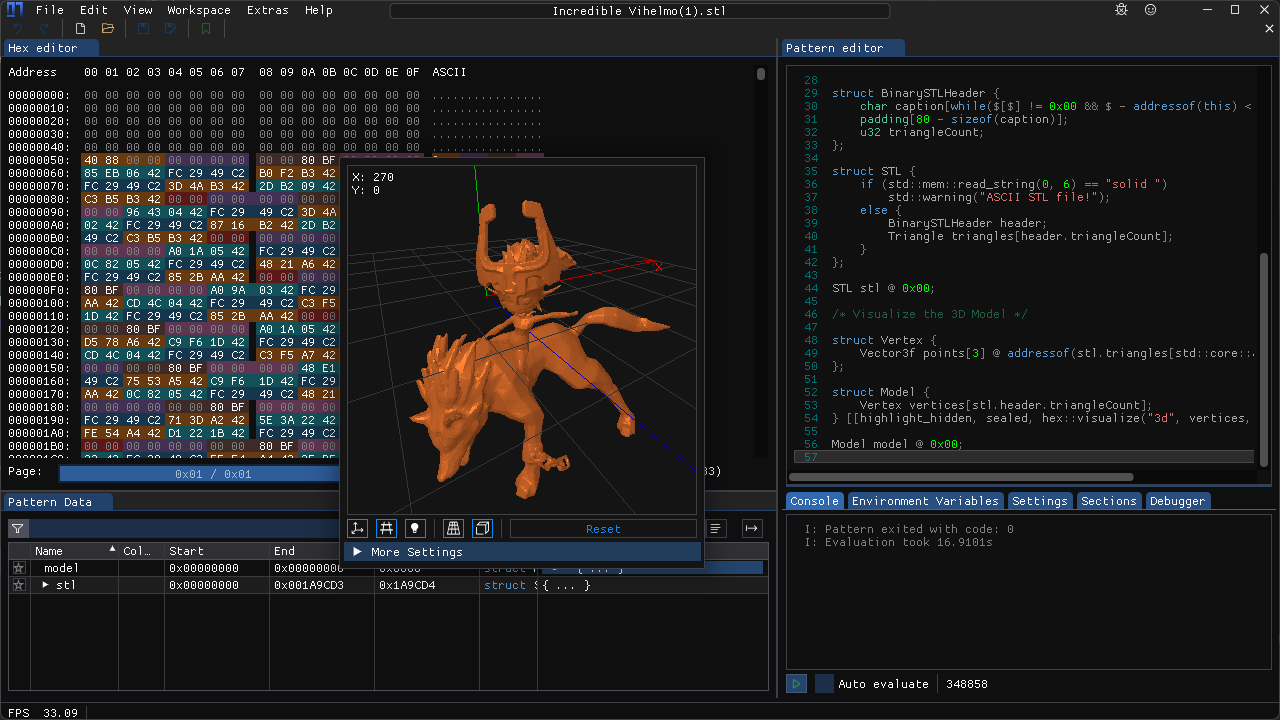
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.

Static analyzer for PE executables with plugin-based detection of packers, compilers, suspicious imports, cryptographic constants, and ClamAV…

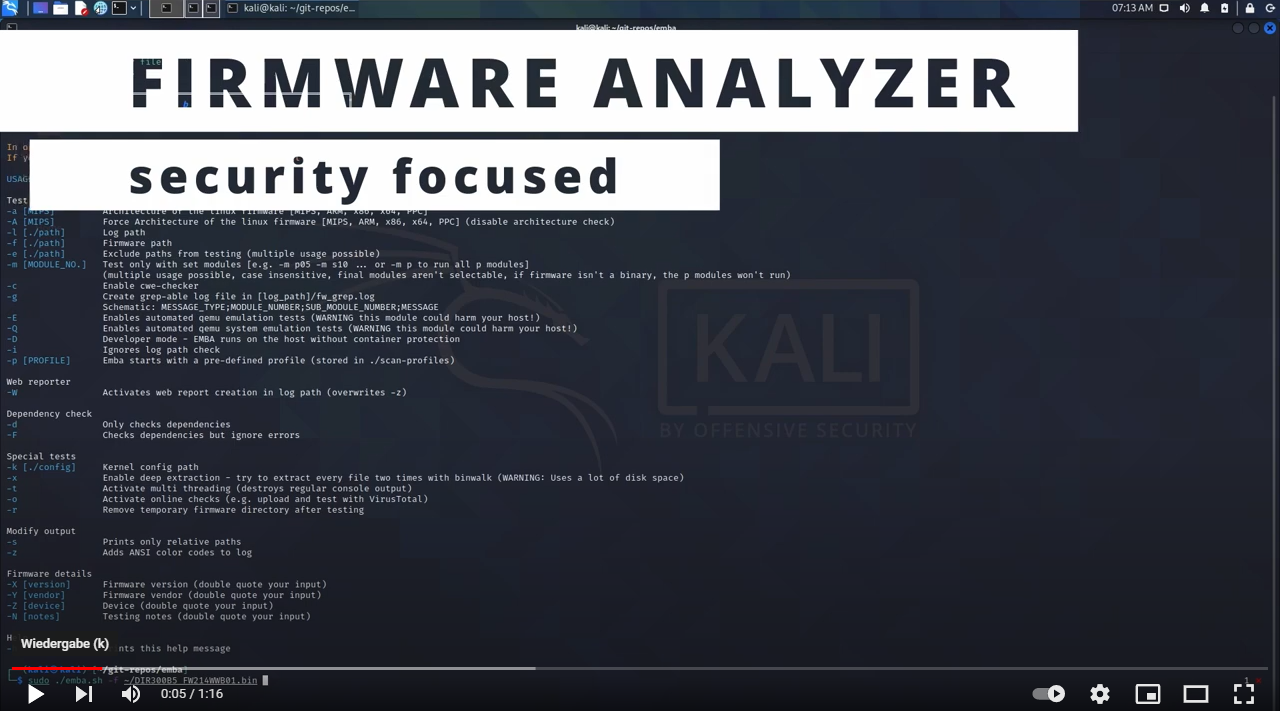
EMBA - The firmware security analyzer

A byte code analyzer for finding deserialization gadget chains in Java applications


A Python pickling decompiler and static analyzer

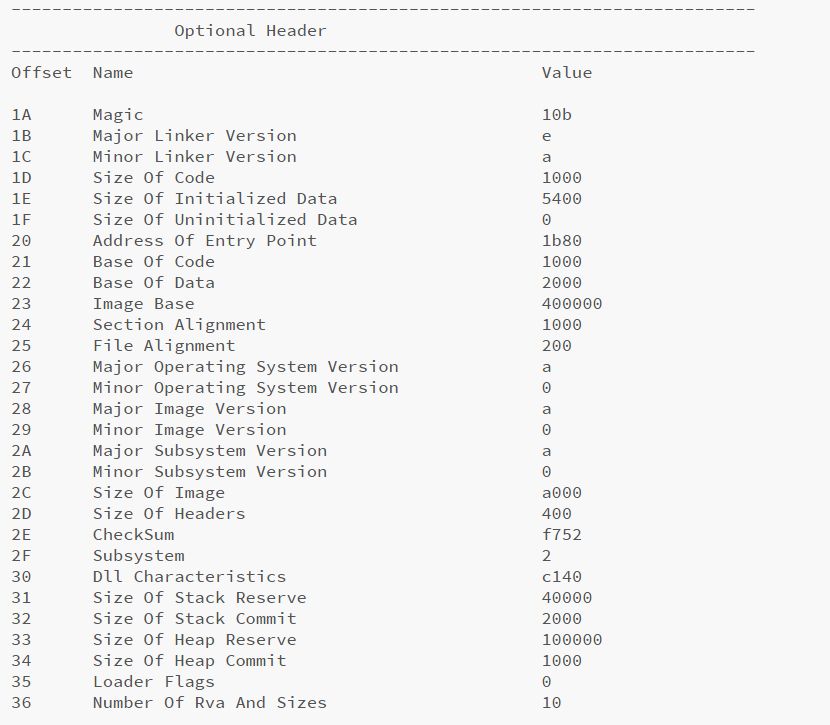
Advanced Portable Executable File Analyzer And Disassembler 32 & 64 Bit

Static analyzer for Flutter/Dart AOT snapshots — recovers function names, class hierarchies, call graphs, and behavioral signals from libapp.so…

A Zeek ELF File Analyzer

Static binary vulnerability scanner using abstract interpretation on Ghidra Pcode. Detects CWE classes like buffer overflows, use-after-free, and…

Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…

MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…

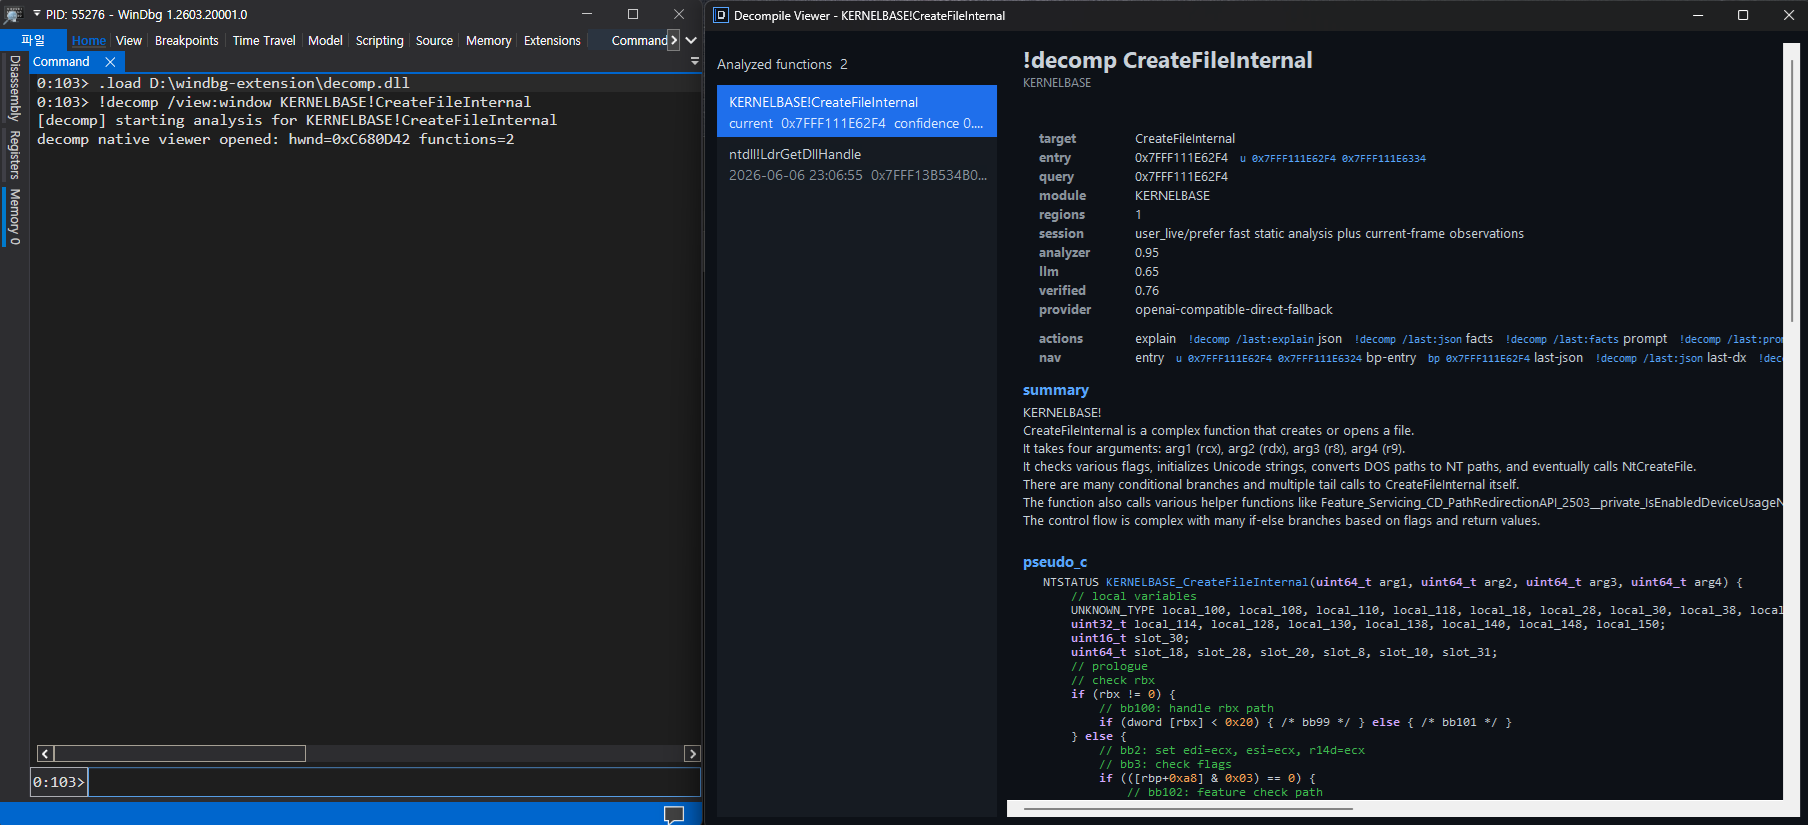
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.

Research project related to memory address analysis