
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
61 results
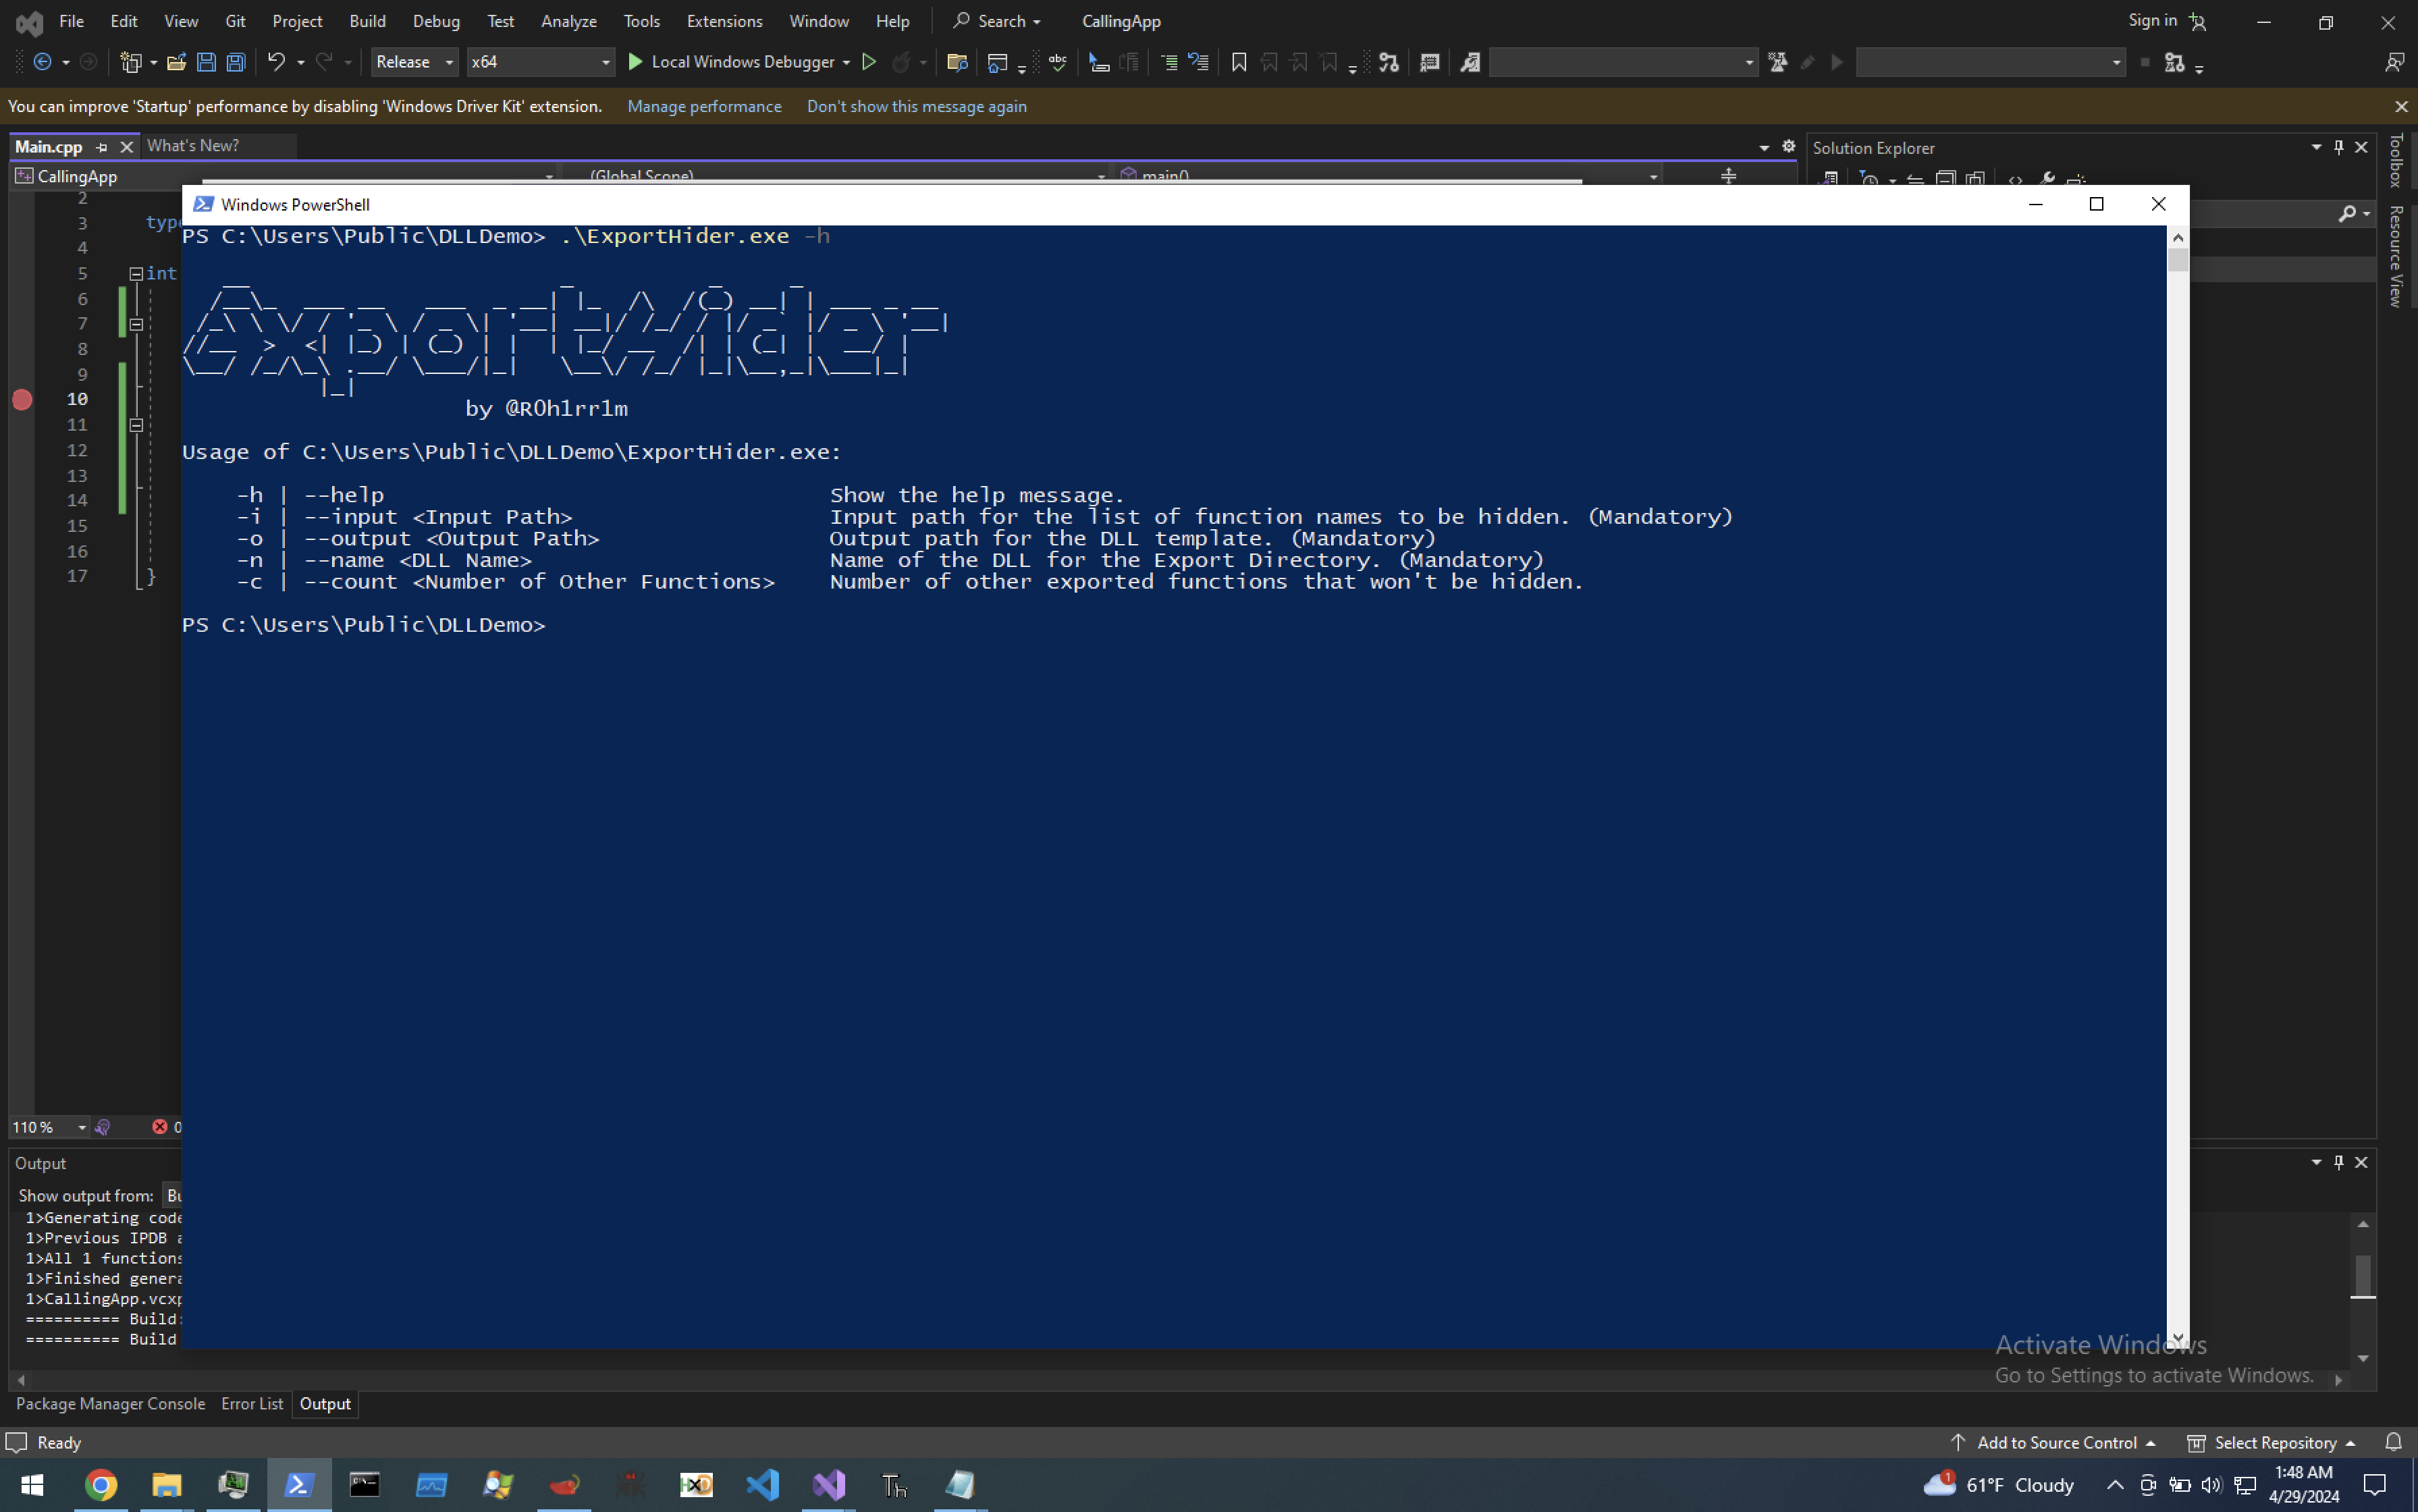
ExportHider preview

ExportHider

GitHubfrkngksl/exporthider

ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
binary-analysisdynamic-code-analysisexploitation+4
35
5 months ago
path-auditor preview
Archived

path-auditor

GitHubgoogle/path-auditor

Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…
binary-analysisdynamic-code-analysisexploitation+3
2505 years ago
dynamorio preview

dynamorio

GitHubdynamorio/dynamorio

Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
binary-analysiscode-analysisdebuggers+3
3.2k1 day ago
speakeasy preview

speakeasy

GitHubmandiant/speakeasy

Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…
binary-analysisdynamic-analysis-sandboxingmalware-analysis+1
2.1k8 days ago
nCPU preview

nCPU

GitHubrobertcprice/ncpu

Research runtime for differentiable neural computers, GPU-based CPU emulation, and program synthesis. Features neural ALU, constant-time crypto, JEPA…
ai-securitybinary-analysiscryptography+8
6582 months ago
WFH preview

WFH

GitHubconscioushacker/wfh

Frida-based dynamic analysis tool that automatically identifies DLL sideloading and COM hijacking vulnerabilities in Windows executables through…
binary-analysisdynamic-analysis-sandboxingexploitation+1
4364 years ago
rikune preview

rikune

GitHublast-emo-boy/rikune

MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
binary-analysisdynamic-analysis-sandboxingeducation+8
24218 days ago
krie preview

krie

GitHubgui774ume/krie

Linux Kernel Runtime Integrity with eBPF

binary-analysisdefensive-toolsintrusion-detection
1872 years ago
aDLL preview

aDLL

GitHubideaslocas/adll

Automated DLL hijacking vulnerability discovery tool that analyzes PE binaries at load-time and runtime via API hooking, enumerating missing DLLs and…
binary-analysisdynamic-analysis-sandboxingexploitation+1
735 years ago
DLLHSC preview

DLLHSC

GitHubctxis/dllhsc

Automated scanner for discovering DLL search order hijacking candidates in Windows executables, featuring import table parsing, runtime module…
binary-analysisexploitationpayload-development+1
1586 years ago
ghidra2frida preview

ghidra2frida

GitHubfedericodotta/ghidra2frida

Ghidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…
android-securitybinary-analysisdynamic-analysis-sandboxing+3
1355 years ago
ios-malicious-bithunter preview

ios-malicious-bithunter

GitHubalipay/ios-malicious-bithunter

iOS Malicious Bit Hunter is a malicious plug-in detection engine for iOS applications. It can analyze the head of the macho file of the injected…
binary-analysisdynamic-analysis-sandboxingios-security+3
885 years ago
OWN-Defender preview

OWN-Defender

GitHubnirvanaon/own-defender

Research project reverse-engineering Windows Security Center COM interfaces to trace AV registration through ATL, vtable, WSCAPI, and RPC, with…

binary-analysisdefensive-toolseducation+2
3628 days ago
dezlock-dump preview

dezlock-dump

GitHubdougwithseismic/dezlock-dump

Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
binary-analysisdebuggersdynamic-code-analysis+6
916 months ago
splinter preview

splinter

GitHubawrped/splinter

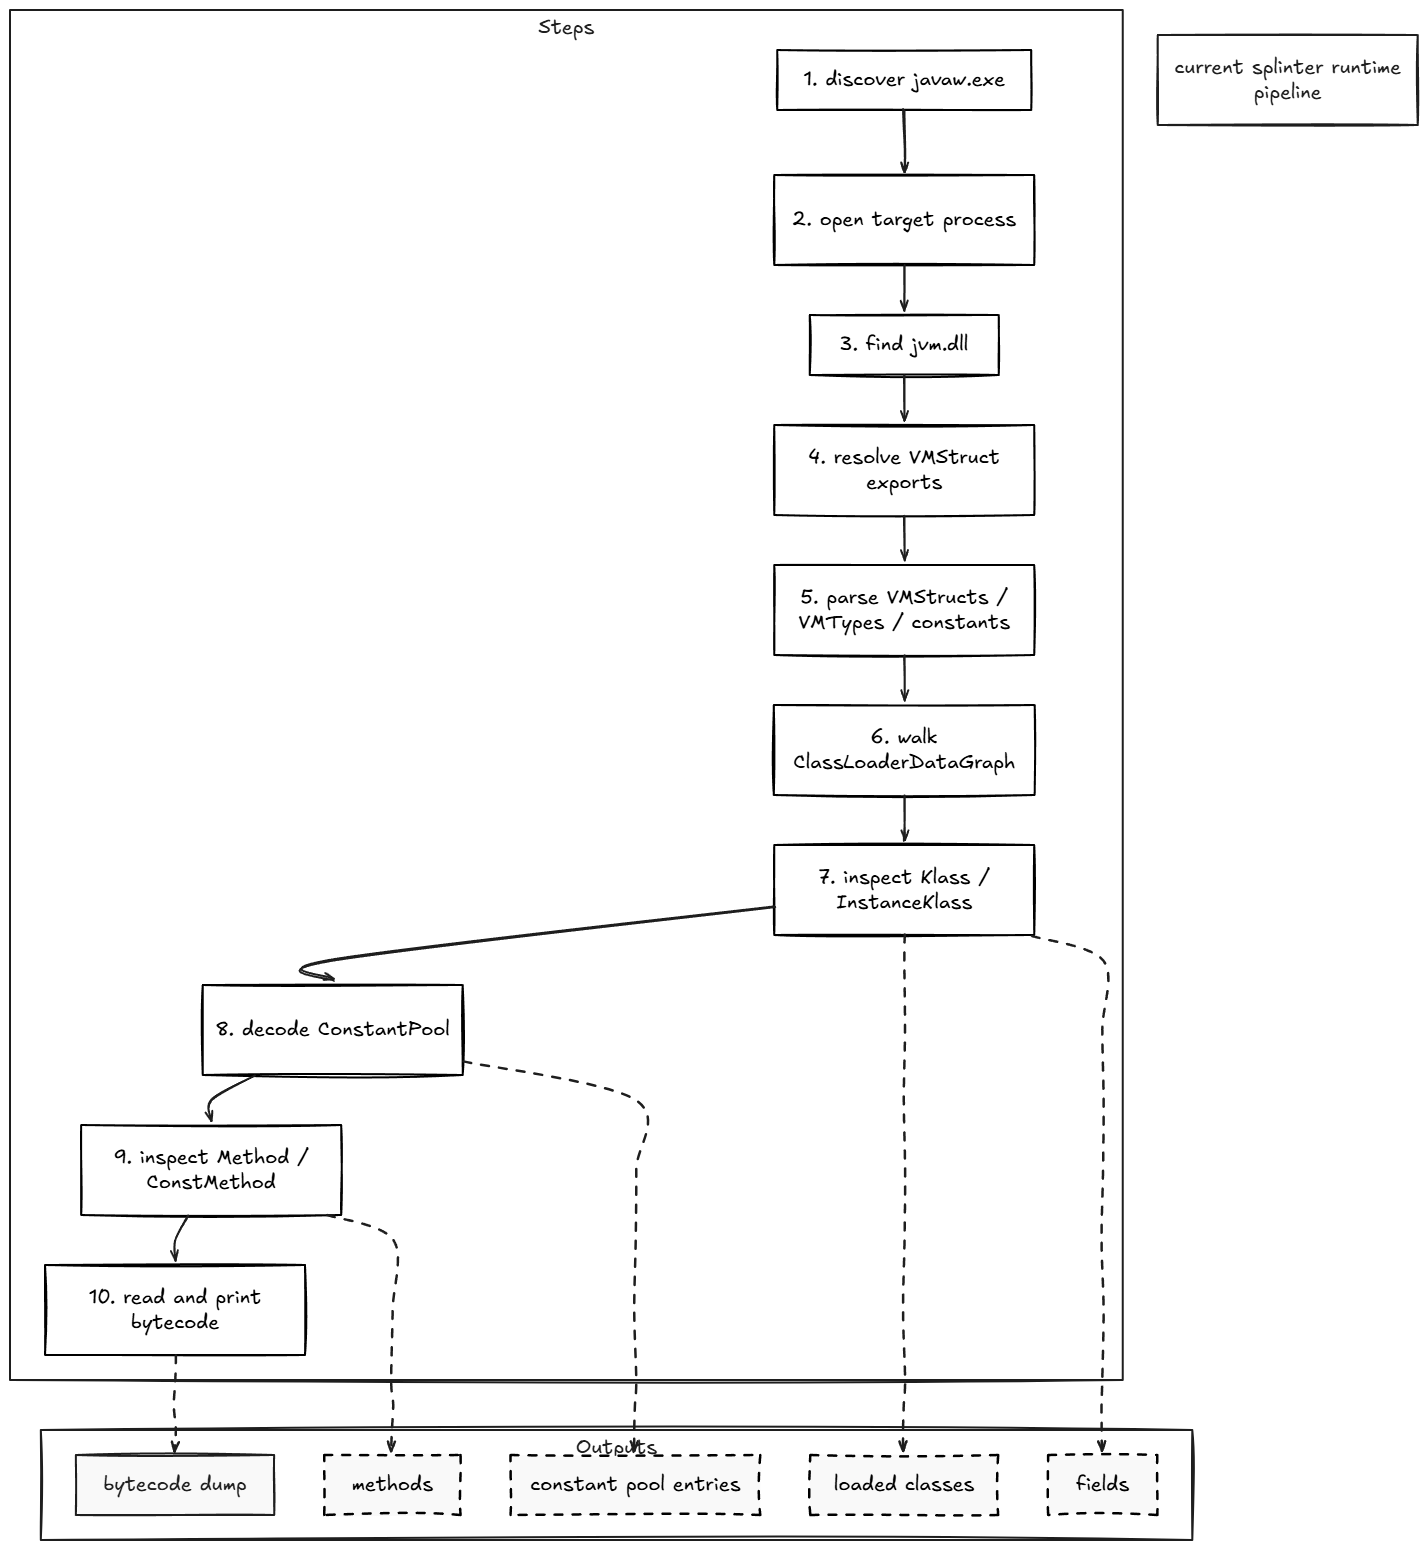
Runtime JVM analysis toolkit for inspecting classes, methods, fields, constant pool, and bytecode

binary-analysisdebuggersdynamic-analysis-sandboxing+4
901 month ago
ODIS-project-explorer preview

ODIS-project-explorer

GitHubkartoffelpflanze/odis-project-explorer

Python dumper/explorer for MCD Runtime Projects used by ODIS
binary-analysisdebuggersembedded-systems-security+4
391 year ago
Soviet preview

Soviet

GitHubmephistolist/soviet

A Runtime Crypter in C for Linux ELF binaries.
anti-botbinary-analysisencryption-decryption-tools+6
357 months ago
DotNetHookerToolkit preview

DotNetHookerToolkit

GitHubsensepost/dotnethookertoolkit

Frida-based .NET Framework injector and managed method hooking toolkit for runtime tracing, native entrypoint resolution, and dynamic analysis of…

binary-analysiscode-analysisdebuggers+4
116 months ago
Previous1234Next