
columbo
 visma-prodsec/columbo
ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…
anomaly-detectionbinary-analysisdigital-forensics+3
61
visma-prodsec/columboML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…
 mandiant/route-sixty-sink
Link sources to sinks in C# applications.
 helixo32/crimsonedr
Simulate the behavior of AV/EDR for malware development training.
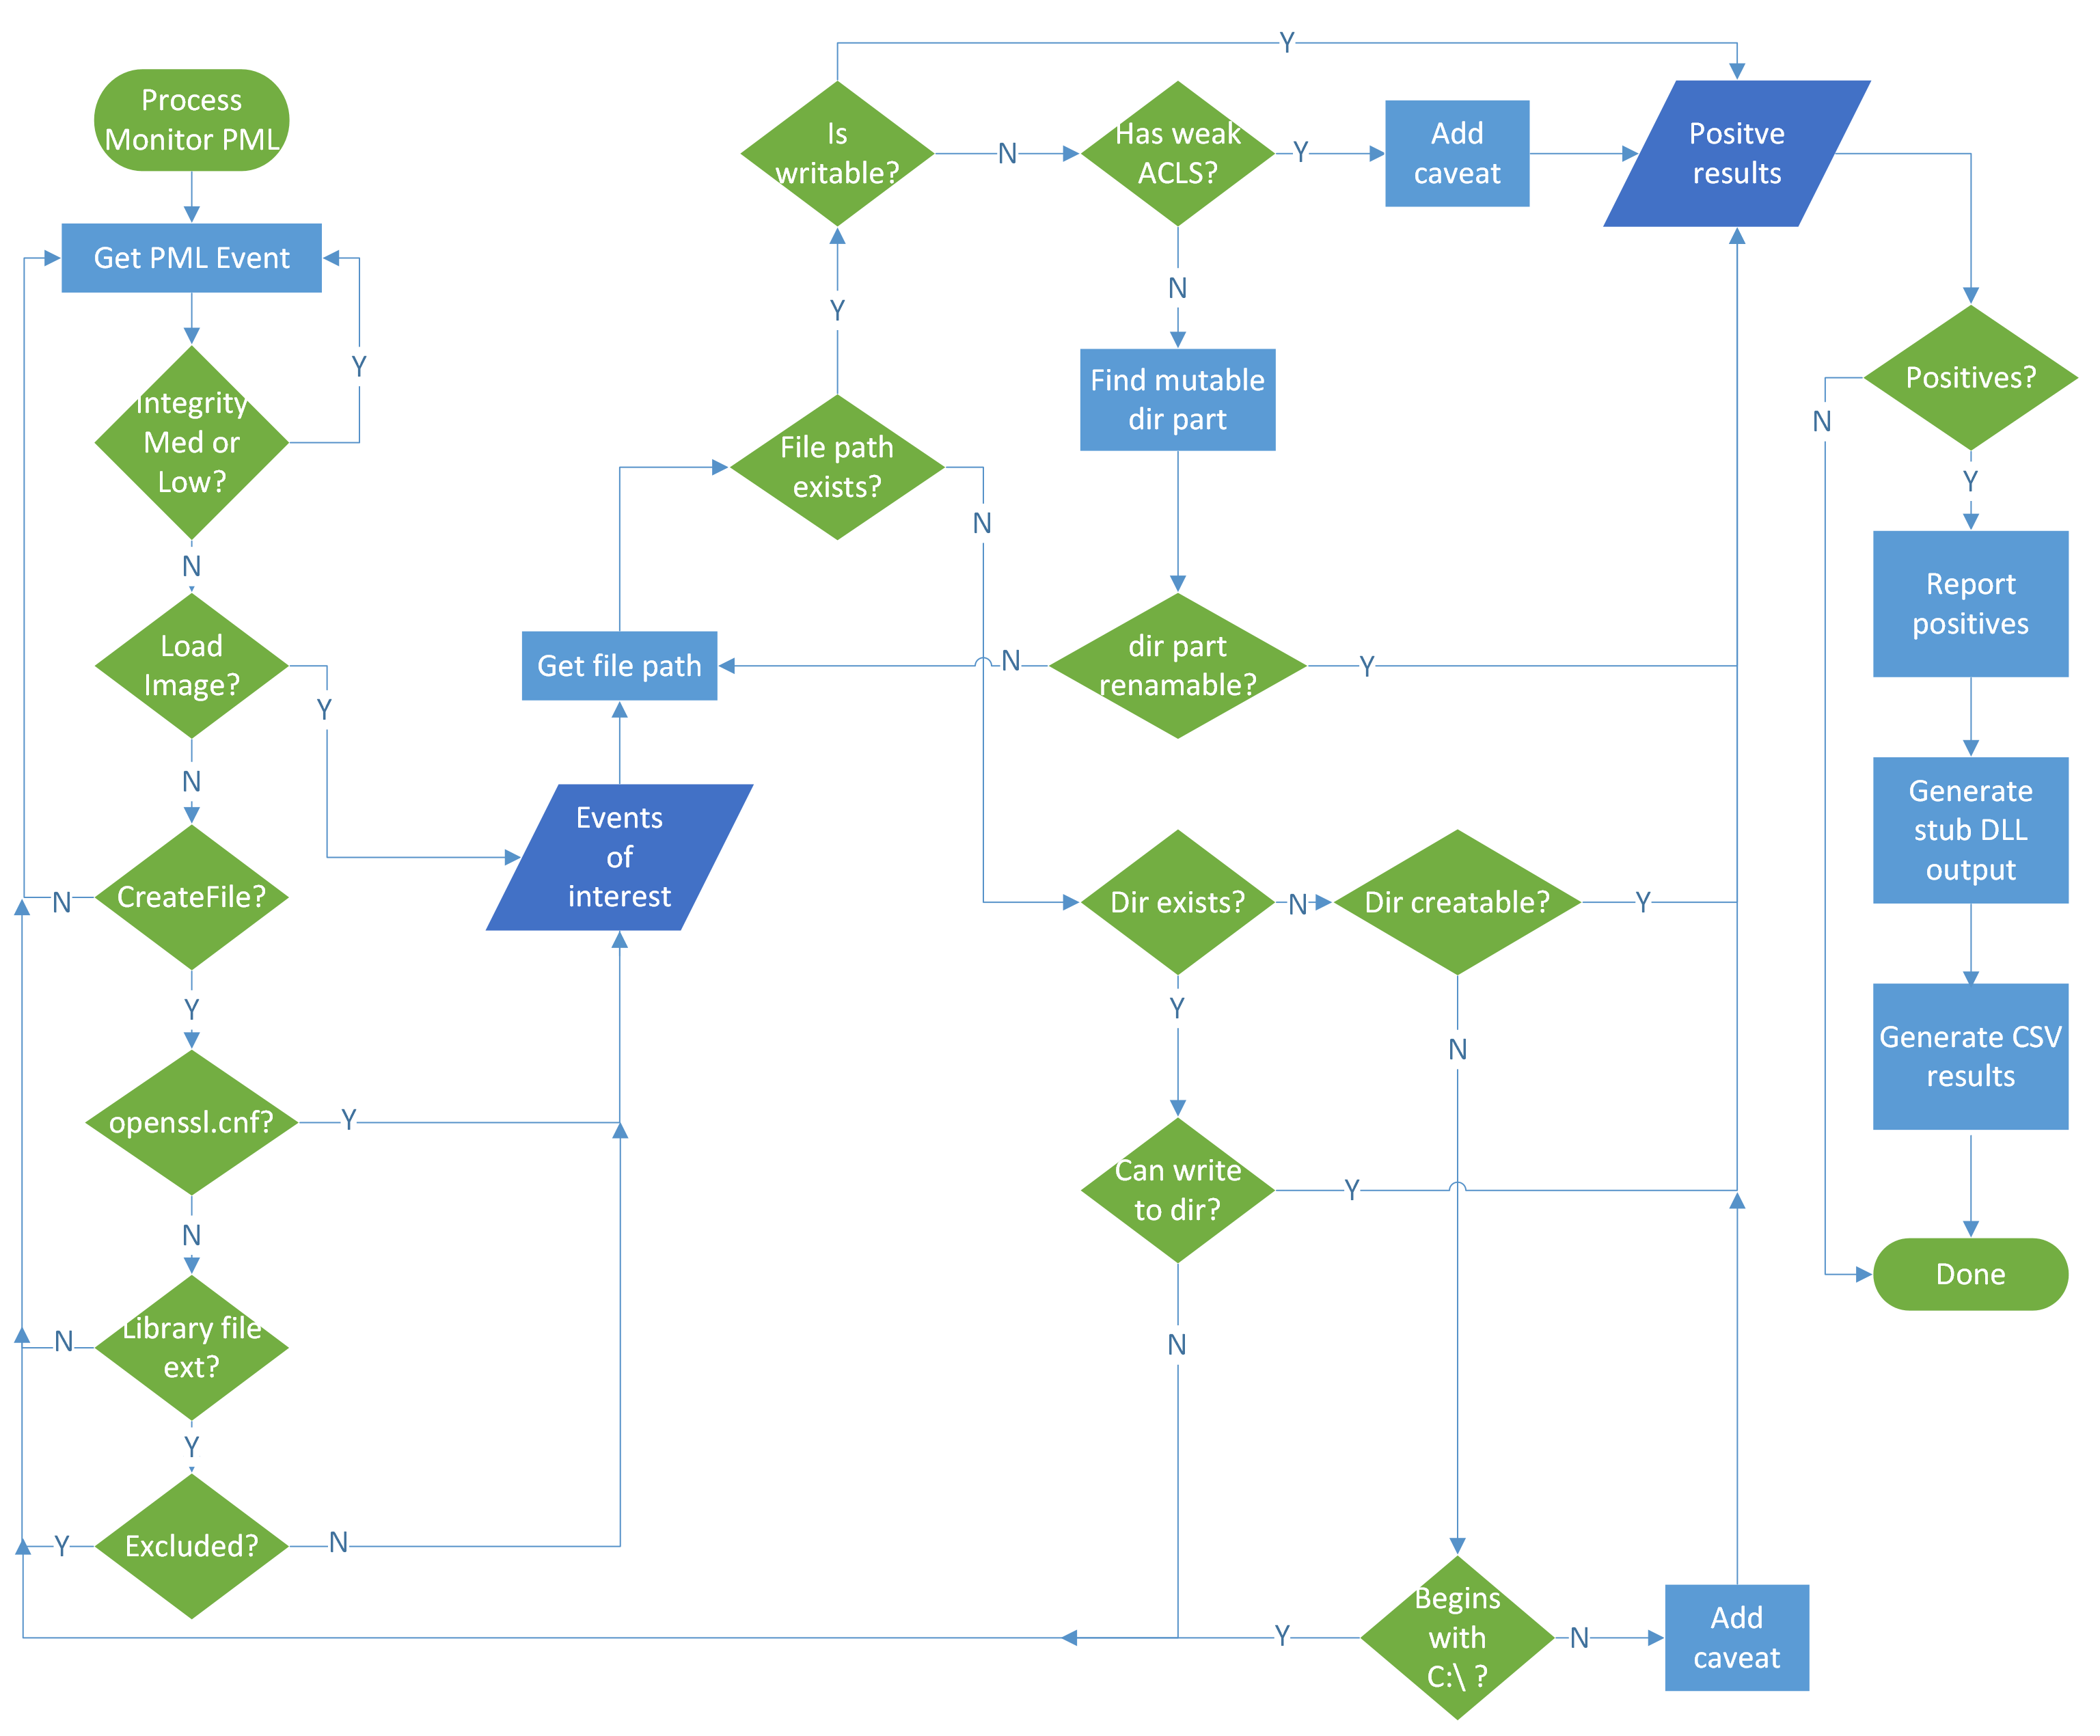 vu-ls/crassus
Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…
 amossys/memitm
Tool to make in memory man in the middle
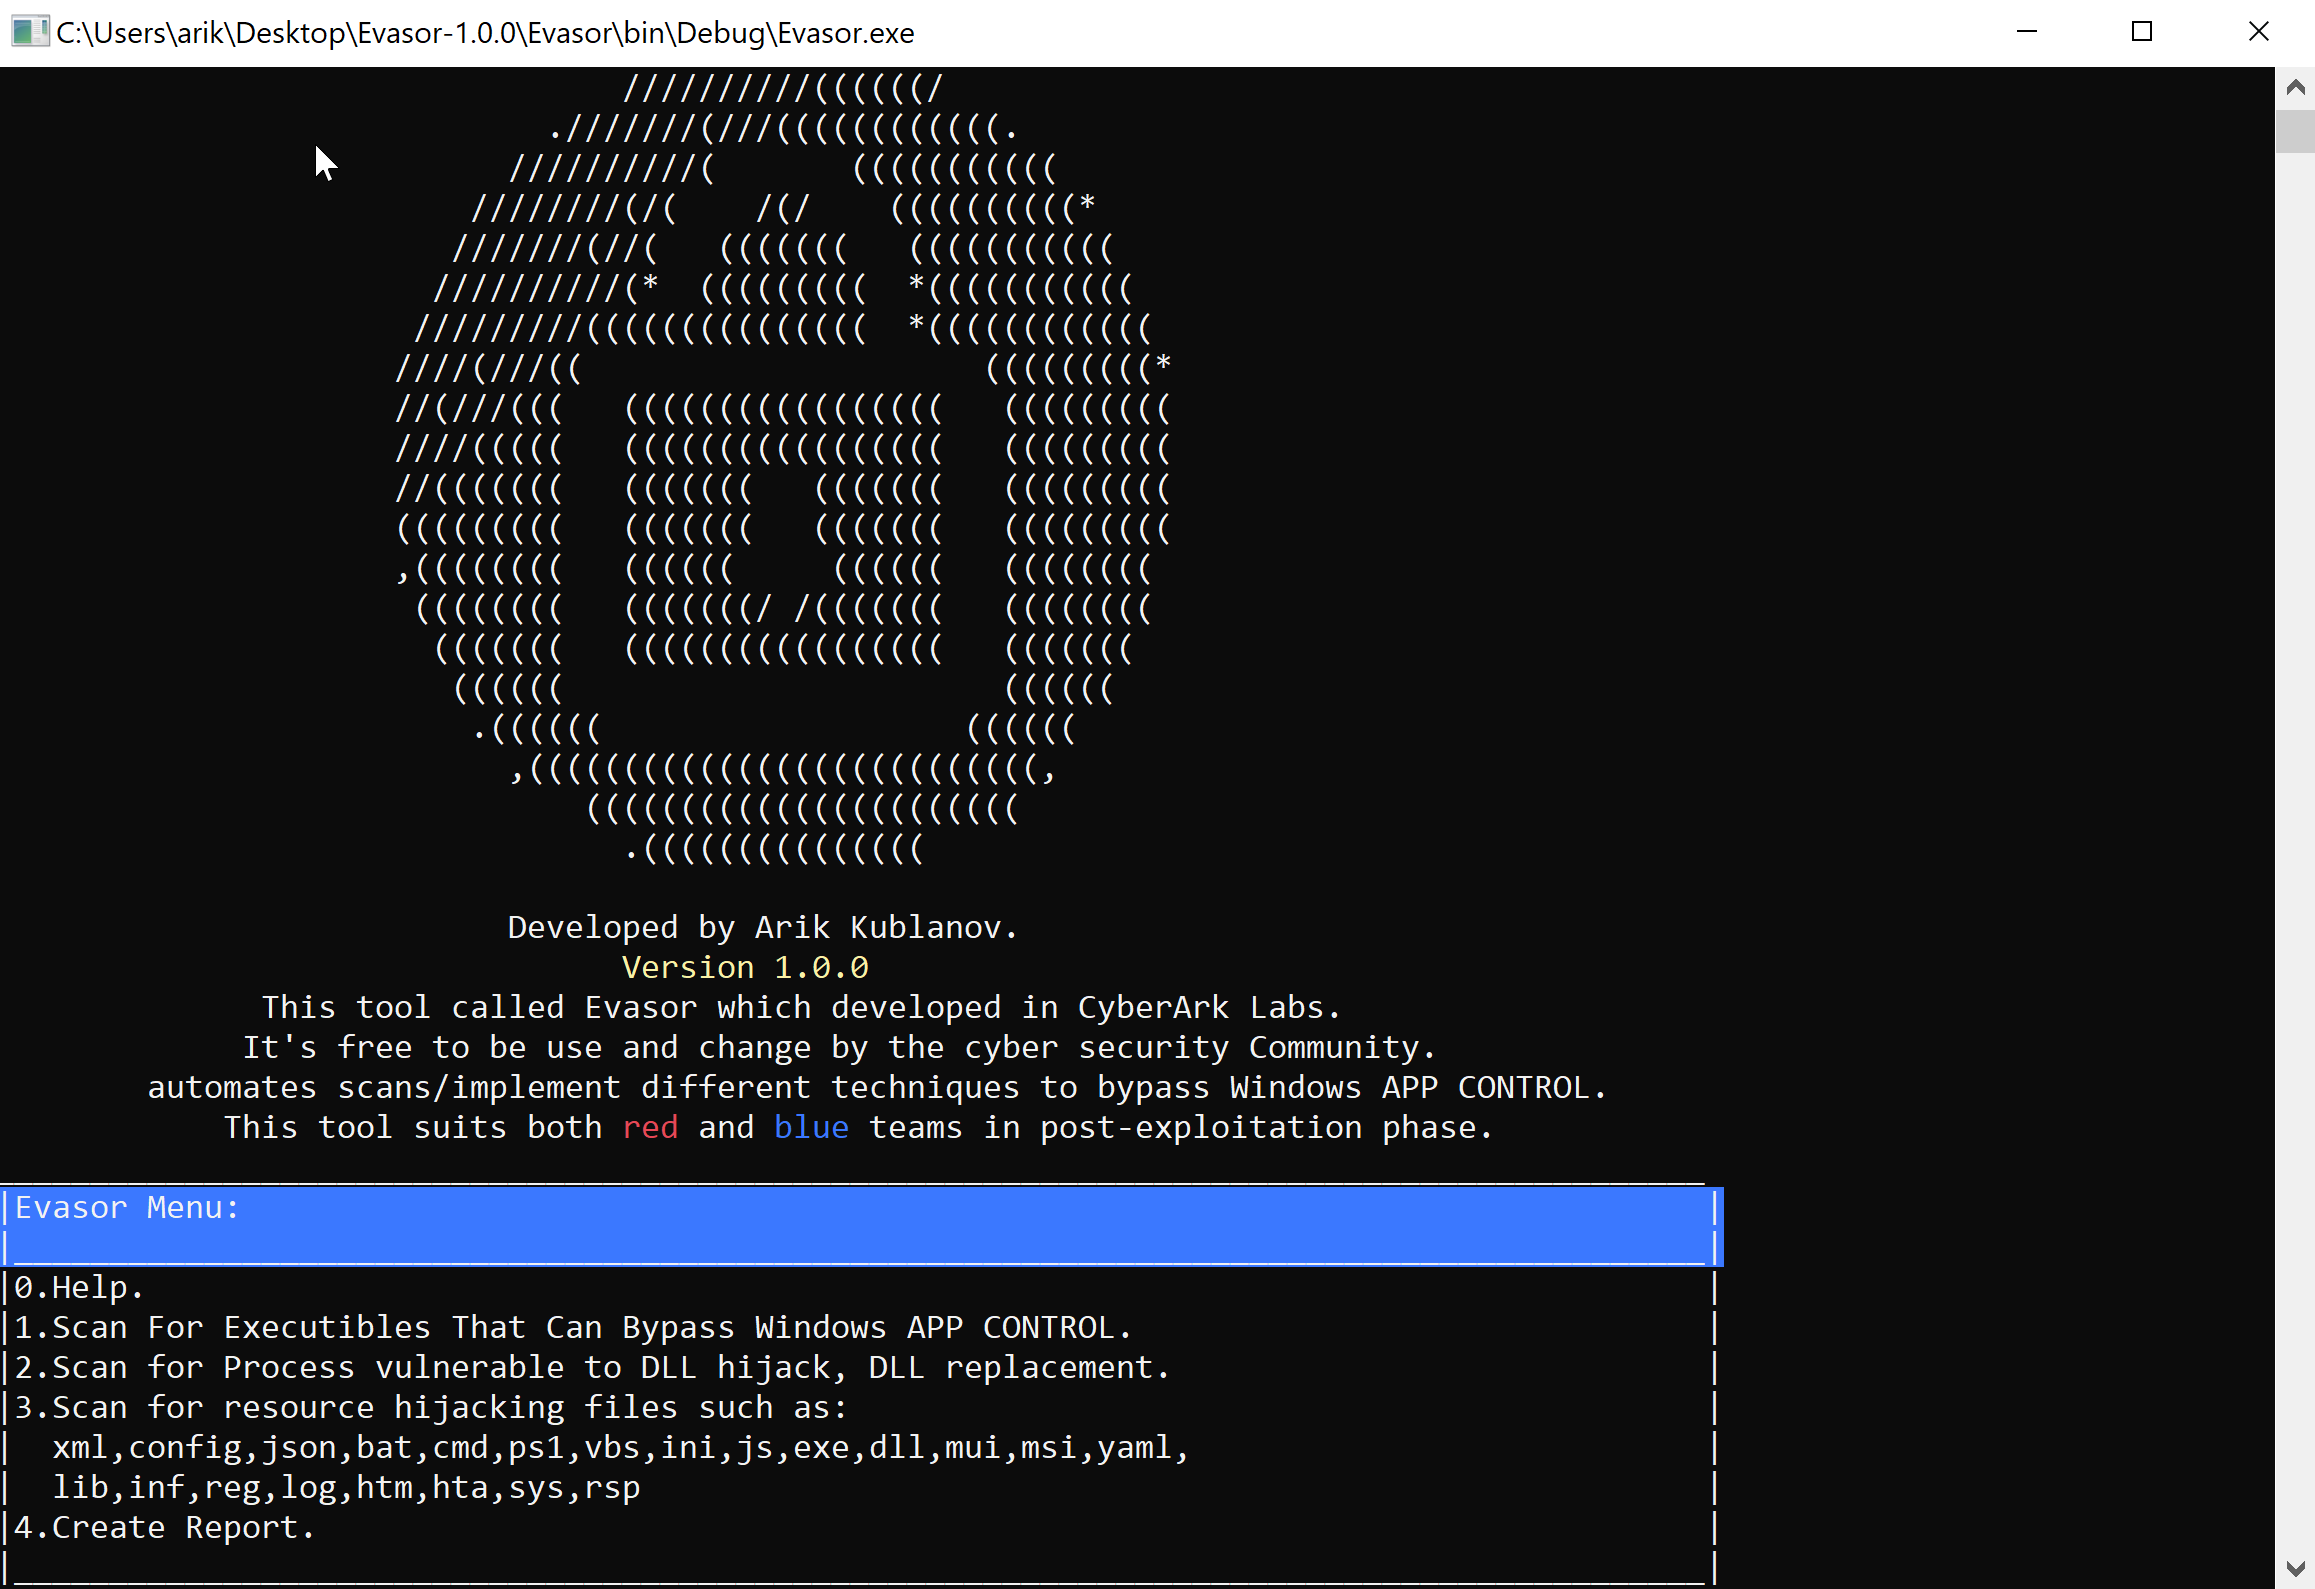 cyberark/evasor
A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies
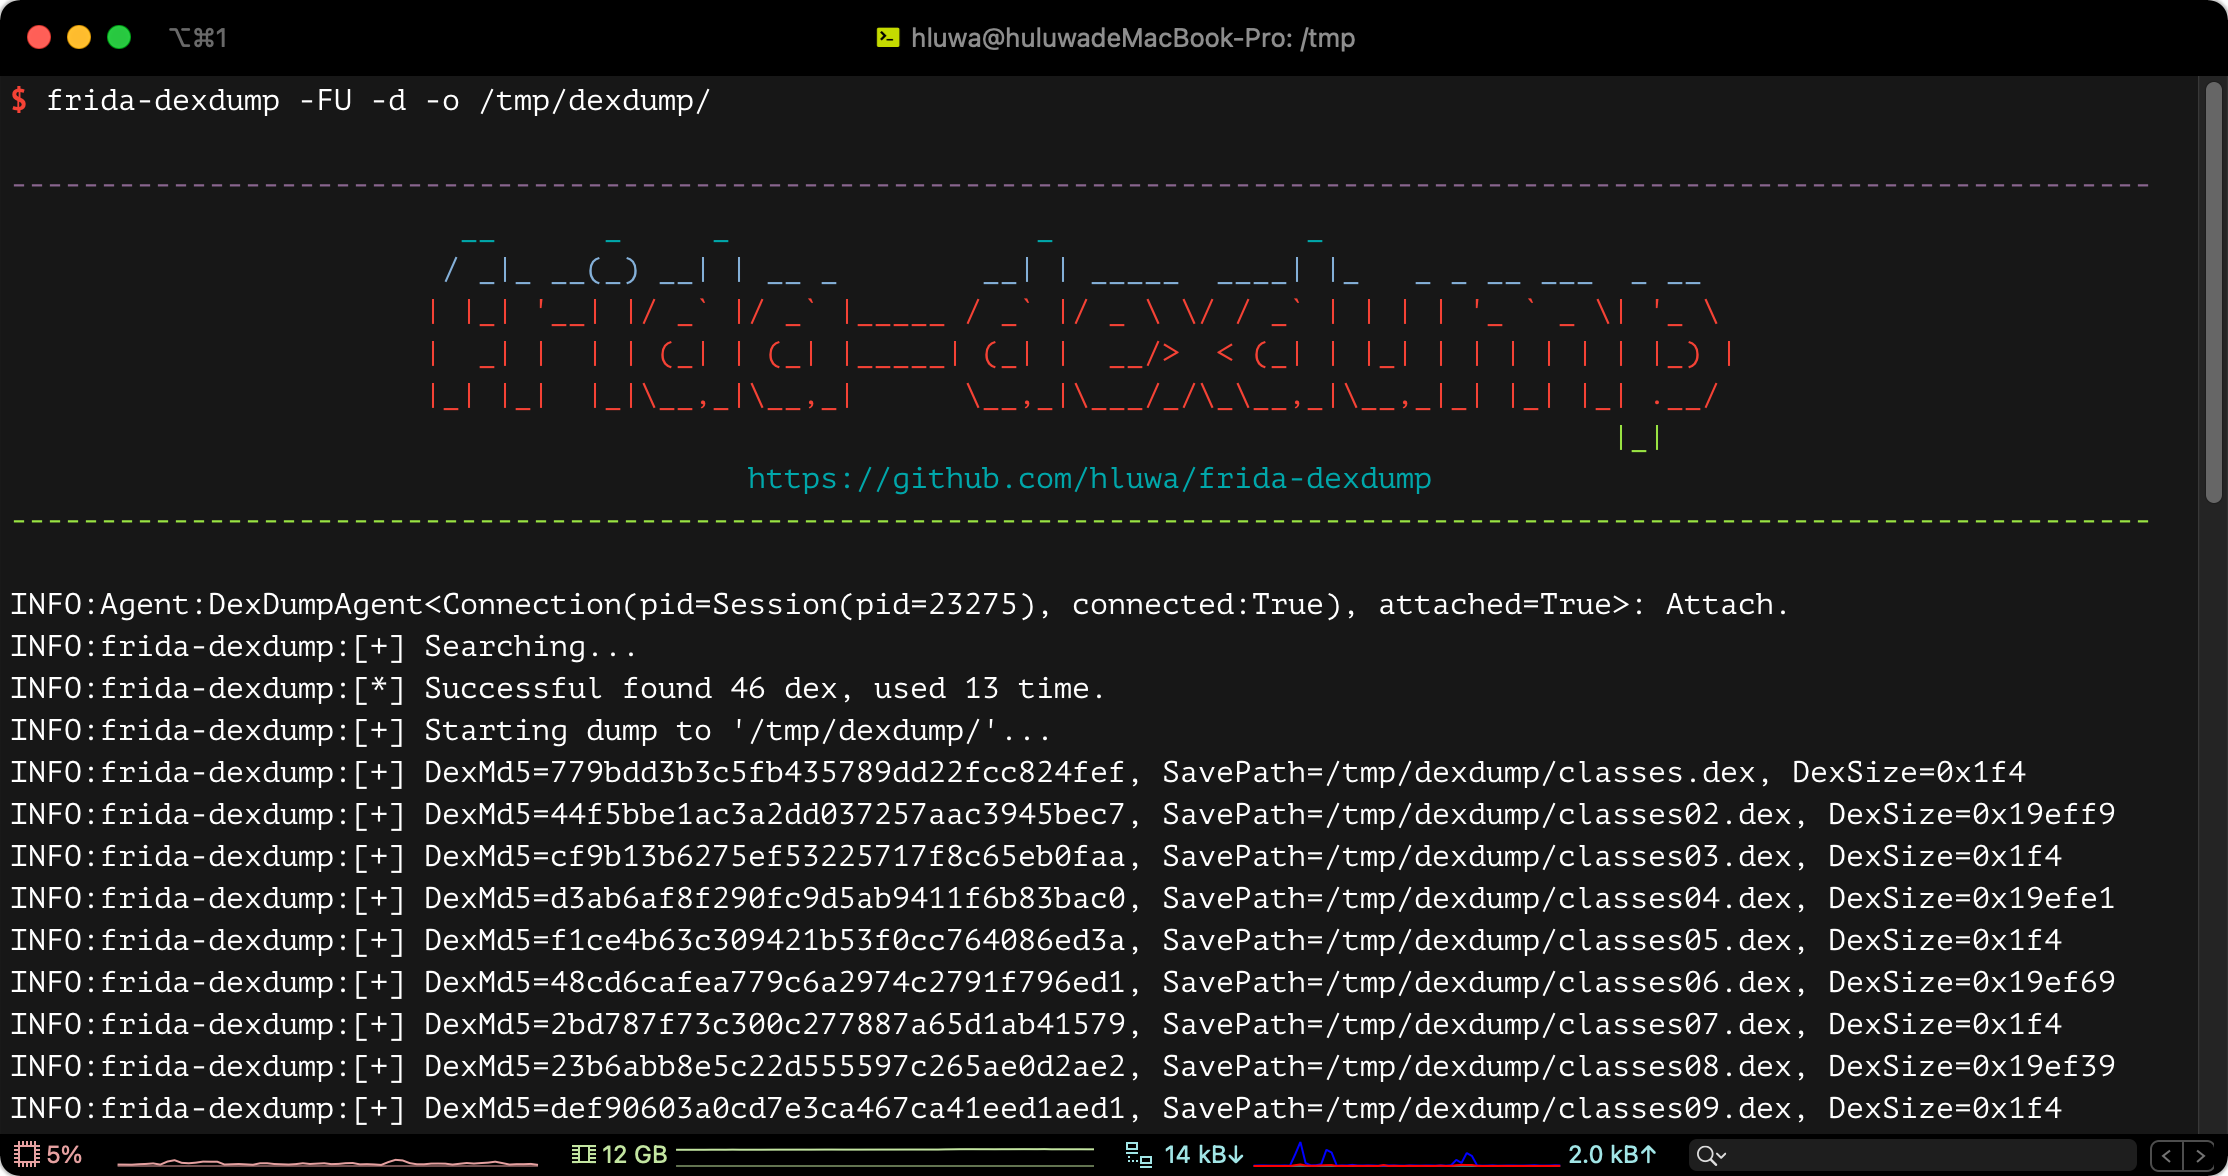 hluwa/frida-dexdump
A frida tool to dump dex in memory to support security engineers analyzing malware.
 gmh5225/hooktools
Basic injectable for analyzing the behavior of evasive malware
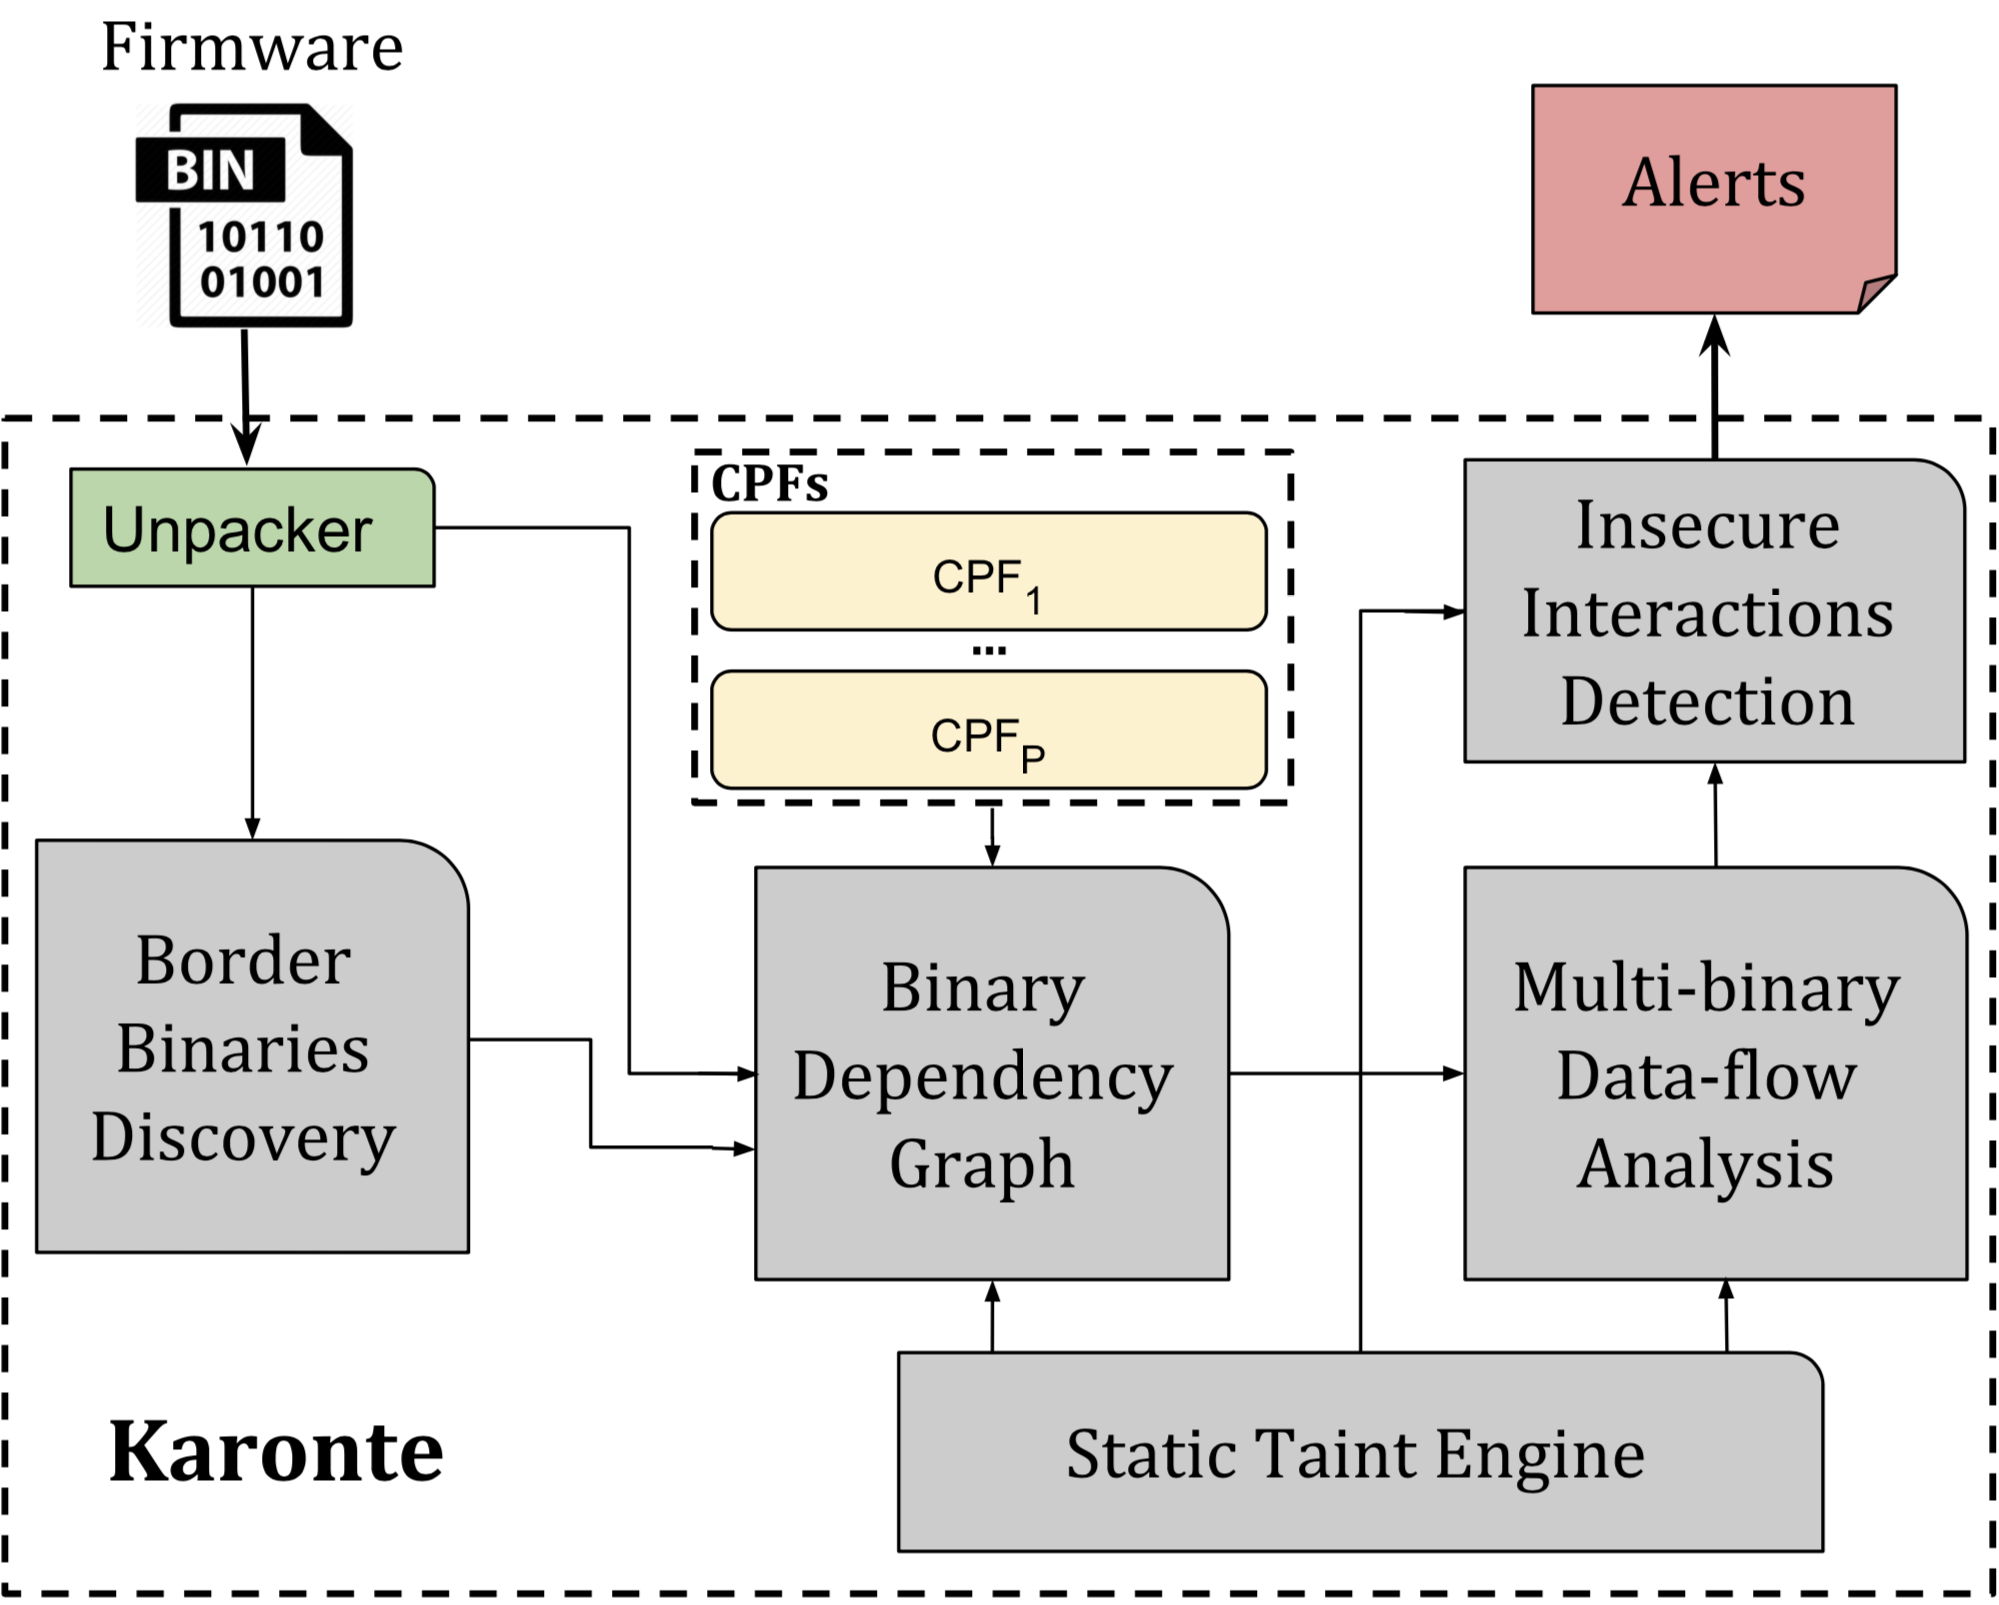 ucsb-seclab/karonte
Karonte is a static analysis tool to detect multi-binary vulnerabilities in embedded firmware
 rscloura/doldrums
A Flutter/Dart reverse engineering tool
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
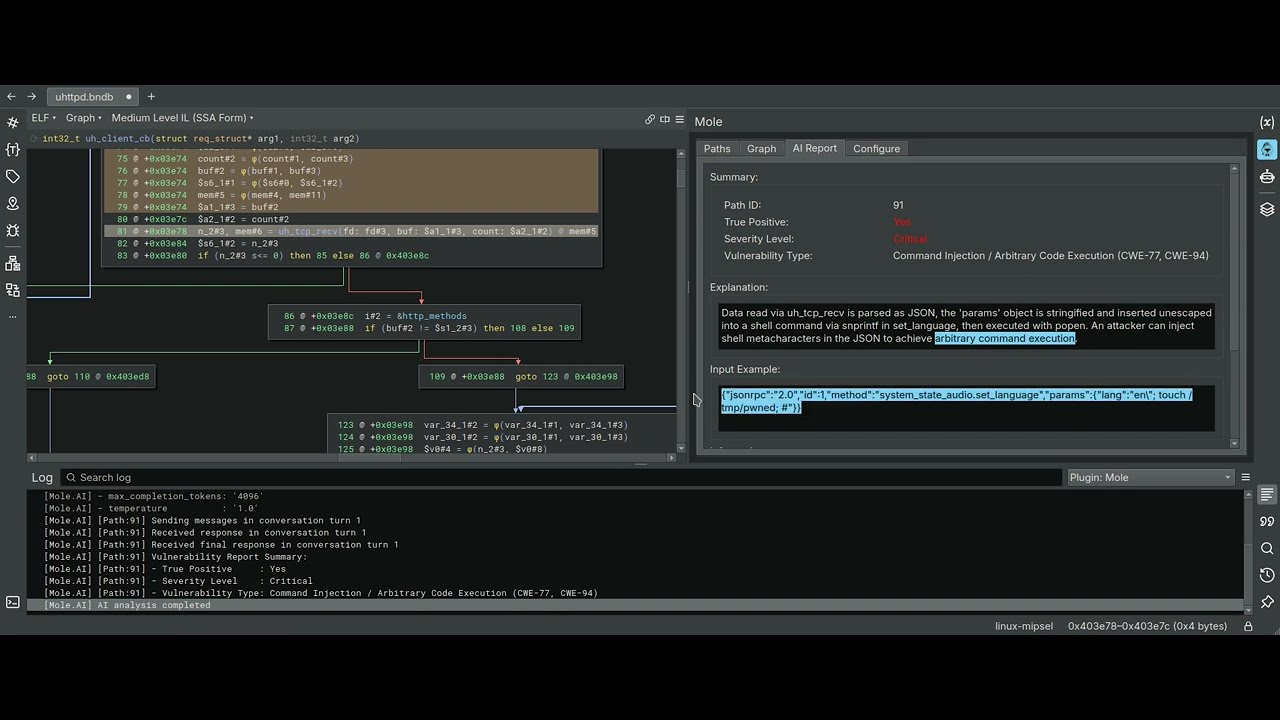 cyber-defence-campus/mole
A Binary Ninja plugin using backward slicing of variables as a driver for static taint analysis
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
 zeze-zeze/ioctlance
A tool that is used to hunt vulnerabilities in x64 WDM drivers
 lucamassarelli/yarasafe
SAFE embeddings to match functions in yara
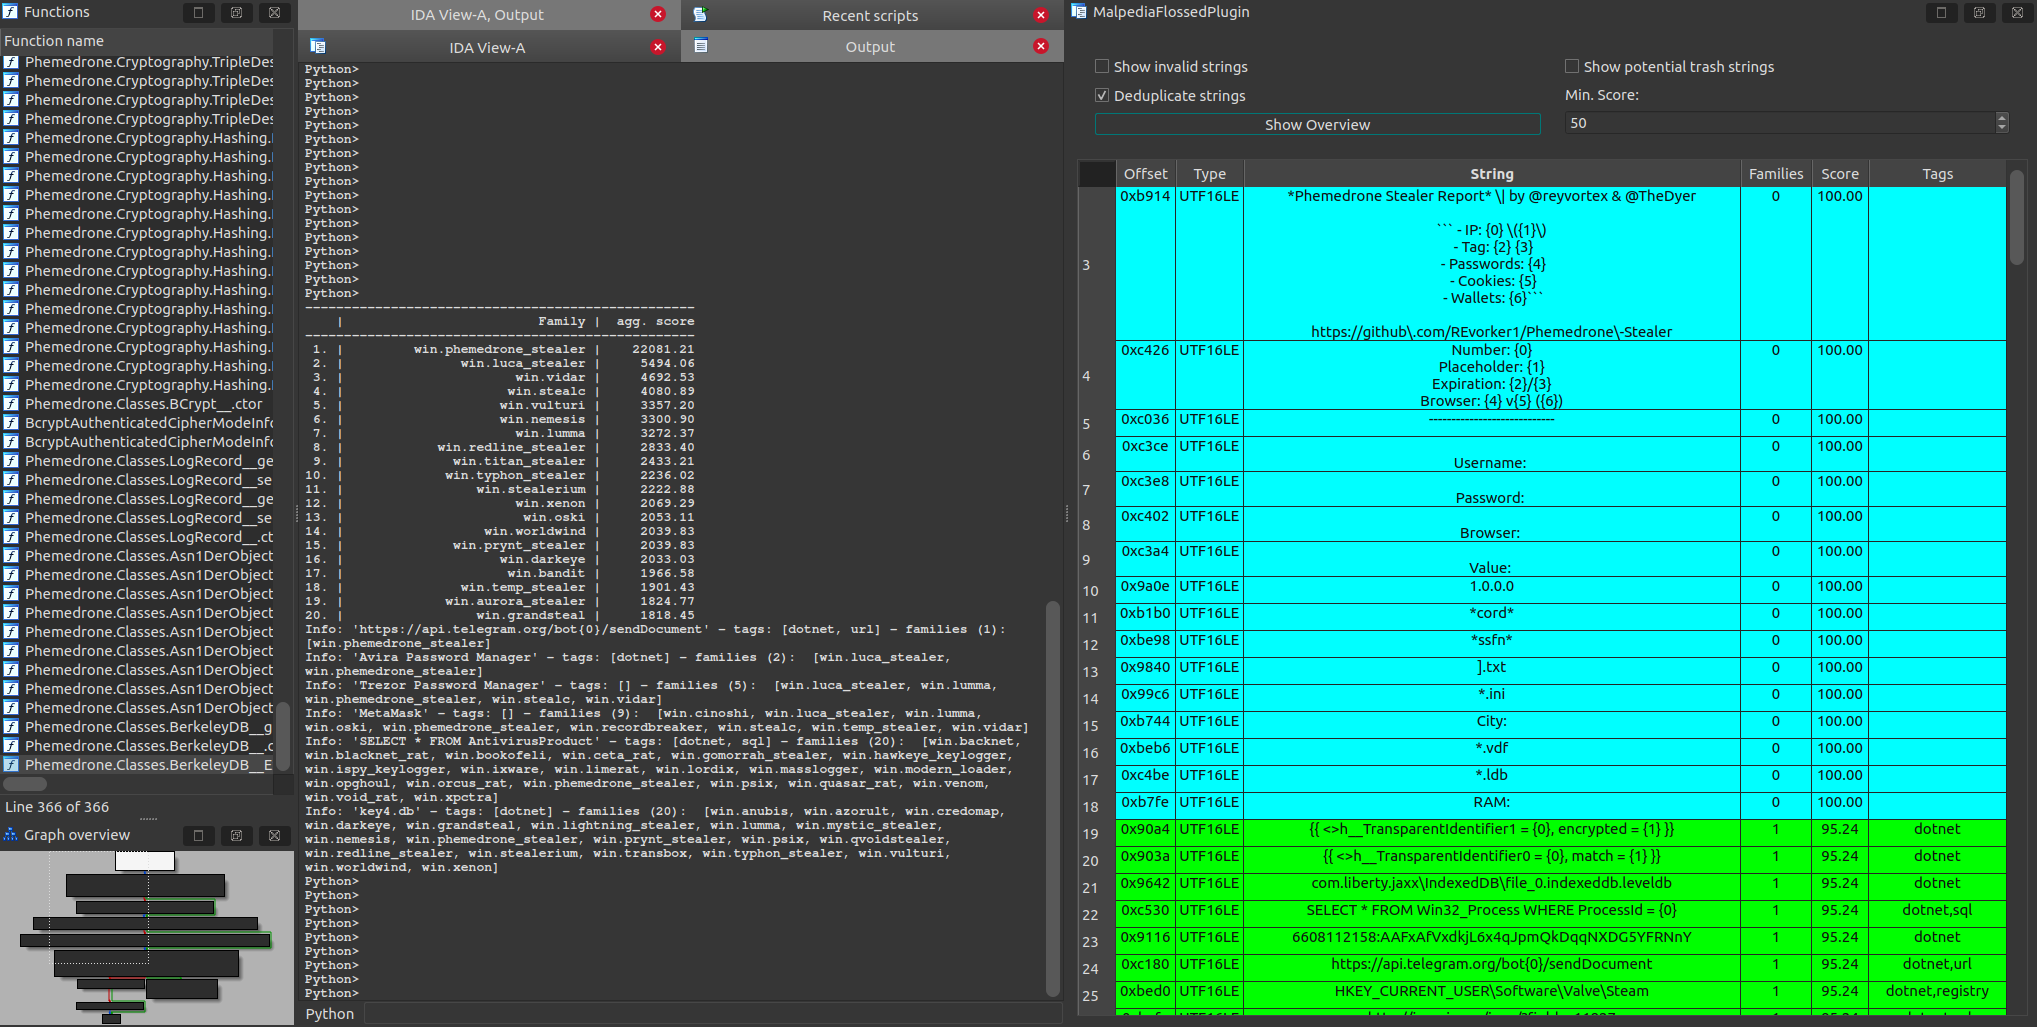 malpedia/malpedia-flossed
FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.