
netzob
 netzob/netzob
Open-source toolkit for reverse engineering, modeling, and fuzzing communication protocols. Infers message formats and state machines from network…
binary-analysisfuzzingnetwork-security+1
838
netzob/netzobOpen-source toolkit for reverse engineering, modeling, and fuzzing communication protocols. Infers message formats and state machines from network…
 mandiant/speakeasy
Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 kyxiaxiang/360wfp_exploit
BYOVD: Use 360 WFP driver to block EDR/XDR network connection.
 sec-tools/litefuzz
A multi-platform fuzzer for poking at userland binaries, network clients and servers
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
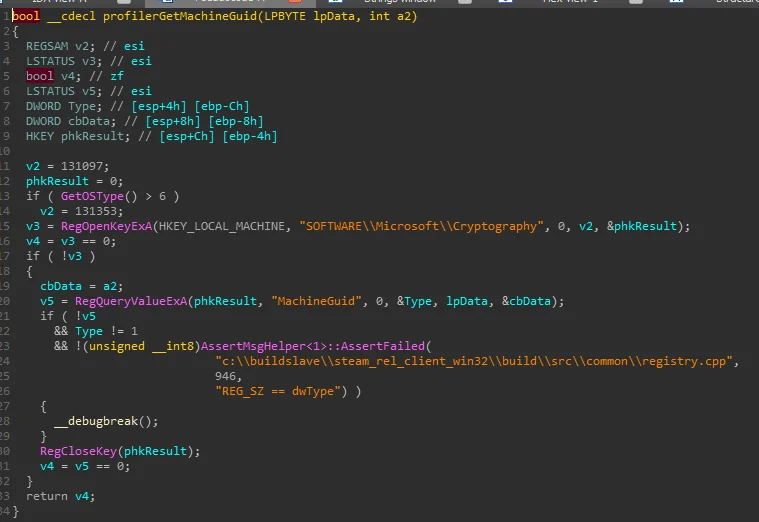 gmh5225/hwid-steamspywareterminator
Work-in-progress library injected into Steam to block the hidden CFillMachineInfoThread that collects HWID, disk, network adapter, and registry…
 trinadh465/linux-4.1.15_cve-2022-3564
Linux kernel 4.1.15 source code snapshot for analyzing and studying CVE-2022-3564, a vulnerability in the kernel's network subsystem.
 trinadh465/platform_system_netd_aosp10_r33_cve-2023-40084
Android netd vulnerability analysis and exploitation research for CVE-2023-40084, focusing on the platform's network daemon.
 robertcprice/ncpu
Research runtime for differentiable neural computers, GPU-based CPU emulation, and program synthesis. Features neural ALU, constant-time crypto, JEPA…
 baptisterajaut/radmin-vpn-linux
Run Radmin VPN on Linux via Wine — custom driver, TAP bridge, zero packet loss
 metrodango/pip3line
Swiss Army knife for raw bytes manipulation & interception
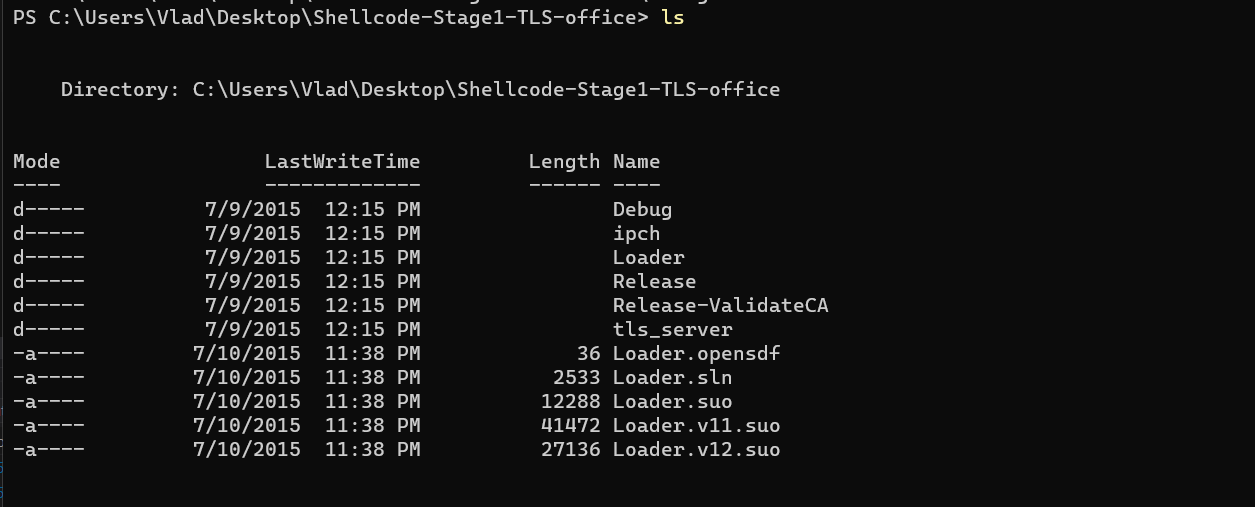 spiralbl0ck/analysis-for-stage1-shellcode-loader-from-hacking-
Analysis for stage1 shellcode loader from hacking
 adikso/cve-2024-5633
PoC for CVE-2024-5633
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.