

rikune
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
binary-analysisdynamic-analysis-sandboxingeducation+8
240
last-emo-boy/rikuneMCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
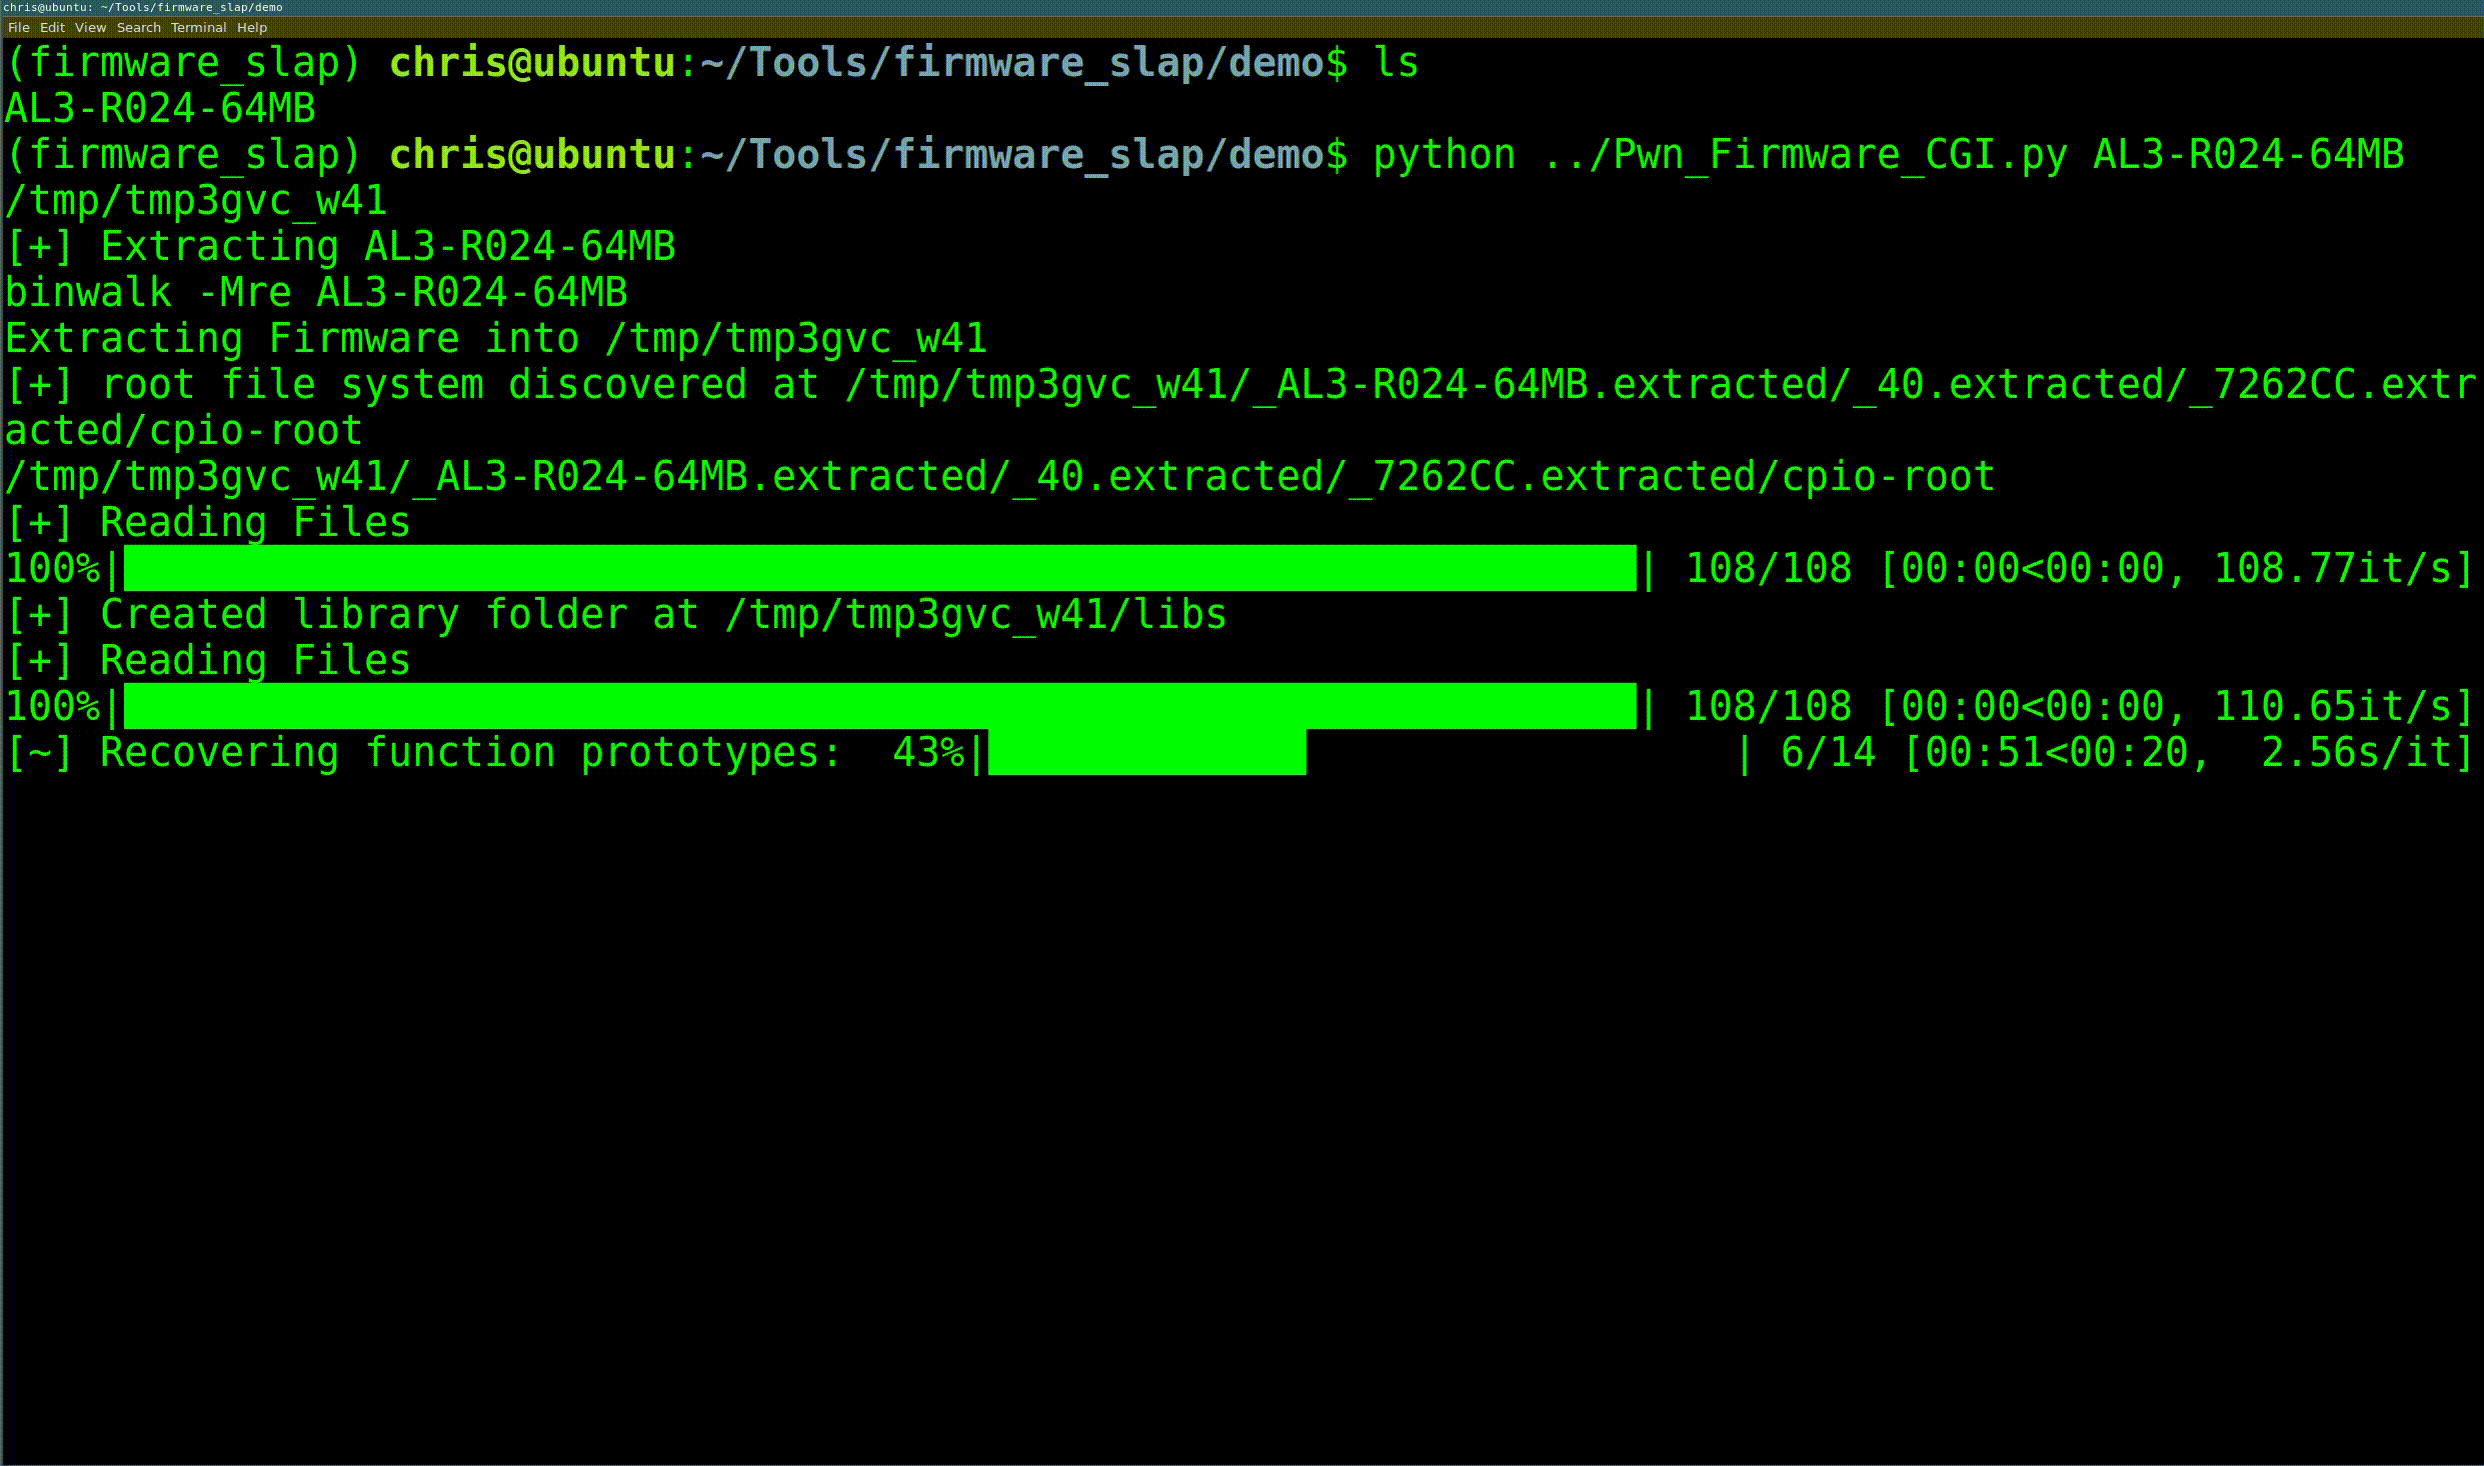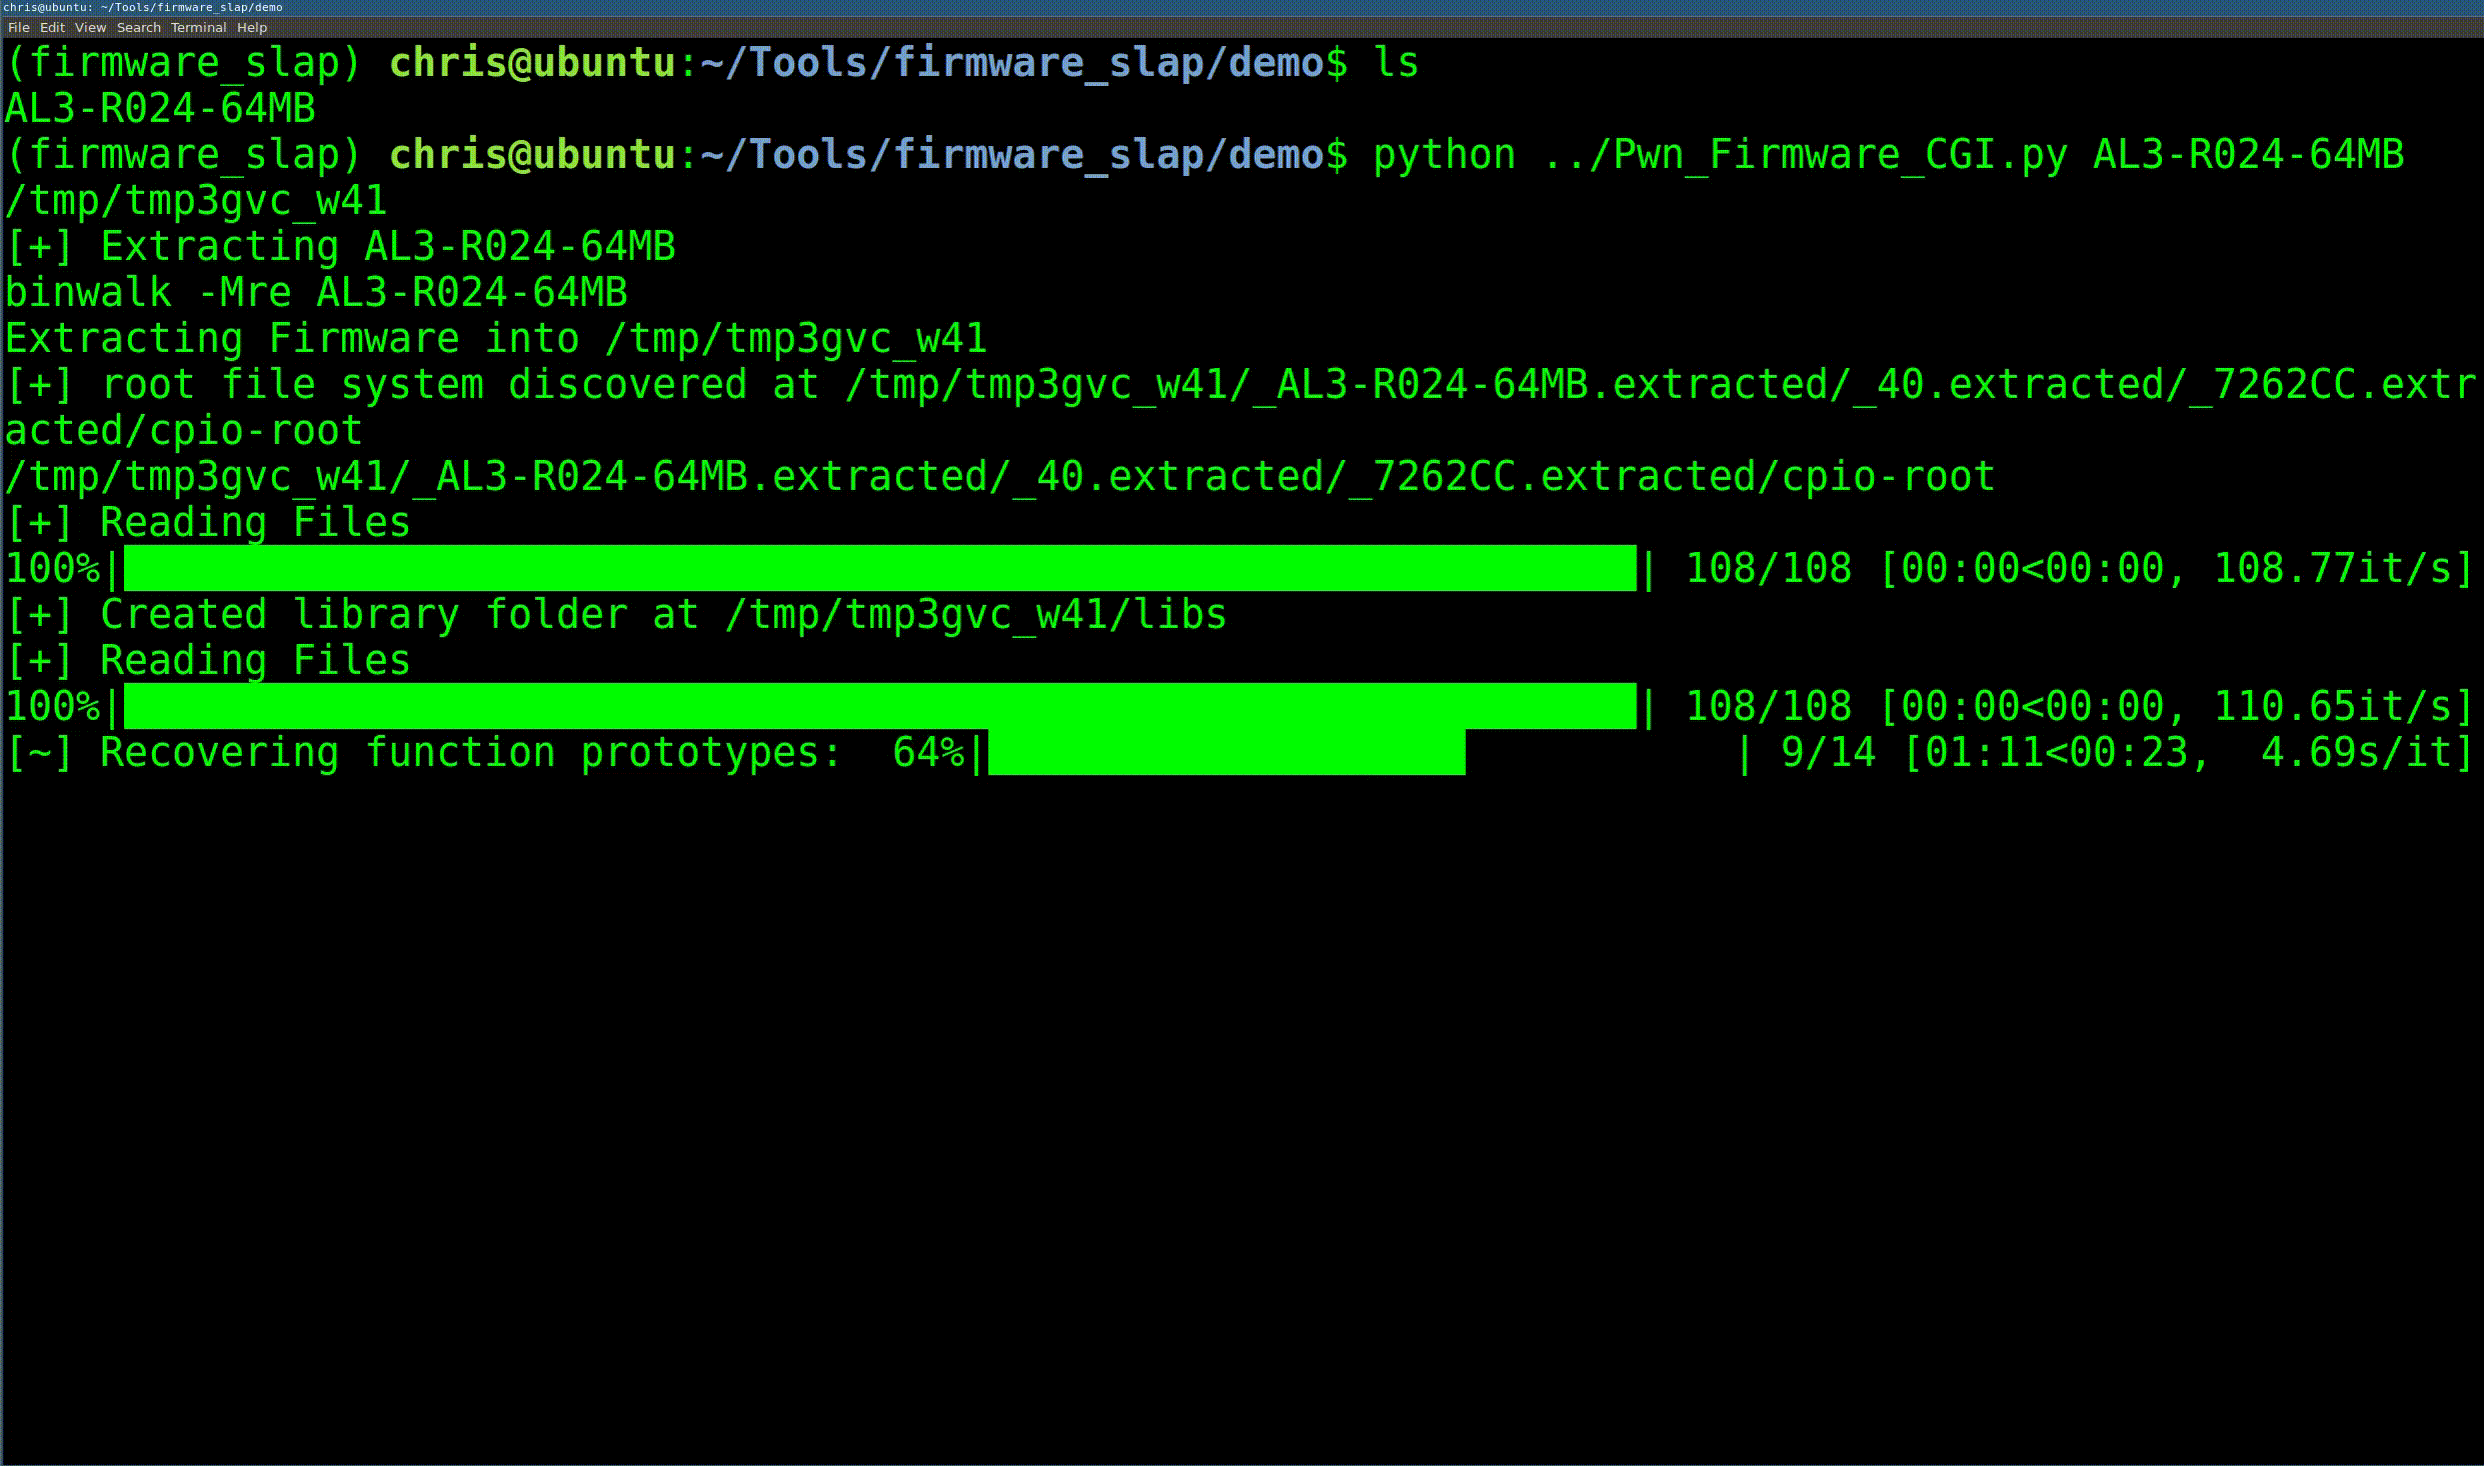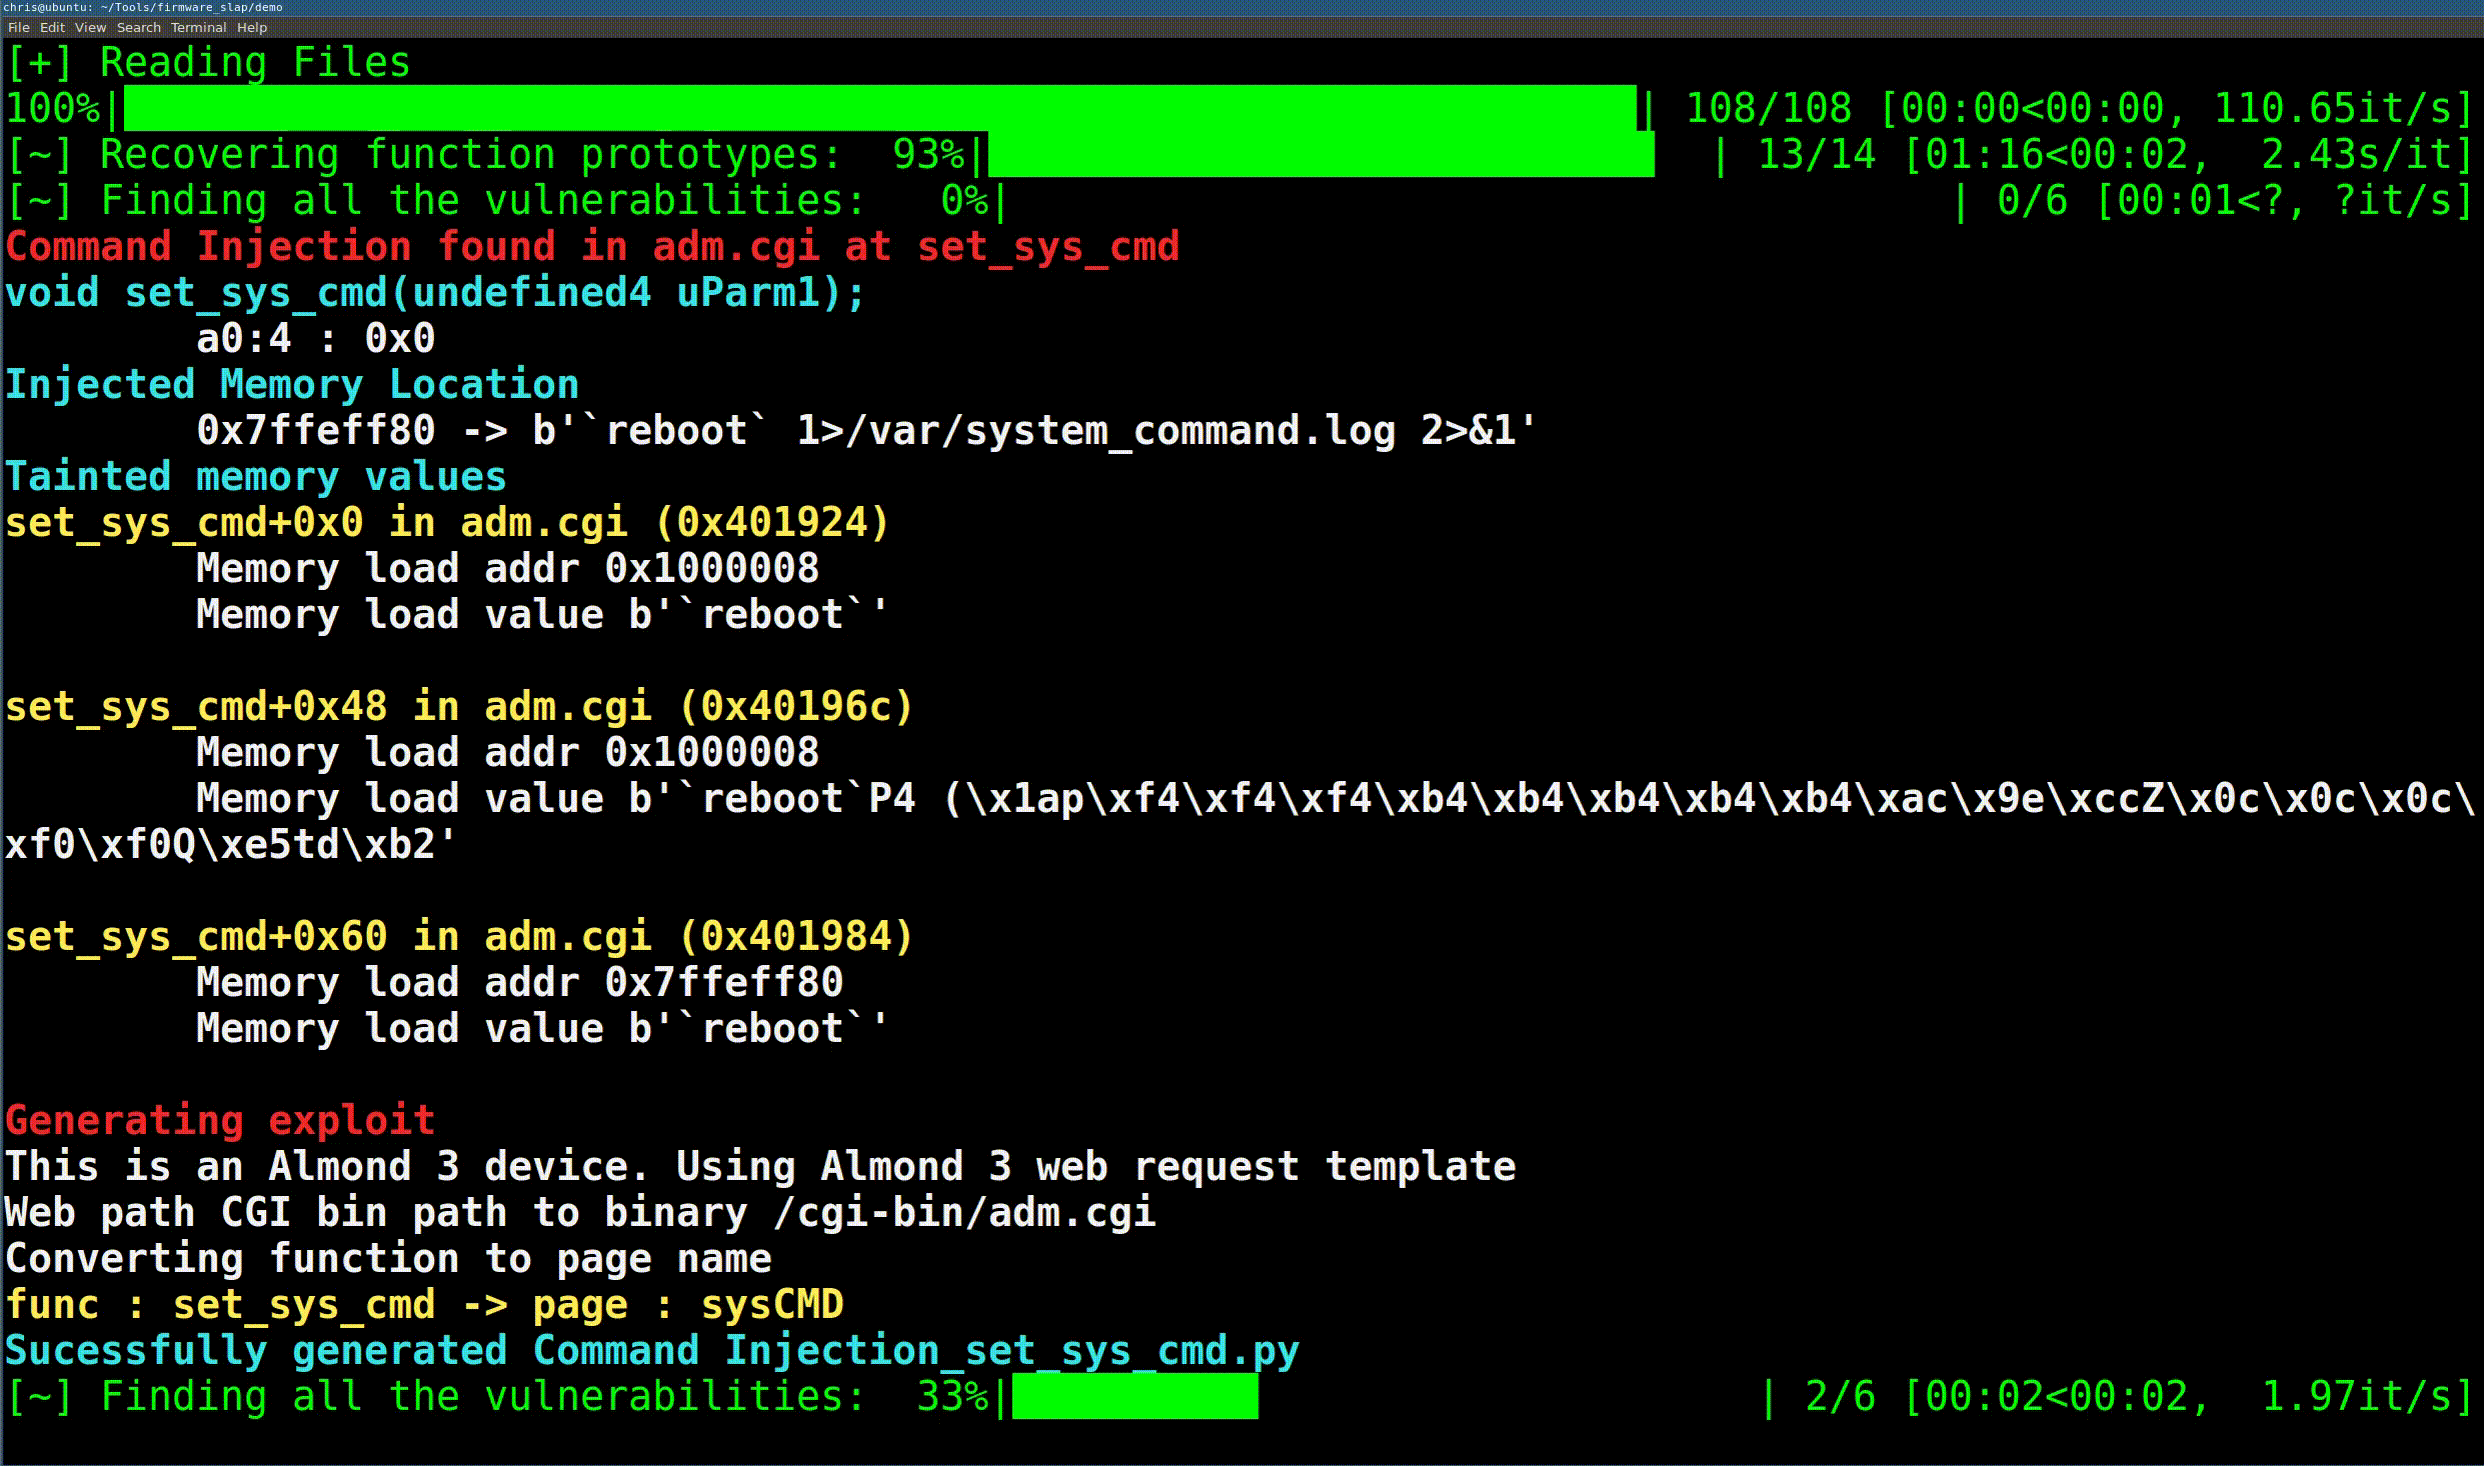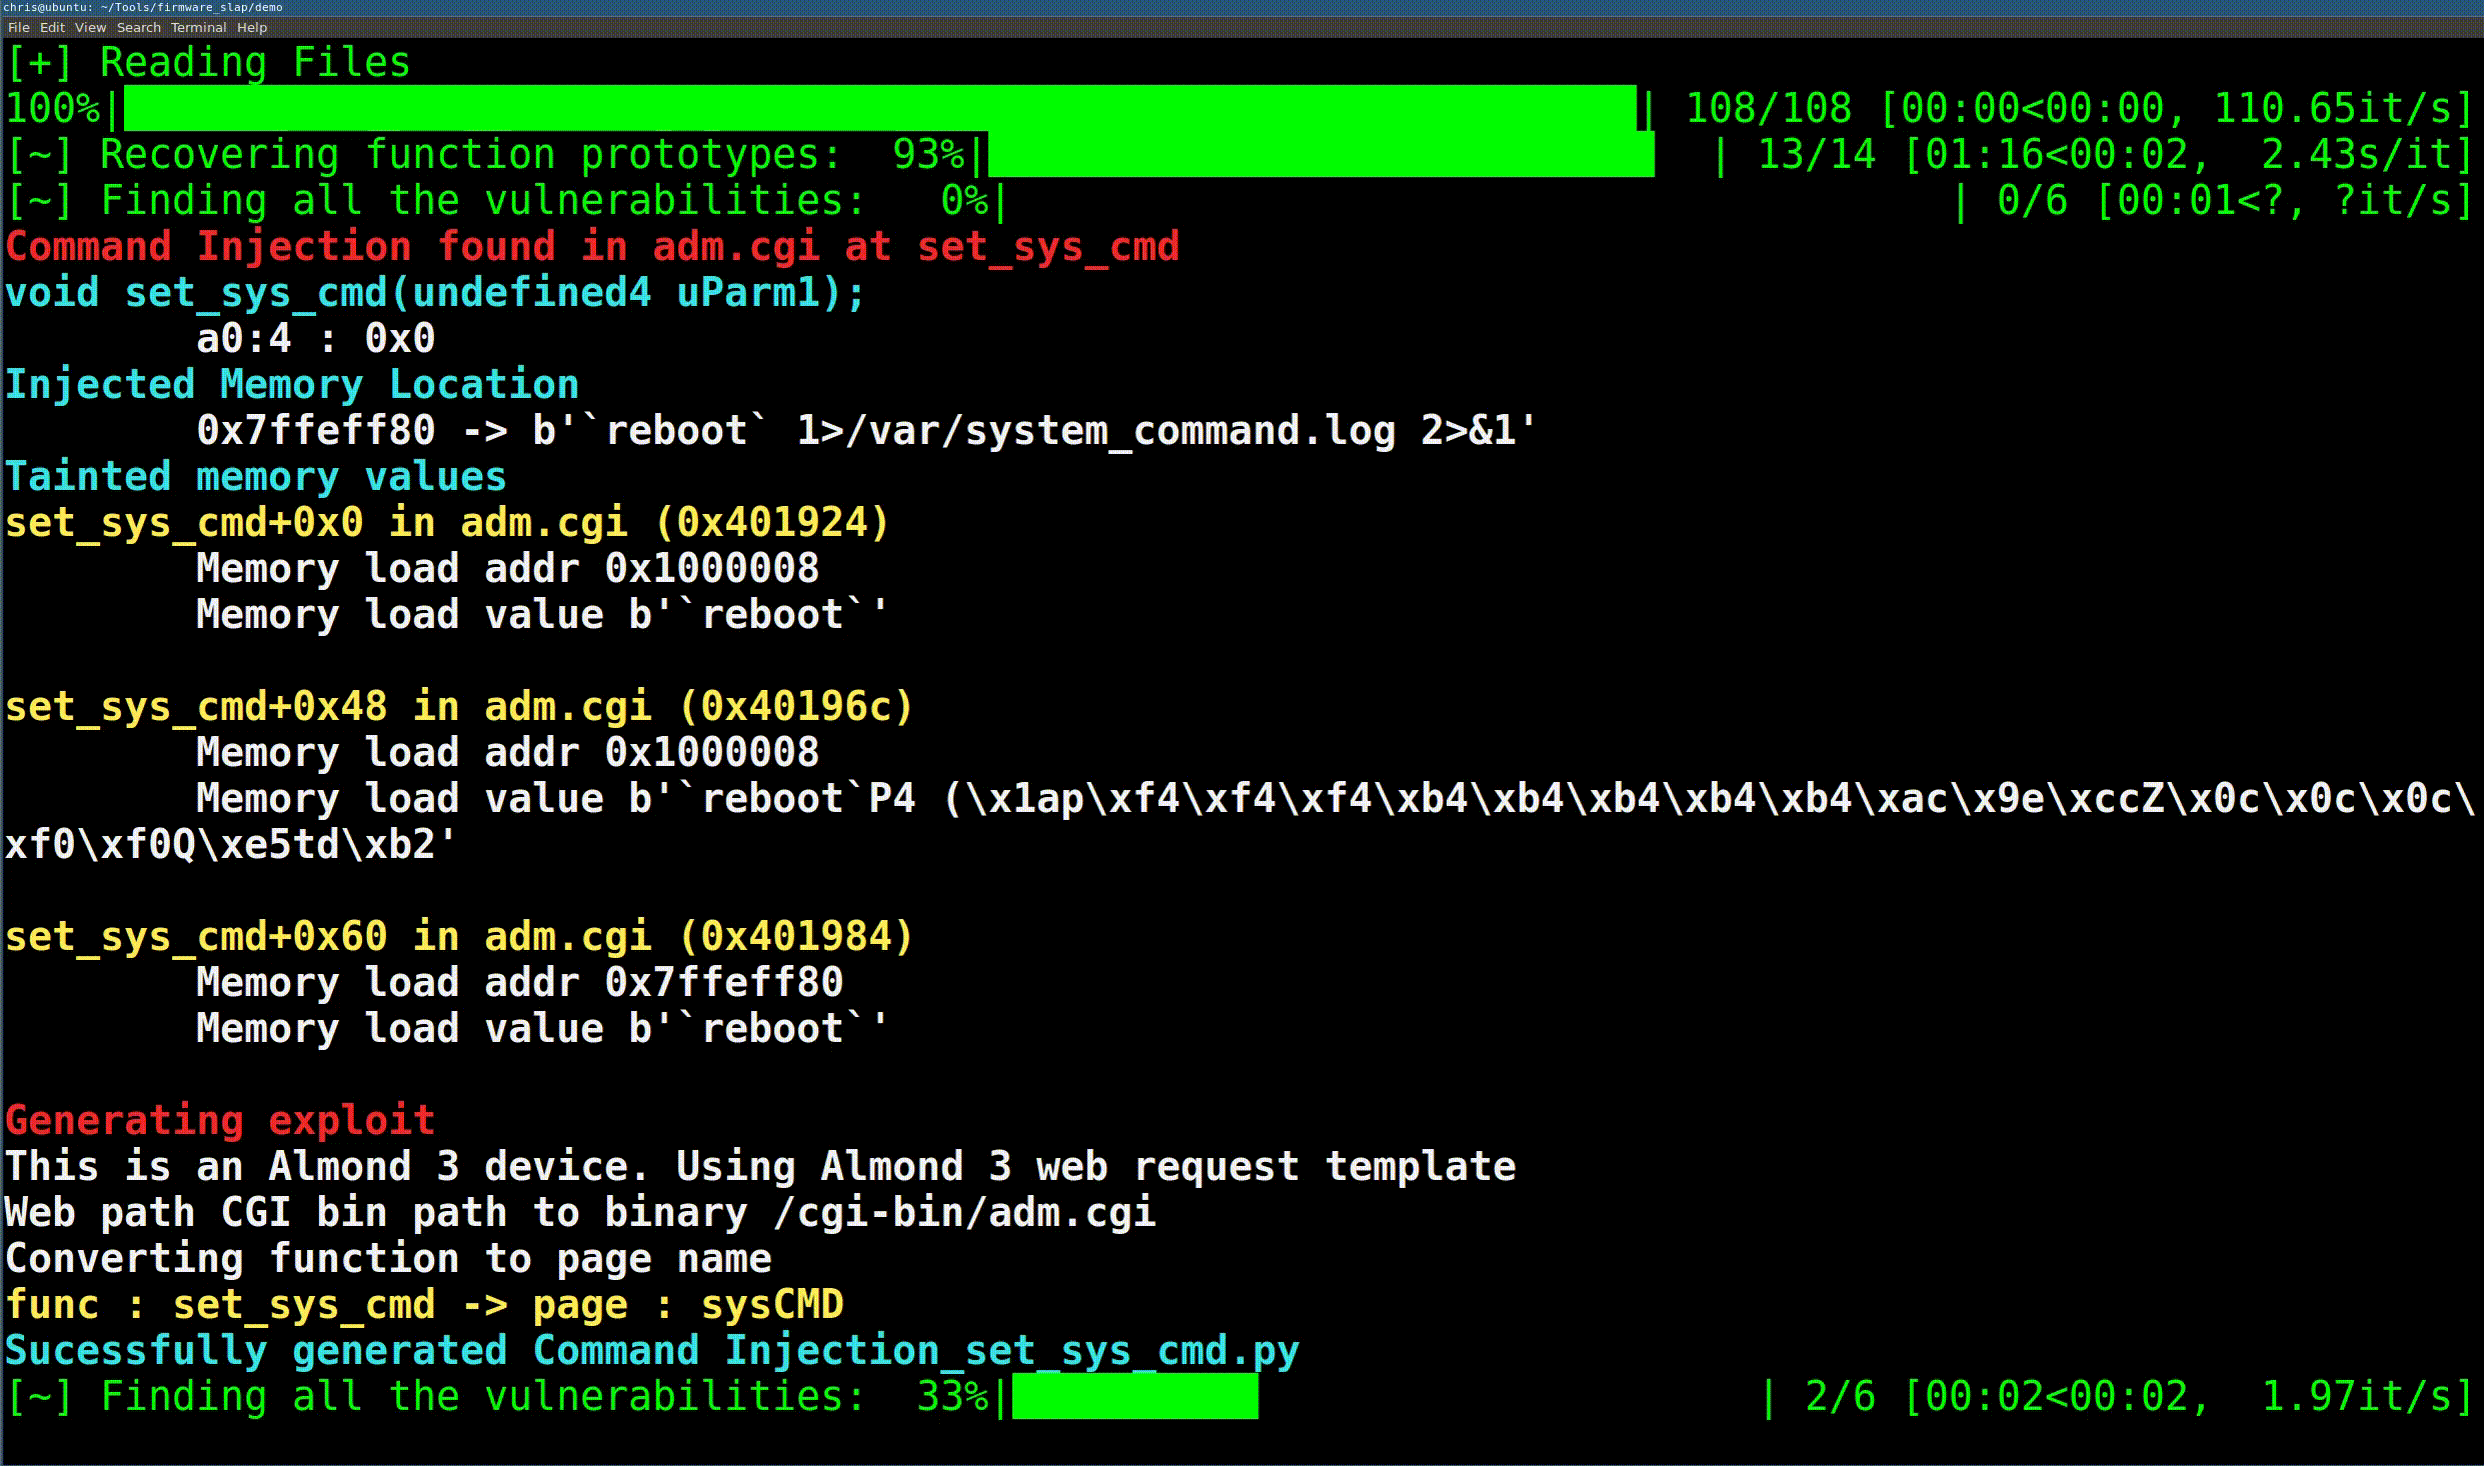 christhecoolhut/firmware_slap
Discovering vulnerabilities in firmware through concolic analysis and function clustering.
 ejfkdev/ddc
Android DEX → Java decompiler in Rust, built for speed — full apps in seconds, queries in milliseconds. Progressive analysis, javac-verified output,…
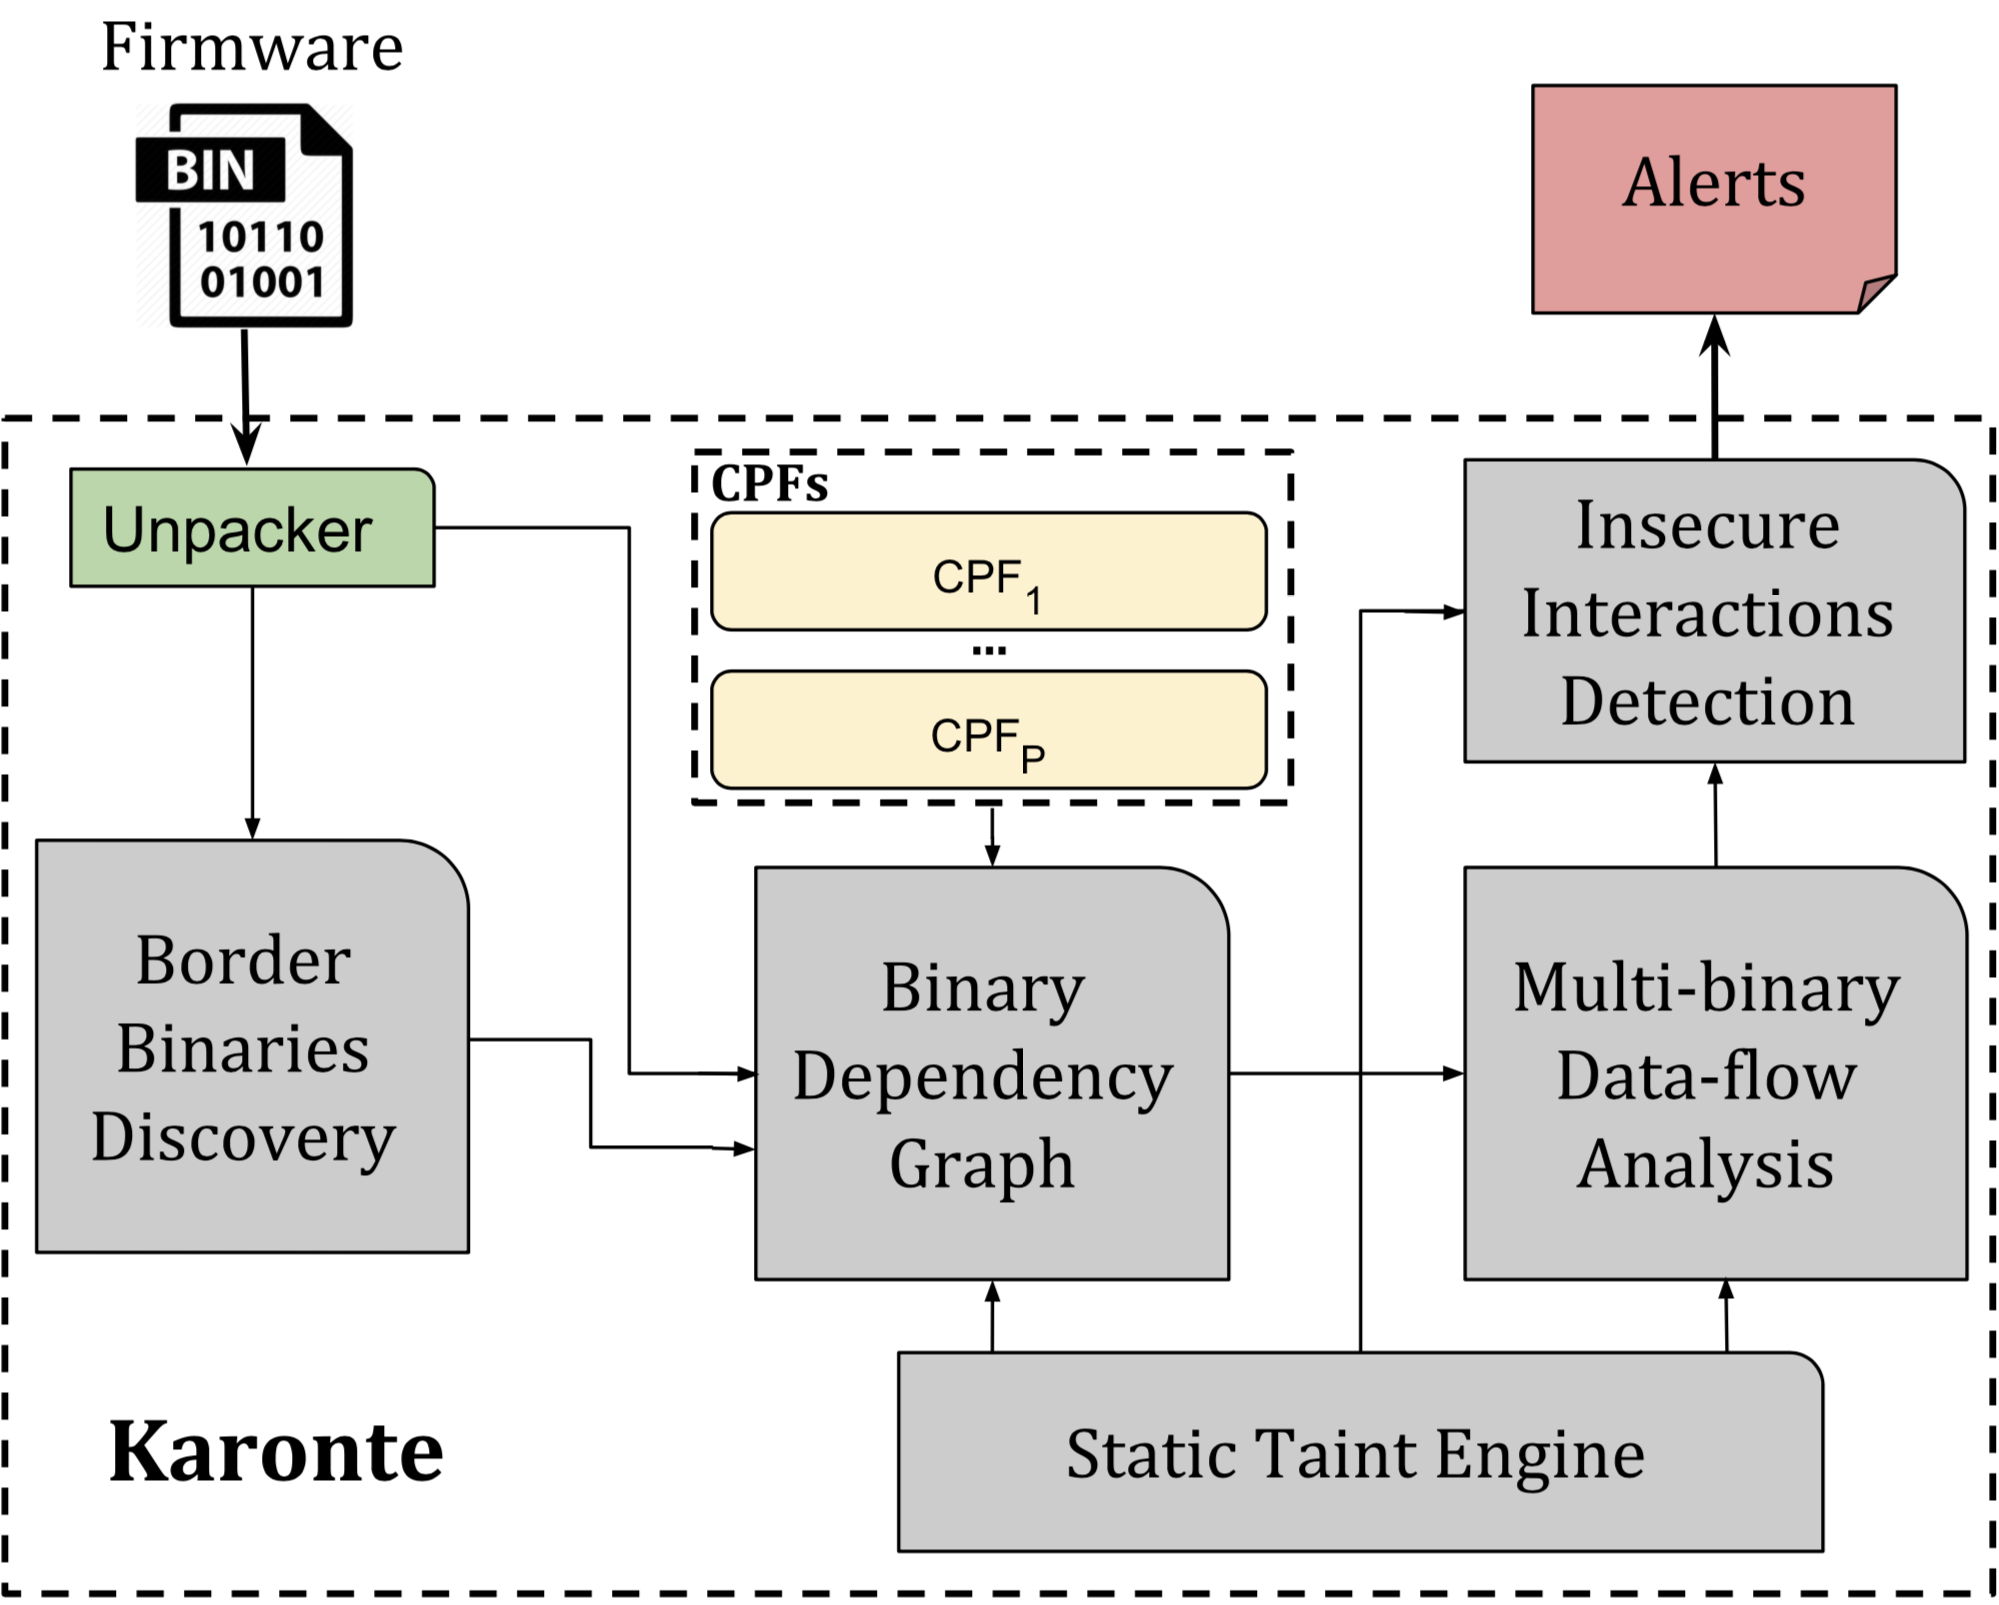 ucsb-seclab/karonte
Karonte is a static analysis tool to detect multi-binary vulnerabilities in embedded firmware
 lepotekil/msfmania
Python AV Evasion Tools
 lucamassarelli/yarasafe
SAFE embeddings to match functions in yara
 zznop/sploit
Go package that aids in binary analysis and exploitation
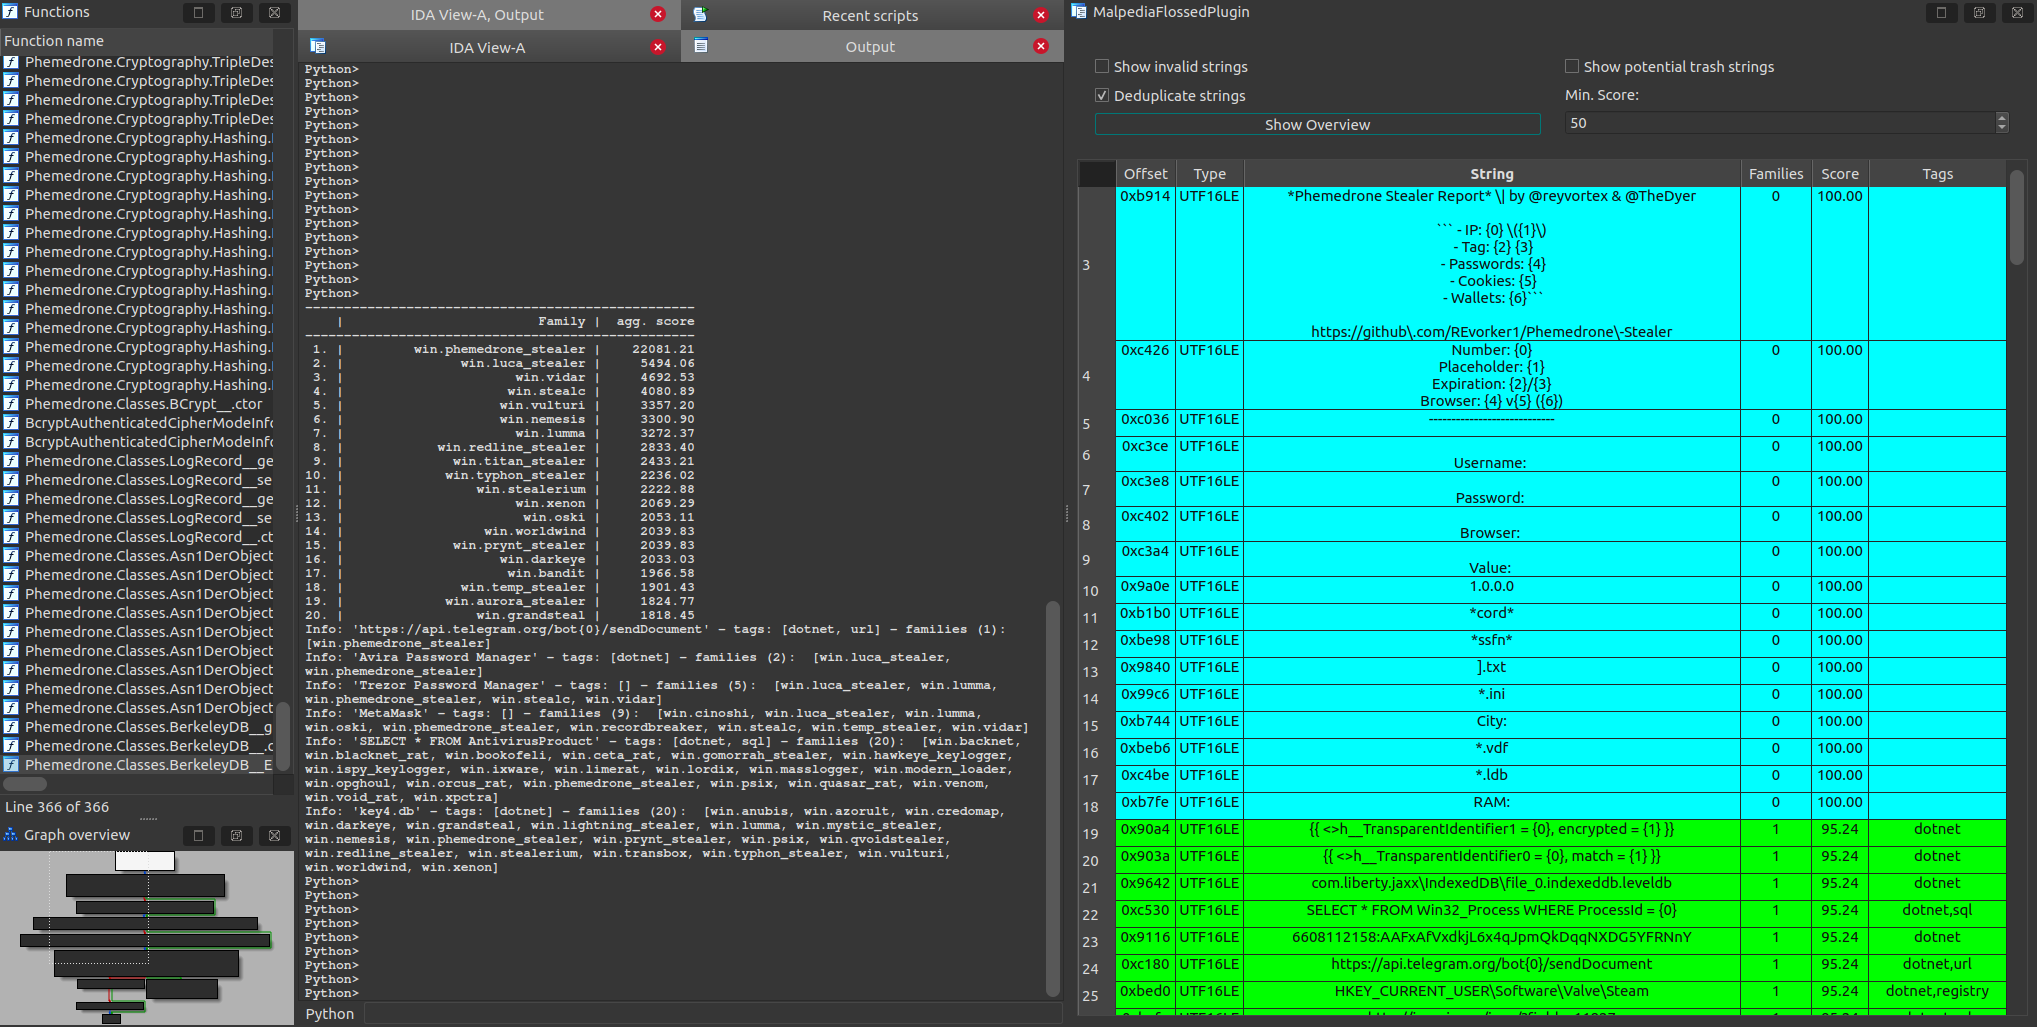 malpedia/malpedia-flossed
FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.
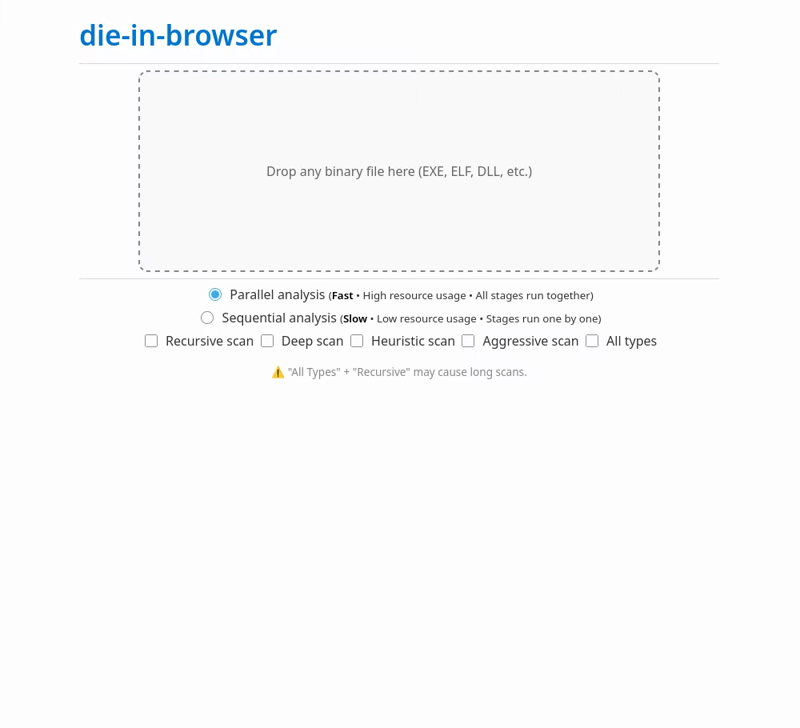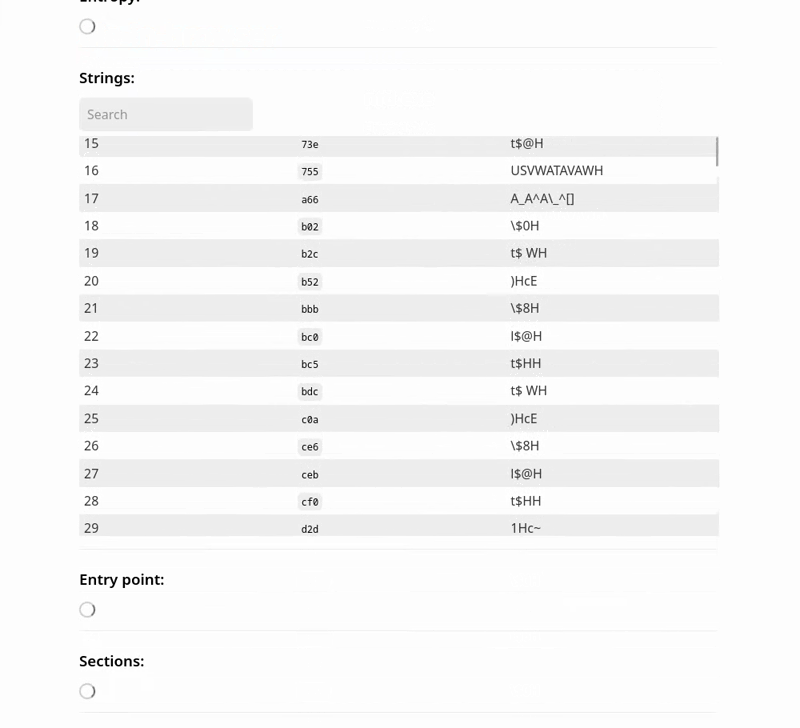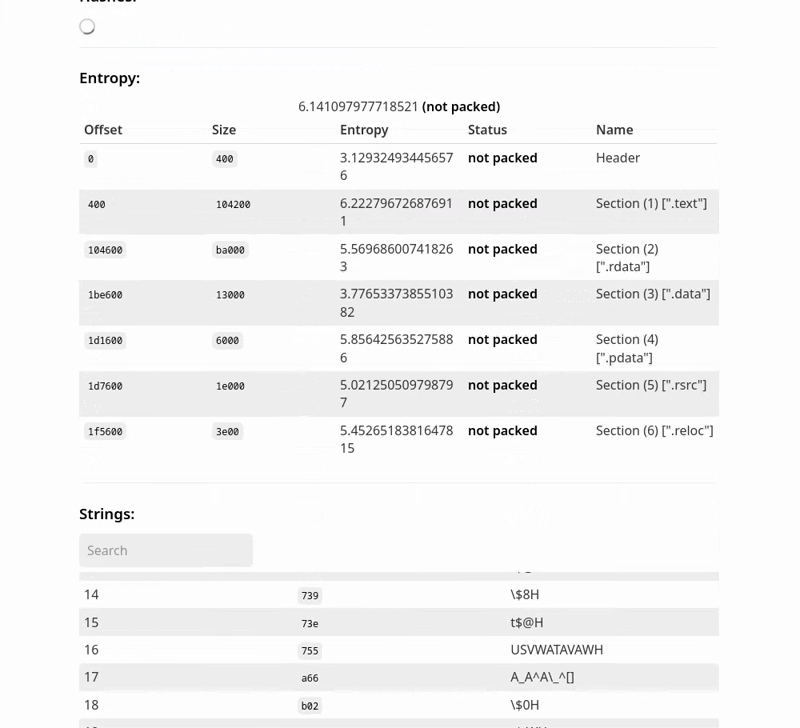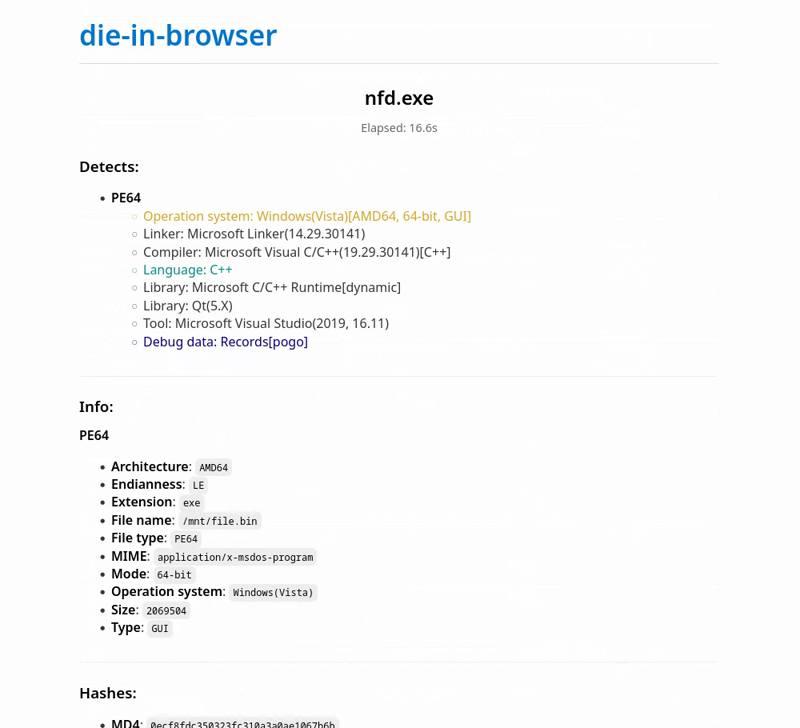 xoreaxlmbdx/die-in-browser
Static binary analysis with Detect It Easy — 100% in your browser, no uploads.
 edera-dev/cve-tarmageddon
Demonstration of CVE-2025-62518: a critical PAX extended header size override bug in tokio-tar and async Rust tar libraries, with reproduction tools…
 0x0oz/cve-2026-7482-poc
Proof-of-concept exploit for CVE-2026-7482, an unauthenticated heap out-of-bounds read in Ollama's GGUF loader, demonstrating memory exfiltration via…
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
 sdodson/cve-2026-46595-proof
Go proof-of-concept demonstrating CVE-2026-46595 in golang.org/x/crypto/ssh, using symbol inspection of stripped binaries and image scans to verify…
 shcesama/cve-2023-4863-analysis
Educational analysis of CVE-2023-4863 (libwebp heap buffer overflow) with Blue Team detection tools, static WebP scanner, defensive Java validator,…
 kaleth4/cve-2026-55200
Technical analysis and proof-of-concept for CVE-2026-55200, a critical heap-based buffer overflow in libssh2 allowing pre-authentication RCE.…
 szybnev/cve-2026-7482
Reproduces CVE-2026-7482 heap out-of-bounds read in Ollama GGUF loading and quantization, with differential analysis of quantized artifacts to…
 spiralbl0ck/learning-history-of-cff-bug-in-iphone
Dive into CFF font and coincidently learn about a bof in cff parsing from some jailbreak. just for fun
 valeriot30/cve-2024-3094
A XZ backdoor vulnerability explained in details