
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
33 results
pefile preview

pefile

GitHuberocarrera/pefile

pefile is a Python module to read and work with PE (Portable Executable) files

binary-analysisforensicsmalware-analysis+3
2.1k
3 days ago
PowerShellArsenal preview

PowerShellArsenal

GitHubmattifestation/powershellarsenal

A PowerShell Module Dedicated to Reverse Engineering

binary-analysisdebuggersdynamic-analysis-sandboxing+6
9025 years ago
Hunt-Sleeping-Beacons preview

Hunt-Sleeping-Beacons

GitHubtheflink/hunt-sleeping-beacons

Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…
binary-analysisdefensive-toolsforensics+3
6807 months ago
efiSeek preview

efiSeek

GitHubdsecurity/efiseek

Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…
binary-analysisembedded-systems-securityfirmware-analysis+3
4072 years ago
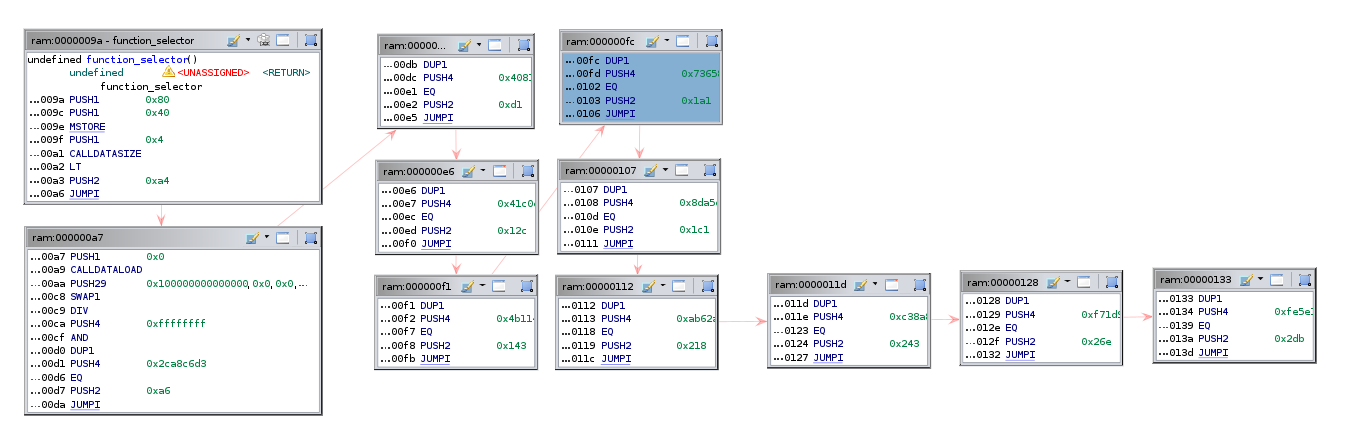
ghidra-evm preview

ghidra-evm

GitHubadelapie/ghidra-evm

Ghidra module for disassembling, decompiling, and analyzing Ethereum smart contract bytecode. Detects insecure instructions, extracts hidden methods,…
binary-analysisreverse-engineeringstatic-analysis+1
1495 years ago
ida_kcpp preview

ida_kcpp

GitHubcellebrite-labs/ida_kcpp

An IDAPython module for enhancing c++ support on top of ida_kernelcache
binary-analysisios-securitymobile-security+2
1441 month ago
ModuleStomping preview

ModuleStomping

GitHubwithsecurelabs/modulestomping

Research and proof-of-concept for module stomping, a technique to hide malicious code in legitimate Windows modules, with documentation and…
binary-analysismalware-analysisred-teaming
1256 years ago
DLLHSC preview

DLLHSC

GitHubctxis/dllhsc

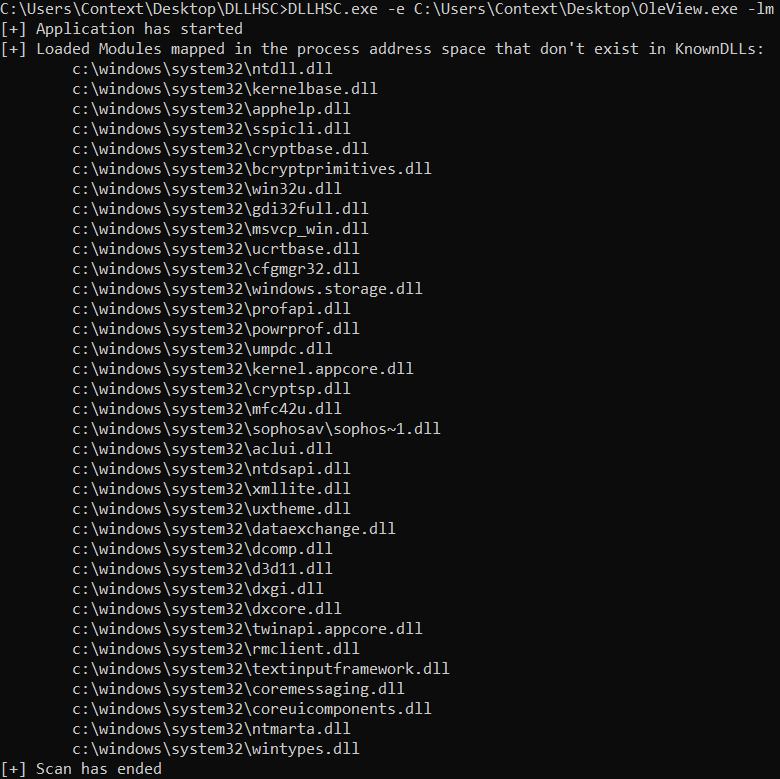
Automated scanner for discovering DLL search order hijacking candidates in Windows executables, featuring import table parsing, runtime module…

binary-analysisexploitationpayload-development+1
1586 years ago
Maverick preview

Maverick

GitHubblacksnufkin/maverick

Adaptix C2 agent using Crystal Palace PIC linker and PICO module system

binary-analysiscommand-and-controlencryption-decryption-tools+5
1153 months ago
patriot preview

patriot

GitHubjoe-desimone/patriot

In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…
anomaly-detectionbinary-analysisdefensive-tools+3
1644 years ago
machofile preview

machofile

GitHubpstirparo/machofile

machofile is a module to parse Mach-O binary files

binary-analysisforensicsmalware-analysis+2
997 months ago
Get-PDInvokeImports preview

Get-PDInvokeImports

GitHubdump-guy/get-pdinvokeimports

PowerShell module for automatic detection of P/Invoke, Dynamic P/Invoke, and D/Invoke in .NET assemblies. Reveals unmanaged API calls, MDTokens, and…

binary-analysismalware-analysisreverse-engineering+1
544 years ago
ghidra-nanomips preview

ghidra-nanomips

GitHubnccgroup/ghidra-nanomips

nanoMIPS module for Ghidra

binary-analysisembedded-systems-securityreverse-engineering+1
5610 months ago
drvtrace preview

drvtrace

GitHubeversinc33/drvtrace

WinDbg plugin to trace module transitions from a debugged driver.
binary-analysisdebuggersreverse-engineering
548 months ago
magisk-renef preview

magisk-renef

GitHubvichhka-git/magisk-renef

Magisk module that auto-packages renef_server (dynamic instrumentation for Android)
android-securitybinary-analysisdynamic-analysis-sandboxing+3
344 months ago
Advanced-Loader-Reverse-Engineering preview

Advanced-Loader-Reverse-Engineering

GitHubkaandemir993/advanced-loader-reverse-engineering

"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…
binary-analysiscode-analysiseducation+8
142 months ago
Ghidra_v810_v830 preview

Ghidra_v810_v830

GitHub20enderdude20/ghidra_v810_v830

Ghidra processor description module for NEC/Renesas v810 and v830 families
binary-analysisembedded-systems-securityfirmware-analysis+3
75 months ago
YARA_for_config_extraction preview

YARA_for_config_extraction

GitHubtheatha/yara_for_config_extraction

Tutorial and source code for building a custom YARA module in C to extract malware configurations, with a practical Danabot example and reusable…

binary-analysiseducationmalware-analysis+1
82 years ago
Previous12Next