
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
175 results
COFFLoader preview

COFFLoader

GitHubtrustedsec/coffloader

Run Beacon Object Files (BOFs) outside Cobalt Strike by parsing 64-bit COFF object files, with Beacon-compatible argument generation and helper…
binary-analysispayload-developmentpenetration-testing+2
652
6 days ago
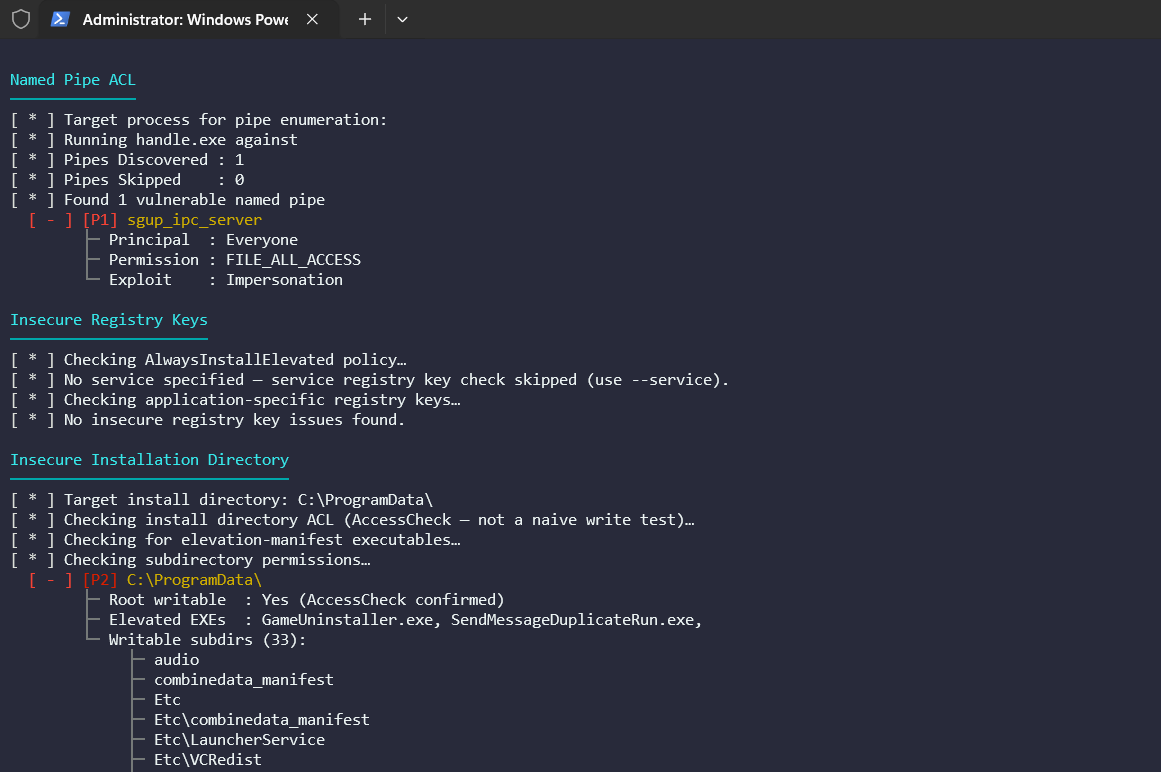
Anvil preview

Anvil

GitHubshellkraft/anvil

Anvil is a runtime-first attack surface assessment tool for Windows thick client applications, built for penetration testers and security researchers…
binary-analysisexploitationpenetration-testing+5
386 months ago
xzbot preview

xzbot

GitHubamlweems/xzbot

notes, honeypot, and exploit demo for the xz backdoor (CVE-2024-3094)

binary-analysiscryptographyexploitation+3
3.6k2 years ago
DeepZero preview

DeepZero

GitHub416rehman/deepzero

Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
ai-assisted-reversingbinary-analysisfuzzing+3
7187 days ago
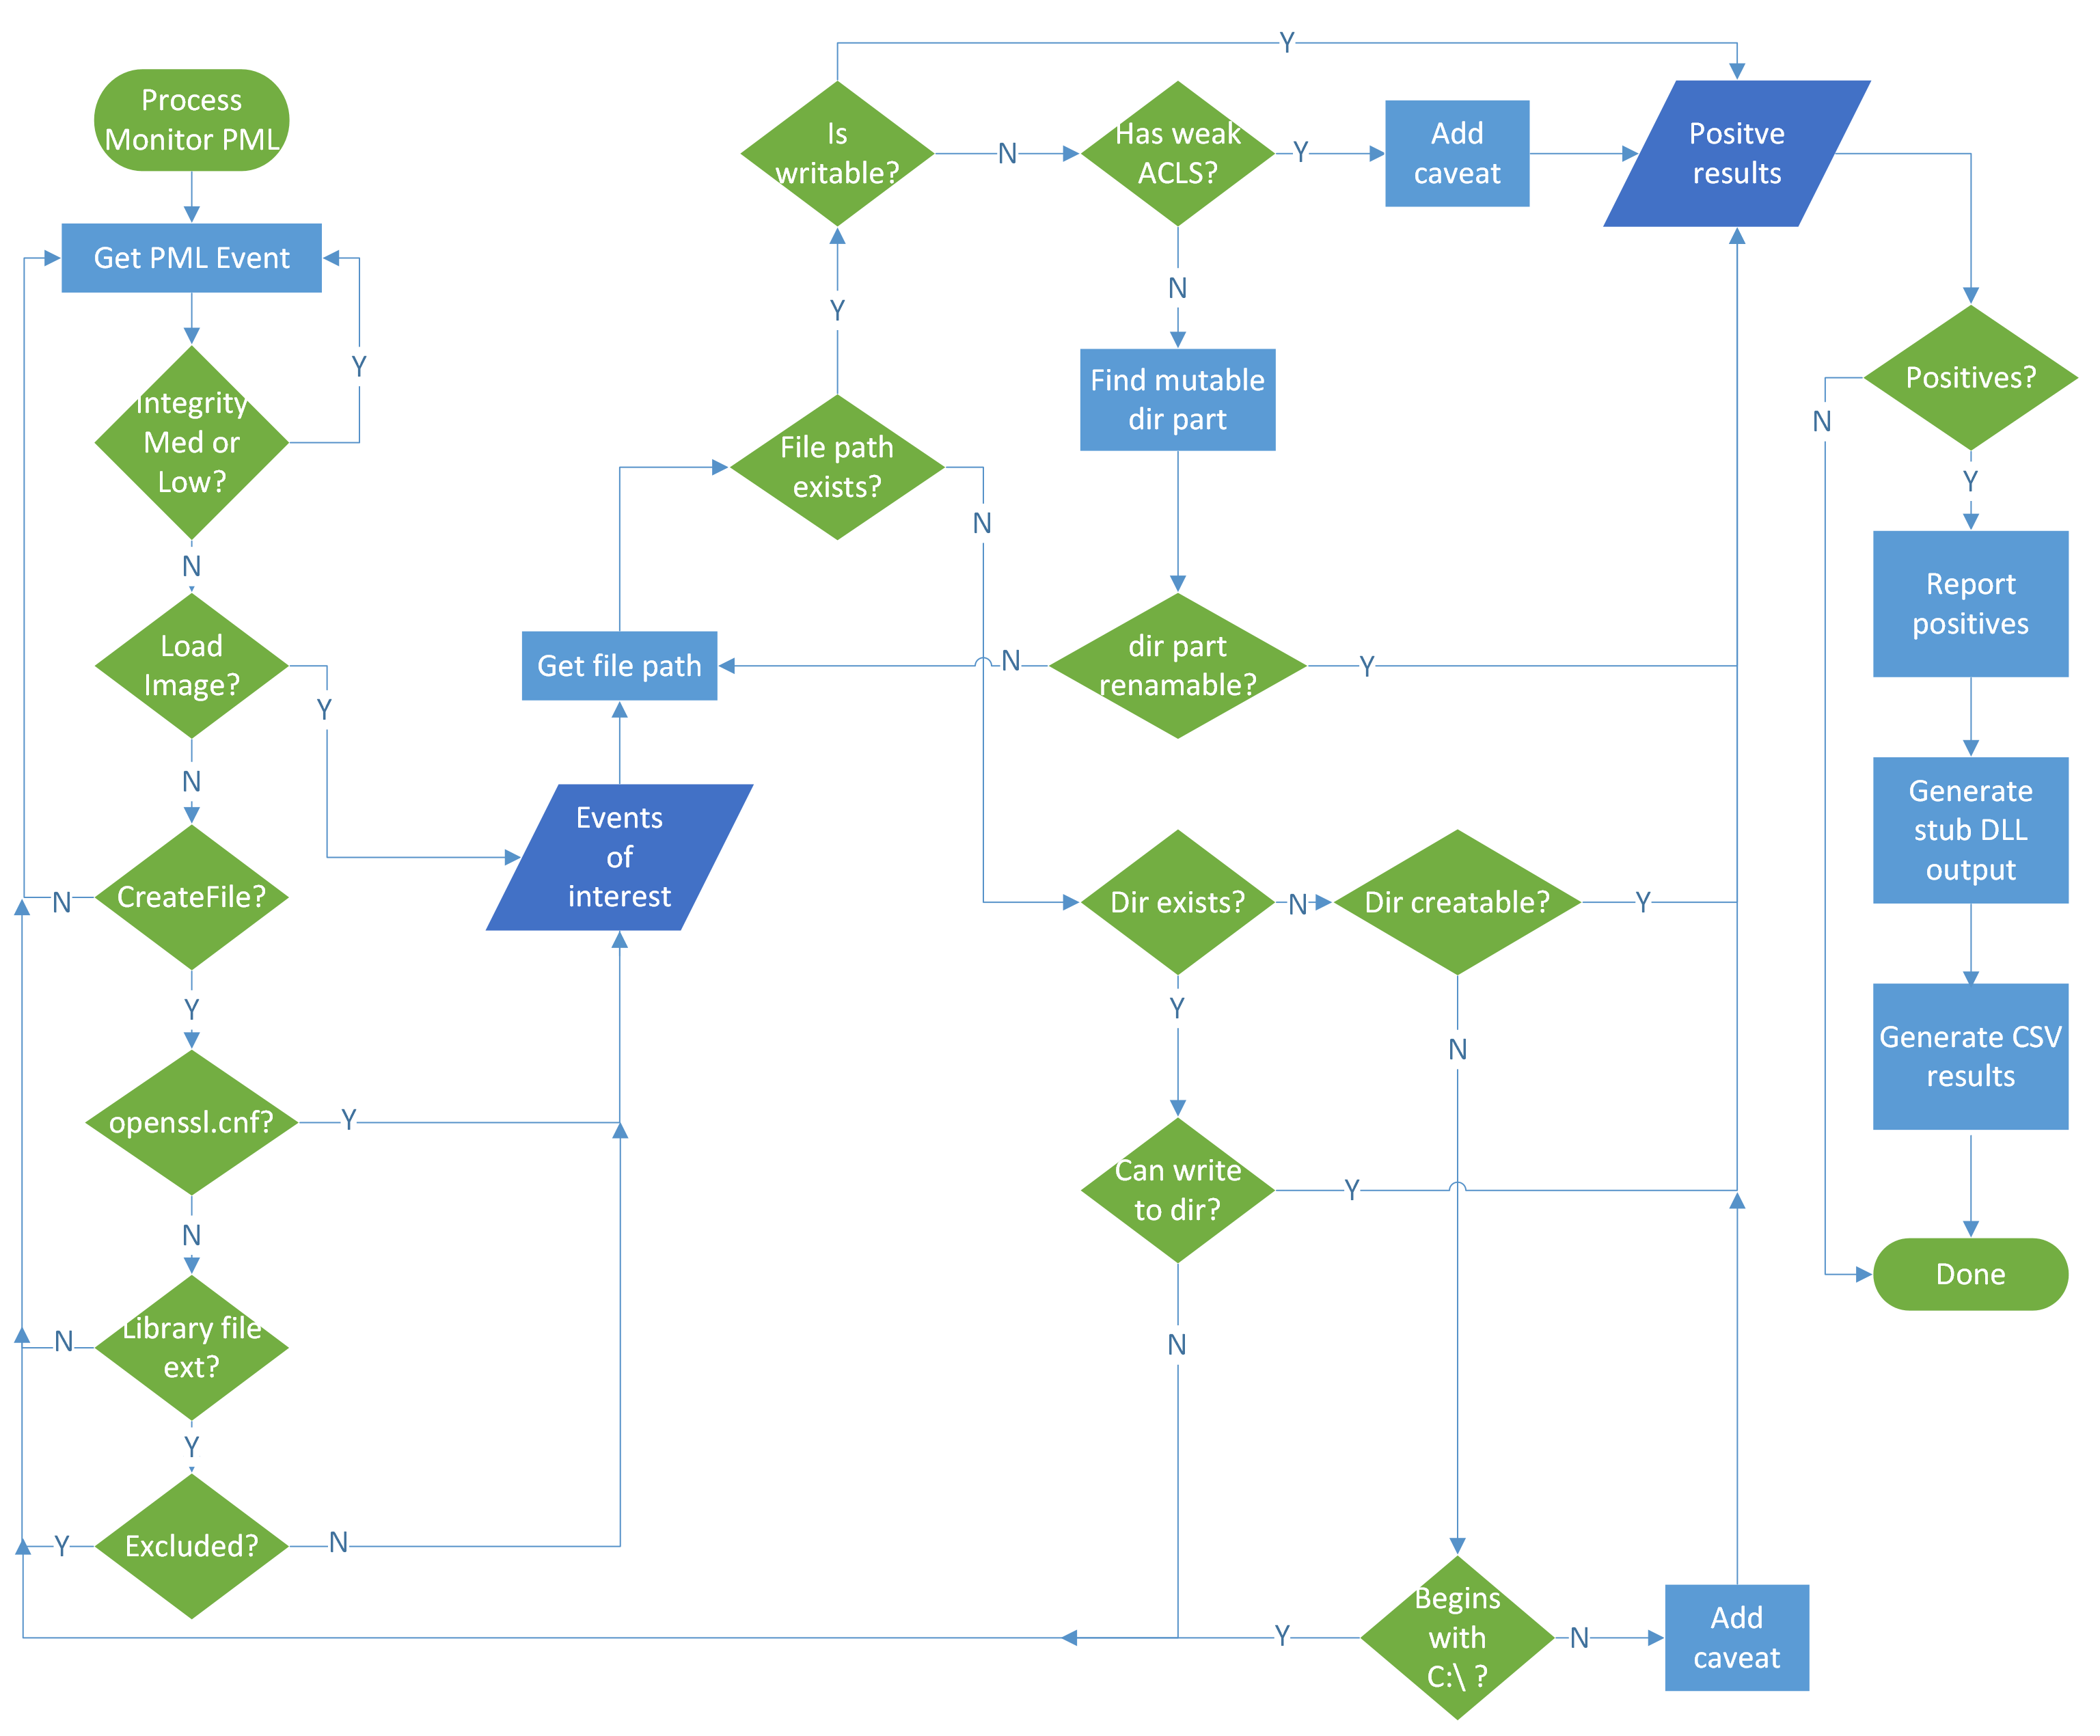
Crassus preview

Crassus

GitHubvu-ls/crassus

Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…
binary-analysisexploitationpenetration-testing+1
6327 months ago
Evasor preview

Evasor

GitHubcyberark/evasor

A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies
binary-analysisdefensive-toolspenetration-testing+3
3266 years ago
PrivKit preview

PrivKit

GitHubmertdas/privkit

PrivKit is a simple beacon object file that detects privilege escalation vulnerabilities caused by misconfigurations on Windows OS.
binary-analysisexploitationpenetration-testing+4
6217 months ago
sgx-step preview

sgx-step

GitHubjovanbulck/sgx-step

A practical attack framework for precise enclave execution control

binary-analysisexploitationhardware-security+1
4808 days ago
javaserializetools preview

javaserializetools

GitHubshack2/javaserializetools

Java反序列化漏洞利用工具V1.0 Java反序列化相关漏洞的检查工具,采用JDK 1.8+NetBeans8.2开发,软件运行必须安装JDK 1.8或者以上版本。 支持:weblogic xml反序列化漏洞…

binary-analysisexploitationpenetration-testing+2
5155 years ago
LeakedHandlesFinder preview

LeakedHandlesFinder

GitHublab52io/leakedhandlesfinder

Leaked Windows processes handles identification tool
binary-analysisexploitationpenetration-testing+1
2994 years ago
RpcInvestigator preview

RpcInvestigator

GitHubtrailofbits/rpcinvestigator

Windows RPC interface discovery and analysis tool with visual endpoint enumeration, PE parsing, symbol resolution, real-time ETW sniffing, and…
binary-analysispenetration-testingreverse-engineering+1
3652 years ago
ansvif preview

ansvif

GitHuboxagast/ansvif

A Not So Very Intelligent Fuzzer: An advanced fuzzing framework designed to find vulnerabilities in C/C++ code.
binary-analysisexploitationfuzzing+2
1055 years ago
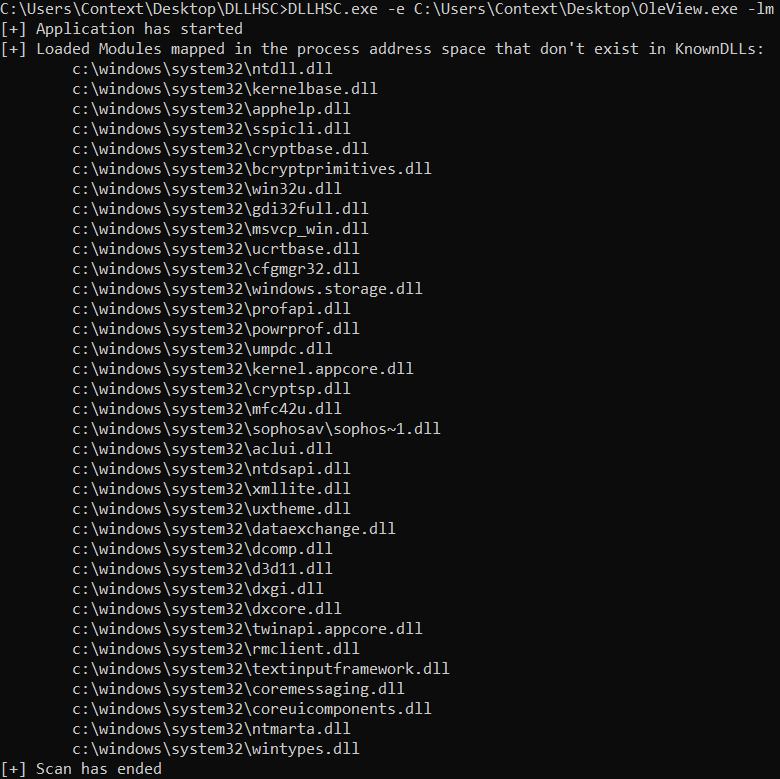
DLLHSC preview

DLLHSC

GitHubctxis/dllhsc

Automated scanner for discovering DLL search order hijacking candidates in Windows executables, featuring import table parsing, runtime module…
binary-analysisexploitationpayload-development+1
1586 years ago
HolyGrail preview

HolyGrail

GitHubblacksnufkin/holygrail

BYOVD hunter to help prioritize windows drivers worth manual analysis

binary-analysisexploitationpenetration-testing+2
1321 year ago
fluffi preview

fluffi

GitHubsiemens/fluffi

FLUFFI (Fully Localized Utility For Fuzzing Instantaneously) - A distributed evolutionary binary fuzzer for pentesters
binary-analysisfuzzingpenetration-testing+1
1024 years ago
r0ak preview

r0ak

GitHubown2pwn/r0ak

r0ak ("roak") is the Ring 0 Army Knife -- A Command Line Utility To Read/Write/Execute Ring Zero on for Windows 10 Systems
binary-analysisexploitationpenetration-testing+3
278 years ago
CVE-2025-21420_POC preview

CVE-2025-21420_POC

GitHubmoiz-2x/cve-2025-21420_poc

Proof of Concept CVE-2025-21420 (Windows Disk Cleanup Tool EoP)
binary-analysisexploitationpenetration-testing+2
561 year ago
doona preview

doona

GitHubwireghoul/doona

Network based protocol fuzzer

binary-analysisexploitationfuzzing+3
774 years ago
Previous12…10Next