
KVM-Januscape
 xj2268-ta/kvm-januscape
CVE-2026-53359漏洞补丁
binary-analysisexploitationvulnerability-analysis
xj2268-ta/kvm-januscapeCVE-2026-53359漏洞补丁
 vorkampfer/pwnkit_safety_check
PwnKit (CVE-2021-4034) Safe Checker This tool performs read-only checks and does not attempt exploitation.
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 gallopsled/pwntools
CTF framework and exploit development library
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 e-m-b-a/emba
EMBA - The firmware security analyzer
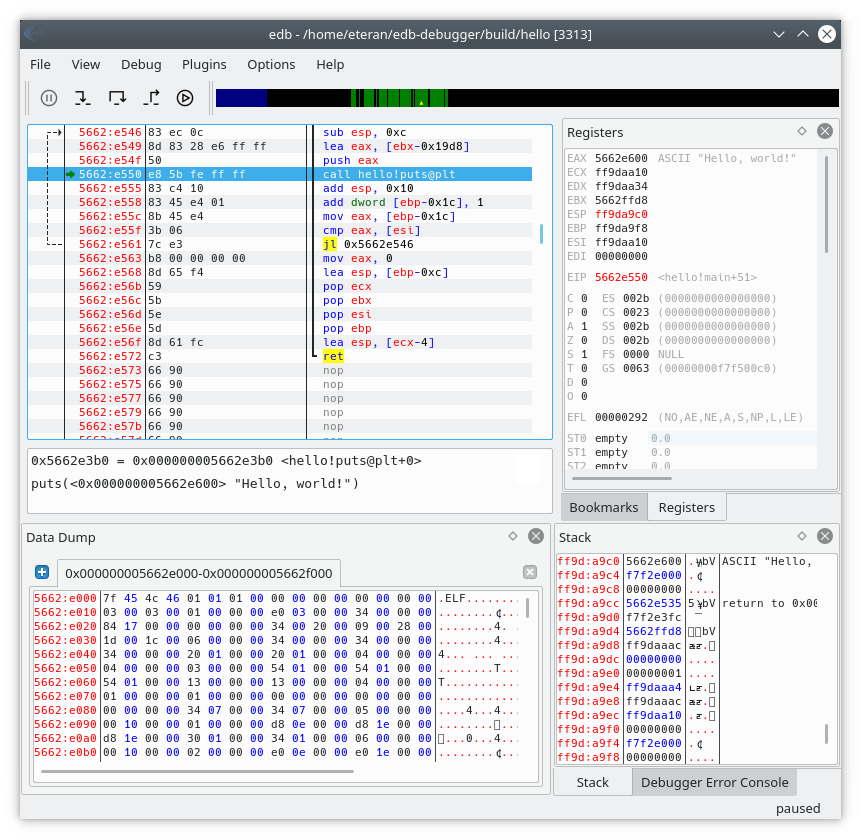 eteran/edb-debugger
edb is a cross-platform AArch32/x86/x86-64 debugger.
 marin-m/vmlinux-to-elf
A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)
 0xdea/frida-scripts
A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.
 igio90/dwarf
Full featured multi arch/os debugger built on top of PyQt5 and frida
 nmatt0/moria
IoT firmware identification and extraction

 zeropointdynamics/zelos
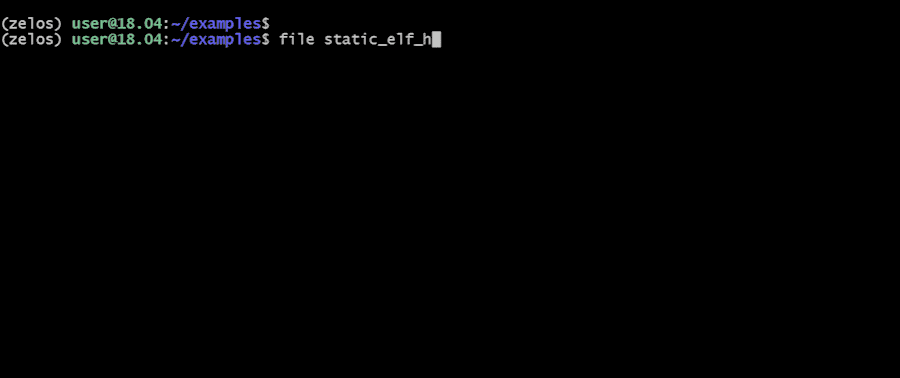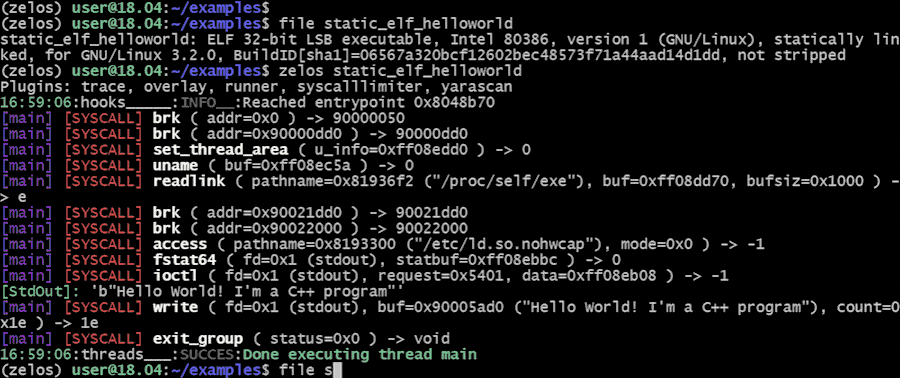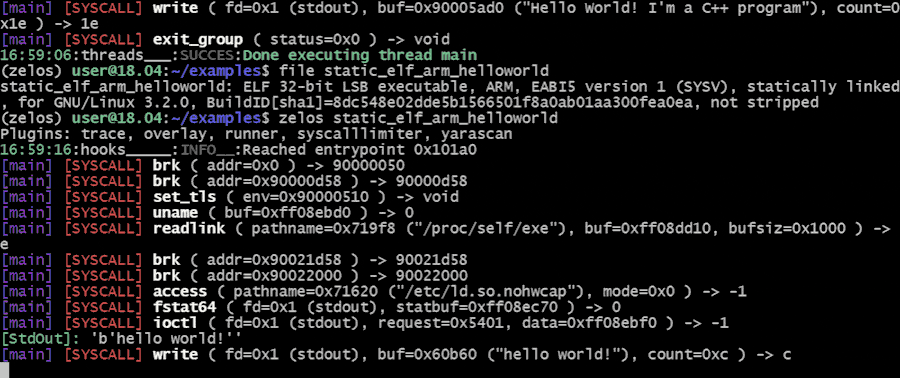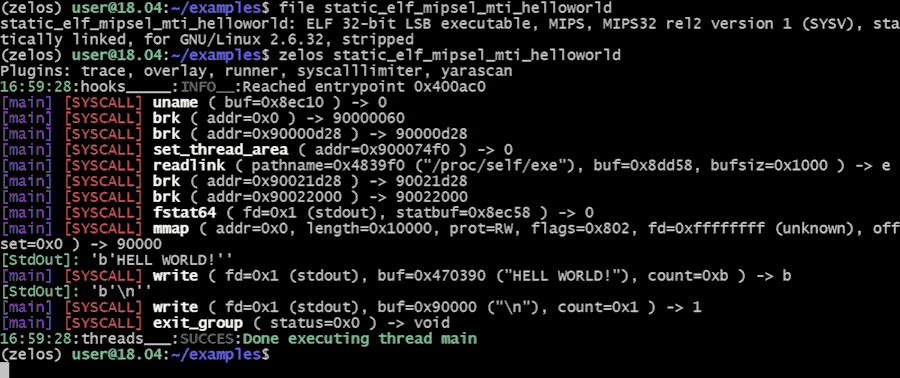
A comprehensive binary emulation and instrumentation platform.
 hugsy/gdb-static
Public repository of statically compiled GDB and GDBServer
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 boratanrikulu/gobee
Write your BPF programs in Go, not C. gobee transpiles a Go subset to BPF C and generates typed cilium/ebpf bindings.
 romainthomas/reverse-engineering-workshop
Slides & Hands-on for the reverse engineering workshop