
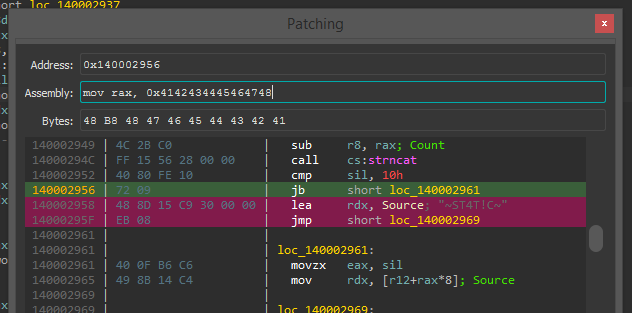
patching
 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
binary-analysisbinary-exploitationdebuggers+8
gaasedelen/patchingAn Interactive Binary Patching Plugin for IDA Pro
 team-atlanta/aixcc-afc-atlantis
Automated cyber reasoning system that discovers and analyzes software vulnerabilities through fuzzing, binary analysis, and program reasoning for…
 endgameinc/xori
Xori is an automation-ready disassembly and static analysis library for PE32, 32+ and shellcode
 trailofbits/maat
Dynamic symbolic execution and binary analysis framework with taint analysis, constraint solving, multi-arch emulation via Ghidra's Sleigh, and…
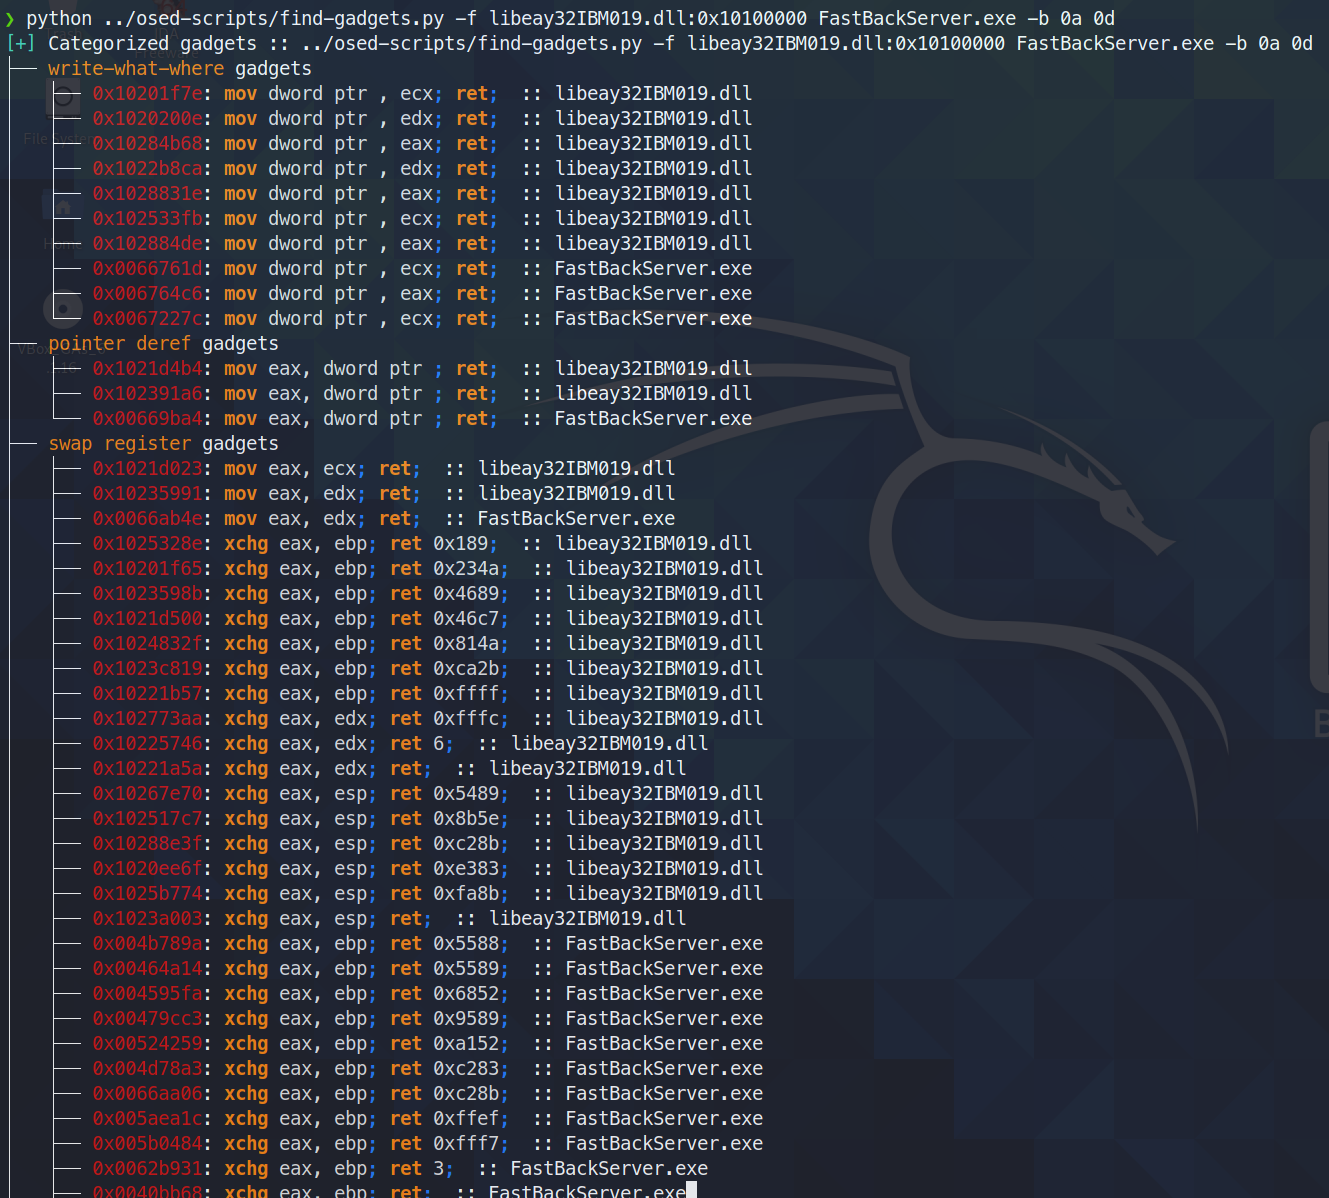 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
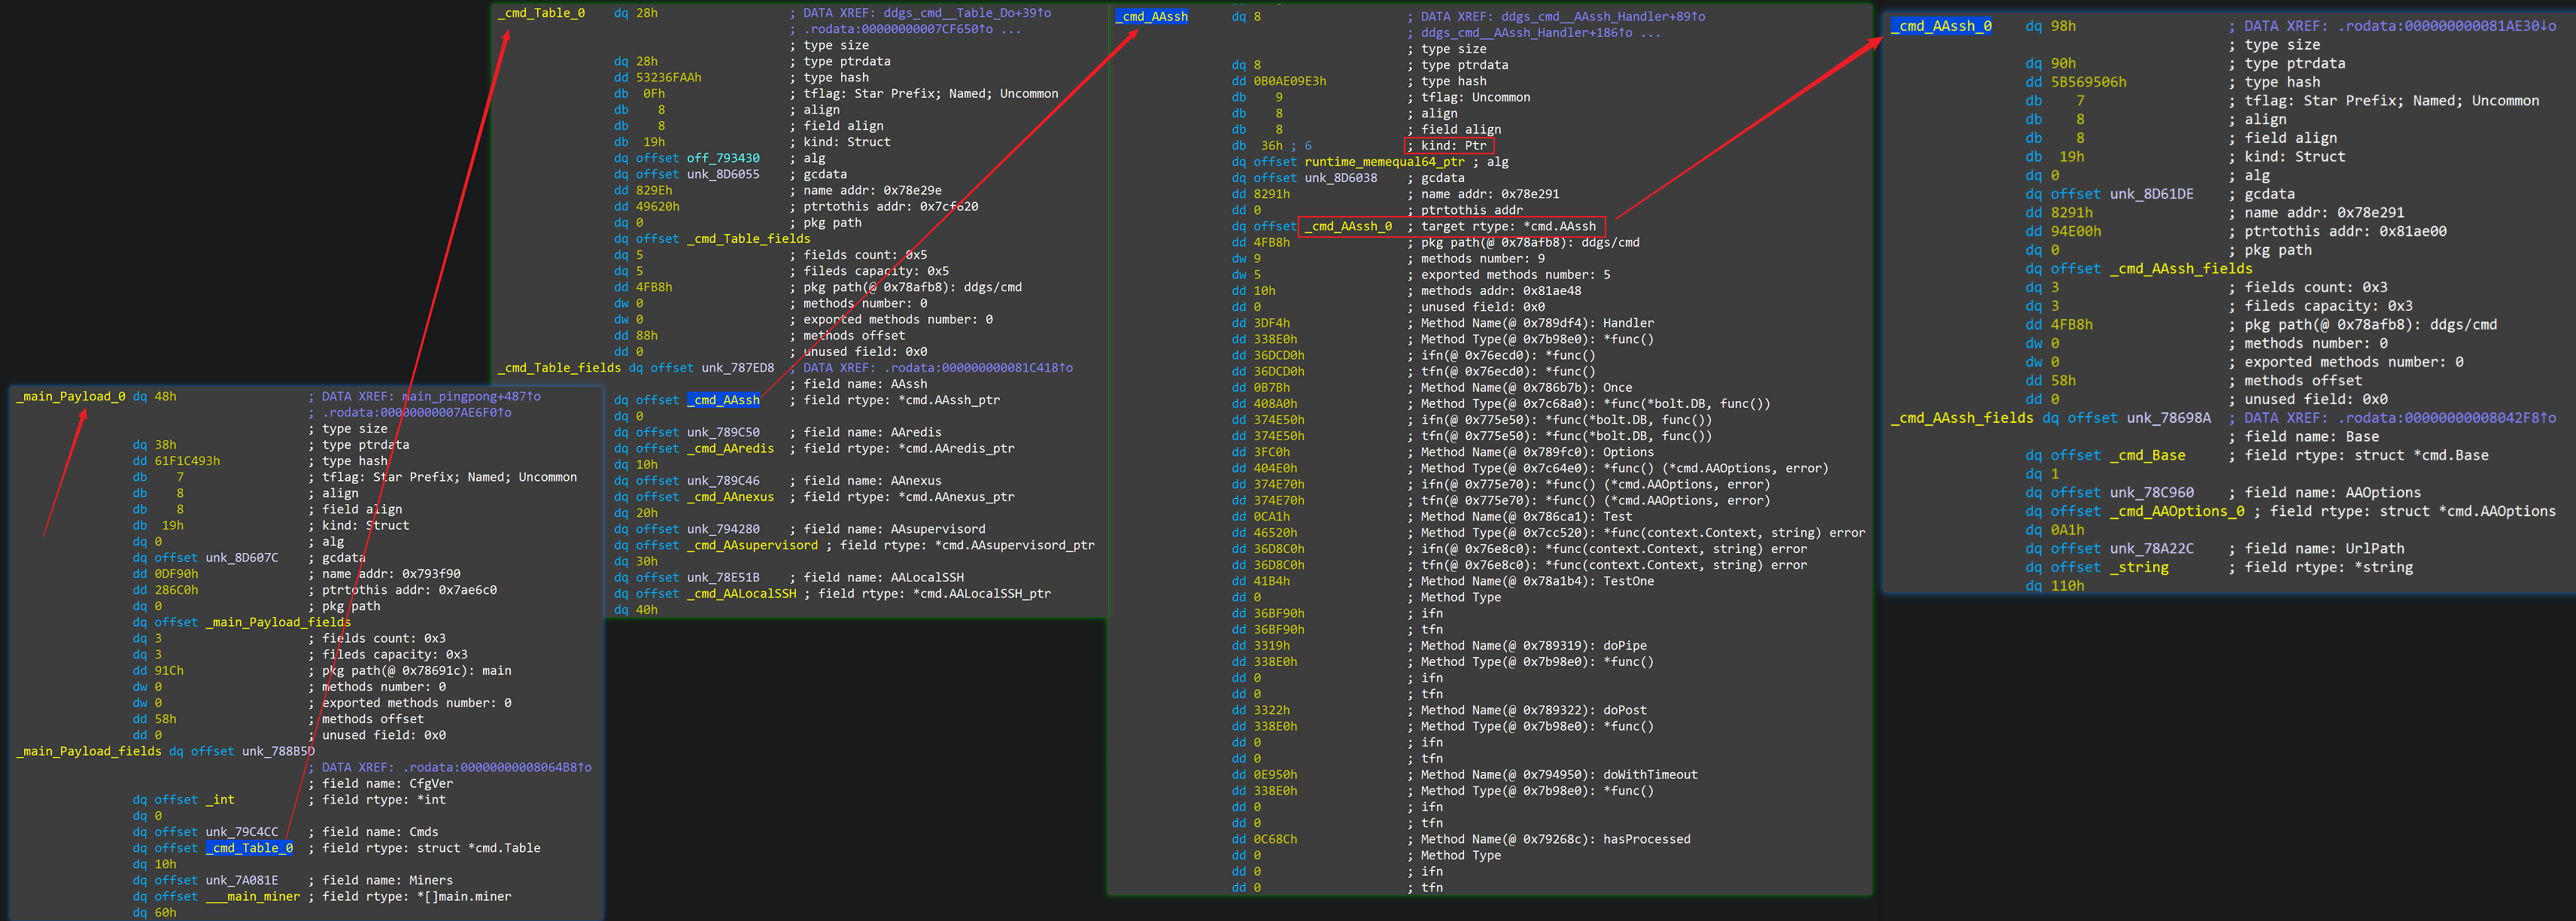 0xjiayu/go_parser
Yet Another Golang binary parser for IDAPro
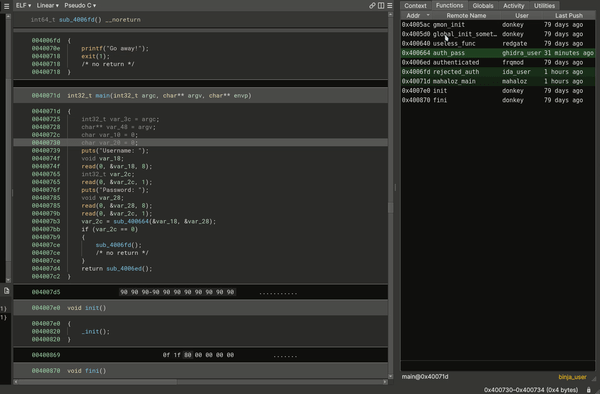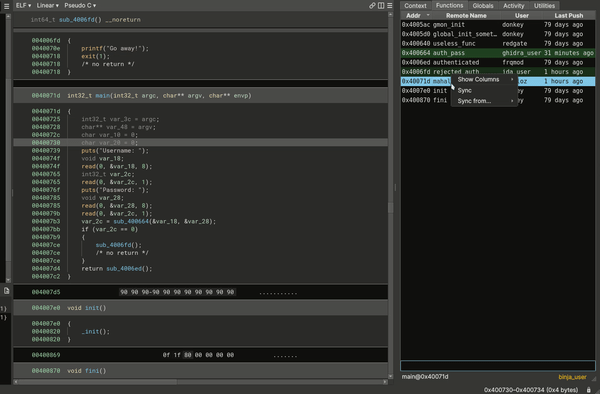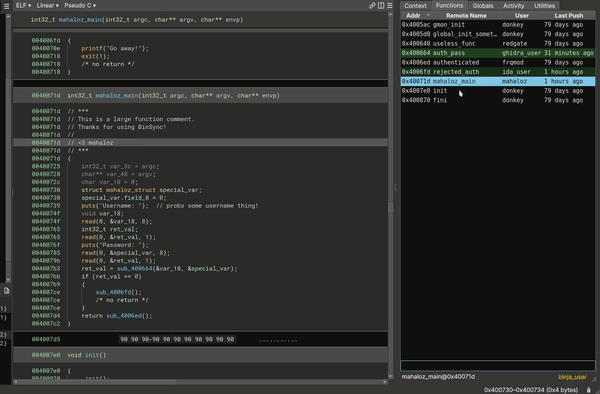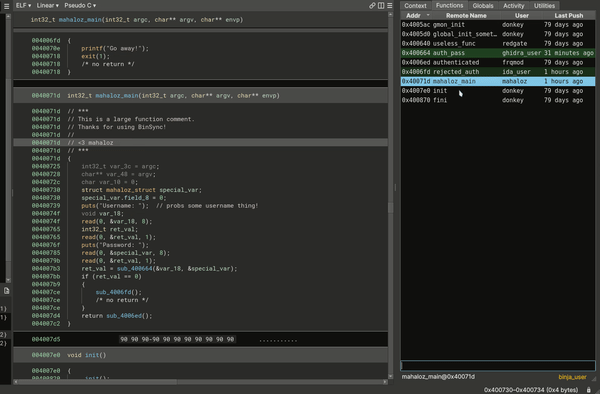 binsync/binsync
A reversing plugin for cross-decompiler collaboration, built on git.
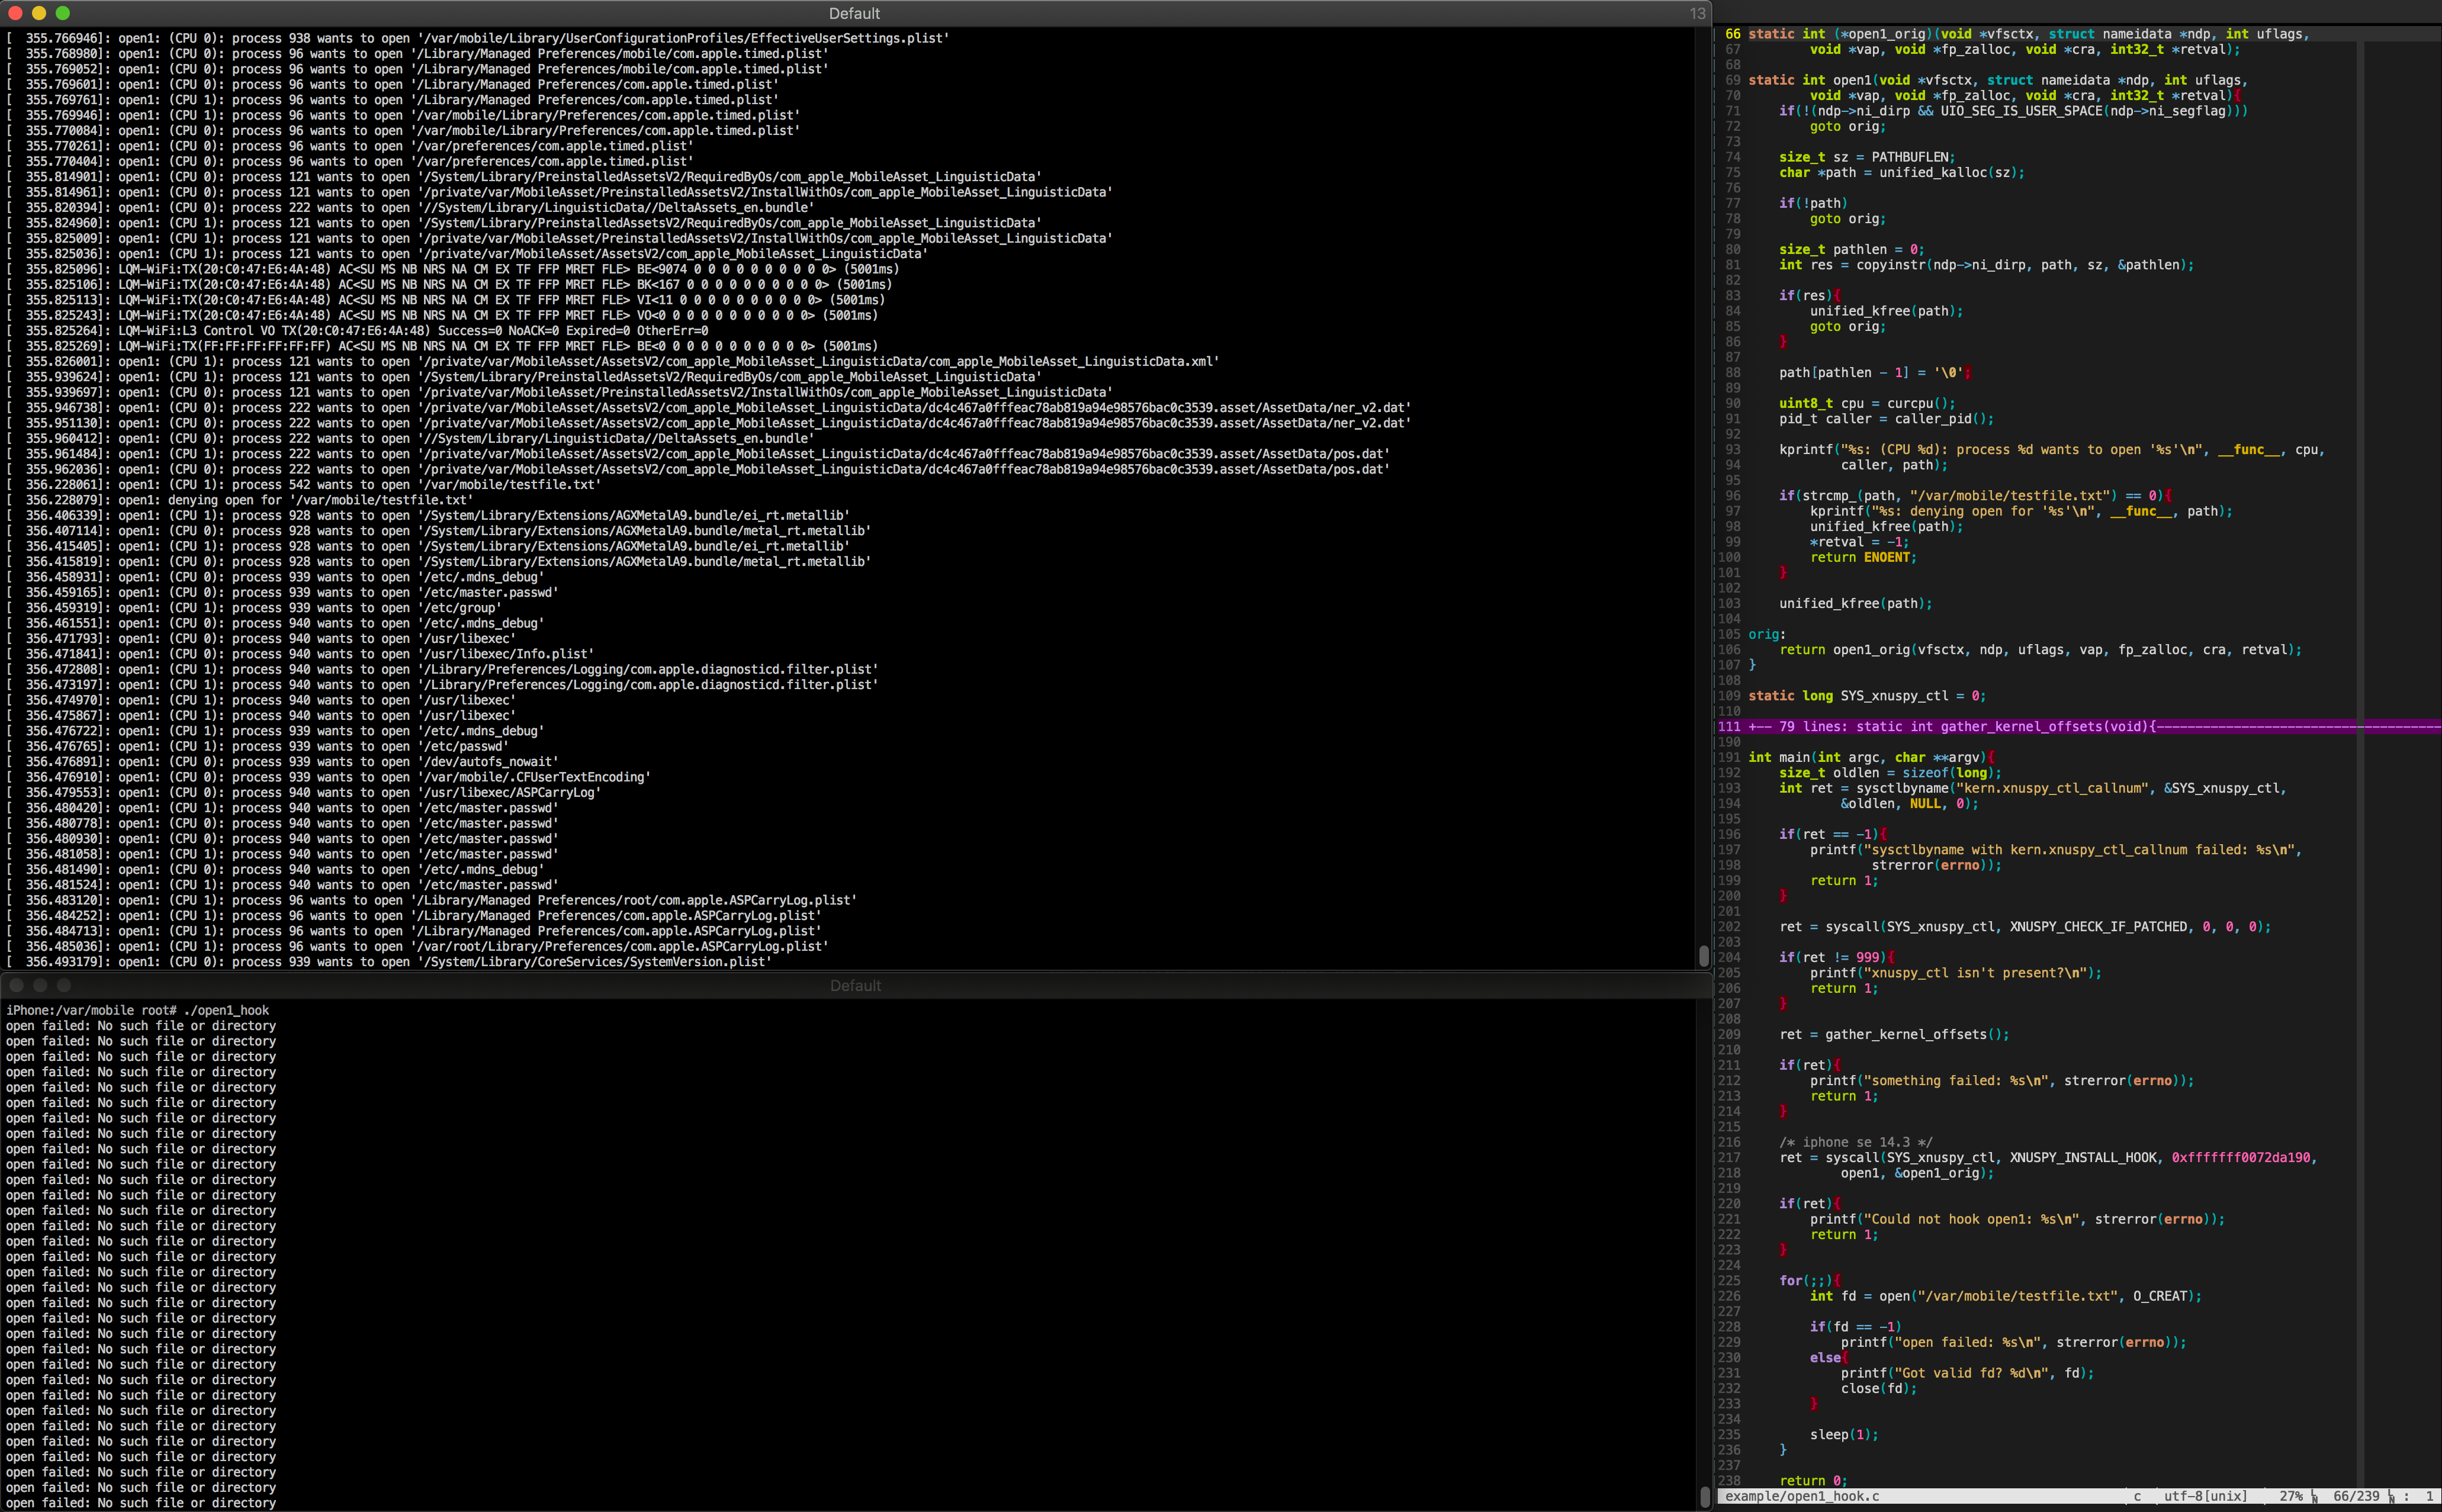 jsherman212/xnuspy
an iOS kernel function hooking framework for checkra1n'able devices
 steven-michaud/hookcase
Tool for reverse engineering macOS/OS X
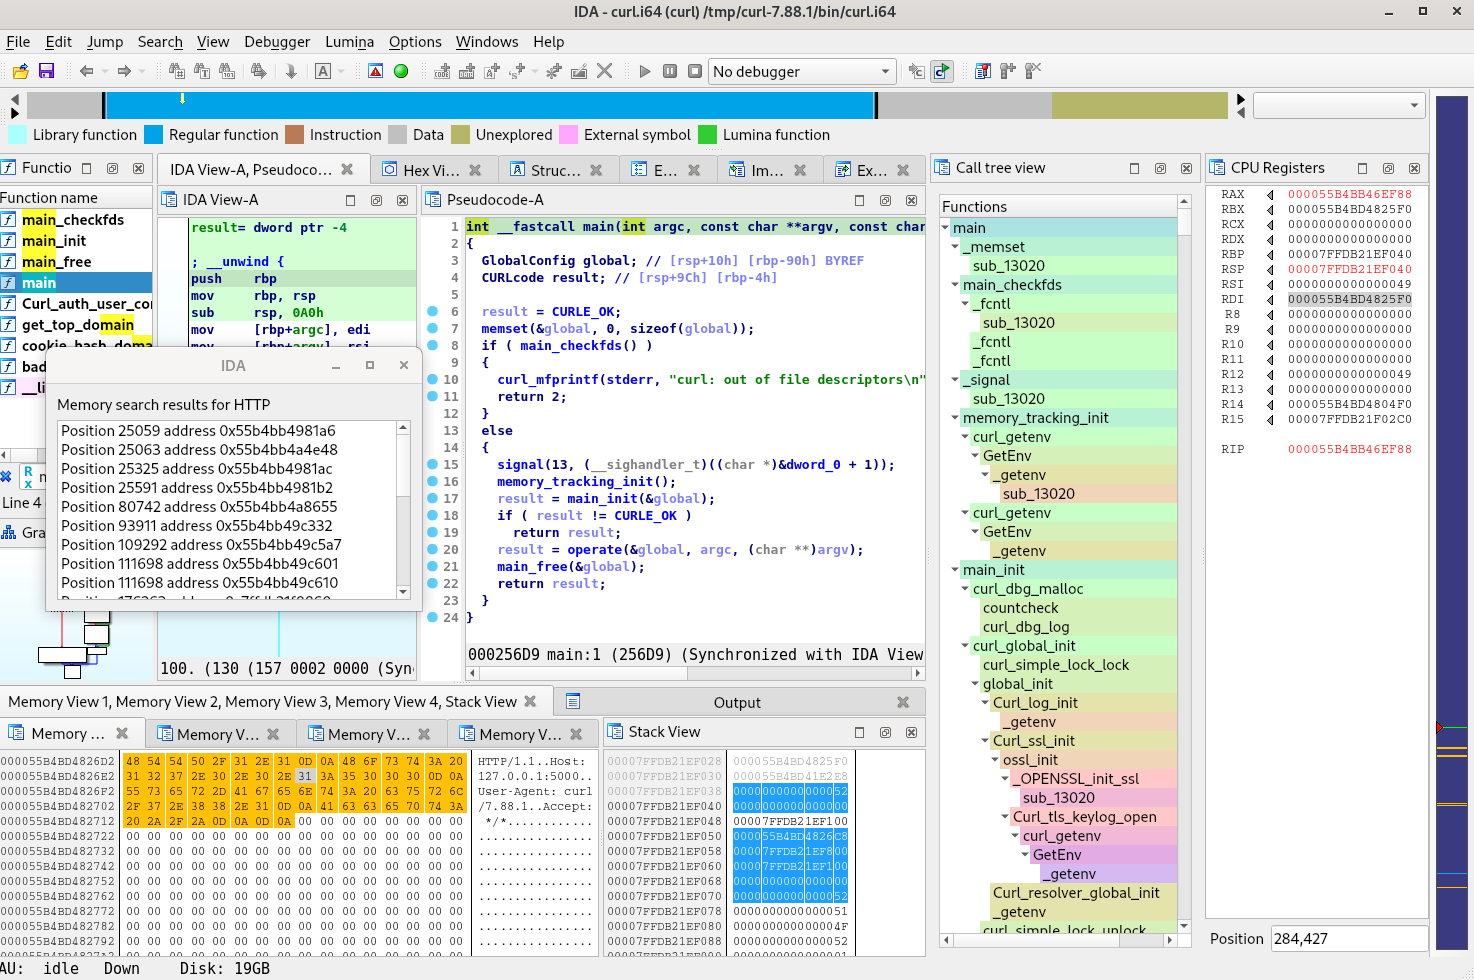 synacktiv/frinet
Frida-based tracer for easier reverse-engineering on Android, iOS, Linux, Windows and most related architectures.
 eset/ipyida
IPython console integration for IDA Pro
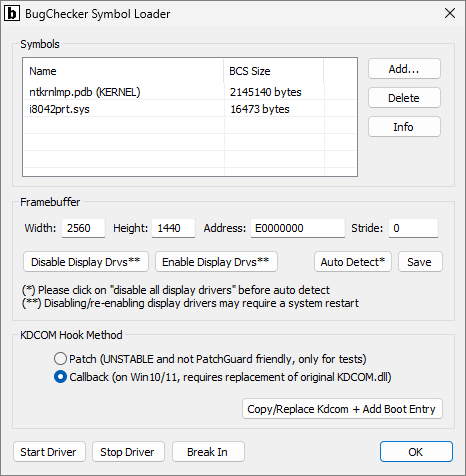 vitoplantamura/bugchecker
SoftICE-like kernel debugger for Windows 11
 netzob/netzob
Open-source toolkit for reverse engineering, modeling, and fuzzing communication protocols. Infers message formats and state machines from network…
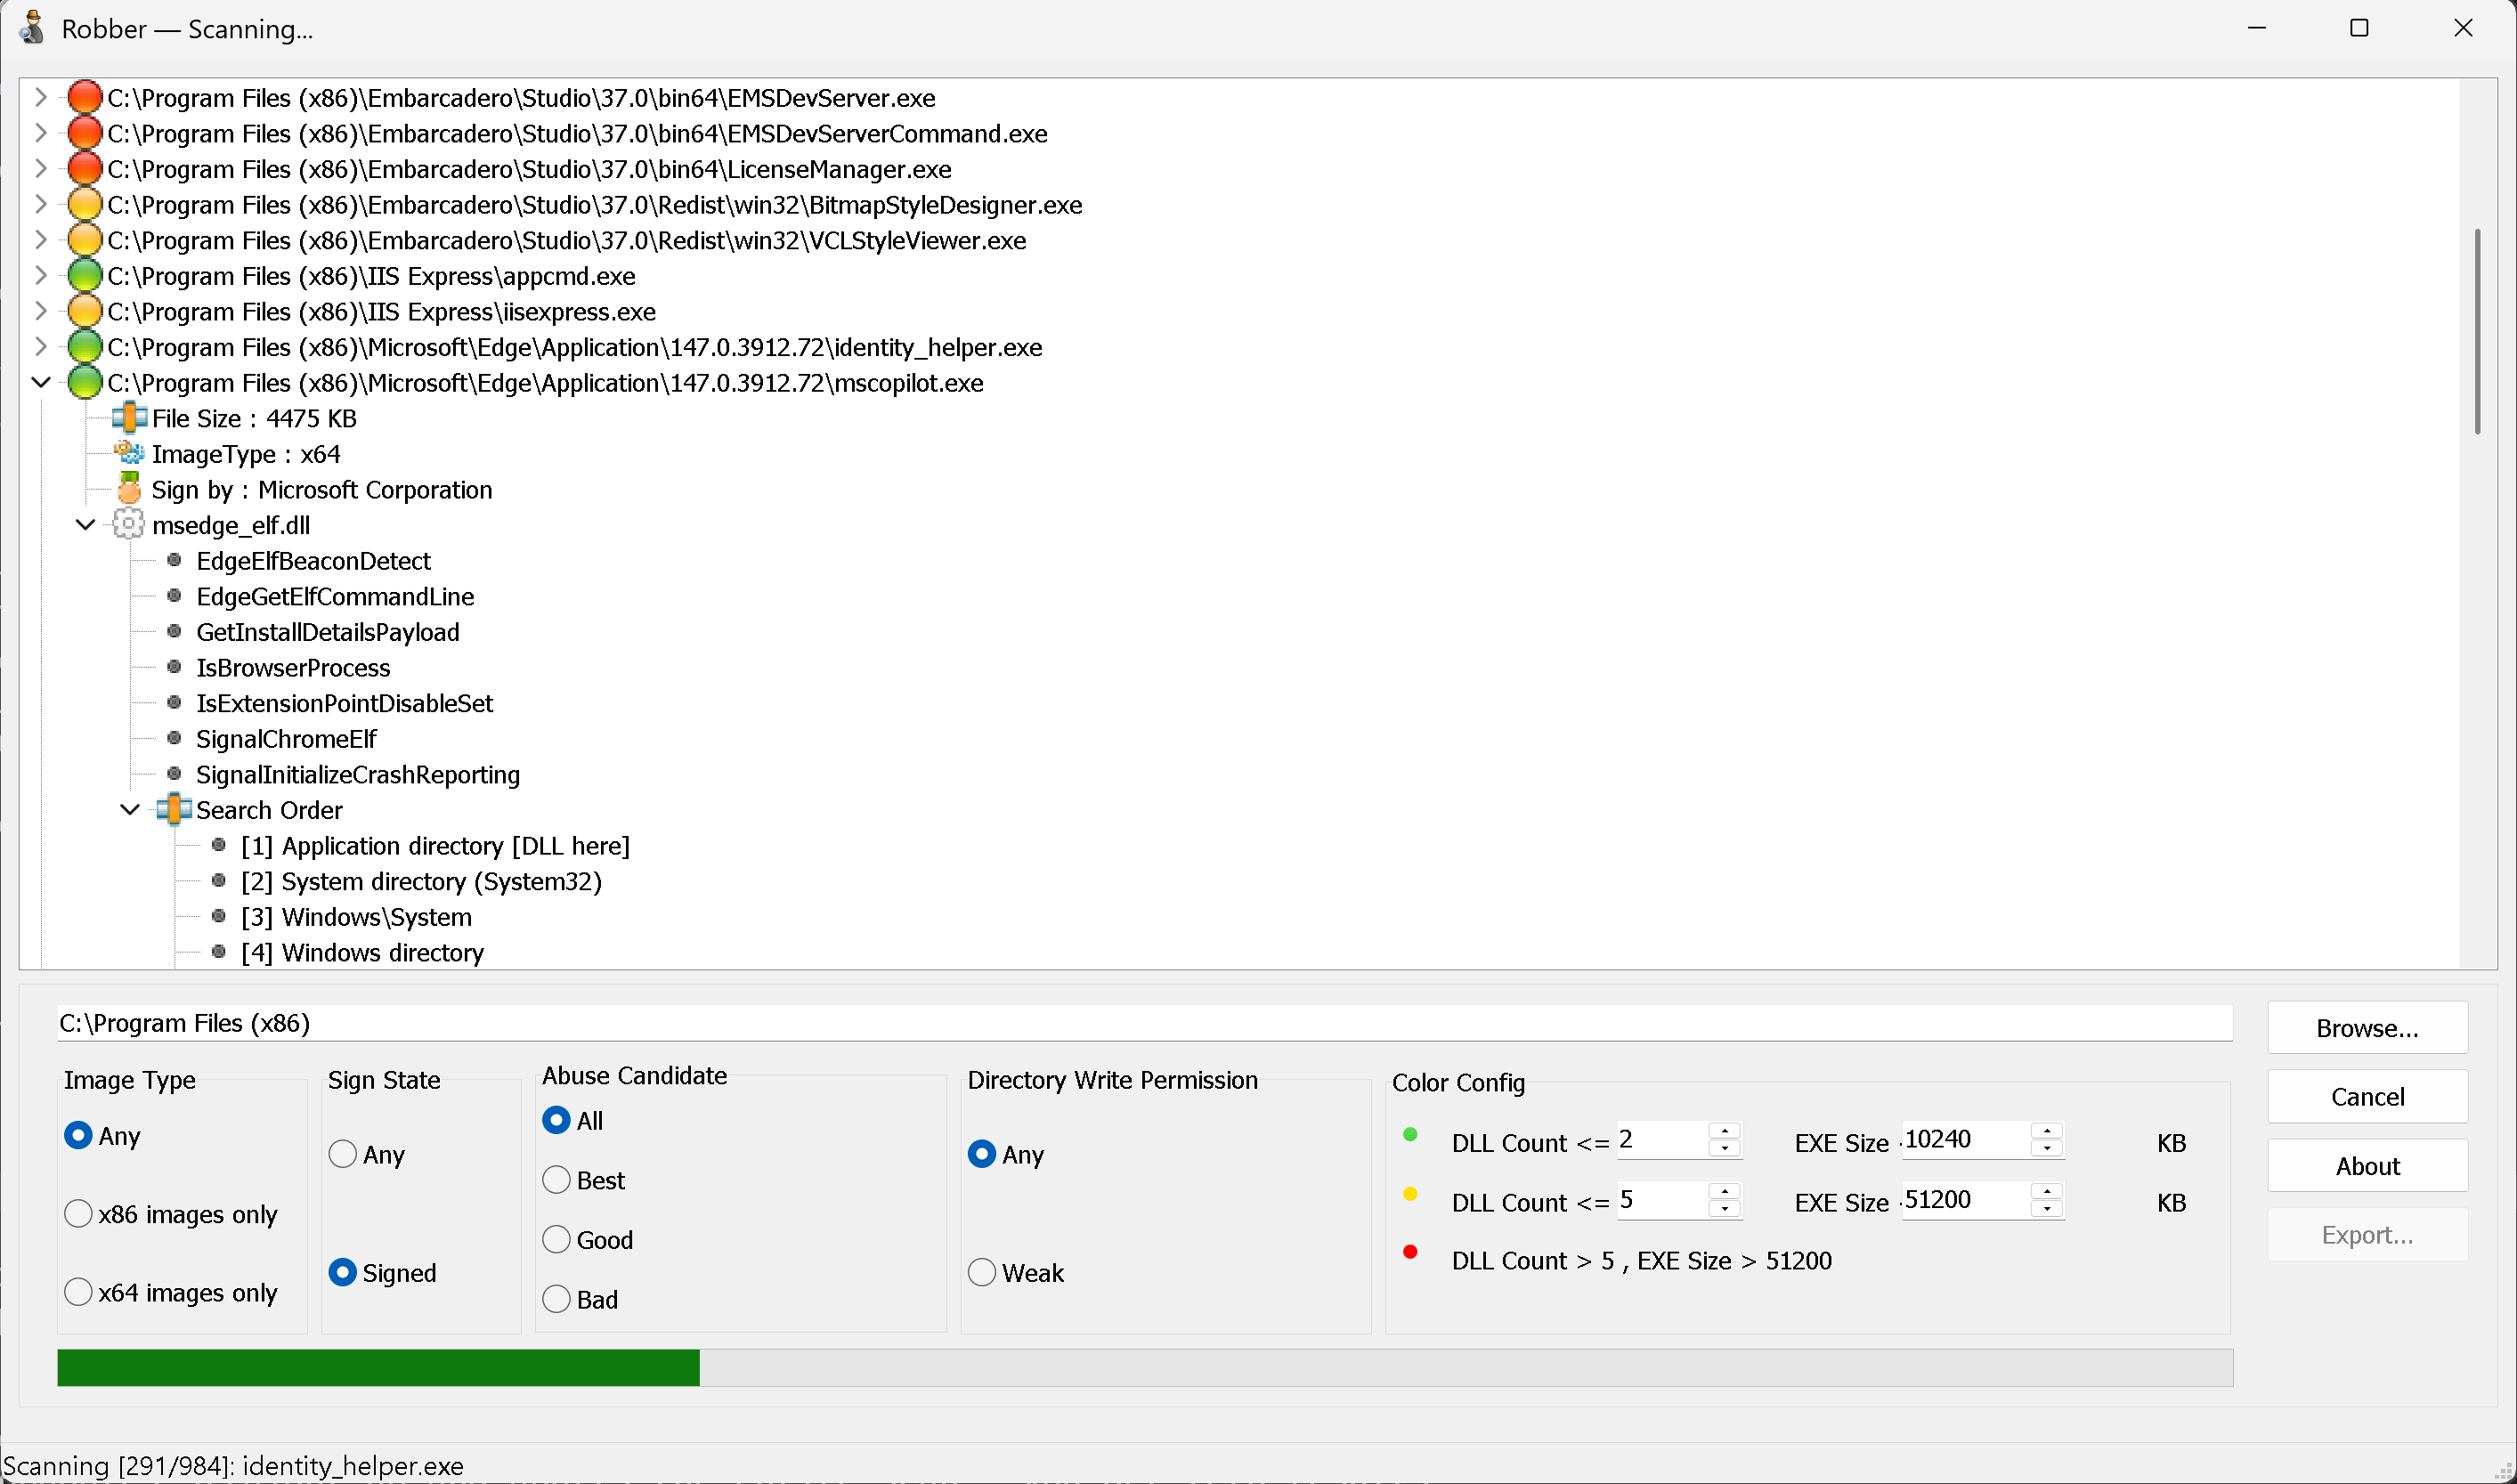 mojtabatajik/robber
Robber is open source tool for finding executables prone to DLL hijacking
 mandiant/flare-emu
Scriptable binary emulation framework integrating IDA Pro/Radare2 with Unicorn engine for automated malware analysis, string decryption, and code…
 radareorg/r2ai
Radare2 AI plugin using local or remote LLMs for decompilation, function explanation, vulnerability detection, renaming, and scripted reverse…
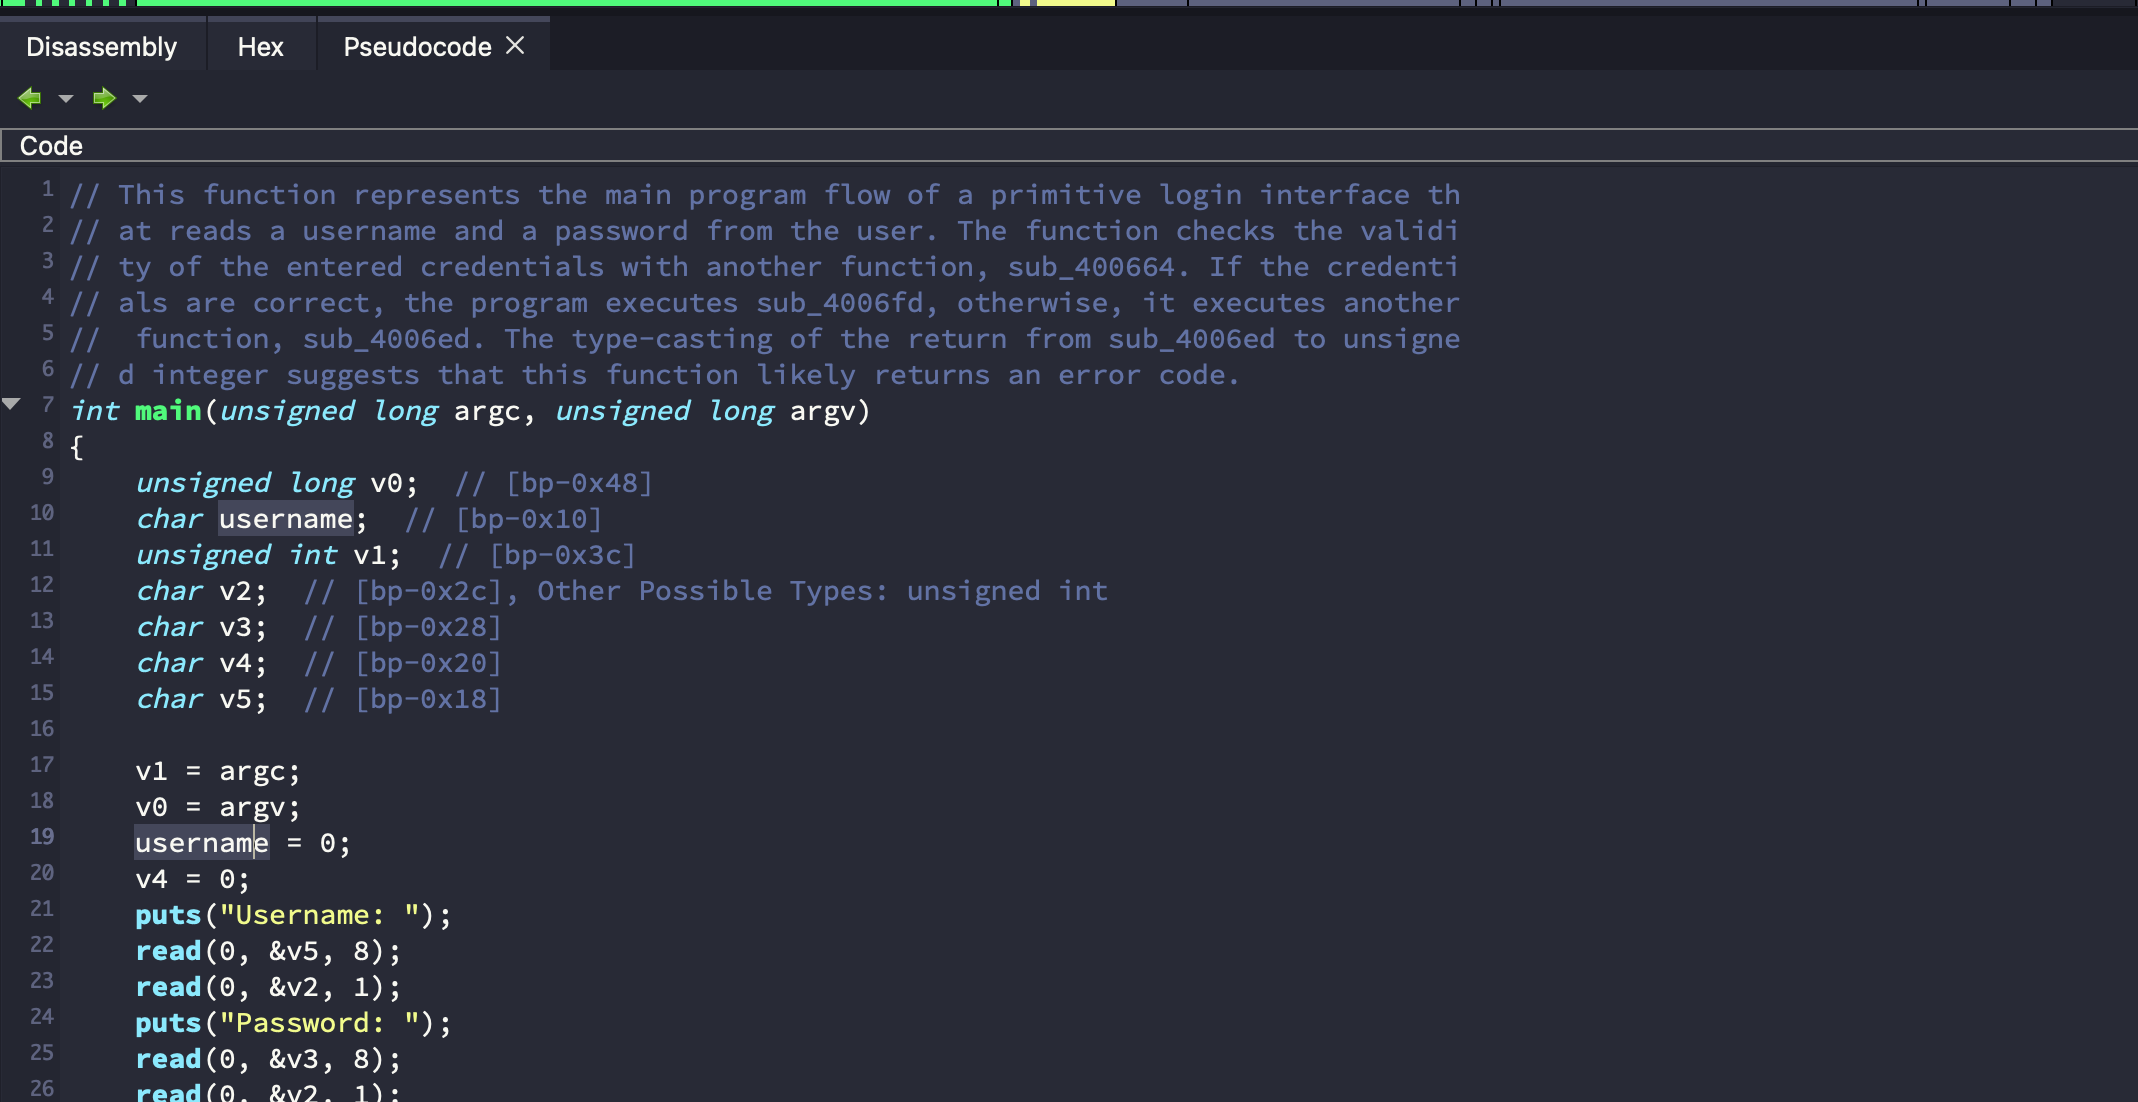 mahaloz/daila
A decompiler-agnostic plugin for interacting with AI in your decompiler. GPT-4, Claude, and local models supported!