Am-I-affected-by-Meltdown

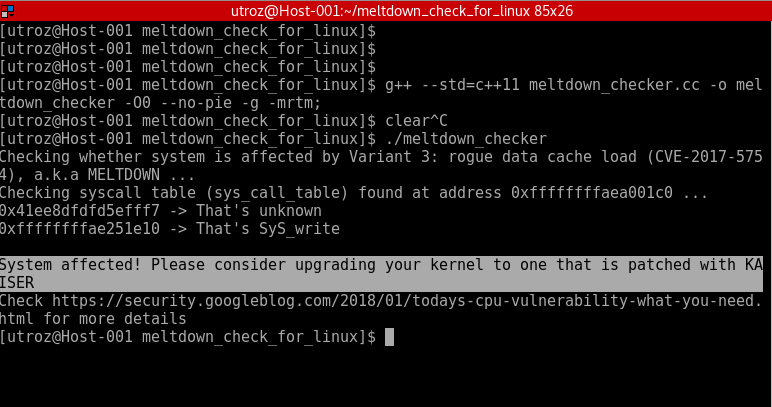
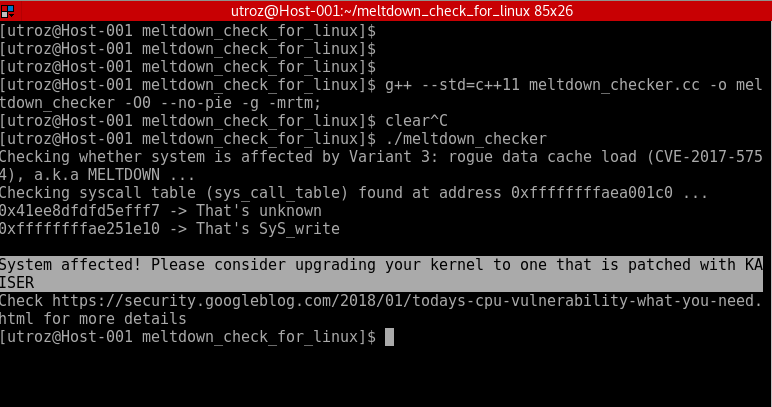
Meltdown Exploit / Proof-of-concept / checks whether system is affected by Variant 3: rogue data cache load (CVE-2017-5754), a.k.a MELTDOWN.

Meltdown Exploit / Proof-of-concept / checks whether system is affected by Variant 3: rogue data cache load (CVE-2017-5754), a.k.a MELTDOWN.

Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…

A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…

Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…

Proof-of-concept / Exploit / checks whether system is affected by Variant 3: rogue data cache load (CVE-2017-5754), a.k.a

Proof-of-concept exploit for CVE-2023-1999 targeting the WebP codec library on Android 10 (r33). Demonstrates a heap buffer overflow vulnerability in…

🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.

EMBA - The firmware security analyzer

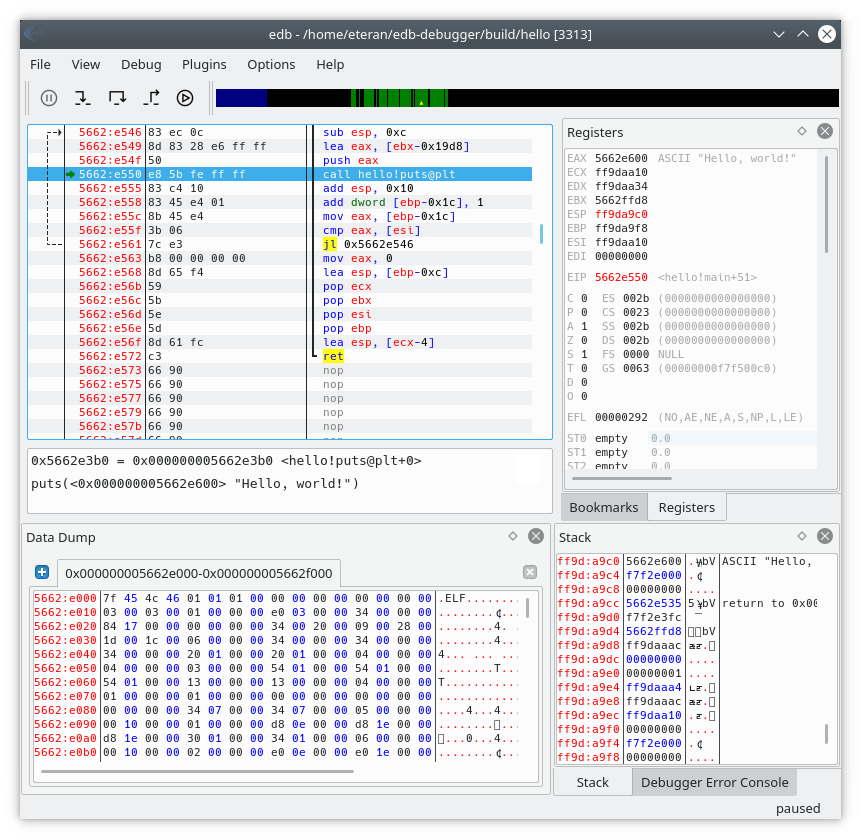
edb is a cross-platform AArch32/x86/x86-64 debugger.

A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)

A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.

Full featured multi arch/os debugger built on top of PyQt5 and frida

IDA 2016 plugin contest winner! Symbolic Execution just one-click away!

IoT firmware identification and extraction

:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes


A comprehensive binary emulation and instrumentation platform.

Public repository of statically compiled GDB and GDBServer