
zelos
 zeropointdynamics/zelos
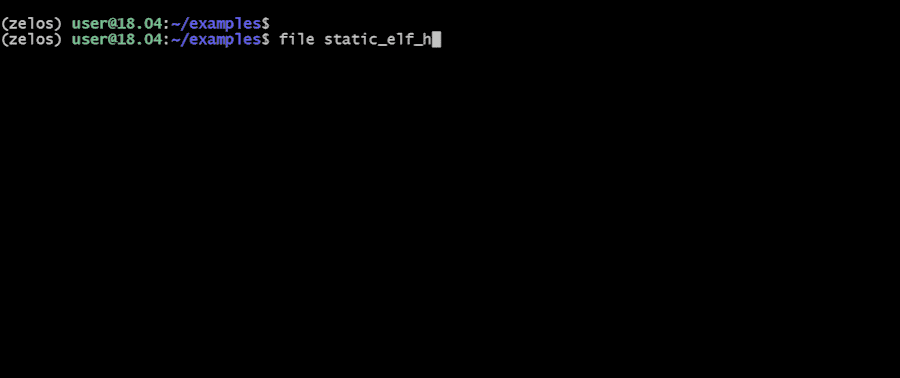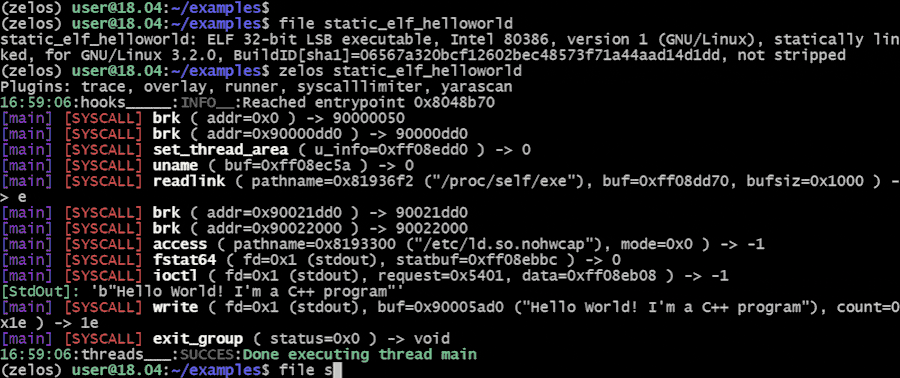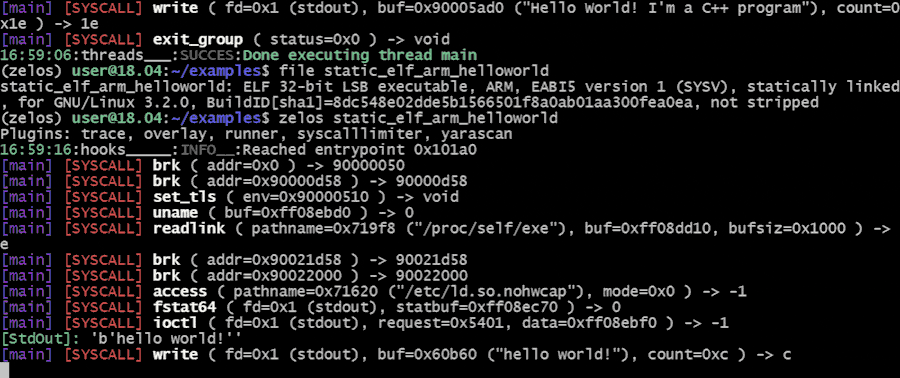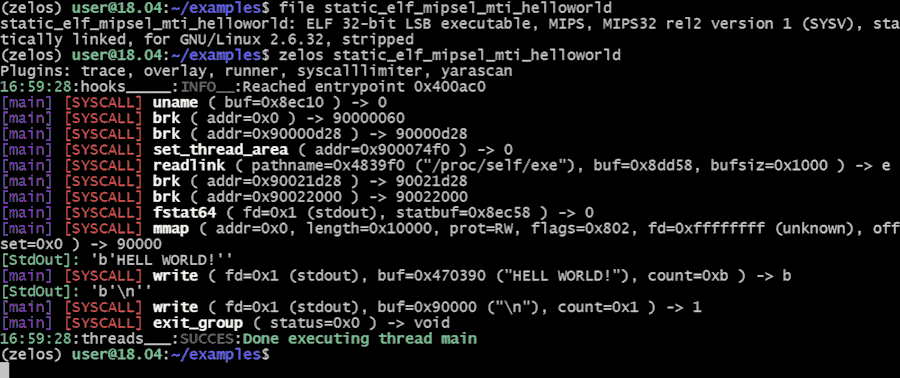
A comprehensive binary emulation and instrumentation platform.
binary-analysisdebuggersdynamic-analysis-sandboxing+3
4203 years ago
zeropointdynamics/zelosA comprehensive binary emulation and instrumentation platform.
 mrexodia/dumpulator
An easy-to-use library for emulating memory dumps. Useful for malware analysis (config extraction, unpacking) and dynamic analysis in general…
 conscioushacker/wfh
Frida-based dynamic analysis tool that automatically identifies DLL sideloading and COM hijacking vulnerabilities in Windows executables through…
 4w4k3/repy2exe
A Reverse Engineering Tool for py2exe applications.
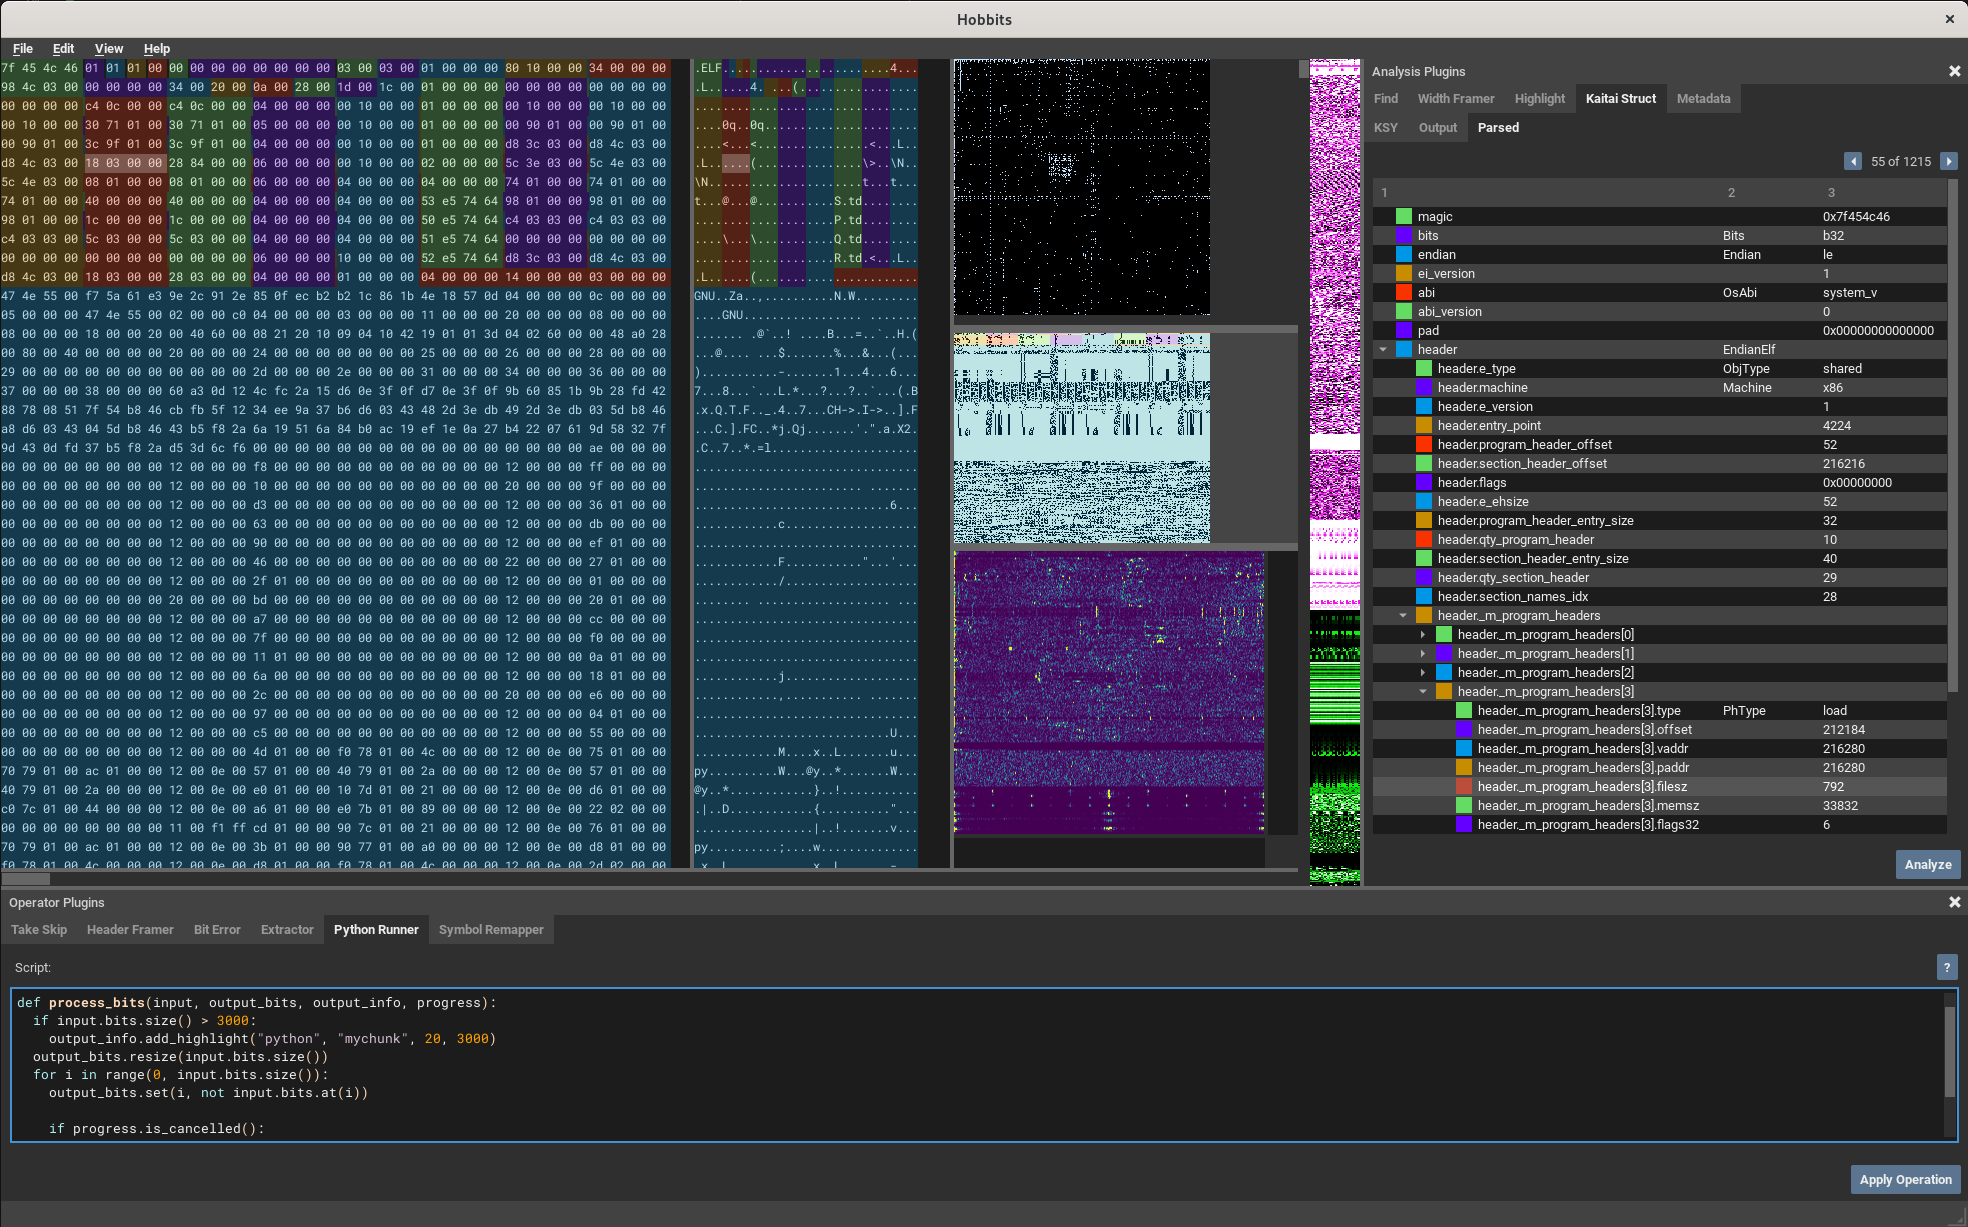 mahlet-inc/hobbits
A multi-platform GUI for bit-based analysis, processing, and visualization
 skylined/bugid
Detect, analyze and uniquely identify crashes in Windows applications
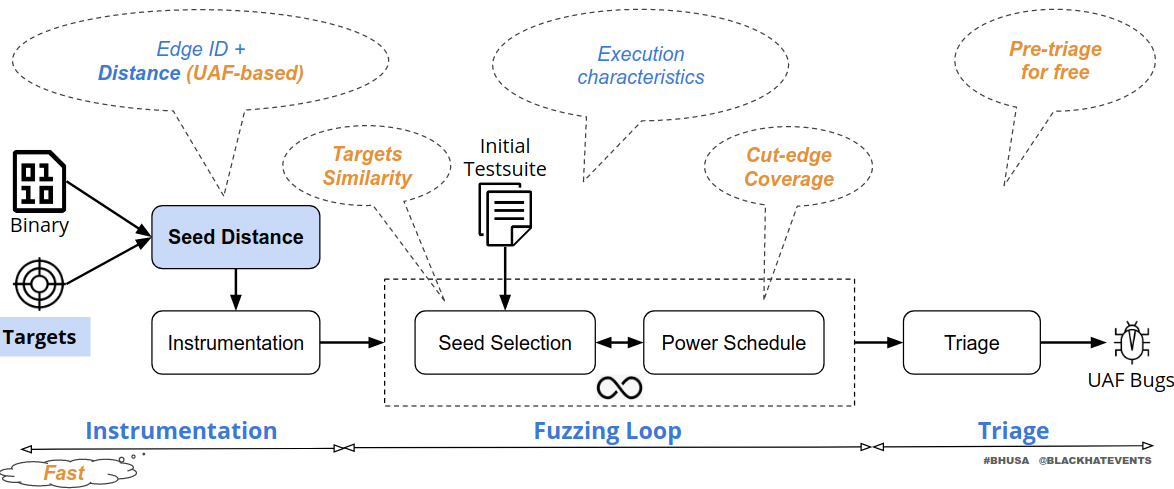 strongcourage/uafuzz
Binary-level directed fuzzer specialized in detecting Use-After-Free vulnerabilities via ordering-aware input metrics and static analysis, enabling…
 nccgroup/susanrtti
Another RTTI Parsing IDA plugin
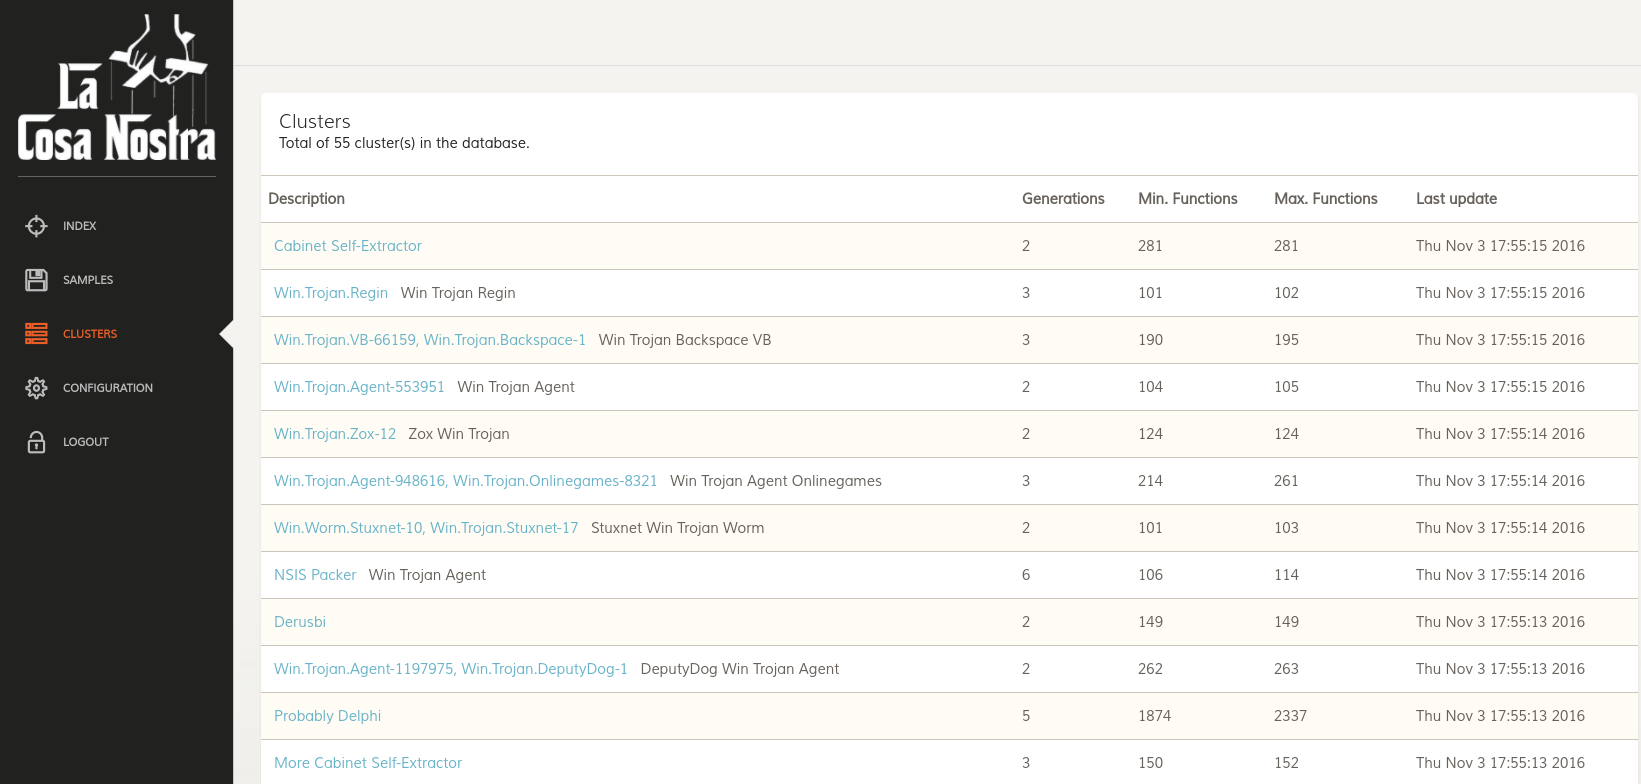 joxeankoret/cosa-nostra
Cosa Nostra, a FOSS graph based malware clusterization toolkit.
 mandiant/dncil
The FLARE team's open-source library to disassemble Common Intermediate Language (CIL) instructions.
 idamcp/idamcp
MCP server integrating IDA Pro with AI agents, featuring a stateless gateway for multi-session management, a relational SQL query engine for binary…
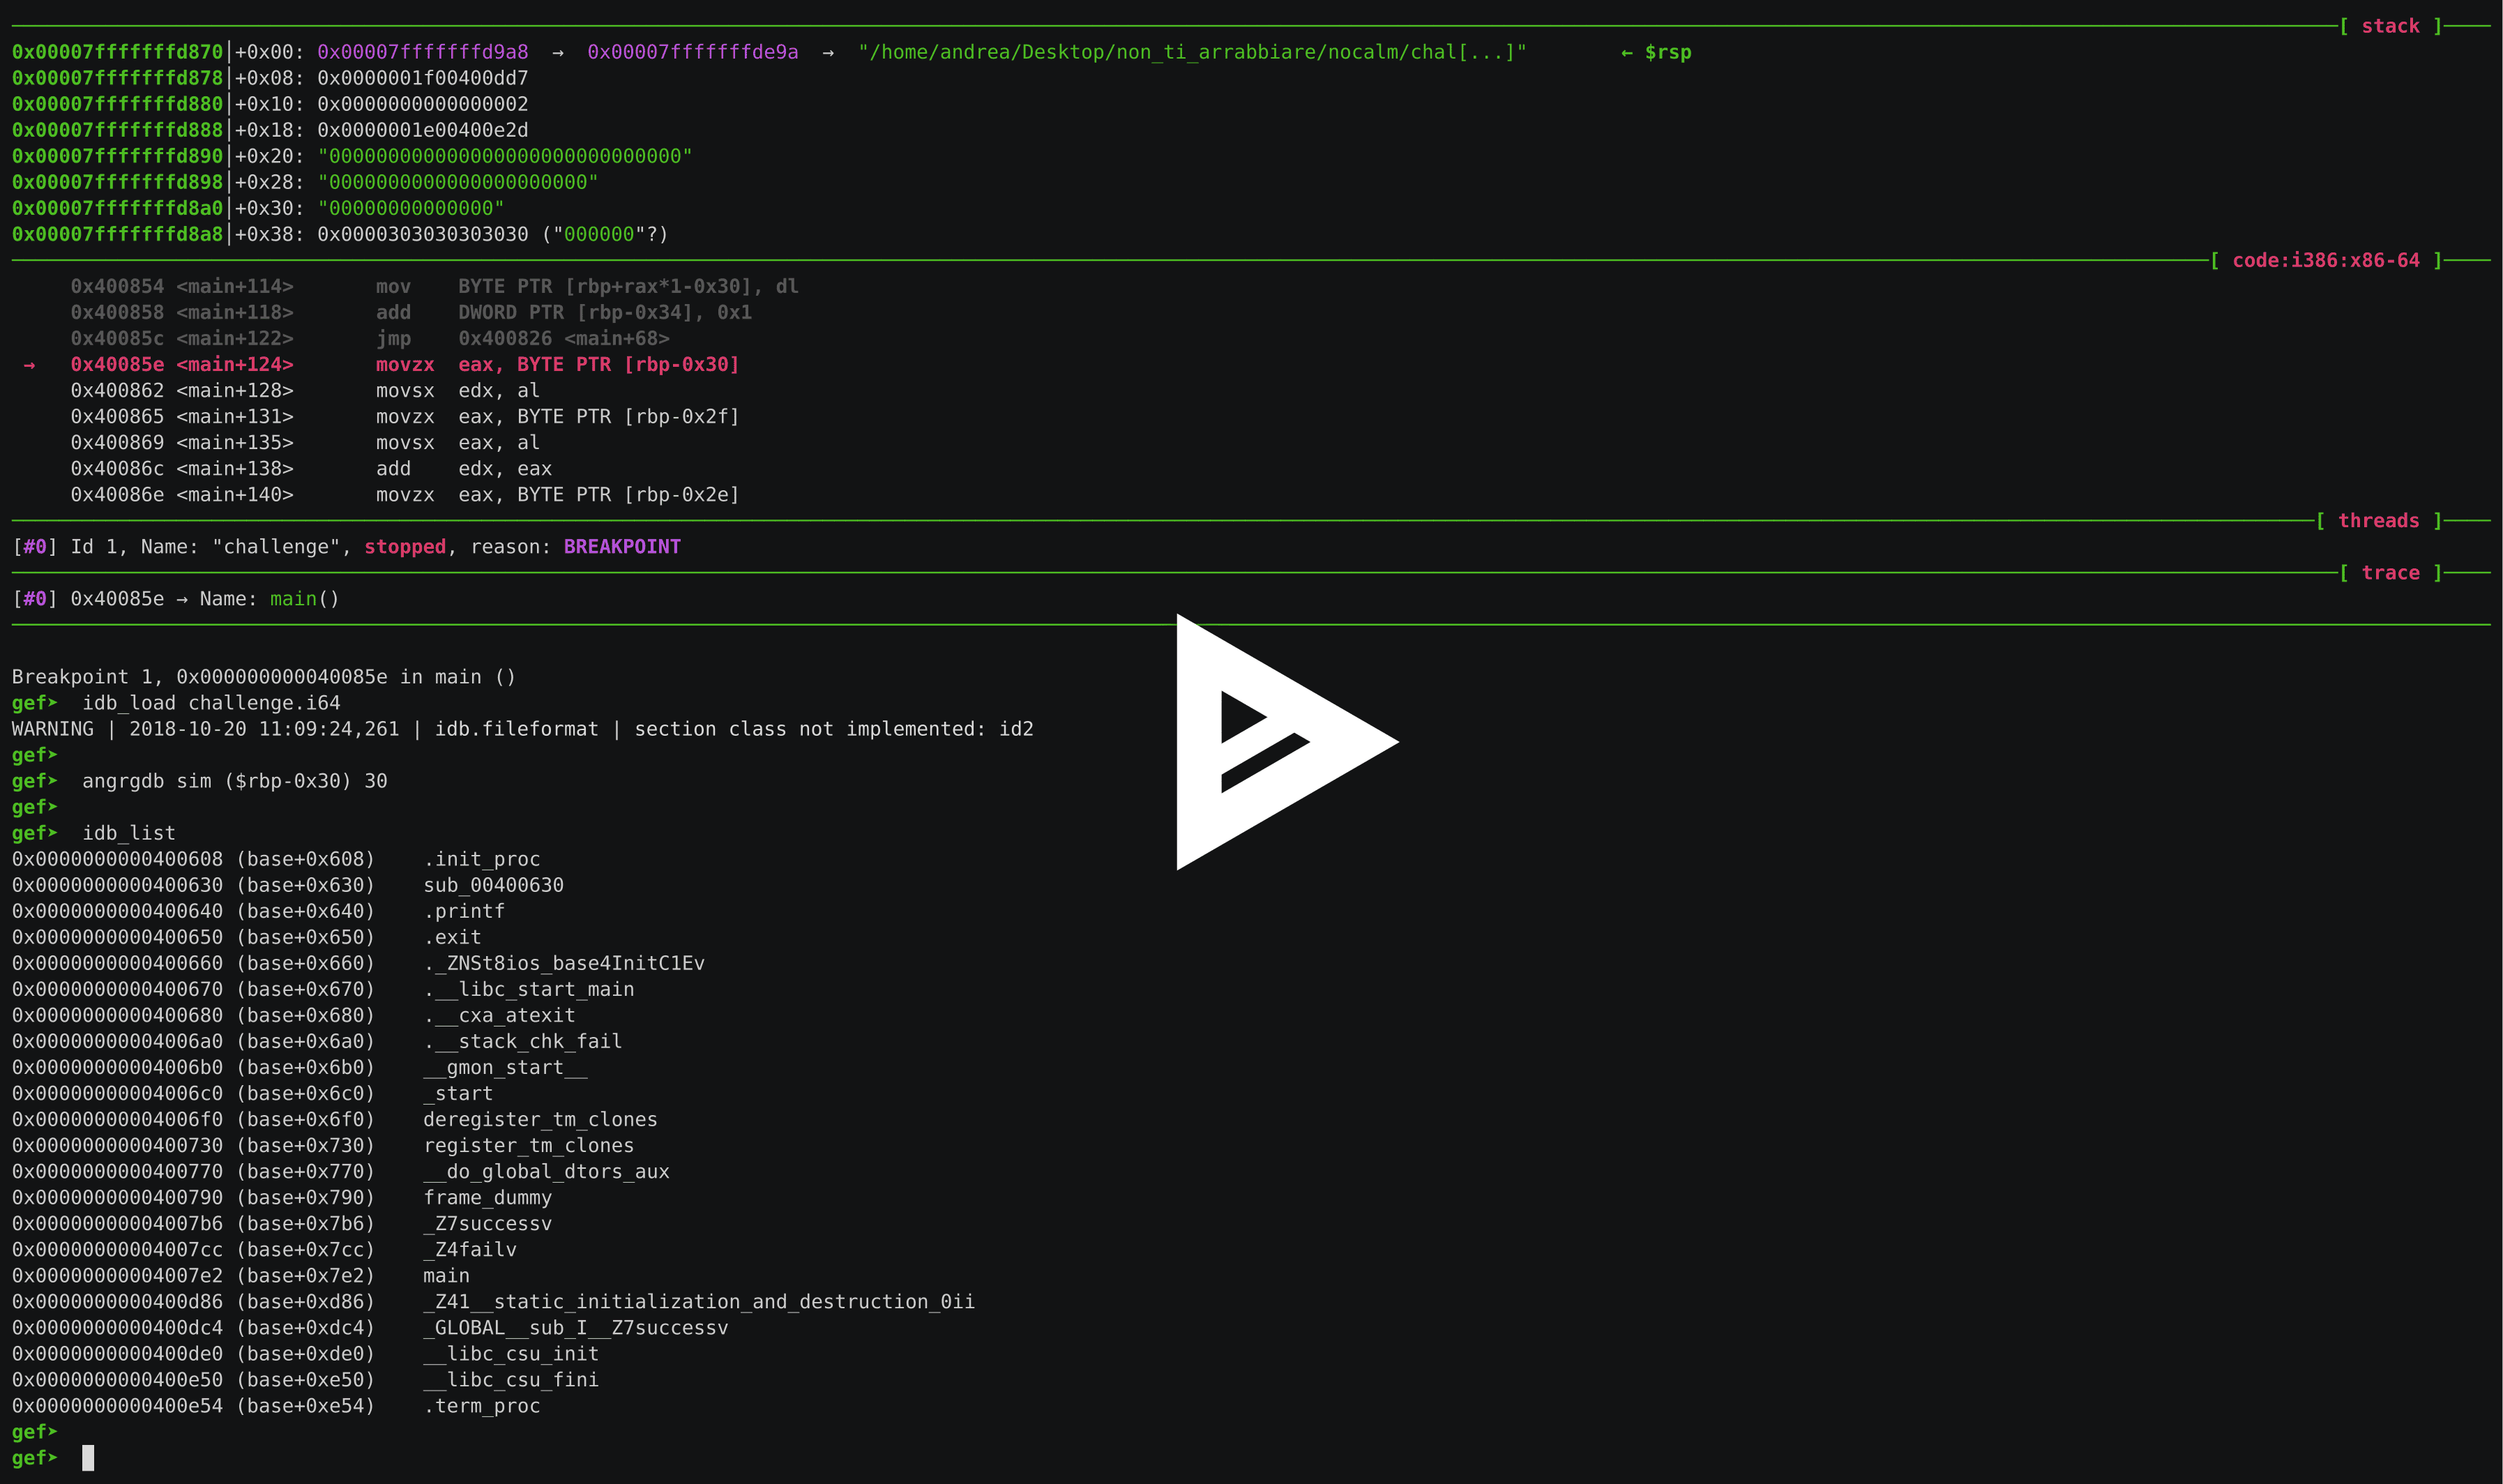 andreafioraldi/angrgdb
Use angr inside GDB. Create an angr state from the current debugger state.
 nazywam/autoit-ripper
Extract AutoIt scripts embedded in PE binaries
 denuvosoftwaresolutions/simba
Efficient Deobfuscation of Linear Mixed Boolean-Arithmetic Expressions
 timetravelthree/idarustdemangler
Rust Demangler & Normalizer plugin for IDA
 nirizr/rematch
REmatch, a complete binary diffing framework that is free and strives to be open source and community driven.
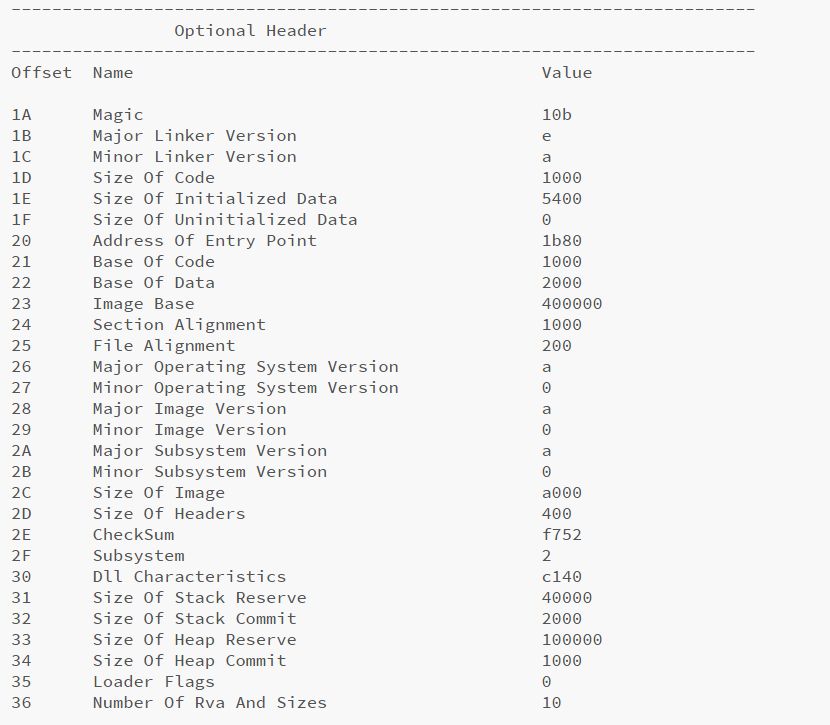 blacknbunny/peanalyzer
Advanced Portable Executable File Analyzer And Disassembler 32 & 64 Bit
