
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
159 results
yarasafe preview

yarasafe

GitHublucamassarelli/yarasafe

SAFE embeddings to match functions in yara
binary-analysismachine-learningmalware-analysis+2
1006 years ago
peanalyzer preview

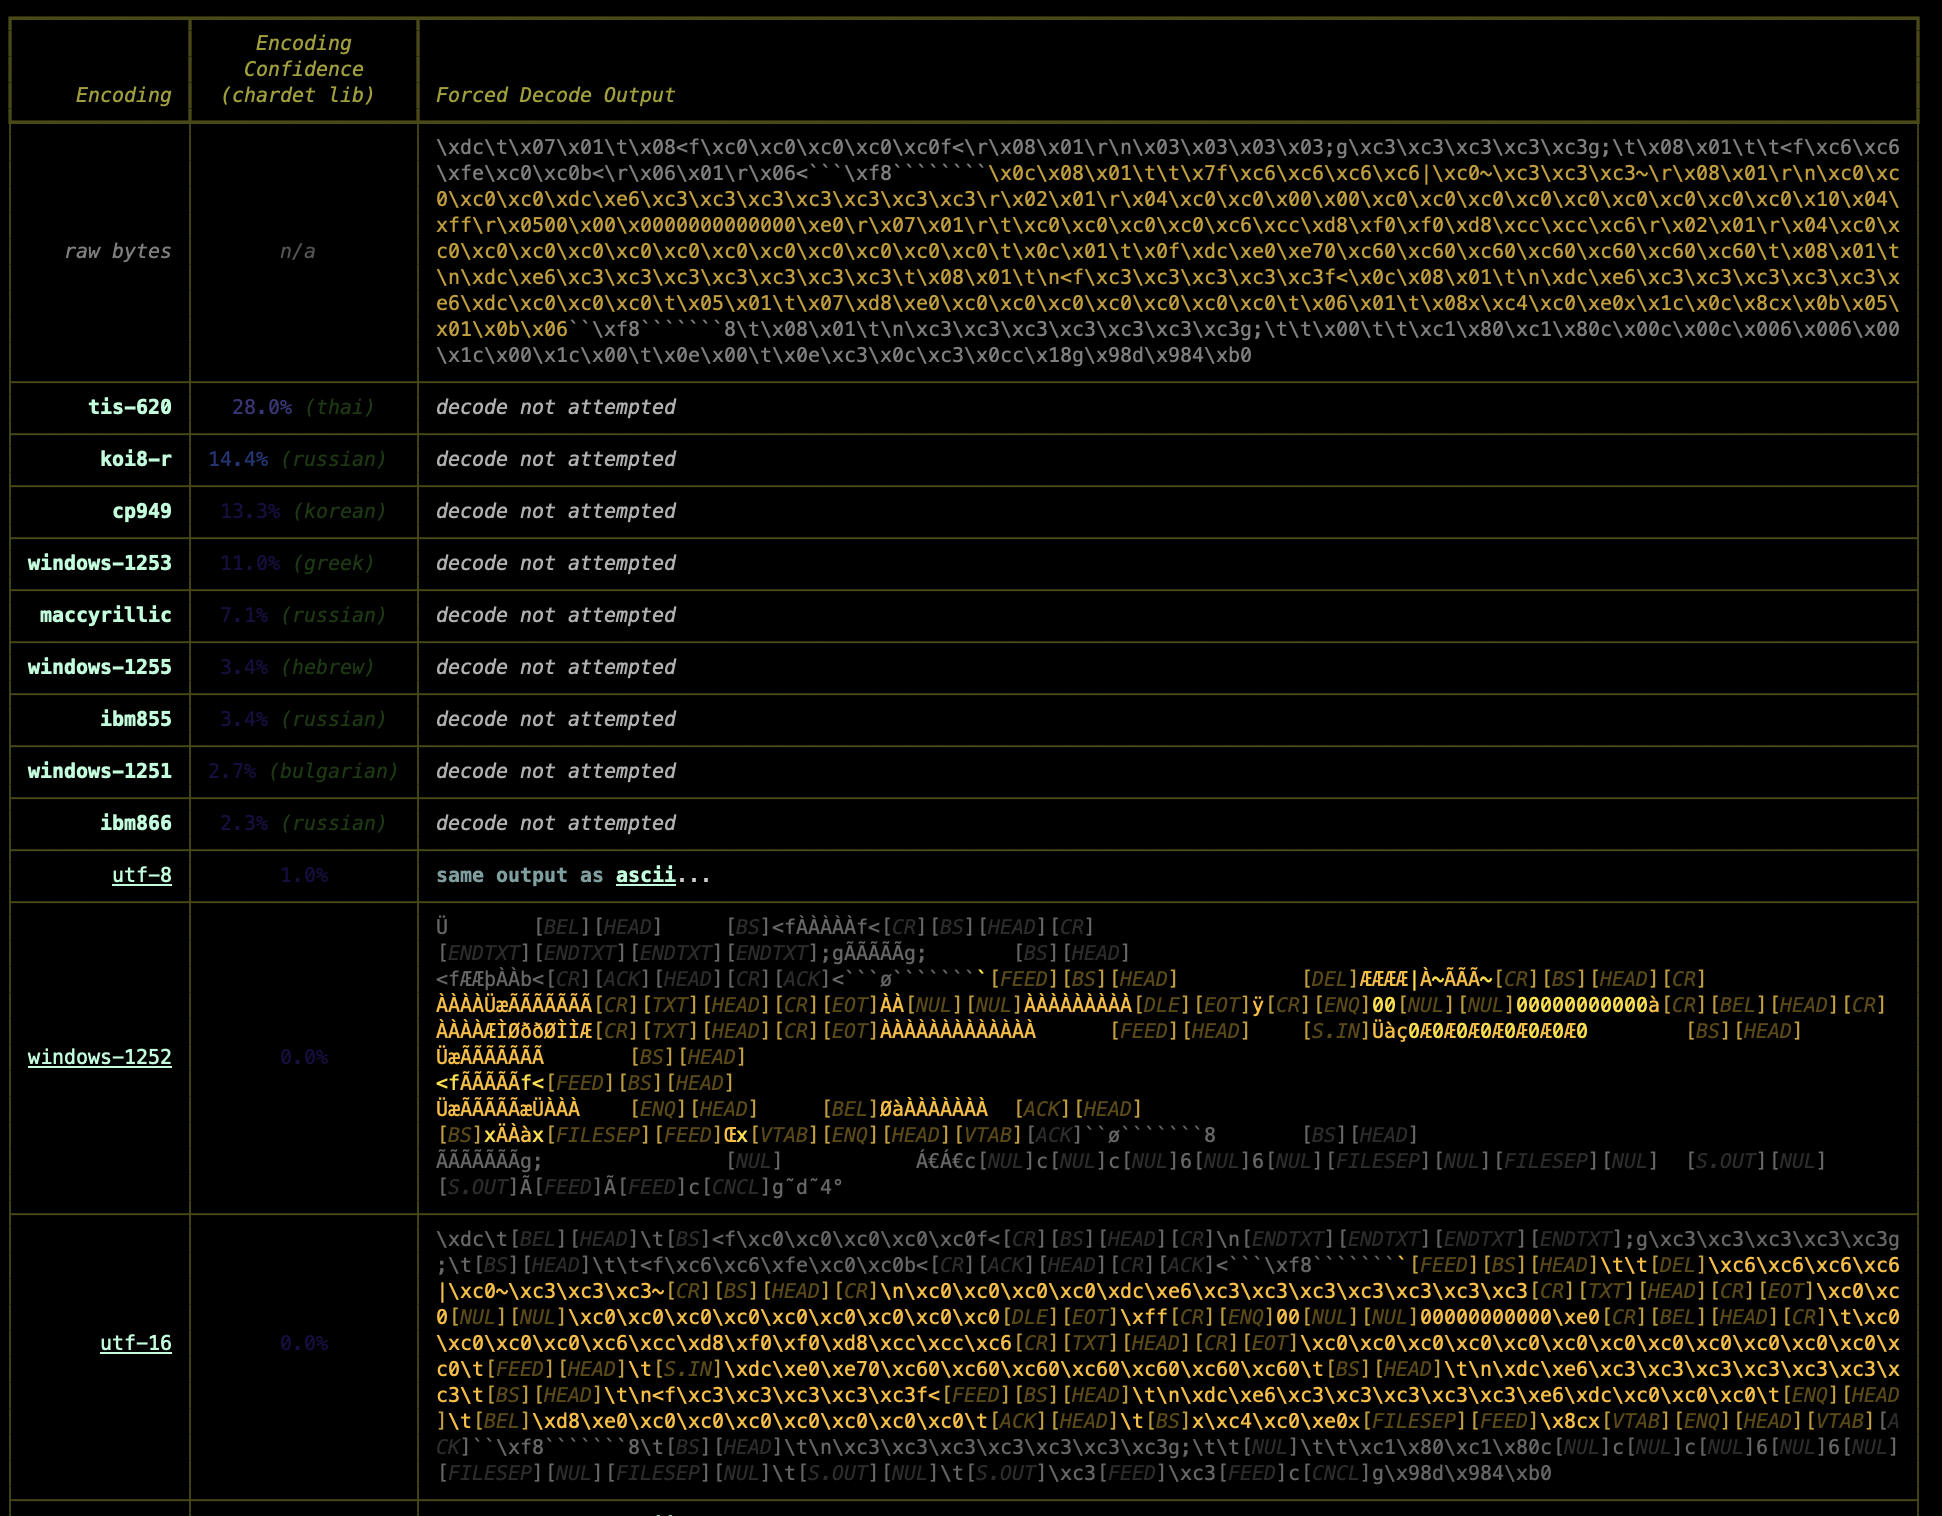
peanalyzer

GitHubblacknbunny/peanalyzer

Advanced Portable Executable File Analyzer And Disassembler 32 & 64 Bit
binary-analysismalware-analysisreverse-engineering+1
1007 years ago
yaralyzer preview

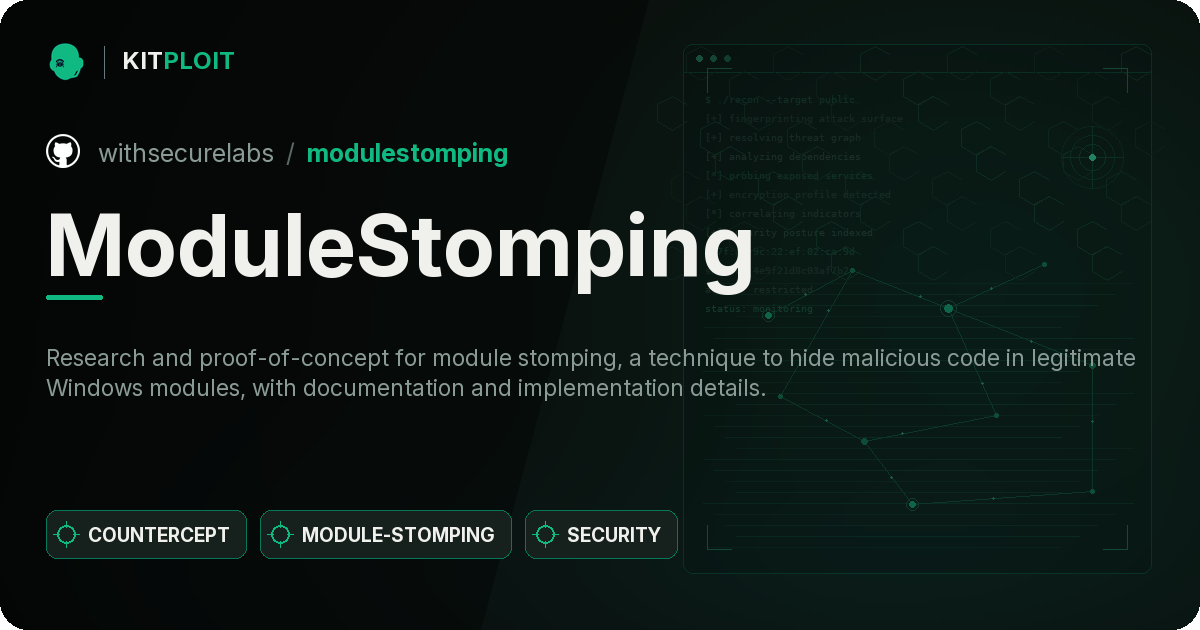
yaralyzer

GitHubmichelcrypt4d4mus/yaralyzer

Visually inspect and force decode YARA and regex matches found in both binary and text data with colors. Lots of colors.
binary-analysisforensicsmalware-analysis+1
1538 months ago
ModuleStomping preview

ModuleStomping

GitHubwithsecurelabs/modulestomping

Research and proof-of-concept for module stomping, a technique to hide malicious code in legitimate Windows modules, with documentation and…
binary-analysismalware-analysisred-teaming
1247 years ago
Rusty-Playground preview

Rusty-Playground

GitHubblacksnufkin/rusty-playground

Some Rust program I wrote while learning Malware Development
binary-analysisexploitationmalware-analysis+6
1631 year ago
upx-recovery-tool preview

upx-recovery-tool

GitHubnozominetworks/upx-recovery-tool

Automates repair of malformed UPX headers in ELF binaries, restoring magic, filesize, blocksize, and overlay fields so standard unpackers can process…
binary-analysismalware-analysisreverse-engineering
1183 years ago
HallWatch preview

HallWatch

GitHubzypherion-technologies/hallwatch

Usermode detector that catches indirect syscalls. Traps Hell's Hall, Tartarus' Gate, RecycledGate, and VEH syscalls & Many more.
binary-analysisdefensive-toolsincident-response+2
914 months ago
mwcfg preview

mwcfg

GitHubc3rb3ru5d3d53c/mwcfg

A Feature Rich Modular Malware Configuration Extraction Utility for MalDuck
binary-analysisdefensive-toolsmalware-analysis+3
1332 years ago
NoMoreXOR preview

NoMoreXOR

GitHubhiddenillusion/nomorexor

Tool to help guess a files 256 byte XOR key by using frequency analysis
binary-analysiscryptographyforensics+3
908 years ago
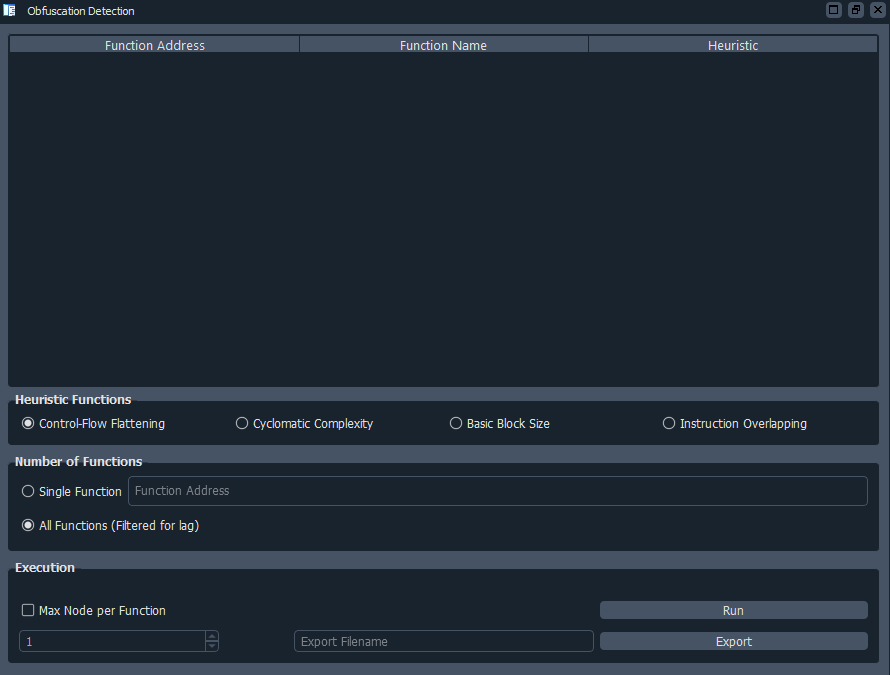
obfDetect preview

obfDetect

GitHubmcdulltii/obfdetect

IDA plugin for automated detection of obfuscated code and control-flow flattening in binaries using heuristic analysis and dominator tree…
binary-analysismalware-analysisreverse-engineering+1
1454 years ago
pecli preview

pecli

GitHubte-k/pecli

CLI tool to analyze PE files

binary-analysismalware-analysisreverse-engineering+1
902 years ago
IDAPython-Malware-Scripts preview

IDAPython-Malware-Scripts

GitHubcdong1012/idapython-malware-scripts

Scripts for automating malware analysis and reverse engineering workflows in IDA Pro, covering binary inspection, static analysis, and code…

binary-analysismalware-analysisreverse-engineering+1
762 years ago
SliverMirage preview

SliverMirage

GitHubdaniomass/slivermirage

Crystal Palace PICO loader for Sliver C2 dual-layer AMSI bypass, ETW silencing, AES-256-CBC encrypted payloads, 6 delivery variants
binary-analysiscommand-and-controlexploitation+4
472 months ago
Lucky-Spark preview

Lucky-Spark

GitHubschich/lucky-spark

A stealthy stager designed for shellcode payloads staged with http/https like Sliver, or on github raw.
binary-analysiscommand-and-controlexploitation+6
643 months ago
DRMBinViaOrdinalImports preview

DRMBinViaOrdinalImports

GitHubmaldev-academy/drmbinviaordinalimports

Create Anti-Copy DRM Malware
adversarial-attackbinary-analysismalware-analysis+2
722 years ago
kernagent preview

kernagent

GitHubkarib0u/kernagent

Headless AI agent for deterministic reverse engineering.
ai-assisted-reversingbinary-analysisforensics+4
10311 months ago
pe2pic preview

pe2pic

GitHubhasherezade/pe2pic

Small visualizator for PE files
binary-analysismalware-analysisreverse-engineering
703 years ago
machofile preview

machofile

GitHubpstirparo/machofile

machofile is a module to parse Mach-O binary files

binary-analysisforensicsmalware-analysis+2
998 months ago
Previous1…567…9Next