
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
257 results
dexcalibur preview

dexcalibur

GitHubreversenseorg/dexcalibur

[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…

android-securitybinary-analysisdebuggers+5
1.2k
17 days ago
MCExtractor preview

MCExtractor

GitHubplatomav/mcextractor

Intel, AMD, VIA & Freescale Microcode Extraction Tool
binary-analysisfirmware-analysishardware-security+2
92520 days ago
SigFlip preview

SigFlip

GitHubmed0x2e/sigflip

SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
binary-analysiscode-analysisdefensive-tools+5
1.3k3 years ago
Virtuailor preview

Virtuailor

GitHub0xgalz/virtuailor

IDAPython tool for creating automatic C++ virtual tables in IDA Pro
binary-analysisdebuggersdynamic-analysis-sandboxing+2
1.4k6 years ago
vmlinux-to-elf preview

vmlinux-to-elf

GitHubmarin-m/vmlinux-to-elf

A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)
binary-analysisembedded-systems-securityfirmware-analysis+1
1.8k3 months ago
Process-Dump preview

Process-Dump

GitHubglmcdona/process-dump

Windows tool for dumping malware PE files from memory back to disk for analysis.

binary-analysisforensicsmalware-analysis+2
1.9k3 years ago
e9patch preview

e9patch

GitHubgjduck/e9patch

A powerful static binary rewriting tool
binary-analysisbinary-exploitationfuzzing+1
1.2k2 months ago
Doldrums preview

Doldrums

GitHubrscloura/doldrums

A Flutter/Dart reverse engineering tool

android-securitybinary-analysismobile-security+1
8624 years ago
frida-ios-hook preview

frida-ios-hook

GitHubnoobpk/frida-ios-hook

A tool that helps you easy trace classes, functions, and modify the return values of methods on iOS platform
binary-analysisdynamic-analysis-sandboxingios-security+3
1.2k7 months ago
rop-tool preview

rop-tool

GitHubt00sh/rop-tool

A tool to help you write binary exploits

binary-analysisbinary-exploitationdebuggers+3
6107 years ago
HookCase preview

HookCase

GitHubsteven-michaud/hookcase

Tool for reverse engineering macOS/OS X
binary-analysisdebuggersdynamic-code-analysis+1
8404 months ago
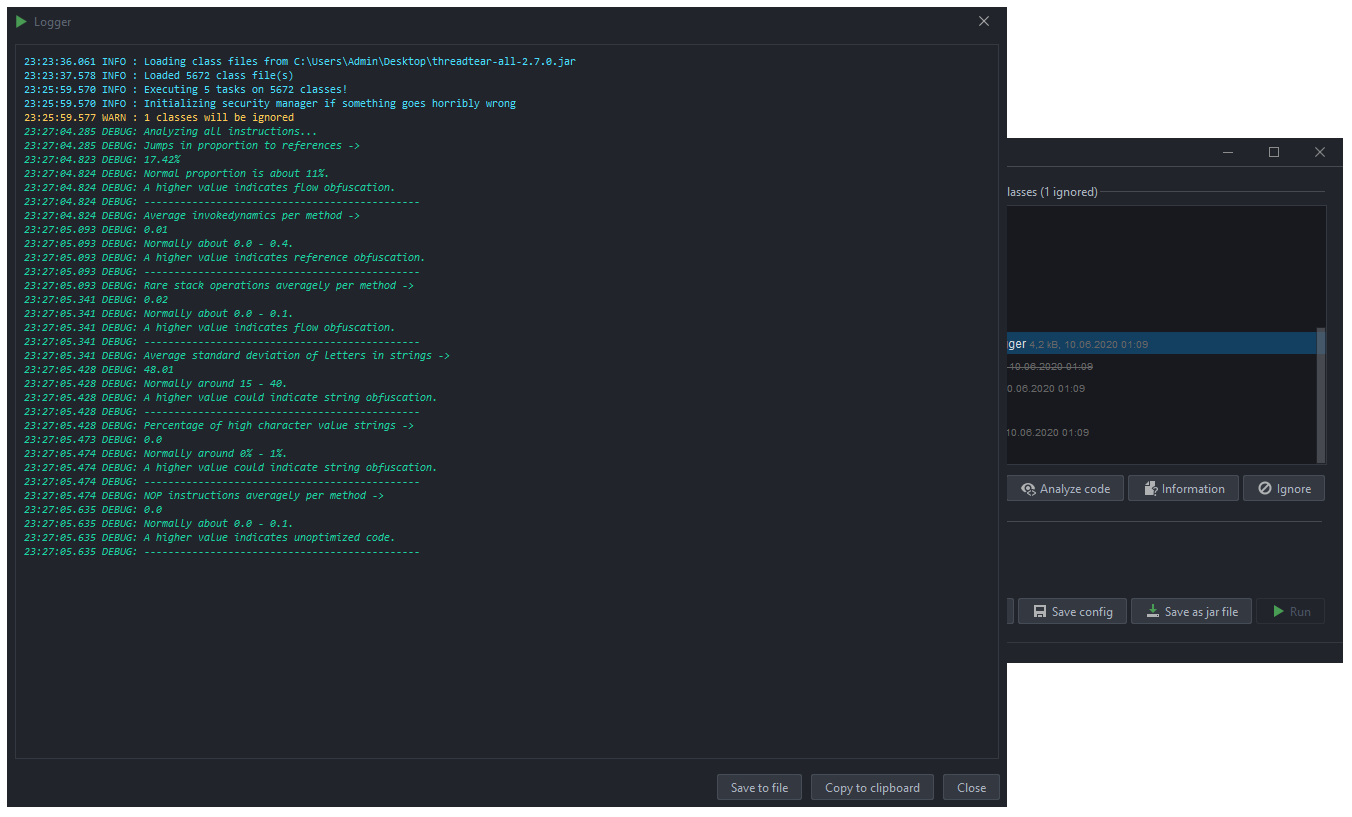
threadtear preview

threadtear

GitHubloerting/threadtear

Multifunctional java deobfuscation tool suite

binary-analysiscode-analysisdebuggers+3
9795 years ago
dr_checker preview

dr_checker

GitHubucsb-seclab/dr_checker

DR.CHECKER : A Soundy Vulnerability Detection Tool for Linux Kernel Drivers
binary-analysisfuzzingstatic-analysis+2
3394 years ago
Robber preview

Robber

GitHubmojtabatajik/robber

Robber is open source tool for finding executables prone to DLL hijacking
binary-analysisprivilege-escalationvulnerability-analysis+1
8004 months ago
Andromeda preview

Andromeda

GitHubsecrary/andromeda

C/C++ interactive reverse engineering tool for Android applications, enabling fast static analysis and binary inspection of APK files.

android-securitybinary-analysisreverse-engineering+1
7136 years ago
ReArk preview

ReArk

GitHublkimuk/reark

An intelligent reverse engineering analysis tool designed for multiple target platforms, currently supporting HarmonyOS (HAP/APP/ABC) and Android…
ai-assisted-reversingandroid-securitybinary-analysis+6
4146 days ago
Crassus preview

Crassus

GitHubvu-ls/crassus

Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…

binary-analysisexploitationpenetration-testing+1
6317 months ago
protobuf-inspector preview

protobuf-inspector

GitHubmildsunrise/protobuf-inspector

🕵️ Tool to reverse-engineer Protocol Buffers with unknown definition

binary-analysisreverse-engineeringutilities-frameworks
1.1k5 years ago
Previous1…456…15Next