
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
258 results
DLLirant preview

DLLirant

GitHubredteamsocietegenerale/dllirant

DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
binary-analysisdynamic-code-analysisexploitation+3
502
3 years ago
hacksguard preview

hacksguard

GitHubrhacknarok/hacksguard

A blazingly fast, multi-threaded TUI malware analysis tool built in Rust. Features deep PE parsing, YARA scanning, and heuristic risk scoring.

binary-analysisforensicsmalware-analysis+2
21422 days ago
asatools preview

asatools

GitHubnccgroup/asatools

Main repository to pull all NCC Group Cisco ASA-related tool projects.
binary-analysisdebuggersembedded-systems-security+3
2398 years ago
cdf preview

cdf

GitHubkudelskisecurity/cdf

Automated differential fuzzing tool for cryptographic software that detects implementation errors, compliance failures, and side-channel leaks…
binary-analysiscryptographyfuzzing+1
1715 years ago
RpcInvestigator preview

RpcInvestigator

GitHubtrailofbits/rpcinvestigator

Windows RPC interface discovery and analysis tool with visual endpoint enumeration, PE parsing, symbol resolution, real-time ETW sniffing, and…
binary-analysispenetration-testingreverse-engineering+1
3652 years ago
frida-extract preview

frida-extract

GitHuboalabs/frida-extract

Frida.re based RunPE (and MapViewOfSection) extraction tool
binary-analysisdynamic-analysis-sandboxingeducation+3
1159 years ago
MemITM preview

MemITM

GitHubamossys/memitm

Tool to make in memory man in the middle

binary-analysisdebuggersdynamic-analysis-sandboxing+4
1267 years ago
LeakedHandlesFinder preview

LeakedHandlesFinder

GitHublab52io/leakedhandlesfinder

Leaked Windows processes handles identification tool
binary-analysisexploitationpenetration-testing+1
2994 years ago
Platbox preview

Platbox

GitHubioactive/platbox

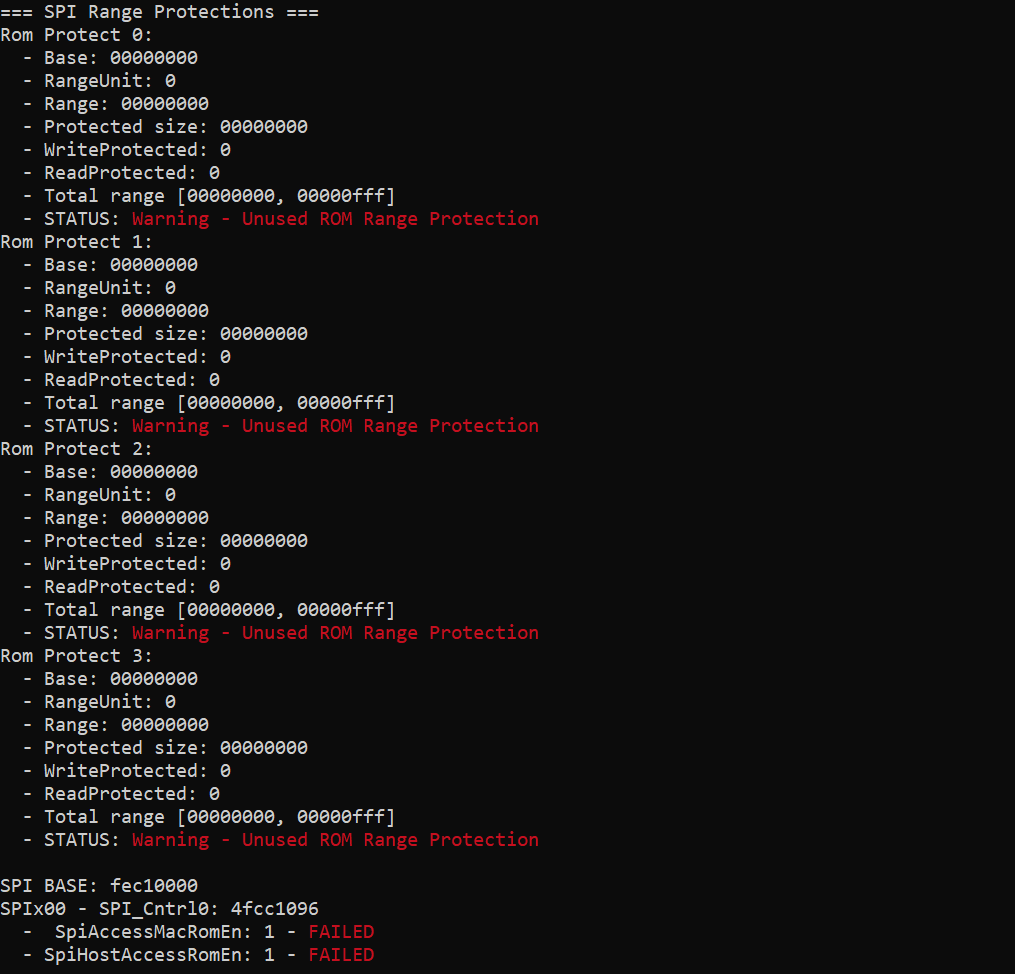
Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…
binary-analysisfirmware-analysisfuzzing+3
2221 year ago
autoharness preview

autoharness

GitHubparikhakshat/autoharness

A tool that automatically creates fuzzing harnesses based on a library
binary-analysiscode-analysisfuzzing+1
2954 years ago
IDA2Obj preview

IDA2Obj

GitHubjhftss/ida2obj

Static binary instrumentation tool that dumps COFF object files from executables, enabling code/data insertion at any location for black-box fuzzing…
binary-analysisdebuggersfuzzing+2
1225 years ago
nuitka-static-unpacker preview

nuitka-static-unpacker

GitHubdimareverse/nuitka-static-unpacker

Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.
binary-analysisdata-recoveryforensics+3
1331 month ago
Squalr preview

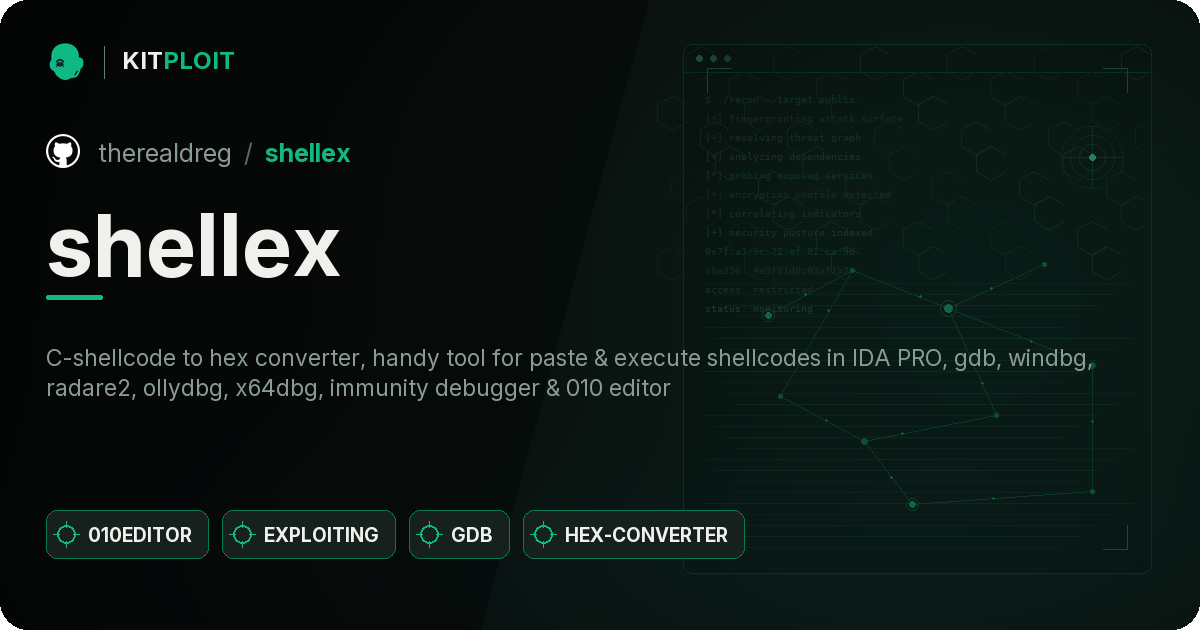
Squalr

GitHubsqualr/squalr

A generic game/software hacking tool written from the ground up in Rust.
binary-analysisdebuggersdynamic-analysis-sandboxing+5
1803 months ago
shellex preview

shellex

GitHubtherealdreg/shellex

C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
binary-analysisdebuggersexploitation+5
1133 years ago
ipa-medit preview

ipa-medit

GitHubsterrasec/ipa-medit

Memory modification tool for re-signed ipa supports iOS apps running on iPhone and Apple Silicon Mac without jailbreaking.
binary-analysisios-securitymemory-forensics+3
2111 year ago
gftrace preview

gftrace

GitHubleandrofroes/gftrace

A command line Windows API tracing tool for Golang binaries.
binary-analysisdebuggersdynamic-analysis-sandboxing+2
1592 years ago
PulseAPK-Core preview

PulseAPK-Core

GitHubdeemoun/pulseapk-core

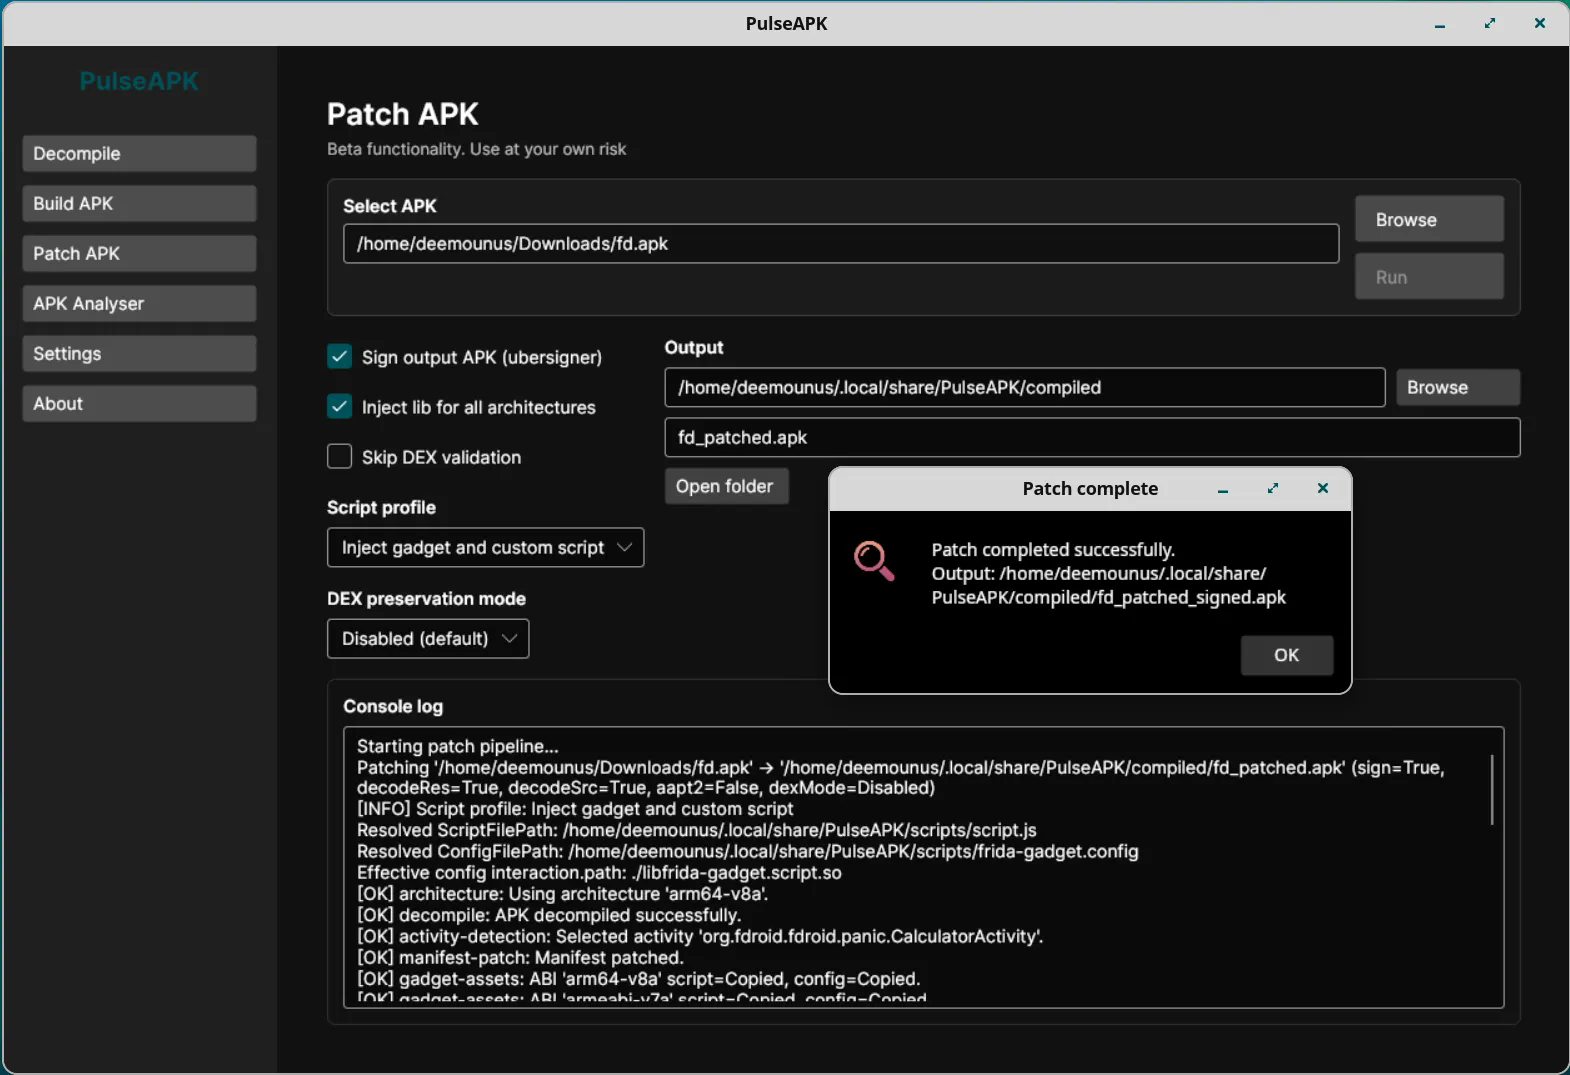
PulseAPK Core: Cross-Platform tool for working with APK files: Decompilation, Analysis, Building
android-securitybinary-analysisdynamic-analysis-sandboxing+8
1263 months ago
pftriage preview

pftriage

GitHubidiom/pftriage

Python tool and library to help analyze files during malware triage and analysis.

binary-analysisdigital-forensicsdynamic-analysis-sandboxing+4
796 years ago
Previous1…345…15Next