
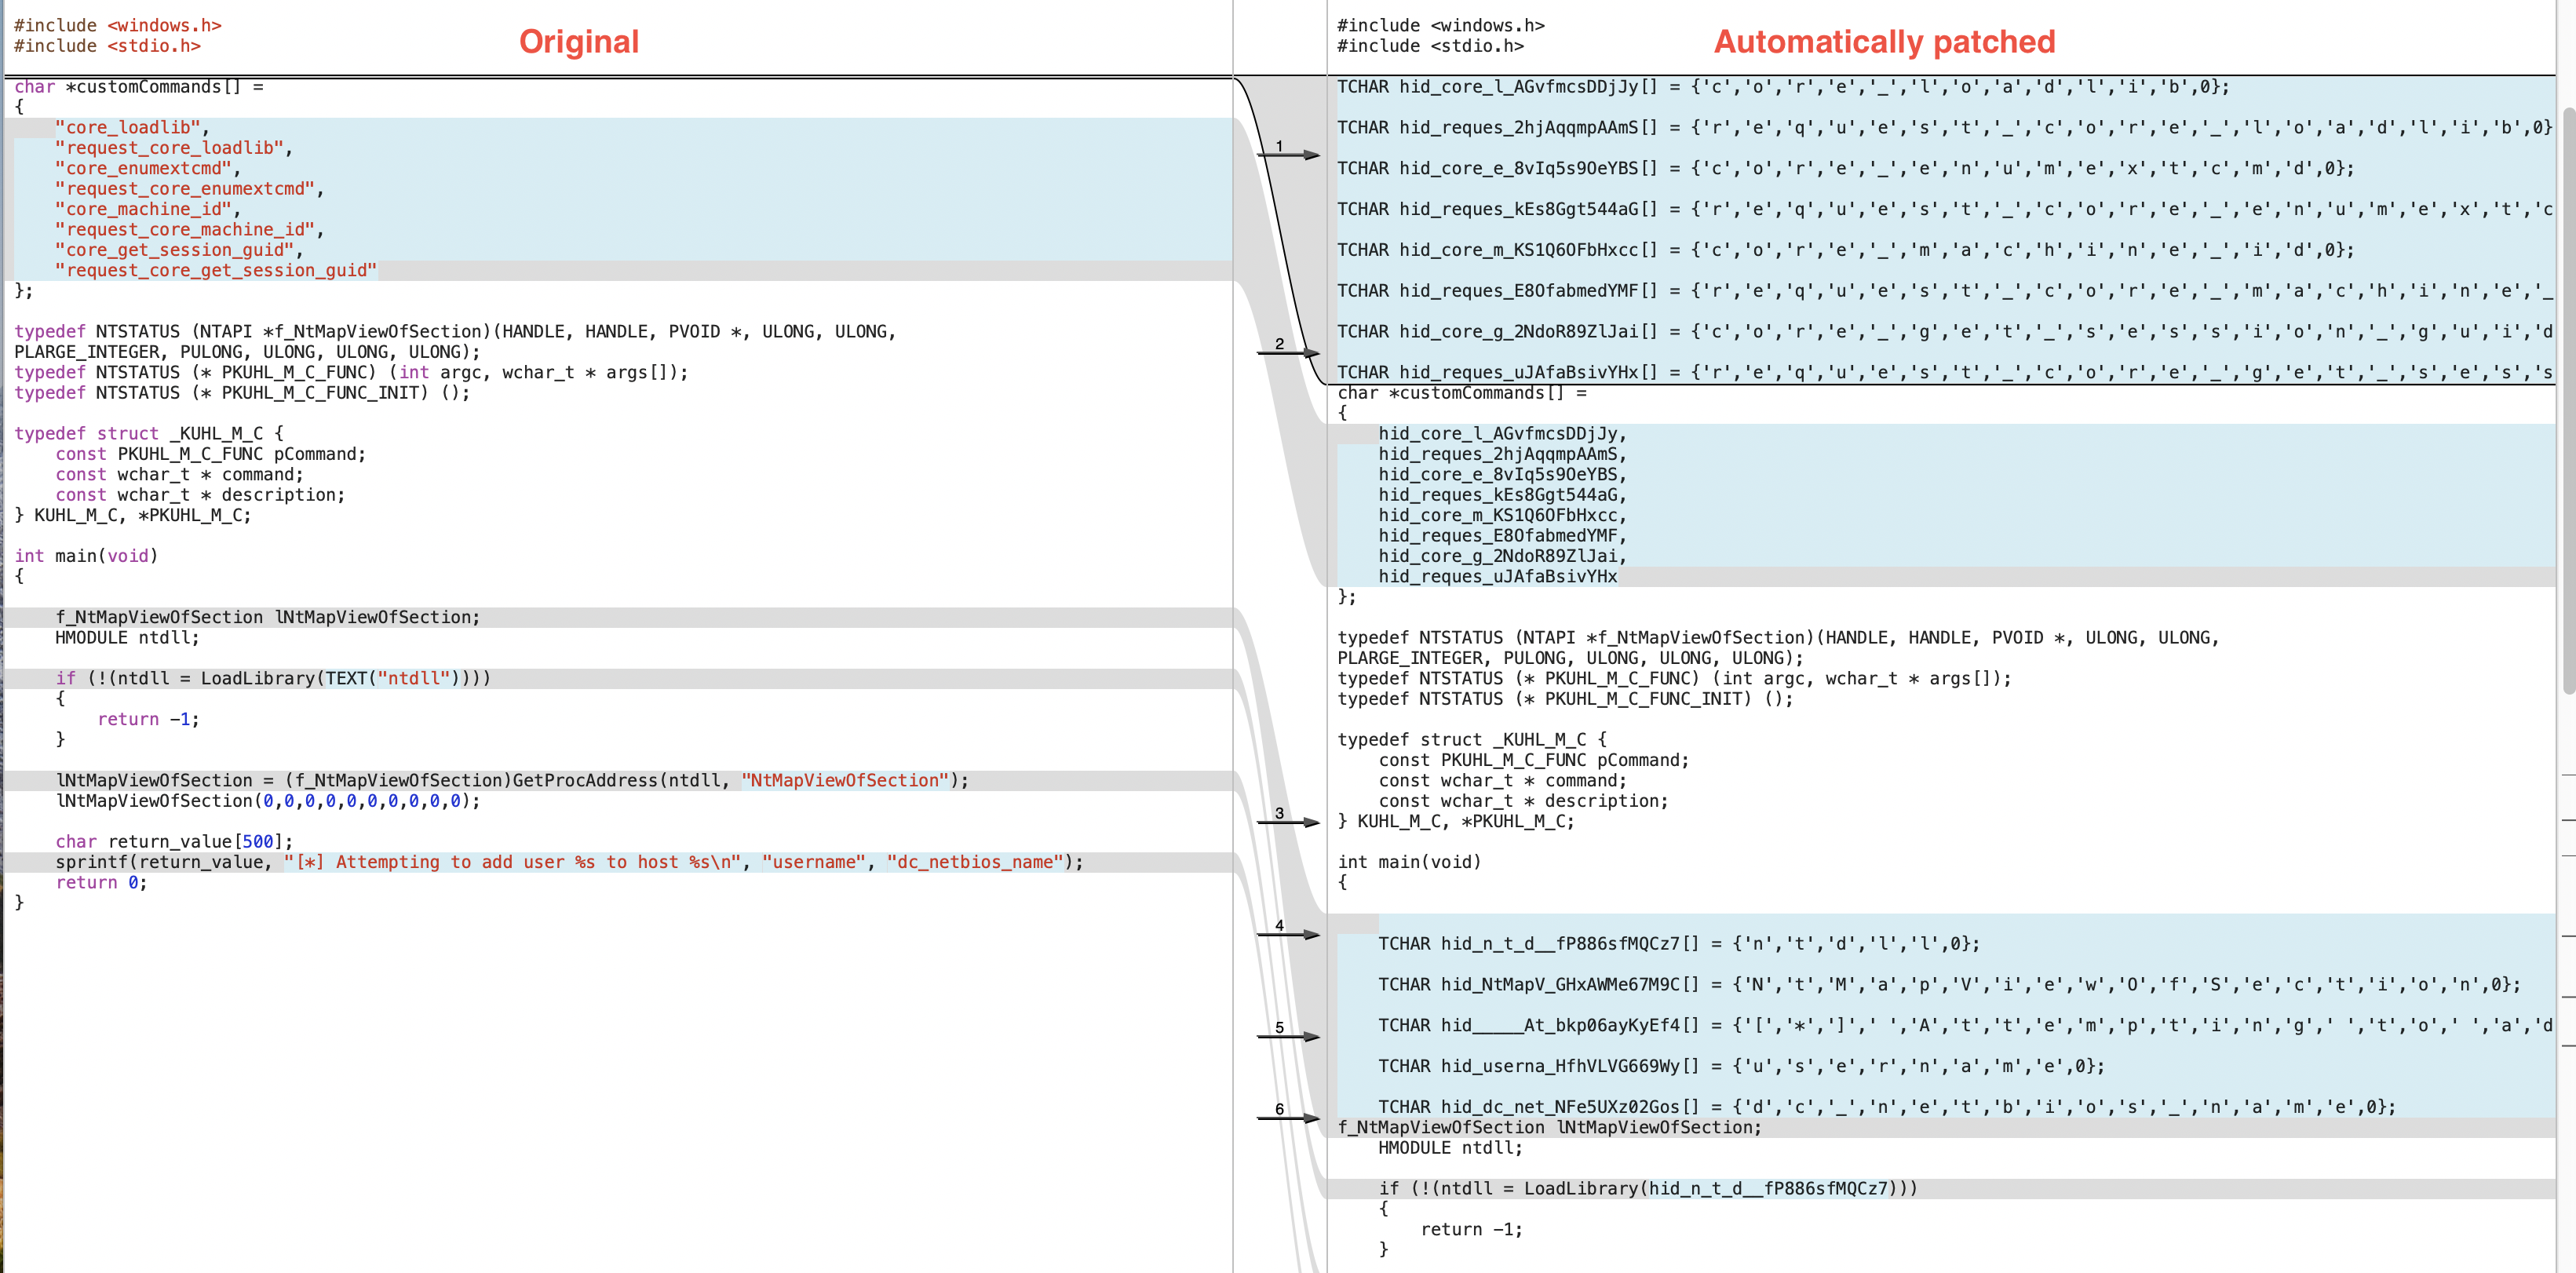
avcleaner
 scrt/avcleaner
C/C++ source obfuscator for antivirus bypass
binary-analysispayload-generation
scrt/avcleanerC/C++ source obfuscator for antivirus bypass
 northpolesec/santa
A binary and file access authorization system for macOS.
 xoreaxeaxeax/schrodingers-toctou
Detect compiler-invented memory loads that turn secure C into TOCTOU vulnerabilities. Includes automated source audits, Unicorn-based binary…
 ylca0/idalib-cli
Agent-native CLI wrapping IDA Pro IDALib for stateless, JSON-output binary analysis: disassembly, Hex-Rays decompilation, CFG, xrefs, strings, and…
 xyl2k/black-eye-rsa-attacking-toolkit-v0.1f-compiled
The great RSA Attacking Toolkit compiled for Windows
 sita-technologies/cve-2025-39247
HikCentral Professional - Pre-Auth License ActiveCode Leak
 sandi-go/cve-2018-15968
Technical disclosure of CVE-2018-15968: an out-of-bounds read vulnerability in Adobe Reader's PDF parsing, enabling information disclosure and…
 nccgroup/ghostrings
Ghidra scripts for recovering string definitions in Go binaries
 zznop/sploit
Go package that aids in binary analysis and exploitation
 kaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis
"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…
 ejfkdev/avdroot
Root an Android Studio emulator by patching its ramdisk with Magisk — in pure Go.
 mytechnotalent/reverse-engineering
A FREE comprehensive reverse engineering tutorial covering x86, x64, 32-bit/64-bit ARM, 8-bit AVR and 32-bit RISC-V architectures.
 mandiant/flare-learning-hub
Free educational content on reverse engineering and malware analysis from the FLARE team
 sentinelabs/alphagolang
IDApython Scripts for Analyzing Golang Binaries
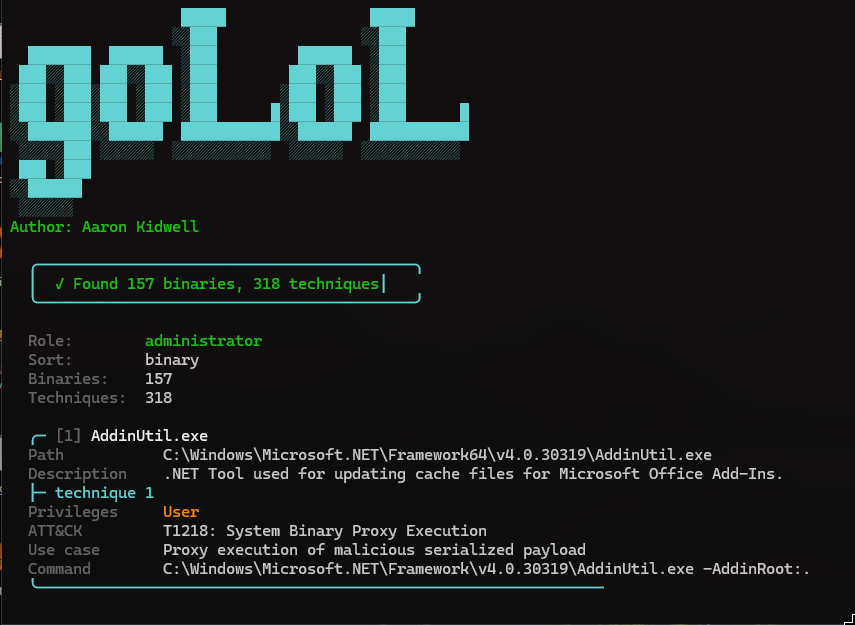 aaron-kidwell/golol
goLoL is a Windows host scanner with dual support for LOLBAS binaries and LOLDrivers. It lists LOLBAS techniques runnable at your current privilege…
 yaklang/javajive
Pure-Go Java Decompiler and Serialization Operator
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.