
 fuzztruction/fuzztruction
Fault-injection-based fuzzer that mutates generator programs to produce almost-valid inputs for targets, enabling fuzzing of complex formats and…
 c3rb3ru5d3d53c/mwcfg
A Feature Rich Modular Malware Configuration Extraction Utility for MalDuck
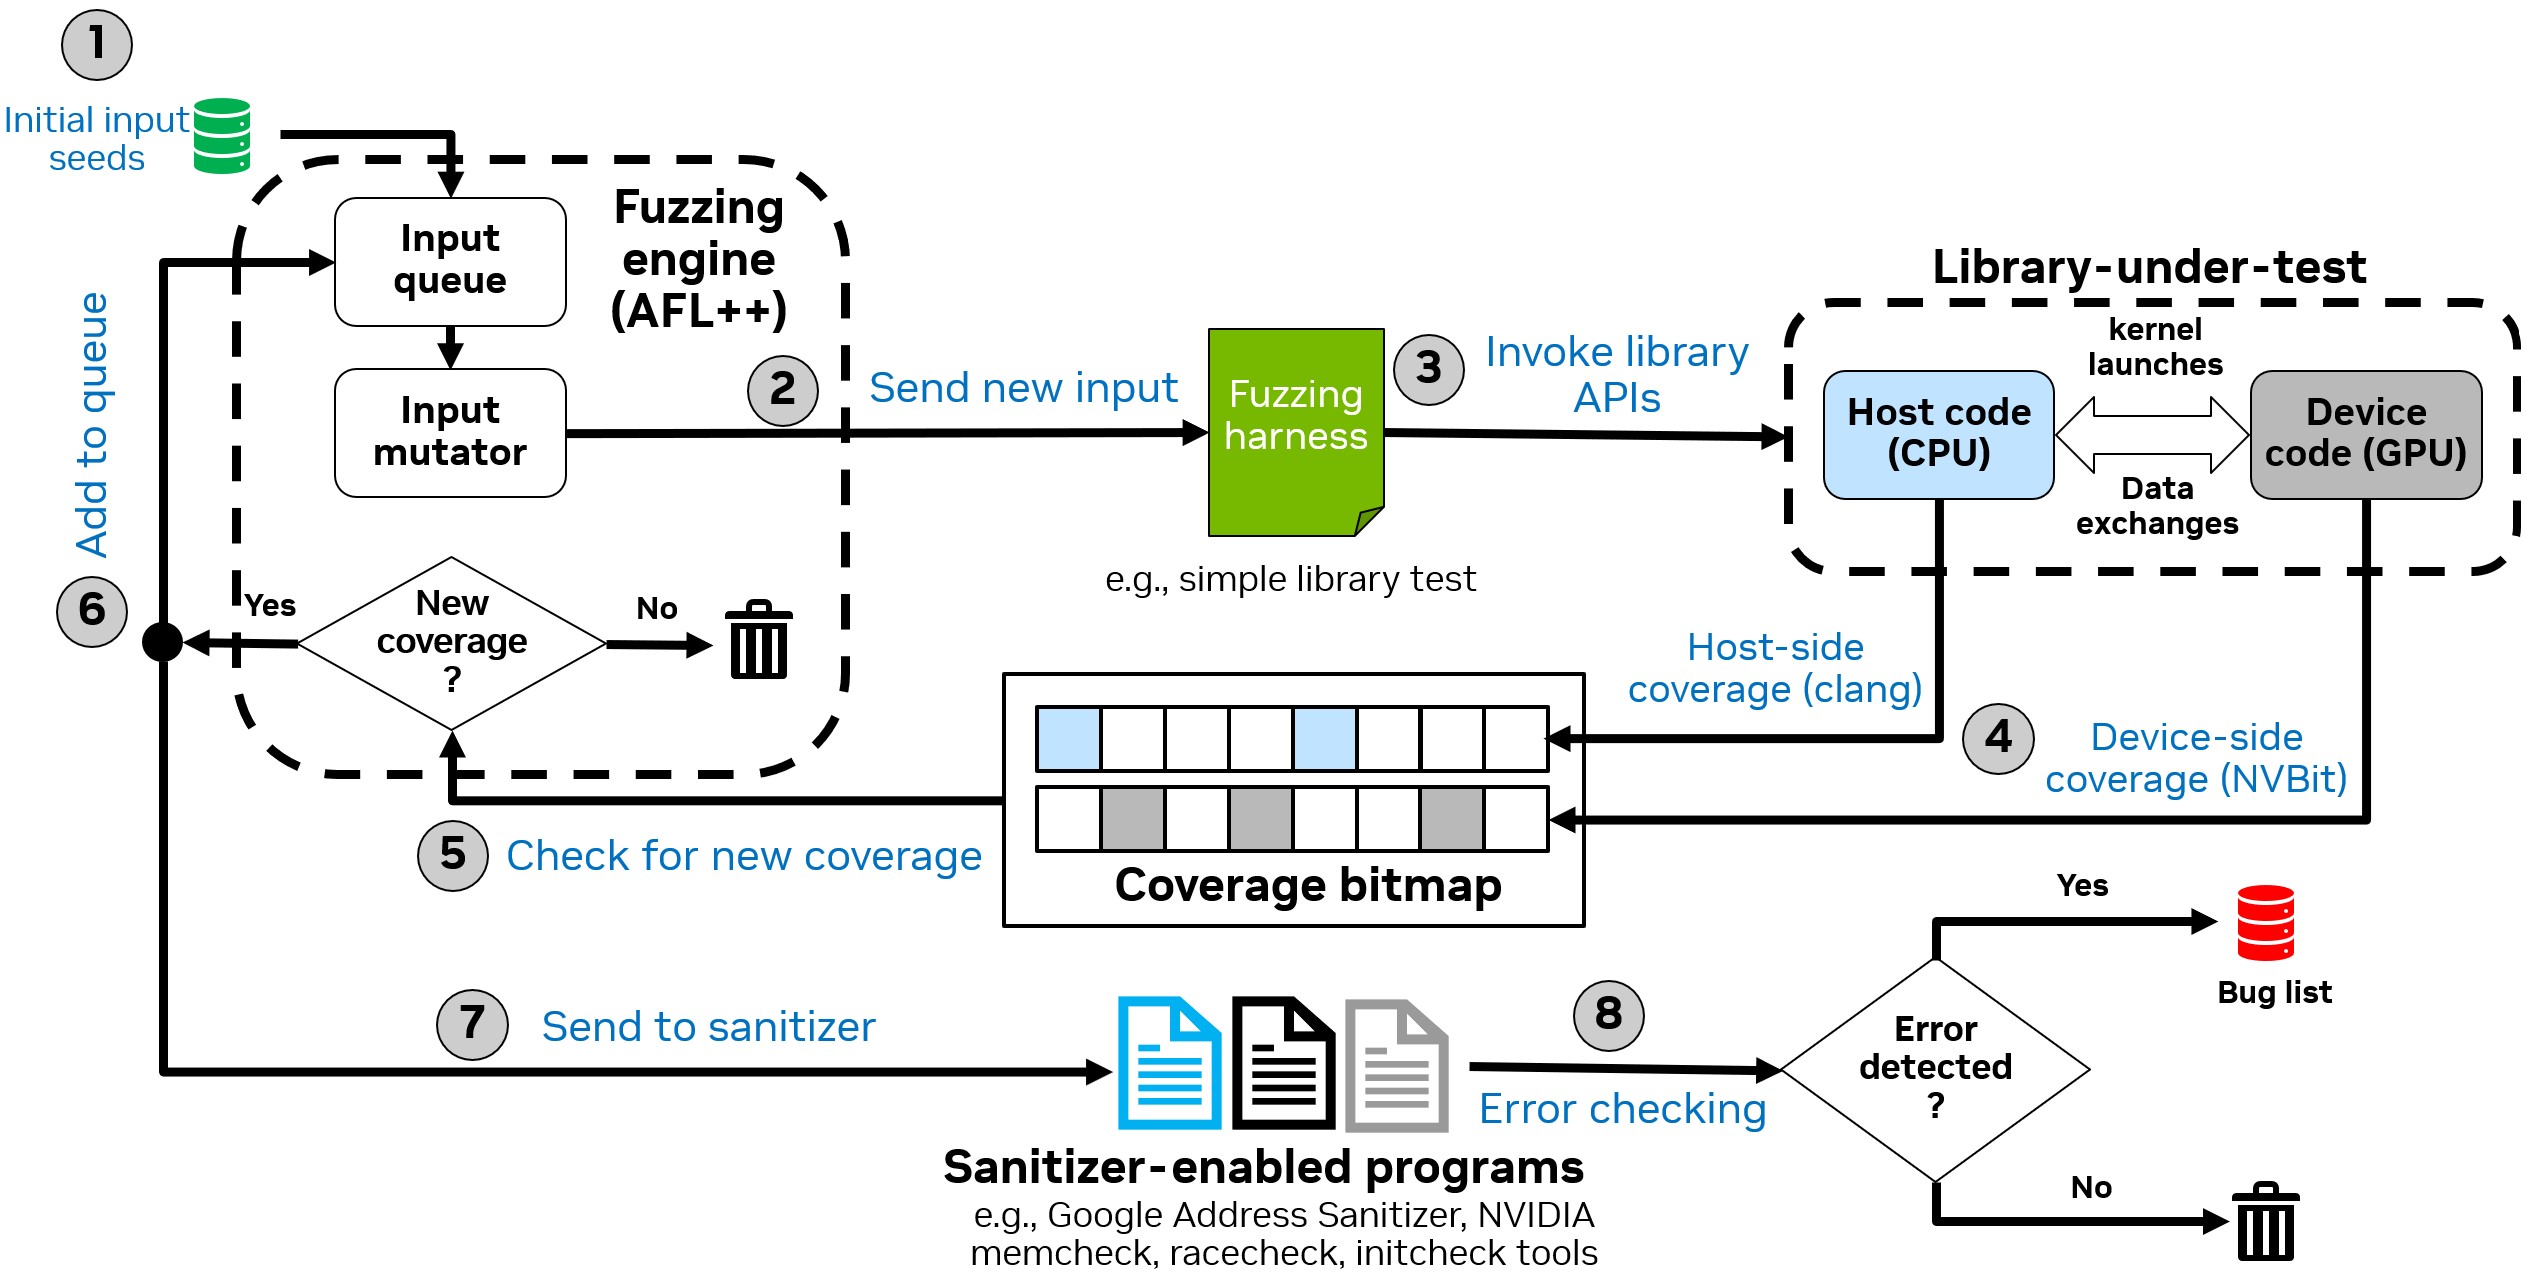 nvlabs/cufuzz
A GPU-oriented coverage-guided fuzzer for userland CUDA applications
 lfi-project/lfi
Top-level repository for LFI: Practical, Efficient, and Secure Software-based Sandboxing
 infobyte/draytek-arsenal
Reverse Engineering and Observability toolkit for Draytek firewalls
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
 sentinel-one/efi_fuzz
Coverage-guided fuzzer for UEFI NVRAM variables using Qiling emulation and AFL++ to discover firmware vulnerabilities through automated input…
 onekey-sec/unblob
Extract files from any kind of container formats
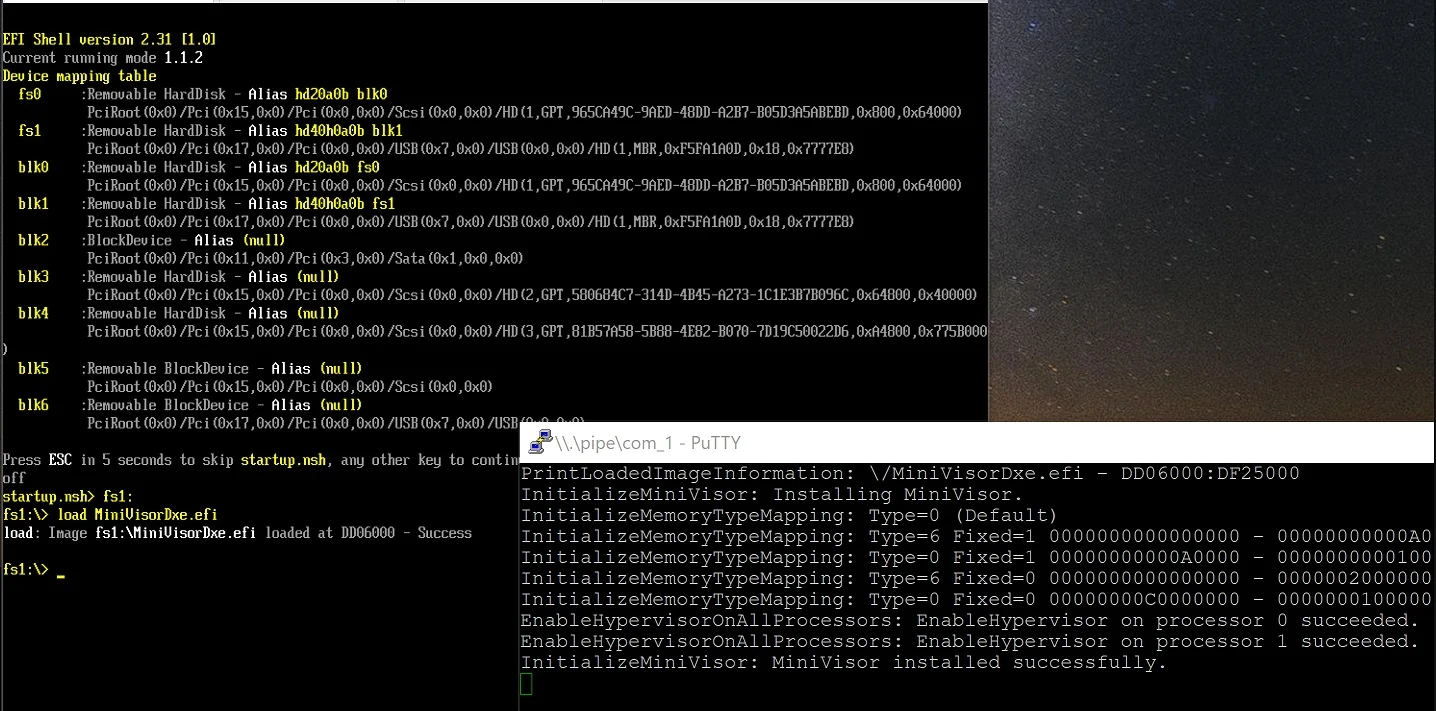 tandasat/minivisorpkg
The research UEFI hypervisor that supports booting an operating system.
 libriscv/libloong
The fastest LoongArch sandbox
 uni-due-syssec/efcf-framework
EF/CF - Extremely Fast smart Contract Fuzzing
 rizinorg/cutter
Free and Open Source Reverse Engineering Platform powered by rizin
 momo5502/sogen
🪅 Windows & Linux userspace emulator
 platomav/mcextractor
Intel, AMD, VIA & Freescale Microcode Extraction Tool
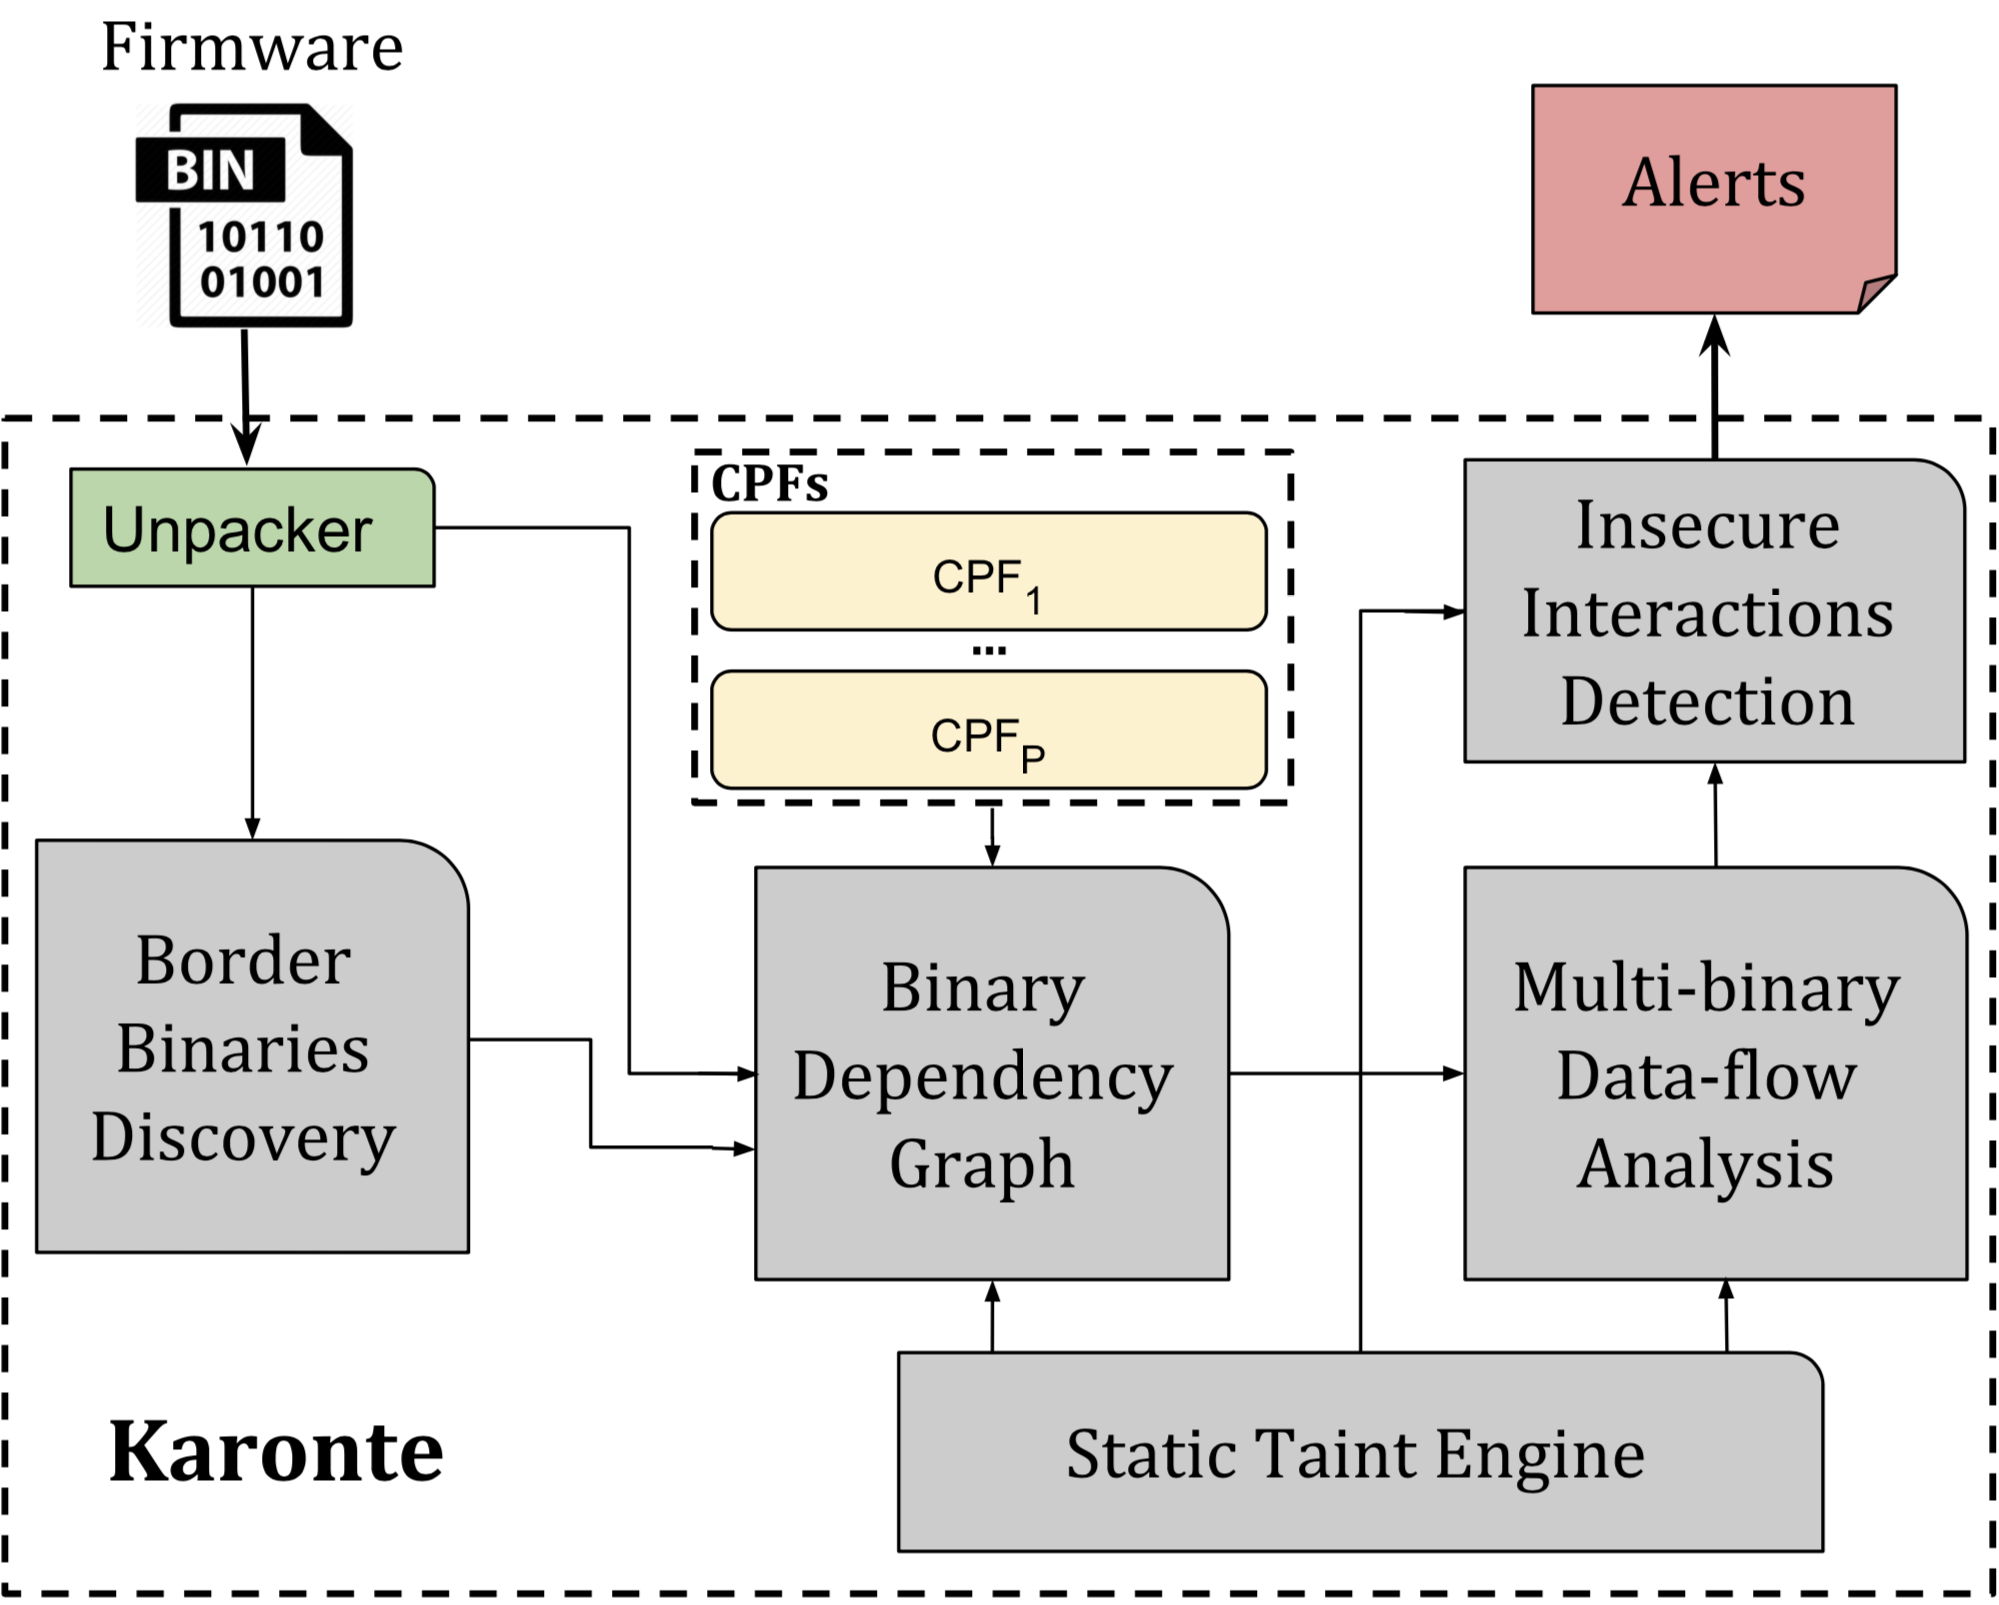 ucsb-seclab/karonte
Karonte is a static analysis tool to detect multi-binary vulnerabilities in embedded firmware
 hfiref0x/wdextract
Extract Windows Defender database from vdm files and unpack it
 lucamassarelli/yarasafe
SAFE embeddings to match functions in yara